President of @web3estonia. Founder and CEO of @complyonce (dealing with global digital identity crisis). VP of EW3O. Photographer to keep my mind sane.
Customer No. 1! And this time, it really means something.
@ComplyOnce has officially become the first member and customer of Roksnet’s newly launched X-Road based trust framework.
Being customer number one is both an honour and something meaningful to us. We share a vision of how trusted data exchange should work and how many of today’s data protection and security problems could be solved by changing the way organisations exchange information.
Roksnet has enormous potential, especially when federated with national X-Road networks. Estonia’s own X-tee ecosystem, operated by Riigi Infosüsteemi Amet // Estonian Information System Authority (NCSC-EE), has already shown what secure, authenticated and auditable data exchange can look like at national scale.
Instead of building yet another jungle of APIs, sharing credentials and trusting that everyone handles sensitive information properly, we can build on infrastructure where organisations authenticate each other and data exchanges are cryptographically protected, documented and auditable.
Having watched from the sidelines how much hard work Riho Oks and his team have put into building the Roksnet trust service, we have enormous respect for what they have achieved.
Building trust infrastructure is not easy. Building it properly is even harder.
Their dedication is also a great example for us at ComplyOnce.
We believe that digital trust should not depend on blind trust between systems. It should be built into the architecture.
#ComplyOnce #Roksnet #XRoad #DigitalIdentity #DigitalTrust
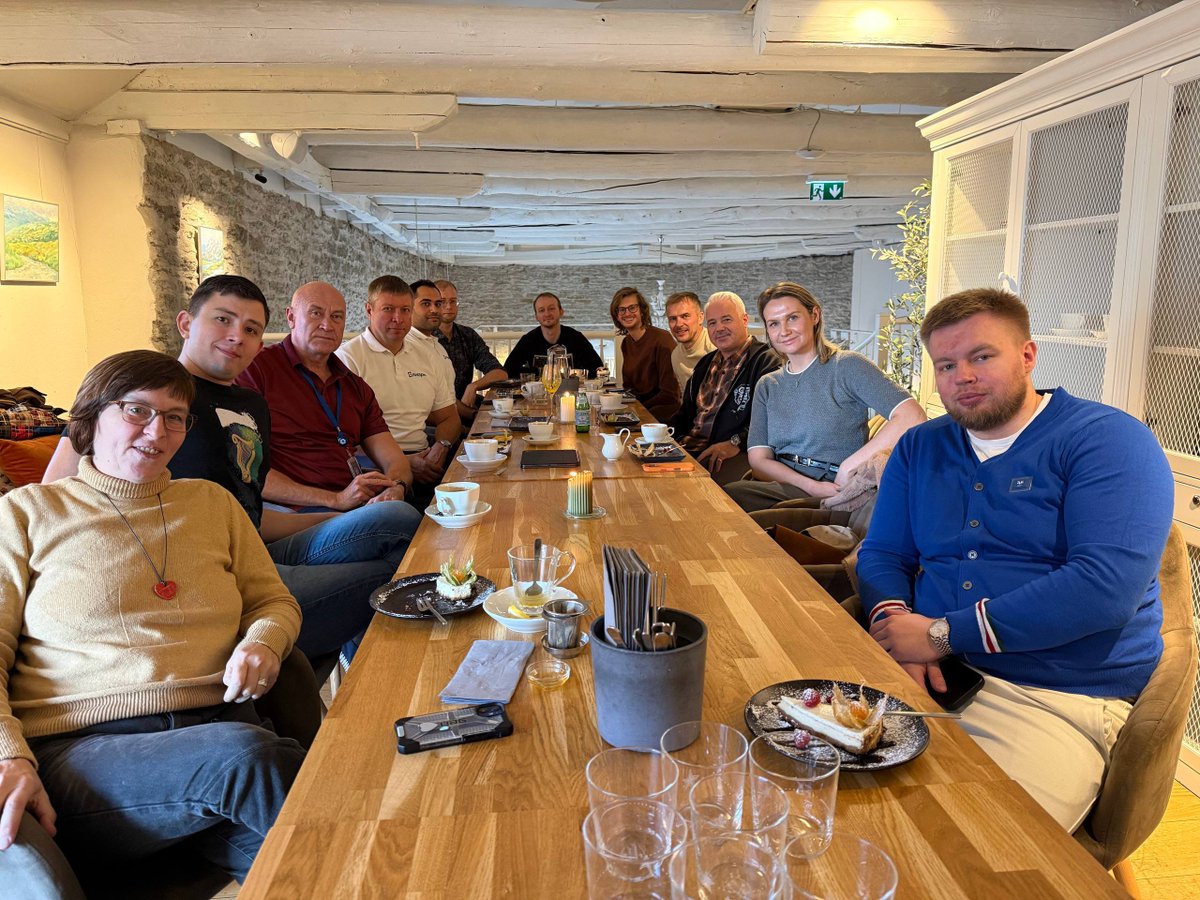
Another wonderful Web3 Community Brunch at Basiilik pitsa ja pasta restoran this morning.
We had good conversations, heard fresh perspectives and familiar faces left us with great energy for the rest of the month.
Thanks to everyone who joined 💙
#Web3#community#estonia
Estonia proved it over 20 years ago: verify the human at the entry point and everything after gets simpler.
Signatures, taxes, health, business. Access comes first. The rest follows.
Identity is becoming one of fintech’s most important infrastructure layers 🤯
@raidosaar and @themagnusjones are in London at FTT Fintech Festival & Future Identity Festival, where the conversation is moving well beyond onboarding alone.
Digital identity now sits at the intersection of fraud prevention, customer experience and compliance.
Great to see the team on the ground, meeting the people shaping what trusted digital access looks like next.
#FTT26 #FutureIdentity #DigitalIdentity #Fintech #ComplyOnce
Your identity shouldn’t stop working at the border.
People live in one country, work in another, invest through a third and use services across the entire EU.
Yet identity verification is still often built country by country. A user verifies with one national eID. Then they move, open an account elsewhere or need access to another regulated service and suddenly the process starts from zero again.
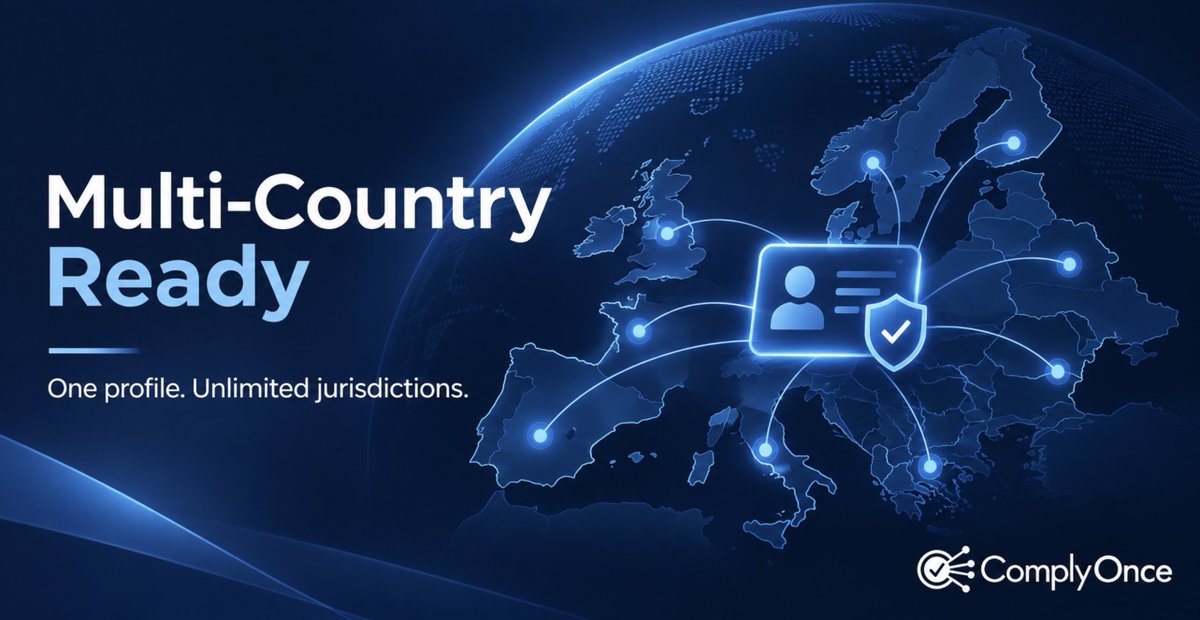
That is exactly the problem behind Multi-Country Ready in ComplyOnce™. A single @ComplyOnce identity profile can link verified identities from multiple jurisdictions.
The user authenticates through a trusted source such as a national eID, EUDI Wallet or regulated identity broker. That identity is then bound to the user’s profile once.
From there, the same trusted identity profile can be used across connected services and jurisdictions.
ComplyOnce supports eIDAS High and Substantial assurance levels, allowing services to work with identity proofs that meet the level of trust their use case requires.
And because the architecture is cross-border native, the user doesn't need a completely separate identity profile every time they interact with a service in another EU Member State.
Why does this matter?
Because the future of European digital services cannot be built on 27 disconnected onboarding experiences. Fintechs, gaming platforms, age-restricted services and other regulated businesses increasingly serve users across borders. Their identity infrastructure needs to be able to do the same.
And this brings us closer to what digital identity was always supposed to become: portable, interoperable and trusted across borders.
Comply once. Move freely.
#verification #Europe #EU #digitalidentity #fintech #gaming #eID #complyonce
eIDAS 2.0 puts a digital identity wallet within reach of every EU citizen. Prove who you are or just the one fact needed without handing over everything. The tech exists. What's missing is the will to stop defaulting to passwords.
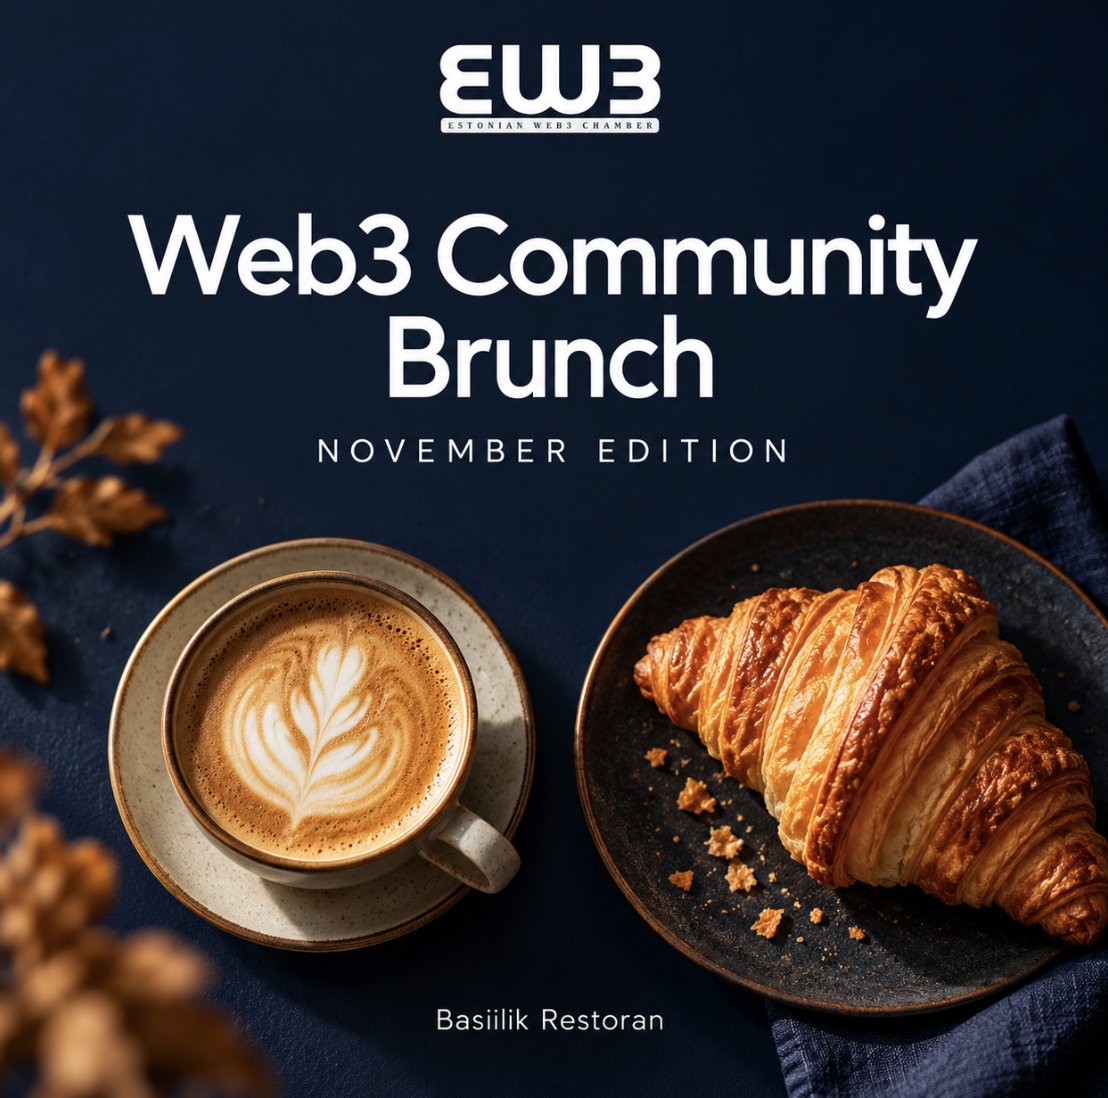
🥐 Coffee, brunch & Estonia’s Web3 community.
Join the Estonian Web3 Chamber to catch up, share ideas and meet fellow builders.
📅 Fri, Nov 13 · 10:00–12:00
📍 Basiilik Restoran
☕ 10% off the menu with code EW3
Grab a seat 👉 https://t.co/s8rkUH7FQW
Your identity shouldn’t need a new copy every time you verify.
Raido explains how the @ComplyOnce ID Vault keeps verified identity data protected while services receive only the proof they need.
Less data copied. Less data exposed.
#verification#digitalidentity#compliance #KYC #complyonce #data
The undefined human is the real attack surface. Phishing, account takeovers, bot farms, synthetic identities all exploit the same gap: the system knows the credentials, never the person.
Username and password is a 1960s workaround. We still use it to decide who signs contracts, receives benefits and talks to AI. Human access deserves better infrastructure than a shared secret.
ComplyOnce is ISO/IEC 27001:2022 certified.
Independent confirmation that the way we build and run privacy-centric digital identity infrastructure meets the international security standard. Before launch, not after.
Thanks to our team and to Smart Service Solution OÜ for the implementation support.
#ISO27001 #DigitalIdentity
ComplyOnce is now a member of ITL, the Estonian Association of Information Technology and Telecommunications. 🇪🇪
Estonia built the world's reference model for digital identity. ITL brings together the companies that built it and keep it running. We're proud to join them.
@ComplyOnce is a verified fact-sharing ecosystem built on eIDAS 2.0. Our mission is to make online trust work without handing over more personal data than the moment requires:
- Passwordless login that also proves to you that the service is genuine
- Proofs instead of raw data, such as age, eligibility or humanness, from your own ID-Vault
- ISO 27001 certified.
Fraud, bots and fake accounts are a shared problem across the whole digital economy. We look forward to working with fellow ITL members on the next chapter of a smart, secure Estonia, and to taking that model to Europe.
Thank you to the ITL Estonia team for the warm welcome. If you're a member and identity, KYC or fraud prevention is on your roadmap, let's talk.
A question for every CIO: who is actually on the other side of your login screen? If the honest answer is "whoever knows the password", your digital strategy is built on sand.
We are building @ComplyOnce because compliance should not stop a customer from paying for an app from another country. Right now, a traveler abroad can face SMS codes and a full ID check just to complete a small purchase.
We are working on verification that protects people without getting in the way of their own money.
Storing personal data at scale has become one of the most dangerous things a financial institution can do.
Every KYC database is a liability waiting to be breached. We are building toward a model where compliance and user safety can coexist without turning sensitive data into a honeypot for bad actors.
The legal framework needs to catch up with that reality.
#kyc #verification #complyonce #data #compliance