🚨Critical vulnerability: CVE-2026-41940 (CVSS 9.8) in cPanel and WHM
This pre-authentication bypass allows a remote attacker to gain administrative access with no credentials required.
⚠️ Exploitation attempts observed
🛠️ Patch immediately
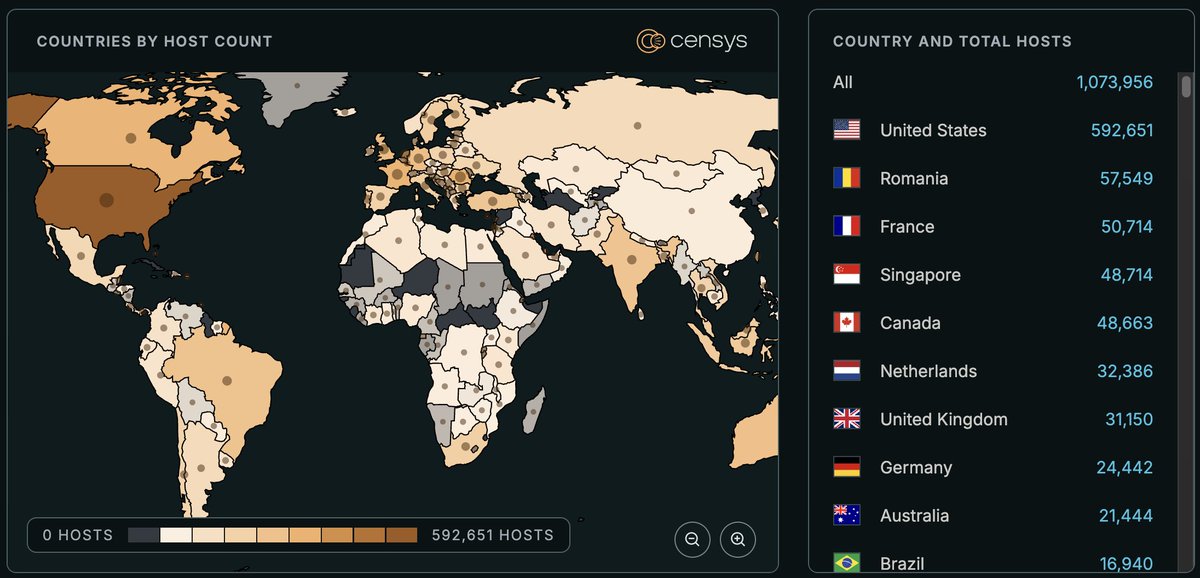
Determining vulnerability is difficult, however, Censys observes ~1.1M exposed hosts and ~6.7M web properties.
Full advisory: https://t.co/1TOrv2u3LS
#CVE202641940 #infosec
🔐 cPanel Emergency Patch: Critical Auth Bypass Hits 3.5M+ Servers
A critical vulnerability in cPanel and WHM just got an emergency fix, and here's why you need to care.
The bug allows unauthenticated access to the control panel. No login, no credentials, no firewall rules stopping it. Just direct access to the administrative interface that manages your web hosting environment.
Think about what that means:
🔍 An attacker can reset passwords, modify DNS records, inject malicious code into hosted sites, and pivot to the underlying server.
🔍 cPanel powers millions of shared hosting environments. A single compromised WHM instance can lead to dozens or hundreds of compromised customer websites.
🔍 This is the kind of vulnerability that botnets actively scan for within hours of disclosure.
The attack surface here is massive. Small businesses, agencies, and managed hosting providers running outdated cPanel versions are the primary targets. If you're running anything other than the latest patched version, assume you're exposed.
What to do right now:
✅ Update to the latest cPanel and WHM version immediately. This is not a "schedule for next week" fix.
✅ Check your access logs for suspicious unauthenticated requests to the WHM login endpoint.
✅ Restrict WHM access to trusted IP ranges if you haven't already.
#threatintel #cybersecurity #infosec