Starting with v1.98 on desktop, Brave removes hidden identifiers that Meta adds to your photos on Instagram and Facebook.
This makes it harder for Meta to link the same photo across accounts and sites.
⚠️ 🇸🇻 🏦 🗄️ PREVENTIVE ALERT – ALLEGED DATA EXFILTRATION FROM THE CENTRAL RESERVE BANK OF EL SALVADOR
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: RESISTENCIA TEAM / DATE: NOVEMBER 9, 2026]
Centralized cyber-intelligence systems have intercepted a post on clandestine messaging channels (recorded on November 9, 2026) by the group "Resistencia Team." The post announces the alleged exfiltration and public availability of a compressed repository titled "Leak .zip," with a file size of 1427.5 MB, purportedly extracted from the infrastructure of the Central Reserve Bank of El Salvador (BCR).
The attached visual evidence shows the group’s announcement, which includes the official logo of the Central Reserve Bank and the institutional emblems of the Government of El Salvador, alongside a downloadable file that allegedly contains confidential financial or governmental information.
It is strictly noted that the veracity of this intrusion, the initial access vector, and the overall authenticity of the exposed files have not been officially confirmed by the Central Reserve Bank of El Salvador or the relevant competent authorities.
🌐 Incident Summary and Targets (Alleged / Unconfirmed)
Threat Actor: Resistencia Team
Victim / Target: Central Reserve Bank of El Salvador (BCR) / Government of El Salvador — 🇸🇻 El Salvador
Sector: 🏦 Banking, Financial, Government, and Central Banking
Publication Date: November 9, 2026
Reported Volume: 1427.5 MB in a compressed leak file (Leak. zip)
Nature of the Incident: Alleged compromise of the central bank’s institutional servers, massive exfiltration of documentation, and the release of a large-volume repository via encrypted messaging channels.
🔍 Technical Breakdown of Compromised Information (Alleged)
Based on telemetry and metadata from the intercepted post:
Exfiltration Format: Compressed container file (Leak .zip) with a size of approximately 1.4 GB.
Affected Institutional Assets: Alleged internal documentation, financial records, databases, or operational files linked to the operations of the Central Reserve Bank of El Salvador.
🛡️ Technical Preventive and Containment Recommendations (SOC / CSIRT / Central Bank)
Audit and Review of Technological Infrastructure:
The technology and information security teams at the Central Reserve Bank of El Salvador must immediately audit their network gateways, database servers, and internal systems to verify the integrity of the infrastructure and rule out unauthorized access.
Protection of Financial Assets and Critical Systems:
Given the alleged exfiltration of over 1.4 GB of data, it is urged that perimeter access controls be strengthened and that the monitoring of outbound data flows be enhanced. Active Monitoring of Clandestine Channels:
🖥️ Centralized Threat Monitoring System
Intelligence System: https://t.co/wk9bZJ3laQ
Quickly check your security at: https://t.co/5LuqwzZ2HE
Quotes and services: https://t.co/TNlfnMHgK9
#ElSalvador #BCR #CentralBank #ResistenciaTeam #DataLeak #DataBreach #BreachAlert #DarkWeb #Hacking #ThreatIntel #ThreatIntelligence #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert #CyberDefense #CyberRisk
⚠️⚠️ All LNbits users should stop their LNbits servers IMMEDIATELY. ⚠️⚠️
Please forward this announcement.
Following a wave of attacks, we have a number of security patches to push. Until then, it's better to err on the side of caution. 🙏
Updates to follow soon.
Sí, como yo tienes un Amazon Echo Show 5 (1 y 2 gen) que es más inútil que pezón de hombre, le puedes instalar un Linux:
https://t.co/oX5mqm5JId
Y ese es mi proyecto de sábado.
“Hay un error en Electrum, una billetera popular de Bitcoin, y los atacantes ya lo están explotando. Si usas Electrum, actualiza a la versión 4.8.3 ahora mismo.
Así es como funciona el ataque...
Electrum no descarga toda la cadena de bloques. A menos que ejecutes tu propio servidor, le pregunta al servidor de otra persona qué está pasando con tu billetera. Un servidor deshonesto puede abusar de esa confianza.
1. Envías un pago. El servidor deshonesto lo descarta silenciosamente, por lo que nunca llega a la red de Bitcoin.
2. El servidor luego muestra en tu billetera un pago pendiente falso que envía tus monedas al atacante en su lugar. La dirección del atacante está hecha para terminar con los mismos caracteres que la real, por lo que parece correcta a simple vista.
3. El falso no tiene tarifa, por lo que parece atascado. Las versiones antiguas de Electrum no verifican sus firmas, por lo que lo muestran como tu propio pago.
4. Haces lo que cualquiera haría con un pago atascado. Lo aceleras aumentando la tarifa (un "fee bump", también llamado RBF). Tu billetera firma una versión completamente nueva y válida del falso, y ahora el atacante realmente recibe el pago.
Al menos una persona ya ha perdido dinero de esta manera. Verificar solo los últimos caracteres de una dirección no te protegerá aquí. Verifica toda la dirección y el monto antes de firmar.”
Tweet completo 👇🏽
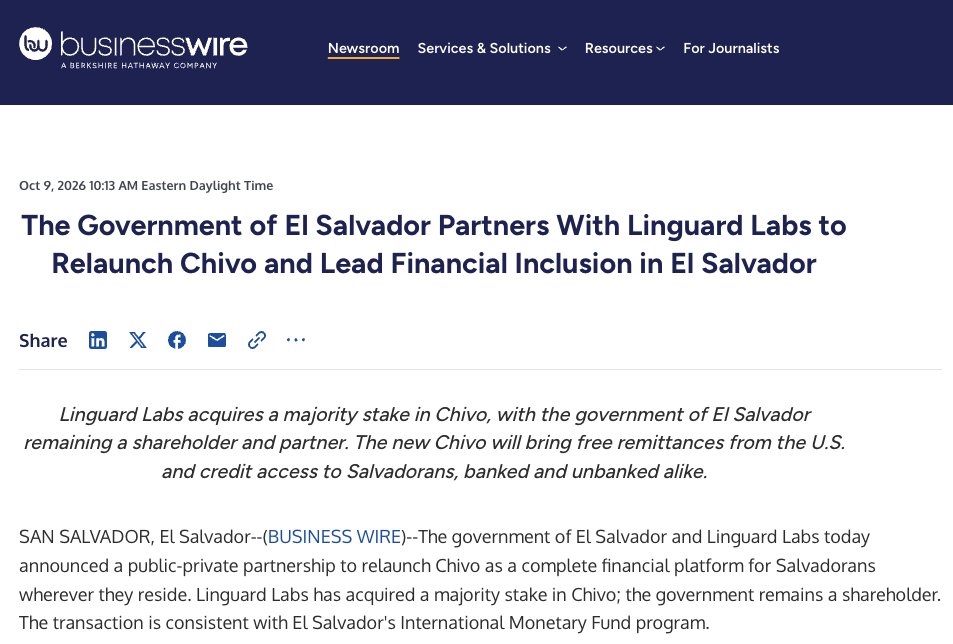
Chivo wallet has finally been sold to Linguard Labs
it's run by ex-bankers and they're adding stablecoins and microloans + focusing on remittances.
What a disappointment for bitcoin chivo was, hey.
Bottom Up > Top Down
🚨 We're releasing BTPay Server 2.4.7 an emergency update fixing one critical and several medium-severity security vulnerabilities brought to our attention through @Anthropic's frontier OSS scanner.
We recommend that you update your BTCPay Server as soon as possible.
📱 Motorola ouvre une porte de sortie
GrapheneOS va ENFIN tourner sur un téléphone qui n'est pas un Pixel
- Pas de Google au cœur du système
- Motorola fournit lui-même les pilotes et le firmware au projet
- Et à terme, le Signature 27 sera vendu avec @GrapheneOS préinstallé
On en a parlé quelques fois ici... jusqu'à maintenant pour se dégoogliser il fallait acheter un téléphone... Google !
Ce paradoxe est en train de tomber
Le support n'est pas disponible avant 2027, le portage est en cours. Pour l'instant le téléphone sort sous l'Android de Motorola
Bref... Pendant que d'autres veulent filtrer le réseau... Vous, vous pouvez reprendre le téléphone 😉
🚨 Si tienes un nodo #Bitcoin con umbrelOS 2.0, esto te interesa.
Acabo de comprobar 6 paquetes pendientes de actualización, incluidos Docker y containerd.
¿Quién garantiza que los parches de seguridad llegan a tiempo? 🧵