Government agencies are balancing mission demands with the need to modernize securely. Join public sector leaders at the @RedHat Government Symposium to explore AI, automation and open source strategies for mission-ready IT. #GovIT Register: https://t.co/MoBRKYCsqd
Our report with @NIST shares technical recommendations for federal agencies & cloud service providers to safeguard the identity assertions + tokens threat actors increasingly target to move laterally within networks & reach sensitive data. Learn more🔗 https://t.co/uGYVKjZtb0
There are numerous ways to extract cloud credentials (like tokens) once an attacker gains access to a workstation. Protect your cloud admin credentials as Tier 0.
https://t.co/yjD8tKv2eA
Can’t agree with this more! All the hottest trends are focused on analyzing AI for exploit development, which is definitely a path forward, but defenders have so many use cases that can benefit right now from applying AI to protect!
We need to stop thinking of “AI for cybersecurity” as just bug hunting and alert triage. There’s so much more that AI can do for defense.
For example, using LLMs for monitoring and detection is extremely underexplored.
Still one of the most overlooked basic steps of AD (and even Entra in some environments!) that let’s Red Teamers and Adversaries get domain admin access in minutes. Worth your time to train on and remediate!
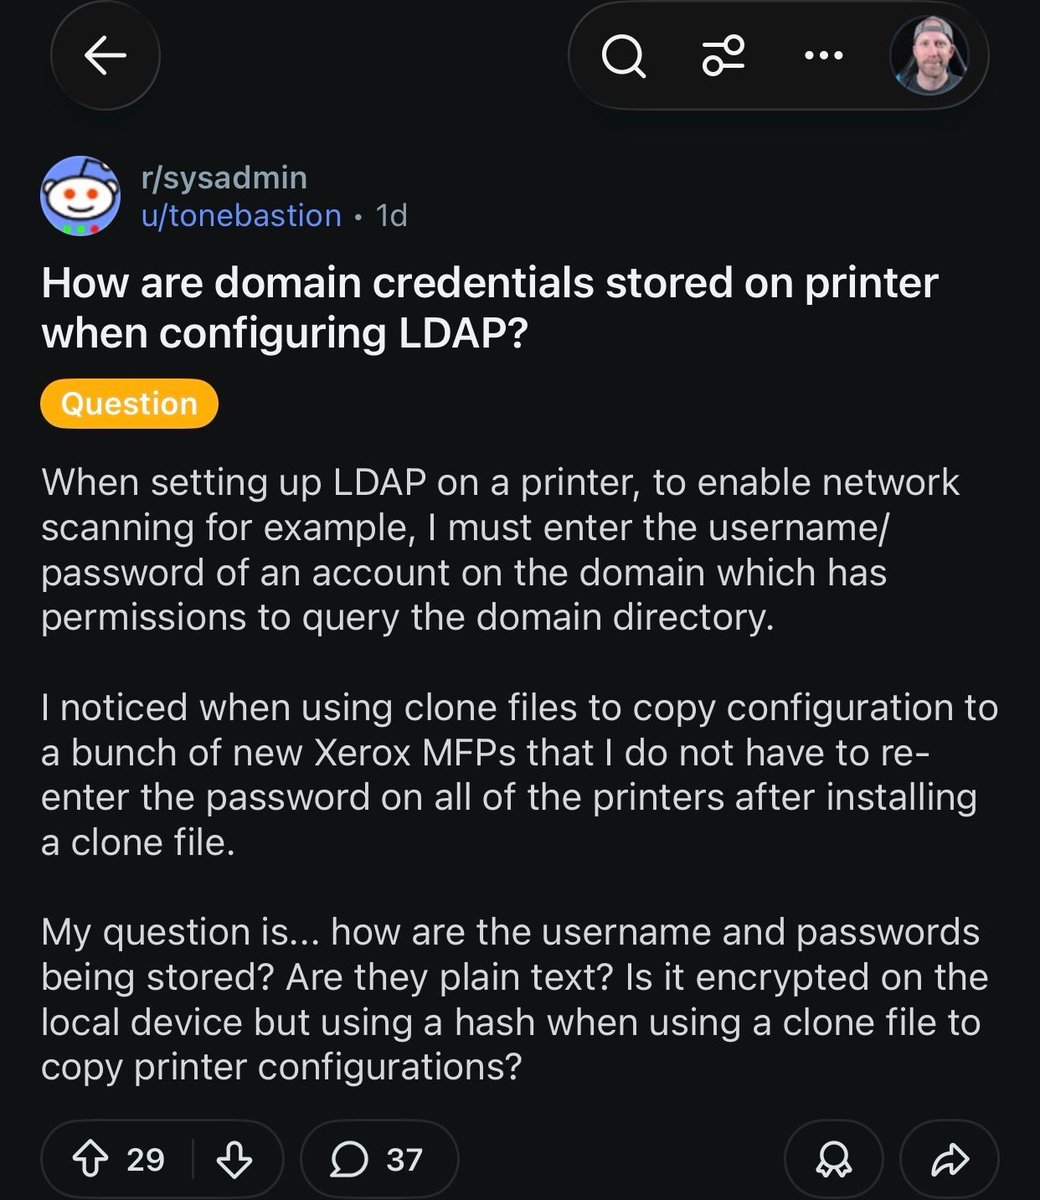
One time on an internal I found a xerox MFP that had 40+ CVEs. Ended up abusing some weird RCE to get a shell, then later was able to dump credentials from a cloud storage connector config.
Printers are wild 😆
https://t.co/tBs6Ezxeqd
While AI has and will continue to lower the barrier of entry for adversaries, it’s also not the first time adversaries have used new tech to do bad things. Defenders have to evolve too, or we’ll always be behind the curve. Integrating agents into your SIEM yet?
Q4 is here, don’t forget to add the following to your password spraying lists:
Fall2025
Fall2025!
Autumn2025
Autumn2025!
Autum25!
Password2025
Password2025!
Companyname2025!
Companyname2025!
Lateral movement getting blocked by traditional methods?
@werdhaihai just dropped research on a new lateral movement technique using Windows Installer Custom Action Server, complete with working BOF code. https://t.co/sS6P6d6ADC
This one’s nasty folks, and it looks like the good guys are behind the power curve on discovery. Please patch quickly, but not so quick you don’t see if you’ve already been exploited!
https://t.co/tZqXgn7Hyh
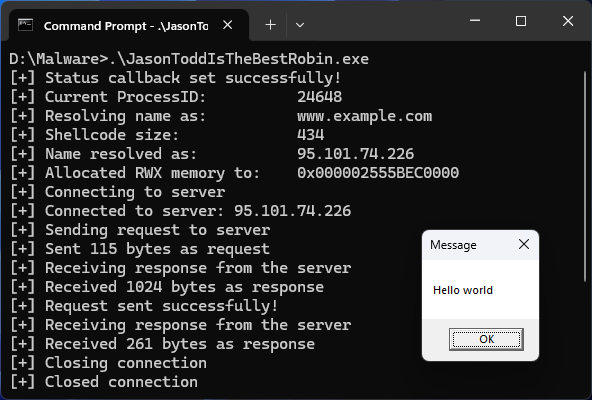
Do you want to trigger shellcode only when:
- Certain DNS resolution happens?
- Certain servers are reached out to?
- When you get a 112 byte long response?
...etc
Meet InternetSetStatusCallback() for fine tuning execution (or if you are just bored):
https://t.co/774bIeEsN7
I Just documented a cool way to authenticate proxied tooling to LDAP in an AD environment using C2 payload auth context, without stealing any tickets or hashes!
Keep tooling execution off-host and away from EDR on your Red Team assessments!
https://t.co/VLE2Kh4idY
The AD CS security landscape keeps evolving, and so does our tooling. 🛠️
@bytewreck drops info on Certify 2.0, including a suite of new capabilities and refined usability improvements. https://t.co/7VEjWCOHi1