We used this technique on an op recently, and I wanted to create a simple resource on it due to it being seldom covered but very useful.
It's a cool way to get around various NTLM relay constraints when operating over C2 from low-privilege.
See it here:
https://t.co/YtCZ7Ah0CB
Meet Sage: open-source AI for assumed-breach operations, built into Mythic. State your objective; Sage prepares commands for your approval in supervised mode.
@Ne0nd0g breaks it down in his new blog ⤵️ https://t.co/haYwfjObTc
Hopefully coming to Mythic v4 soon. Direct RDP and VNC functionality via Guacamole. No rportfwd involved, just a direct feed to Guacamole via a new interactive streaming mode from the mythic agent.
Might be a tough watch from a mobile device, so I'd recommend a larger screen.
1/2
LDAP signing was supposed to stop NTLM relay to LDAP. I found a way to relay coerced SMB auth to a DC with LDAP signing and channel binding enforced.
Patched in October.
Blog: https://t.co/dUHIN6JfaE
PoC: https://t.co/xT98z64V96
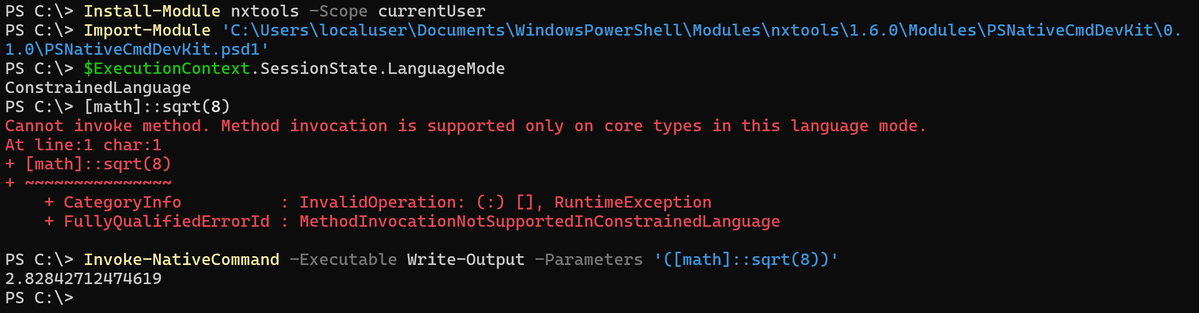
Need to circumvent Constrained Language Mode while operating in an environment with App Control for Business enabled? https://t.co/rxotmrMLEz (Was reported, is by design). Enjoy!
Friday afternoon (vibe)coding project that was on my to-do for a while: obtaining Entra ID tokens from an endpoint by asking the WAM. This alternative to using the PRT cookie follows the legitimate SSO flow used by apps like Teams to obtain tokens. Code: https://t.co/qAEk8lXGYG
ServiceNow won't let you query cleartext discovery credentials, not even as admin. @Tw1sm found a way to make the server hand them over anyway, no coercion or relay needed.
Works on SSH keys, AWS keys, Entra secrets, and LDAP creds.
Check it out ⤵️ https://t.co/ryVKdaDmGE
CVE-2026-34348 exploitation demo from my #BHUSA "Pass-the-Passkey Family of Attacks" talk: WebAuthn assertion from recent YubiKey authentication is extracted from Windows Event Log and replayed against Microsoft Entra ID using Passkey Injector.
Whitepaper: https://t.co/bp5sriMB5z
Happening now! @bagelbyt3s is kicking of his briefing session presenting original research into a new Attack Path technique that results in full WSUS infrastructure takeover. #BHUSA
Compromise one node in a Windows Server Failover Cluster and you've compromised all of them.
@unsigned_sh0rt dug into why: shared credentials, forged tickets, and a full attack chain to own the cluster.
Check it out! https://t.co/53K9xgF7rY
Need to do an NTLM relay over C2 but local priv-esc isn't possible?
@_logangoins new post walks through relaying NTLM auth out of a network and back in through red team infra to bypass traditional relay controls, plus how defenders actually stop it.
https://t.co/gV9M93hBhs
Registration for training at #BHUSA 2026 is officially open, and we are bringing a full slate of adversary-focused courses to Las Vegas. 🎰
Early reg. pricing ends May 22, so now is the time to lock in your seat.
🧵 Links to each course ⤵️
@dez_@_xpn_@cryps1s@SpecterOps Yes! We have a library of other scenarios and testing ranges available as well. I'm happy to talk through what we offer whenever you'd like. Linking our 2-pager on that service below: https://t.co/gGAlhUk6Ur
Just added krb5 auth over ADWS in my tool SOAPy. I noticed since SOAPy released 2 yrs ago with the first ADWS python code nobody had implemented krb5 auth in python.
Check it out here, and stay tuned for an upcoming blog post + big release 👀
https://t.co/PvIQC4iWlh