Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
Palo Alto Networks says attackers are exploiting a new flaw that lets them run code as root on its firewalls.
CVE-2026-0322 needs a login to the PAN-OS management interface. Palo Alto says exploitation is "very limited". Patches are available.
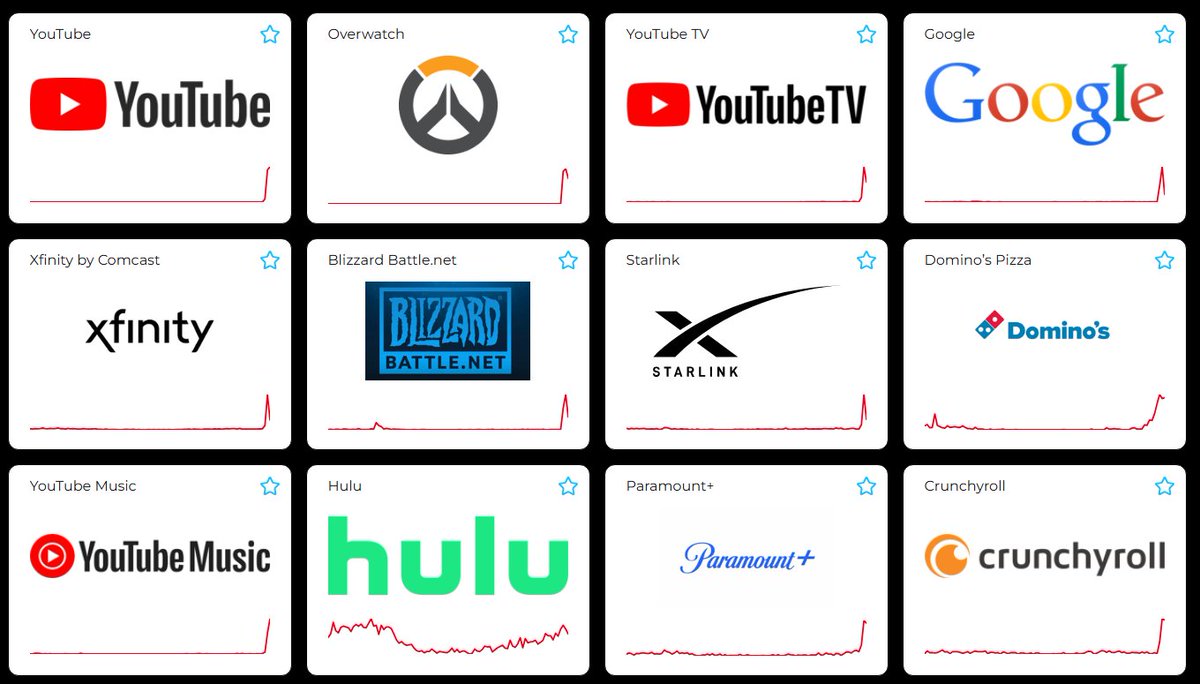
‼️ Lots of services experiencing issues right now...
YouTube
Overwatch
YouTubeTV
Google
xFinity
https://t.co/p6ZoDYTDE0
Starlink
Domaino's
YouTube Music
Paramount+
Crunchyroll
🚨 Key ShinyHunters Member Detained in Jordan
Saif al-Din Khader, an alleged key member of ShinyHunters who reportedly uses the handle "Rey," was detained by Jordanian authorities earlier this week, according to Reuters.
Two sources told Reuters that Khader is cooperating with the FBI and other law enforcement agencies to help identify and locate other members of the group.
The detention comes amid an FBI investigation into a recent intrusion allegedly involving ShinyHunters, which has claimed to have stolen extensive data belonging to FBI employees.
We are tracking rumors + honeypot activity relating to a new vulnerability affecting Citrix appliances, acknowledged just now in a Citrix blog.
It is currently unclear whether this is “DoS via bad patch" or "another bad vuln in SAML config'd appliances"
Our hearts 💔
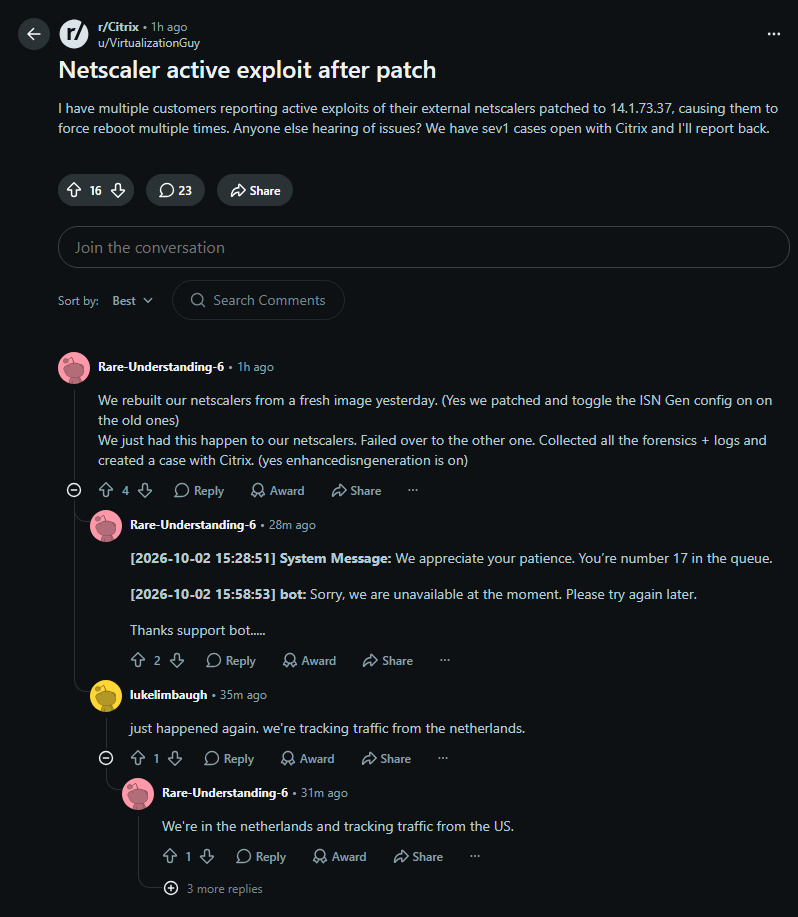
🚨 Reports of NetScaler Incidents After Latest Patch Raise Concerns Over Continued Exploitation
Multiple Citrix administrators are reporting suspicious activity affecting NetScaler appliances even after updating to version 14.1-73.37.
The reports surfaced on Reddit, where one administrator said multiple customers experienced incidents that caused externally accessible NetScaler appliances to repeatedly reboot.
Other administrators reported similar behavior on newly rebuilt appliances, including systems where Enhanced ISN Generation had already been enabled. Several affected organizations said they collected forensic data and opened cases with Citrix.
It is currently unclear whether the activity represents successful exploitation of a new or existing vulnerability, residual compromise, vulnerability scanning, or an issue with the updated firmware.
The reports come days after Citrix disclosed active exploitation of CVE-2026-88771 and CVE-2026-88772, two critical vulnerabilities affecting NetScaler ADC and NetScaler Gateway.
The latest post-patch activity has not yet been confirmed by Citrix as exploitation.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
🚨 BREAKING: Finland's cyber agency reports several intrusions through the Citrix NetScaler zero-days.
NCSC-FI has contacted the owners of hundreds of NetScaler instances in Finland and warns that patching alone will not remove an attacker who is already inside.
CVE-2026-88771 allows command execution without authentication.
🚨Citrix NetScaler ADC and NetScaler Gateway are affected by multiple vulnerabilities, including 2 critical zero-day #RCE vulnerabilities being exploited globally. See our Alert for more: https://t.co/pDudecAuzQ
Please see our latest Citrix NetScaler ADC and Citrix NetScaler Gateway Security Bulletin for CVE-2026-88771 through CVE-2026-88778. Citrix urges affected customers to install the relevant updated versions as soon as possible. https://t.co/0JS7KidPd8
Per watchTowr on the Citrix situation...
- Citrix comms & patches are expected early next week.
- Two vulnerabilities - both RCE. Unpatched, 0days.
- Exploited in-the-wild - discovered during forensics.
Nothing really to update on this but...
- watchTower has confirmed this with national certs.
- CVE-2026-19490 is not the vulnerability.
- Citrix has remained silent.
Shut down if you can. Better safe than sorry.
‼️ Two chained SSH flaws gave attackers full admin on MikroTik routers — one of them using -2 as a username.
No password. No SSH key. No authentication at all.
CERT Polska says it was exploited before patches shipped.
Learn how it works ↓ https://t.co/xkwXsXT0UZ
The FBI is aware of a cyber-criminal enterprise group claiming a compromise of the https://t.co/xzuiRQwBTb portal and alleged impact to FBI employee personally identifiable information (PII). While the point of breach is still undetermined—whether a third-party or the FBI’s enterprise—we are actively and aggressively investigating this matter and working closely with those third-party providers that support https://t.co/xzuiRQwBTb to mitigate any and all risk.
‼️ URGENT - WordPress issues patch a new critical flaw (CVE-2026-87902) that requires no account and can lead to code execution on some servers.
Versions 4.7.0 through 7.1.1 are affected.
Here's how the flaw works: https://t.co/7zcWyMyHR4
❗️ Nightmare Eclipse, the researcher feuding with Microsoft, has released another Defender zero-day that blocks antivirus updates.
BigDiskBuster waits for Defender to start an update, then fills the system drive with a hidden file so the update has no room to install. Defender stays on, stuck with whatever signatures it already has.
Nightmare Eclipse is also known as ex-Microsoft Germany security researcher Abdelhamid Naceri, and has now dropped almost a dozen Windows zero-days since April.