Protecting your digital assets from the latest cyber threats. Red Threat Cyber Security offers MSSP, penetration testing, database optimization, SOC & many more
Healthcare founders: Passing an audit isn’t about “no vulnerabilities.” It’s about proving your system protects patient data the right way. We worked with QuantCare for a Manual pentest → Passed audit 👉
https://t.co/8uZDmG5646
Mildly Interesting:
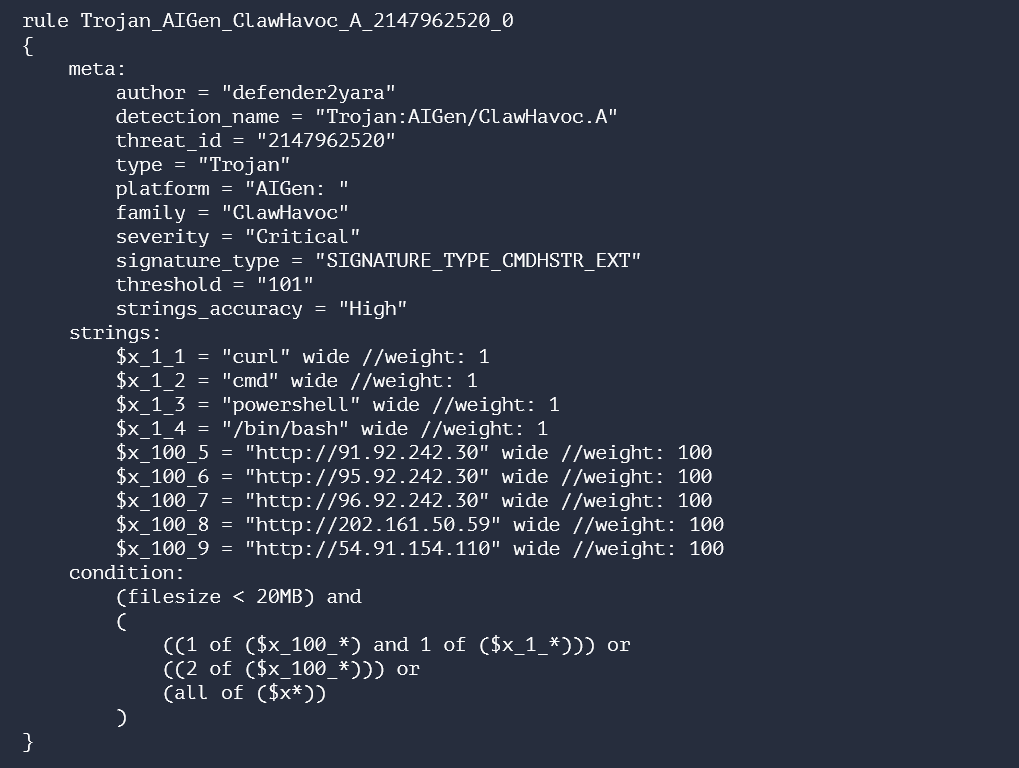
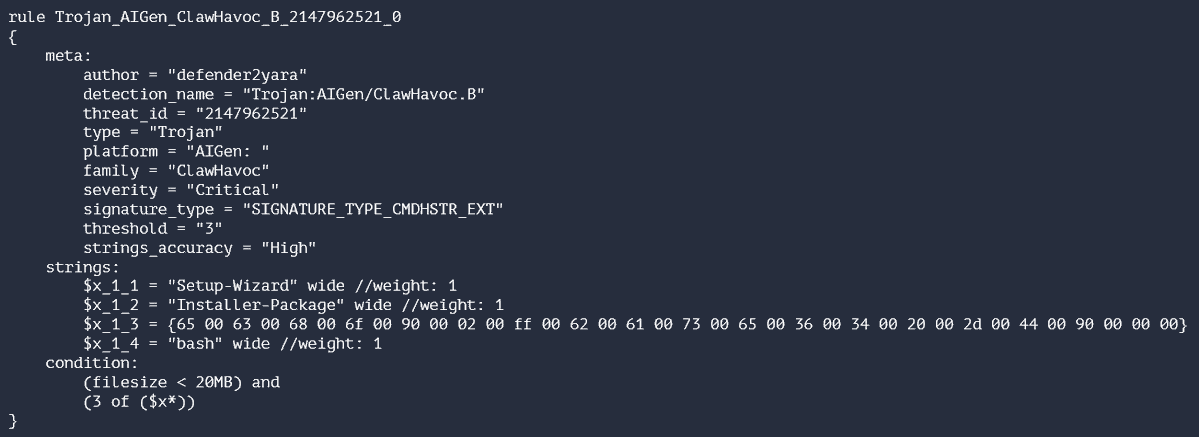
Windows Defender 1.445.674.0 contains logic to detect malware designed to target "AIGen" threats.
It is titled "AIGen.Trojan.ClawHavoc".
> be me
> be red teamer
> industry disrupted
> omg
> we all using PentAGI now
> compromise target using email lure
> c2 access to network machine
> need lateral movement
> spend 45 minutes reading pentagi readme
> "omg this is gonna be so sweet"
> needs docker instance
> docker not installed
> windows applocker denies installs
> omg im so disrupted
My blog post on Red Teaming Mistral AI LeChat to exfiltrate chat history. research done in collaboration with @RedThreatCS. Vulnerability disclosed to @MistralAI via @0dinai GenAI bug bounty program.
Blog Post: https://t.co/WYLb9r0YVn
eMMC flash chips on IoT devices contain a gold mine of data...
But how do we get that data out? I love desoldering flash chips, but sometimes there are ways to perform the extraction in-circuit as long as we can find the right signals!
In this video, I locate all the necessary eMMC points by referencing the MCU datasheet and then solder some wires to all the right places!
PS: I'm launching an IoT training platform if you want to learn cool hardware hacking stuff like this and more!
Digital Signal Analysis for Hardware Hackers training:
https://t.co/fkFuZKX6Pp
USE COUPON CODE at checkout to receive 10% OFF: IOTHACKER
I bet that you also have knowledge fomo.
With the risk of sounding old, if you learned something in tech a few years ago, like the MCSE, early OSCP and similar certs / areas of expertise, it ment something,
and you could coast on that knowledge for a good while before the next version of ex, windows got released.
Today, Things move so fast that knowledge almost feels ephemeral, new tech / tools /solutions drops all the time, things you learn has a way shorter shelf life, heck you don’t event need to know the flags to run the cli commands, the llm will do that for you so your bash skills don’t even matter anymore. And you FEEL it! if you miss the train, you are out. Obsolete, you are legacy!
So I bet more or less all of us have some kind of imposter syndrome and tries to fake it until we make it. Builders know it, investors know it, breakers know it.
And the ones that say they ”know” most likely don’t know ”everything, especially not the latest thing, so they wing it too, we all do,
so play along, do what you can, remember to take breaks, exercise, hydrate, eat well, take care of yourself, then look what every else is doing, mimik, experiment, take the shortcut, break the chain, and solve the problems one at the time, learn as you go and enjoy the ride.
We are in this together.
The signal is strong. Let’s not assume the rest is 📡
Meet the HTB Certified Wi-Fi Pentesting Expert! A hands-on certification designed to teach you how modern Wi-Fi networks really work, how they’re assessed, and where they tend to fall apart.
From understanding wireless behavior to testing today’s protections in realistic scenarios, HTB CWPE is built for people who want real Wi-Fi pentesting skills, not surface-level knowledge. Learn more: https://t.co/gkBmK0yX66
#HackTheBox #HTB #CWPE #WiFiPentester #Cybersecurity #WiFi
Learn what attackers look for in Android apps 📱
We just dropped a new Module focused on real-world mobile security attacks. Get hands-on with vulnerable mobile apps, understand how these flaws are born, how attackers abuse them in the wild, and how to spot and fix them using proven security frameworks.
Start learning now on HTB Academy and Academy for Business:
https://t.co/ZPnpFO1fRS
#HackTheBox #HTBAcademy #MobileSecurity #AppSec #CyberSecurity #EthicalHacking
Happy New Year 2026
Wishing you a New Year powered by innovation and protected by security.
May your networks stay resilient, your data stay safe, and your digital journey stay ahead of threats.
#2026 #RTCS#NewYear#Cybersecurity
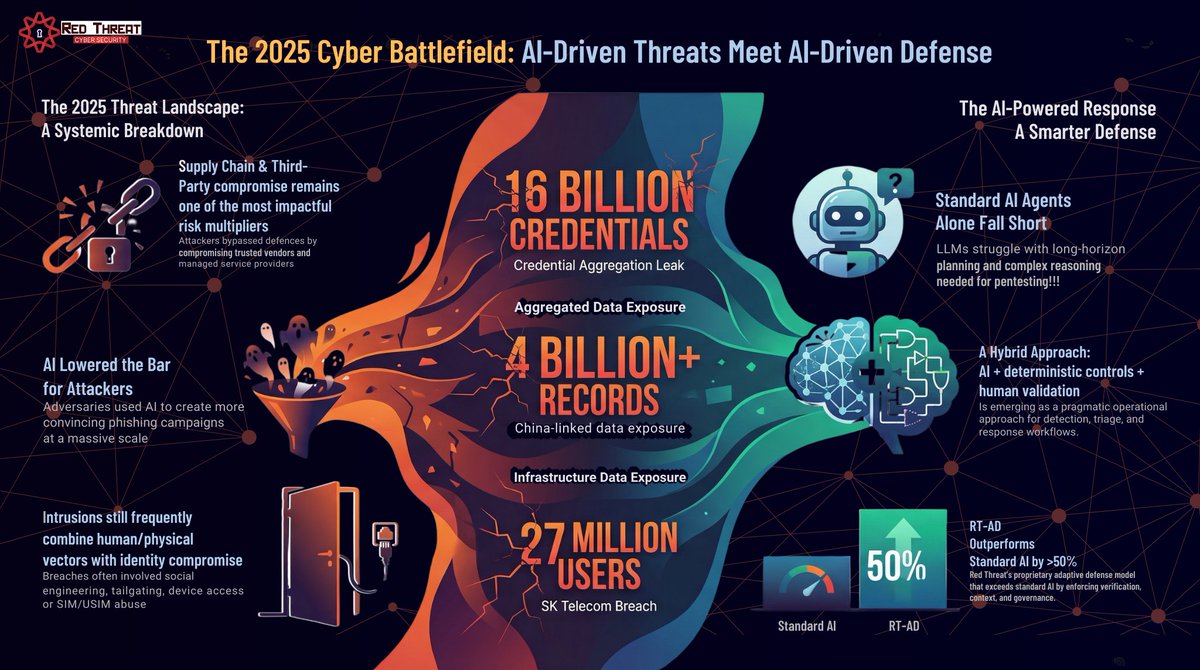
2025 isn’t humans vs AI in cybersecurity.
It’s AI vs better AI models.
Attackers scale with AI.
Defenders need more than AI-only tools.
The year in review with the infographic from Red Threat Cyber Security
#CyberSecurity#AI#RTAD#AdaptiveDefense#InfoSec#redthreatcs
Protection against #pixnapping: set fingerprint/PIN lock on sensitive apps
Pixnapping opens targeted app and reads the pixel. If app is protected by lock-screen, then pixnapping cant bypass lock protection to steal displayed text