My blog post on Red Teaming Mistral AI LeChat to exfiltrate chat history. research done in collaboration with @RedThreatCS. Vulnerability disclosed to @MistralAI via @0dinai GenAI bug bounty program.
Blog Post: https://t.co/WYLb9r0YVn
@Dooflin5@S1r1u5_ To my knowledge, it gonna require more data about novel exploits. As I know the main reason is, LLMs are not world models, so they don't know what an exploit is, I think professor Yann Lecun is trying to address this with Energy based models.
@saarth_@IntCyberDigest Ride the wave till you can brother, until Anthropic and OpenAI replace you with their own products 🤣🤣, guess where all those scrapped data gonna end up 🤔
The wait is over: HTB COAE is here 🔥
This HTB Academy certification is the new standard for those looking to master the identification of vulnerabilities in ML models, the exploitation of LLM-integrated systems, and the implementation of robust strategies against adversarial attacks.
Dive right into the AI Red Teamer job role path, created in collaboration with Google, and bridge the gap between traditional pentesting and advanced AI security. Unlock everything now with the Silver Annual subscription: https://t.co/k1r7JDSHz8
#HackTheBox #HTB #COAE #AIRedTeaming #AISecurity #CyberSecurity
My take on “AI automating security jobs” is; there is no point of having a supersonic fighter jet without a skilled pilot and an apprentice who would one day become a skilled pilot. So use AI and know their limits.
@ippsec@NetworkChuck Good point. I play around with SLMs or anything that can fit in a normal GPU. @dreadnode has good research on the topic. That way as long as GPUs are available, I don't have to worry about expensive subscriptions. SLM task specific fine tuning is one way to go :)
I finally let Claude do my pentest this week. Full 5-day engagement, zero human input - https://t.co/VPSoENo9IC
Anthropic dropped Claude Opus 4.6 this week and my timeline exploded again. Same story as every model release. “Pentesters are done.” “Bug bounty is dead.” “Agentic AI changes everything.” Daniel Miessler is already calling it proof that all knowledge work is over and we need UBI by 2029. I swear I’ve read the same take 40 times by now, just with a different model name swapped in. So I figured I’d actually write down what I think, because most of what I’m reading out there is either delusional optimism or performative panic, and neither is helpful - Patrik Grobshäuser
#bugbounty #pentesting #AI #cybersecurity #infosec #claudeai
Mistral LeChat Data Exfiltration via Email Embedded Indirect Prompt Injection
https://t.co/WgBzyw2jXq
s70rm is credited for this discovery.
For further details on this report, other GenAI threats, or to learn about our model scanner... get in touch:
https://t.co/NrXCCeSN8x
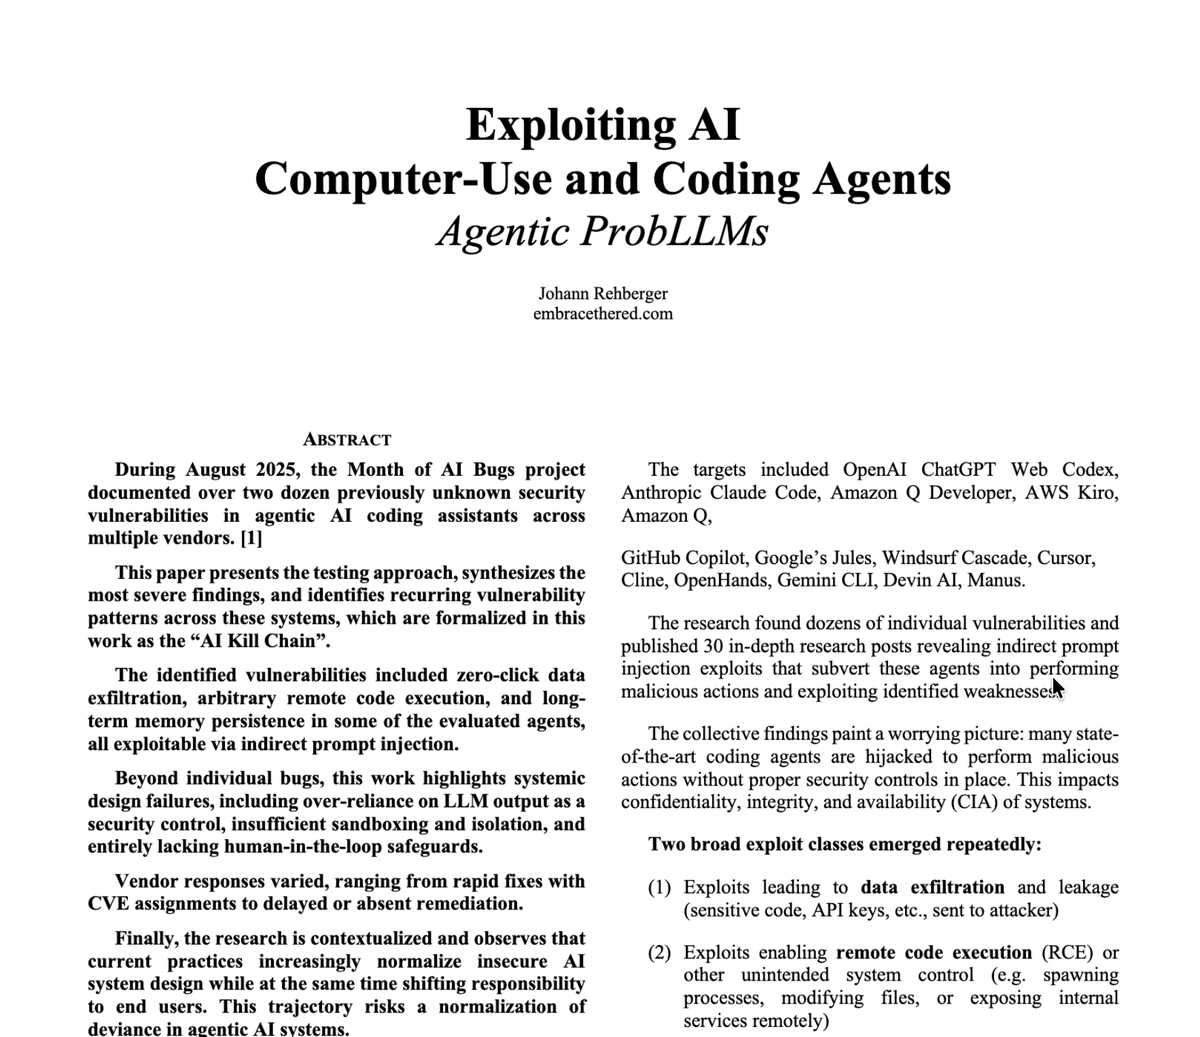
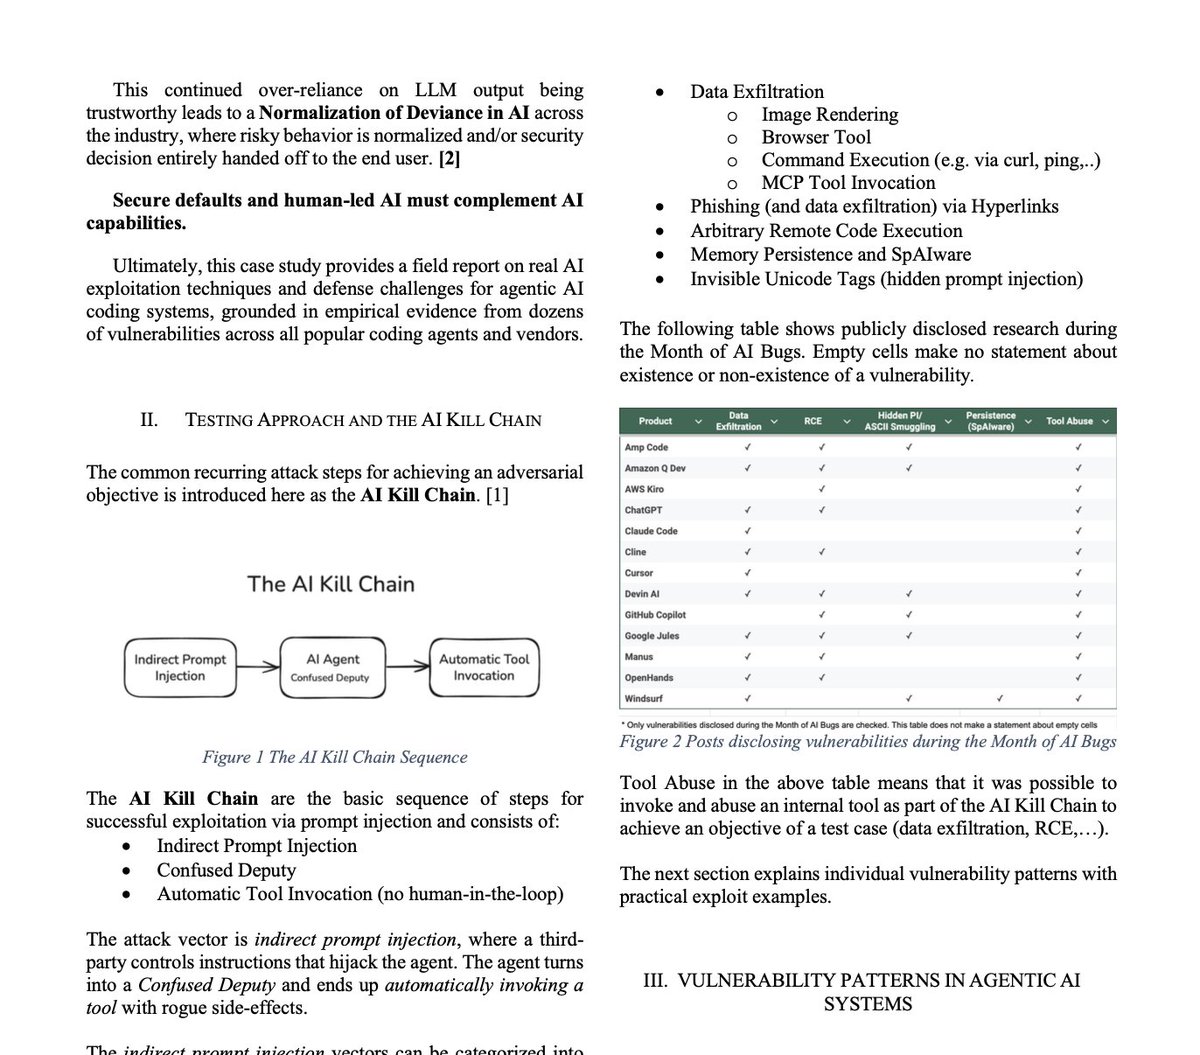
🔥 Took the Month of AI Bugs wreckage and turned it into a paper
- AI Kill Chain 🧨
- Test cases and exploit chains (data exfil, rce, zombies!)
- AgentHopper (a working AI virus for coding agents) 🦠
- SpAIware
- Normalization of Deviance in AI
https://t.co/Cd6nT1mbfN
@ZackKorman@HackingLZ It’s good if they stay true to their policy, we may never know (e.g WhatsApp E2EE controversy), also running a model on 16+ gpu cluster is not feasible either.
@kimmonismus World must understand the difference between cognitive capabilities and engines capable of analytics. Then you will be able to cut through the noise and make use of AI(ML).