You ever just blindly import a rule and turn it on in the SIEM? Be honest, we've all done it. In the next release of @reflexsoar we automatically assess the rules hit volume, query speed and tuning options before the rule is even turned on.
What are detection repositories? Reflex will soon support sharing detections via repos, some native, some custom. New detections are automatically baselined for slowness, high volume, etc. #reflexsoar#soar#secops#infosec
We've been quiet, by design. We've been hard at working putting the finishing touches on our next release. Internally we are excited for what is coming and know you will be too when you see it. It's worth the wait.
It's been awhile. ReflexSOAR is still alive and kicking, we are repositioning the project so that we can dedicate resources to it full time and bring it to the next level. Your support and patience is appreciated. A new release is coming with enhancements, features and bug fixes
Wouldn't it be nice if you could just paste the Sigma rule into your detection engine? We got you, ReflexSOAR will convert it for you! We promise Detections are coming soon!
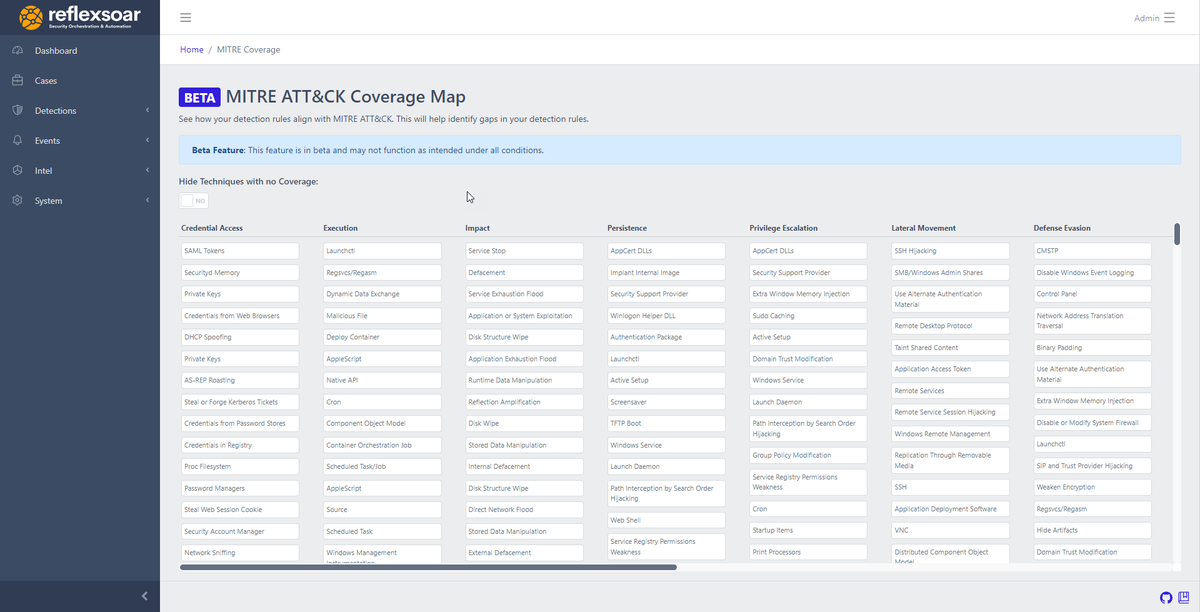
The next release is almost ready, we are finishing off notifications channels to Teams, Slack, Email as well as polishing up our MITRE ATT&CK coverage map for our built-in detections rules (preview below)
Teasing a Beta feature available with Detections launch. Select the MITRE ATT&CK Tactics/Techniques when setting up a Detection, Reflex will map it to MITRE for you! Check your MITRE ATT&CK coverage easily from within Reflex, and see details on the Technique
Next release may be delayed a bit as we add a desired feature. Notification Channels will allow Event Rules/Case activity to msg your teams via Teams, Slack, Email, PagerDuty, etc. MSSPs can alert directly to their customers to shorten feedback time. #soc#soar#reflexsoar
Started early testing of Detections in ReflexSOAR. Reflex Agents will act as detectors so you can scale as needed and get to alarm sources in hard to reach environments. Also some other enhancements, bug fixes and micro features coming, a new dashboard and more!
Even more changes to Event Rules in the next release (coming soon). We have introduced a feature so rules can check if IP values are in a list of CIDR ranges in an Intel List. Allowing updates to many rules at once by updating the Intel List. #soc#infosec#soar
We are adding Event Rule priority in our next release somyou can chain Event Rules in a specific order and use the results of one Rule to impact another rule. Hopefully this extends Event Rule usefulness as we brainstorm our automation plans!
@Am6Vue2 Can you please open an issue on https://t.co/6g03OQnhH2 . This way we can share some screenshots and other troubleshooting information and help get you fixed.
@Am6Vue2 If you used our install script the default credentials for the UI would be [email protected] and a randomly generated password that is output during install time. If you chose to go docker compose on your own the default is [email protected]/reflex
Teasing a new feature we are working on...Detection Rules directly in @reflexsoar! Let us know what you like or dislike about your current alerting platform. Stay tuned! #reflexsoar#soc#infosec#soar
We've been live for a month and are continuing to work on our next feature; an Alert engine. If you could pick, what would you wish your alert engine did that it doesn't do today? Stay tuned for a preview of Detections #reflexsoar#soc#soar#infosec