a big quantum computer could break the key every solana wallet uses today...
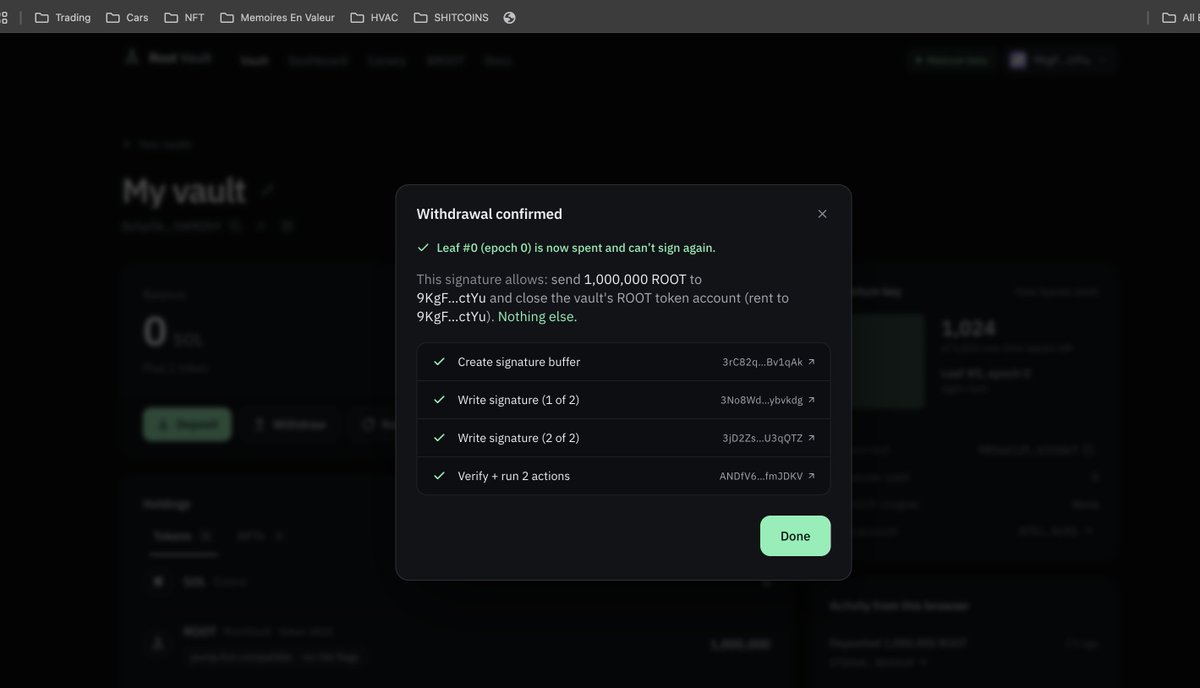
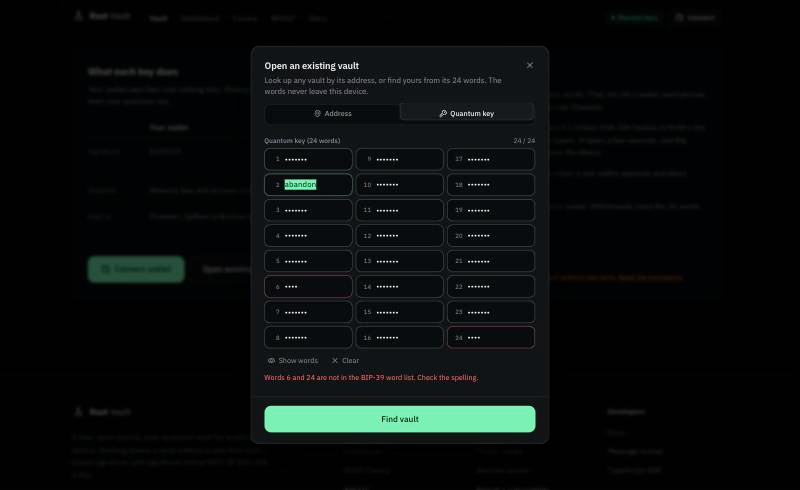
so we built root vault: deposit SOL, tokens or NFTs, and nothing leaves without a one-time hash-based signature that says exactly what happens.
free and open source. https://t.co/Jhd4L93cZS
AYuNTGHHYzmH6LgwveNVc9TZFmPVZKUsM4k5tPqEpump
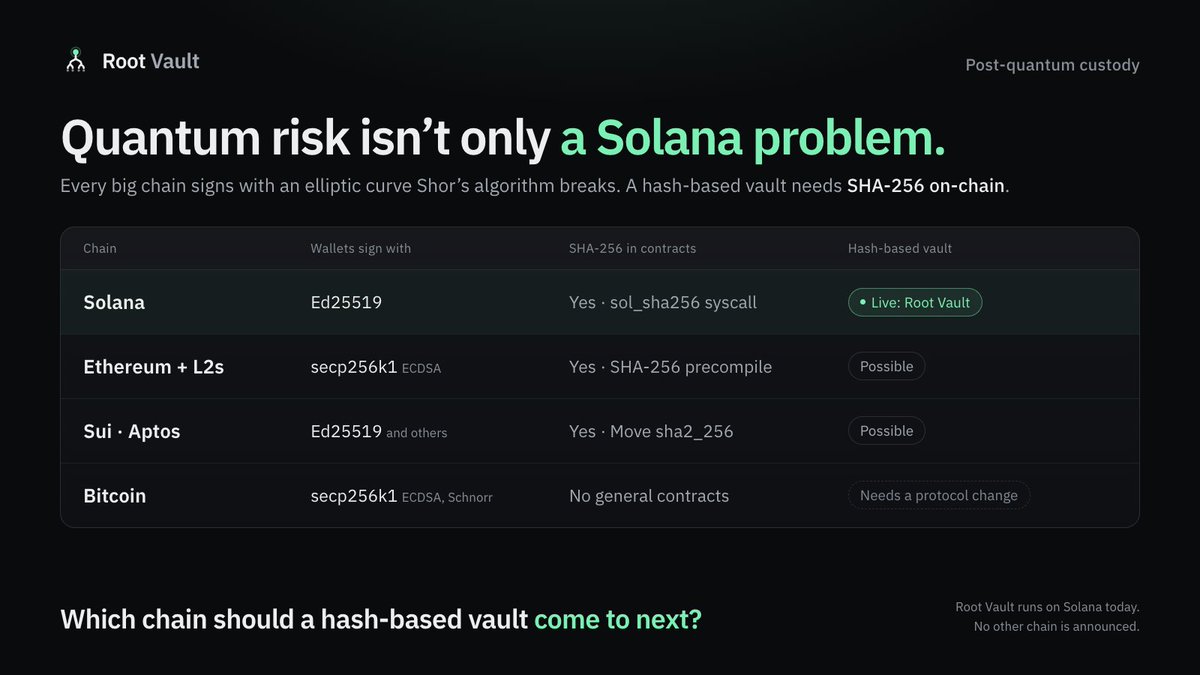
quantum risk isn't only a solana problem.
every big chain signs with an elliptic curve. a hash-based vault only needs SHA-256 on-chain, and most smart contract chains have it.
root vault runs on @solana today. which chain should be next? (bitcoin not possible)😂
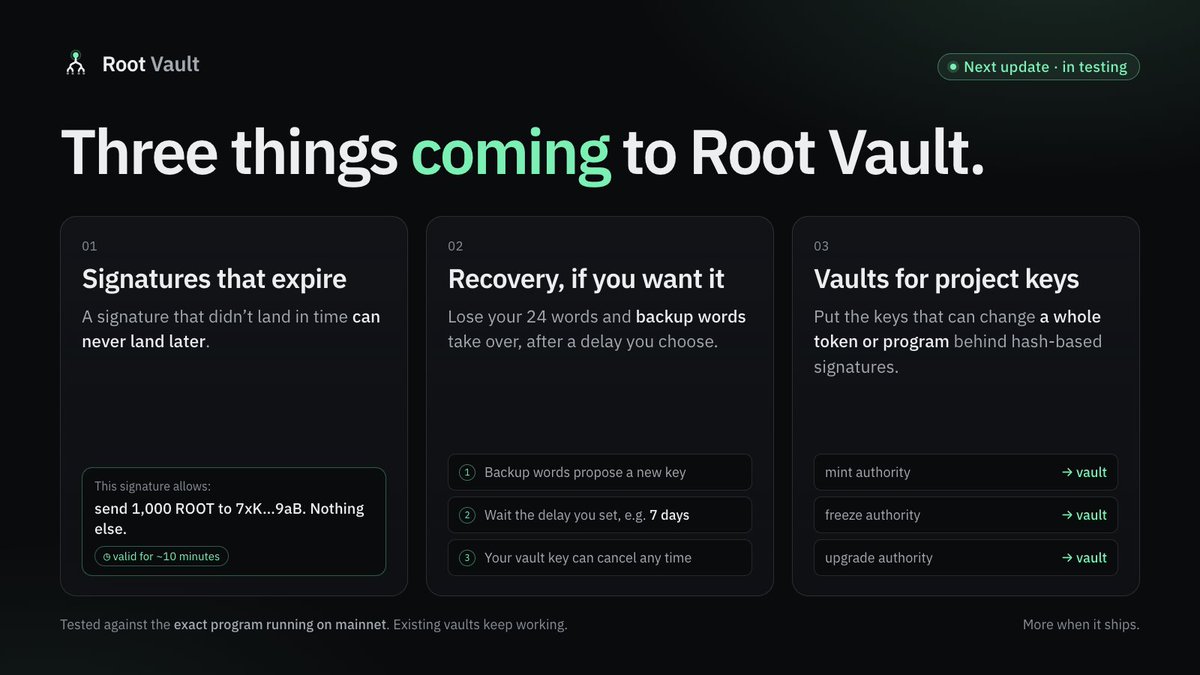
next root vault update is in testing.
signatures that expire. recovery if you lose your words. vaults for the keys that control whole tokens and programs.
existing vaults keep working. more when it ships.
We are submitting Root and its protocol to the Solana Foundation for approval and Audit. One step closer to bring Root level security to participating Solana wallets by default.
https://t.co/dq6VN437sC
If quantum computing is generalizable and scalable enough to break Satoshi’s stash then we are entering an Information Age that’s equivalent to a level 2 kardeshev civ.
NSA is taking proactive steps to protect national security systems from quantum computing threats. Key initiatives include the launch of the Post-Quantum Cryptography Resources Hub, collaboration on standards and guidelines, raising awareness and education, and partnering with industry and academia. Learn more: https://t.co/ogBE3SHPzY
@elonmusk Quantum computing will challenge how crypto wallets stay secure. ROOT is building for that future: a Solana vault using hash-based signatures designed to resist quantum attacks and keep withdrawals under your control. Open source. No token required. https://t.co/SCZkZMSoZ3
post-quantum signatures aren't one thing.
lattice schemes like ML-DSA and Falcon: compact, fast, newer math.
hash-based schemes like SLH-DSA and LMS: bigger, but they rest only on the hash function.
ed25519 for comparison: 64 bytes, and broken by shor.
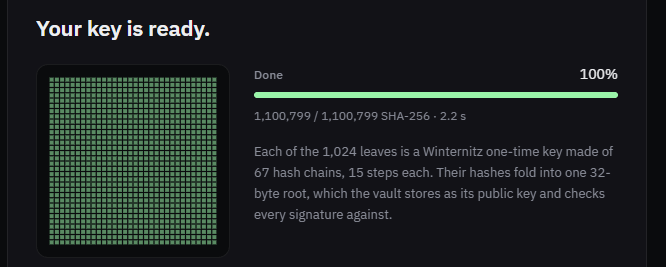
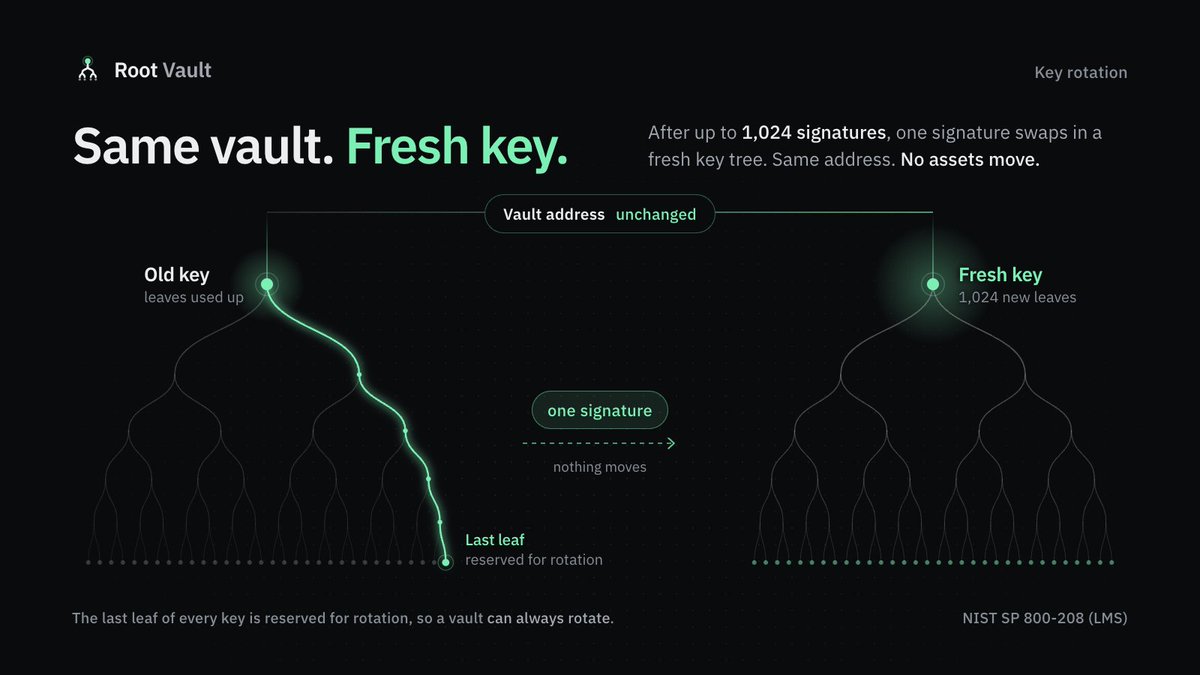
one-time keys run out. a key tree with 1,024 leaves can sign 1,024 times.
the fix is rotation: one signature points the account at a fresh key tree. the address stays the same, nothing has to move, and the last leaf is kept back so rotation is always possible.