Found a Mid–High risk in UmaCtfAdapter on Polygon:
"abi.encodePacked(...) collision pattern"
Contract: 0x65070BE91477460D8A7AeEb94ef92fe056C2f2A7
Different inputs can produce the same hash and potentially bypass auth/message validation.
Tiny bug, huge impact.
#Web3Security
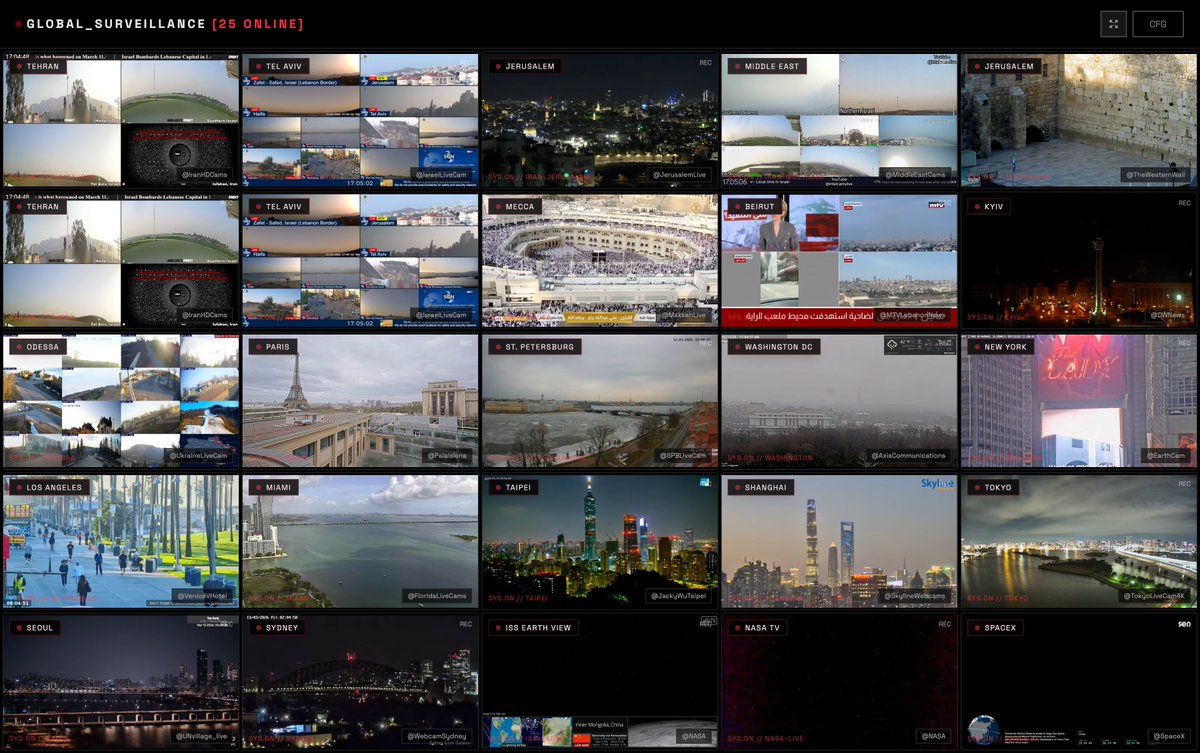
A global surveillance-style dashboard watching cities across the world in real time.
Think SOC, but for the physical world.
This is the kind of experience I’m building with @rsch_io Operations.
Signals everywhere. One pane of glass.
#OSINT#Security#SecurityOperationsCenter
In my assessment, this appears to be a fraudulent project. A project called ‘LiquiCore’ that raises multiple red flags and inconsistencies.
See my breakdown below.
#ScamAlert#Cryptocurrency#Airdrop
Recommendation for @vana@v_on_vana: add authentication, restrict access to the code owner, enable logging, and apply rate limiting. These fixes are essential to restore trust and protect contributors.
Observed case: someone used another wallet’s invite code without completing registration. The system still counted it, causing the real contributor to lose recognition while the exploiter gained advantage.