MSTICPy 2.7.0 release
- 2 new threat intel providers for CrowdSec and AbuseIPDB
- New MS Sentinel and Kusto drivers now the defaults
- Query file editor for MSTICPy template queries
- Azure auth fixes for MicrosoftSentinel
More details https://t.co/M8Tn0QuC8f
@olafhartong@Cyb3rMonk@falconforceteam@gijs_h Is there any way to automatically deploy uses-cases stored in a git repository to Microsoft Defender 365? I know that it os possible to sentinel. Amazing Job!
MSTICPy release 2.3.1
- Hide progress bar with TILookup
- init_notebook works offline or in air-gapped env
- some important Azure/Sentinel/AzureML fixes
Now on PyPI https://t.co/OHDnrkTl66
Read the goodness in the rel notes: https://t.co/Y2OHFHxDu1
#msticpy#CyberSec#Jupyter
No hace mucho participé en unos ejercicios en los cuales el equipo de pentesting volcaba la SAM y LSA Secrets de forma remota. Me lo apunté en el TODO con la idea de ver como funcionan dichas técnicas.
#threathunting#Ciberseguridad
https://t.co/9FPn79HiAZ
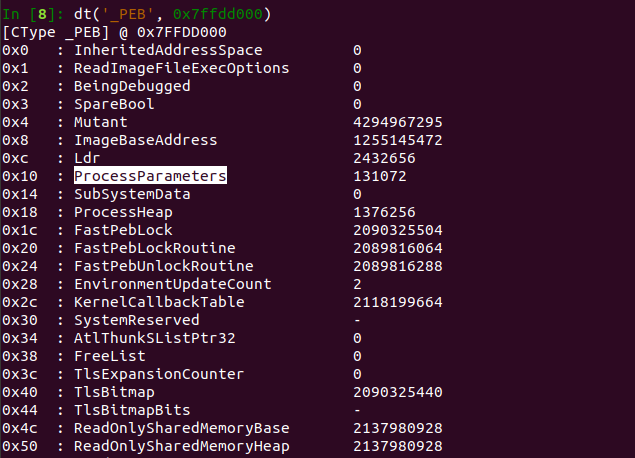
1\ How to detect what command line spawned a process with no EDR/AV? 👀 #DFIR
If you have a memory sample, this is how you can figure out what cmd spawned the processes by using volshell and memory forensics.
STEP BY STEP GUIDE BELOW
👇 👇 👇 👇
#MemoryForensics
Malware threats have used well-known Windows APIs, which are used for encoding and decoding pointers, so protecting itself against potential hooking.
#malware#reversing#windows#programming
SilentLsassDump - A new #CobaltStrike Beacon Object Files (BOF) to dump the LSASS process via the Silent Process Exit mechanism using direct syscall generated with @Outflanknl's InlineWhispers
👉 https://t.co/I7eMoxTg4Z
Sources : https://t.co/g44tf49bgF
I found a new #lolbin for downloading arbitrary files
`C:\Windows\System32\IME\SHARED\IMEWDBLD.exe <URL>`
Find the downloaded file in `%LocalAppData%\Microsoft\Windows\INetCache\<8_RANDOM_ALNUM_CHARS>/<FILENAME>[1].<EXTENSION>`
#IMEWDBLD#lolbas#InputMethodEditor
Added another KQL query to identify Exchange servers using Defender for Endpoint TVM inventory data. https://t.co/tSijPcrLY3 # #HAFNIUM#DefenderforEndpoint
Starting anomaly detection for threat hunting can be frustrating. Users do strange things on their systems. Whatever you can imagine, reality is much worse.
We are glad to publish our review of one of the biggest and most interesting malware operations in existence.
How does it work? Who is behind it? Read all about it.
https://t.co/kr298aadHI
Wanna disable Defender when enabled Isolated Core and Tamper protection?
Its a bit more trouble- but doable, without ruining Isolated Core/Secureboot etc.
Defenders process will run as a unkillable protected service- so new tricks needed.
Here we go: