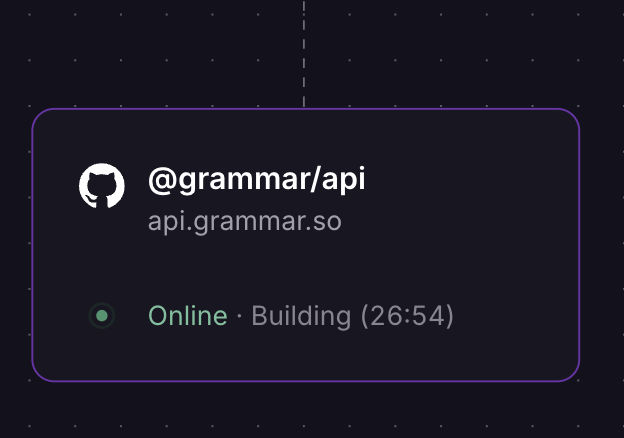
Sadly I am going away from Railway, is really a shame because I love their UI but one day without deploys is not exactly what I expect from a Service that a couple of my systems depend on.
Node.js Security Advisory: a high-severity RCE flaw in Node's Brotli decoder affects Node.js 22, 24, and 26.
Vercel WAF rules are live for every project and block known exploit patterns.
https://t.co/JtfEshHnOC
🚨 BREAKING: PHP is warning admins to prepare for emergency security updates tomorrow to fix two critical vulnerabilities rated CVSS 9.2.
However, security researchers at @watchtowrcyber rate the flaws CVSS 10.0 and say they are RCE vulnerabilities affecting PHP 5 through 8.
Information about the vulnerabilities has reportedly leaked ahead of disclosure.
No known exploitation in the wild.
🔗 https://t.co/ZkCeLGaiAc
https://t.co/ZkCeLGaiAc
@serious_mehta Yeah, I usually save context in https://t.co/gzznk89xGS using the MCP, then I just ask the agent to go and look for the context we need for the feature