Two critical PHP vulnerabilities have a fix scheduled for today.
CVE-2026-109618 and CVE-2026-109619 are both rated CVSS 9.2 and allow remote code execution without authentication on default PHP installs. Details leaked before the fix, so exploits are already in the wild. PHP has scheduled the patches for 14:00 UTC.
Here's where things stand for RunCloud users:
- We've disabled session.upload_progress on all servers as a temporary mitigation. It closes the known attack route until official fixes land. Uploads still work; the only side effect is that PHP-based upload progress bars may stop updating.
- Once PHP publishes the fixes, patches will be applied automatically to PHP 8.2 and newer. Timing depends on your stack (native, Docker, OpenLiteSpeed/LiteSpeed Enterprise), and we'll post updates as each one ships.
⚠️ If you run PHP 8.1 or older, switch your web apps to 8.2+ now. Those versions are end-of-life and won't receive an official fix. The mitigation stays active on them, but it's no substitute for upgrading.
Optional: We've released two NGINX templates that block or rate-limit multipart requests before they reach PHP. Pick the one that fits your site.
Full details, WordPress-specific guidance, and live patch status for every stack:
https://t.co/jEy4a7zTCO
Hi Ailvess, thank you for your patience. We are doing our best to support people 1:1 in support. We've added a notice to our status page regarding ongoing work for our dashboard and API that is affecting performance. In most cases, dashboard access is being restored as we speak. If you still have any issues with accessing the dashboard, please reach out to us by opening a ticket or emailing [email protected] from the email address associated with your account. We'll be able to provide the best possible support in this way.
Hi Jonathan, please reach out to support by opening a ticket, either in your dashboard or by emailing [email protected] from the email address associated with your account. We'll be able to provide the best possible support in this way, as the support team can see exactly which servers you have in your account and their server stack (Native, Containerized, etc.). Thank you.
@jb510@bradt@spinupwp Fair frustration, Jon. With the fix public, the exploit is easy to rebuild, so we took the panel offline to patch it before anyone could use that against it.
Your servers and sites keep running. Only the dashboard is down. We’ll be back shortly.
Everyone’s adding AI to everything.
We shipped a caching plugin. 😅
Meet RunCache 🚀
Make WordPress faster and reduce server load with full-page caching, Redis object caching, and edge caching.
Built for RunCloud. Now open source, making server-side caching more accessible without the usual complexity.
50k+ apps already using it.
No AI. Just caching. Doing caching things.
https://t.co/7P32czYGlF
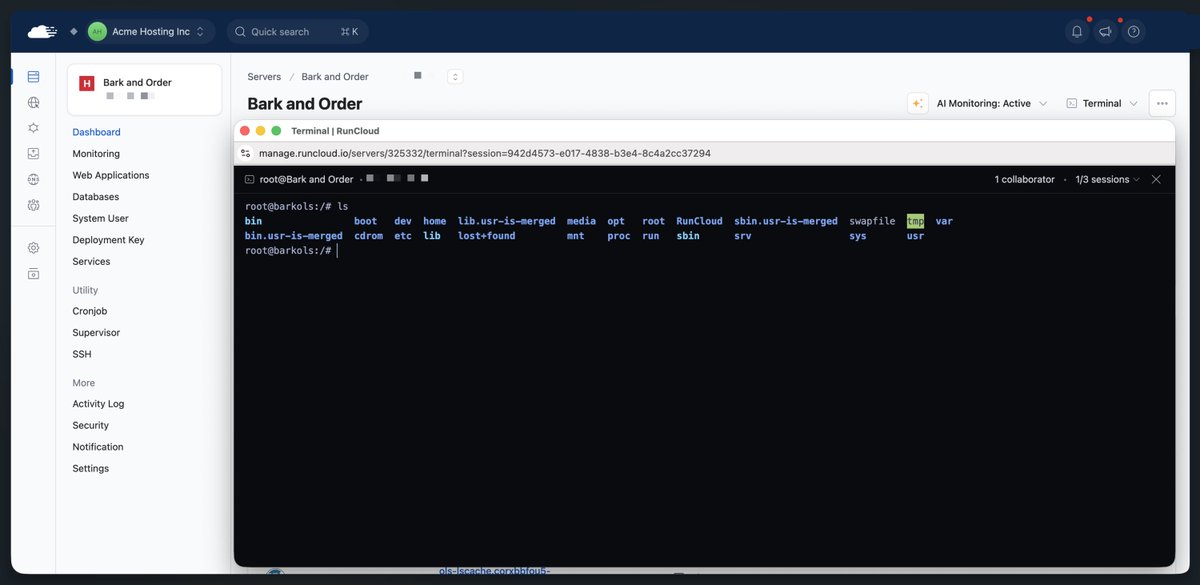
🆕 Introducing Web Terminal: Access Your Server Shell in the Browser
𝗡𝗼𝘁𝗲: Web Terminal is off by default. Workspace owners can enable it with an 8-digit code sent via email, and each session requires a new 2FA challenge.
Learn more & get started: https://t.co/NlXokXSW1n
🆕 We rebuilt the RunCloud Web Server Log UI.
No more walls of raw text. You now get:
• A structured, searchable table
• An interactive timeline with click-to-jump
• Filter by IP, path, status code, or HTTP method
• One-click copy & download
https://t.co/PbfXawewww
🆕 𝗟𝗶𝘁𝗲𝗦𝗽𝗲𝗲𝗱 𝗘𝗻𝘁𝗲𝗿𝗽𝗿𝗶𝘀𝗲 𝗦𝘂𝗽𝗽𝗼𝗿𝘁 𝗶𝘀 𝗡𝗼𝘄 𝗶𝗻 𝗕𝗲𝘁𝗮
LiteSpeed Enterprise is now available as a beta as the third web server stack alongside NGINX and OpenLiteSpeed.
If you've been waiting for LSCache, built-in WAF, https://t.co/0Oi552lpLA, and better performance under load with the convenience of RunCloud server management, this one's for you.
Deploy a new server with LiteSpeed Web Server, bring your own license, and manage everything from your RunCloud dashboard.
Learn more: https://t.co/ru3FznoIv4
🆕 𝗥𝘂𝗻𝗖𝗹𝗼𝘂𝗱 𝗔𝗜 𝗠𝗼𝗻𝗶𝘁𝗼𝗿𝗶𝗻𝗴 𝗶𝘀 𝗵𝗲𝗿𝗲 (𝗕𝗲𝘁𝗮)
RunCloud AI Monitoring continuously analyzes your server to detect anomalies and their severity, diagnose root causes, and surface remediation steps you can act on immediately.
Think of it as having an L3 sysadmin watching your server around the clock. When something goes wrong, you get a full diagnosis of what's happening, why, and the exact steps to fix it.
How it works:
- Read-only by design. It observes and advises. It never runs commands or makes changes automatically.
- You stay in control. Any suggested commands and next steps are for you to review and run manually.
- AI isn't perfect. Recommendations may be incomplete or incorrect. Always verify before making changes.
To enable it, head to any Server in your dashboard, and you'll find a new "Install RunCloud AI" option.
Learn more: https://t.co/beiItfMctg
𝗡𝗼𝘁𝗲: This is a beta, so we want your feedback. If you try it and spot something off (a diagnosis that missed the mark, a remediation step that didn't work, a use case we should cover), let us know. We look forward to any & all feedback.
🆕 🎉 RunCache is Now in Beta
Full-page, object, and edge caching for WordPress in one plugin. WooCommerce-ready, Cloudflare edge caching built in, works with Apache and NGINX, and more.
𝗡𝗼𝘁𝗲: To get started, ensure your server is running RunCloud Agent 2.17.10 (or later).
From there, navigate to your web application(s) of choice and to the Performance (Beta) tab or, if you already have RunCloud Hub installed, to the RunCloud Hub tab, where you will be prompted to upgrade eligible web applications.
23 looks good on WordPress. 🎂
Since May 27, 2003, WordPress has been blogging, building, publishing, shipping, translating, theming, plugin-ing, and making the web a little more wonderfully weird.
Happy birthday, WordPress. 💙
🆕 The RunCloud File Manager now supports file uploads, bulk actions, and more.
You can now upload files directly to your servers from the File Manager in your RunCloud dashboard. 🎉
𝗡𝗼𝘁𝗲: Requires agent version 2.17.0 or above.
See it in action: https://t.co/vo5Gy9q54A
Read the docs: https://t.co/1hpWmJ9fG2
⚠️ "Copy Fail" Linux Kernel Vulnerability: CVE-2026-31431
A critical Linux kernel vulnerability was publicly disclosed on April 29.
It affects every major Linux distribution (including Ubuntu 24.04, 22.04, and 20.04), and allows any user with shell access to gain full root access.
We've already pushed an interim fix to servers via the RunCloud agent where possible.
For verification steps and instructions on manually applying the interim fix, here's the full write-up on our community forum:
https://t.co/d9chQt2rKE
https://t.co/d9chQt2rKE
New RunCache… the team at RunCloud is preparing to launch RunCache plugin, which combines full-page, object, and edge caching in one seamless caching solution. With one dashboard and one configuration... https://t.co/9WvkStPBkz
via WPWeekly_284 @runcloud