MAD Bugs: Claude Wrote a Full FreeBSD Remote Kernel RCE with Root Shell (CVE-2026-4747)
To our knowledge, this is the first remote kernel exploit both discovered and exploited by an AI.
https://t.co/Cv8M69i1Mk
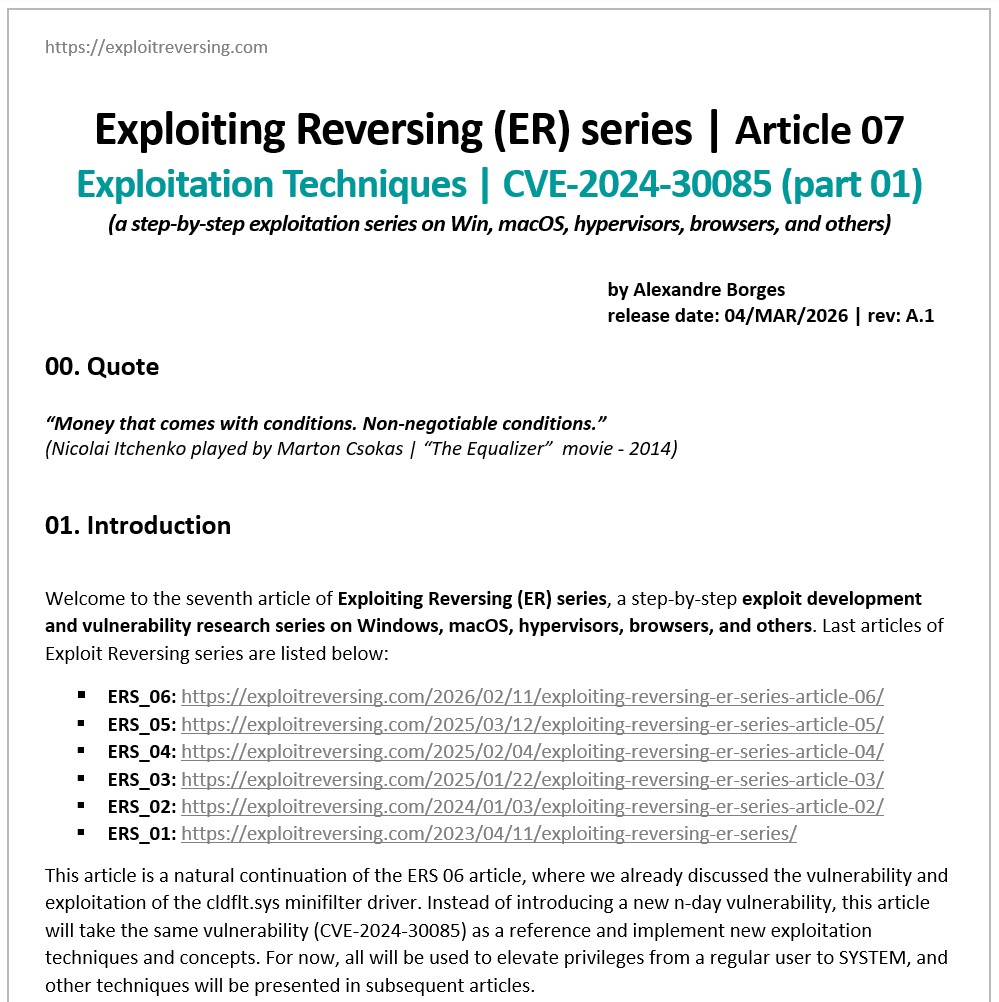
I am excited to release the seventh article in the Exploiting Reversing Series (ERS). Titled “Exploitation Techniques | CVE-2024-30085 (part 01)” this 119-page technical guide offers a comprehensive roadmap for vulnerability exploitation:
https://t.co/h18hZC0azl
Key features of this edition:
[+] Dual Exploit Strategies: Two distinct exploit versions using Token Stealing and I/O Ring techniques.
[+] Exploit ALPC + PreviousMode Flip + Token Stealing: elevation of privilege of a regular user to SYSTEM.
[+] Exploit ALPC + Pipes + I/O Ring: elevation of privilege of a regular user to SYSTEM.
[+] Solid Reliability: Two complete working and stable exploits, including an improved cleanup stage.
[+] Optimized Exploit Logic: Significant refinements to the codebase and technical execution for better stability and predictability.
The article guides you through the two distinct techniques for exploiting the CVE-2024-30085 Heap Buffer Overflow vulnerability.
I would like to thank Ilfak Guilfanov (@ilfak on X) and Hex-Rays SA (@HexRaysSA on X) for their constant and uninterrupted support, which has helped me write these articles over time.
I hope this serves as a definitive resource for your research. If you find it helpful, please feel free to share it or reach out with your feedback!
Enjoy your reading and have an excellent day.
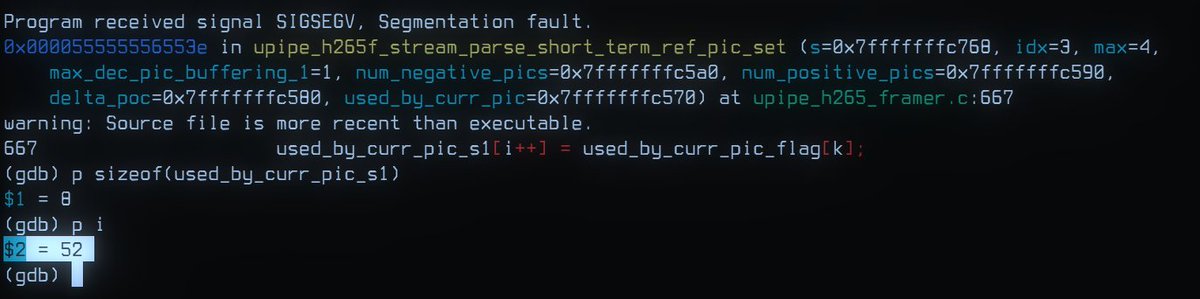
@FFmpeg So now we have read/write stack-based buffer overflow. Game over.
Fuzzer and complete explanation can be found on my github:
https://t.co/7m0i6Dmvud
Multiple, serious security vulnerabilities found in the Rust clone of Sudo — which shipped with Ubuntu 25.10 (the most recent release).
Not little vulnerabilities: We’re talking about the disclosure of passwords and total bypassing of authentication.
In fact, we’re getting new reports of showstopper grade issues every few days on the Rust-based clones (like sudo, du, date, and others) which were forced to ship in Ubuntu before they were fully tested.
Which is, of course, *exactly* what was predicted.
But, never fear! At least these Rust clones are memory safe!
PHEW!
Exploits for Unix variants with significant historical value and may still exist in specialized environments such as scientific computing facilities, ICS, and legacy envs. Coverage includes Cray UNICOS, SGI IRIX, Solaris, HP-UX, and SCO Unix systems. https://t.co/9CIR7y2RN2
From lab to fab: China's quantum cryptography tech leaps to global forefront despite a tech blockade. Witness home-grown innovations from satellite first to phone-sized chips. #InnovateChina
It took 3 years but finally I feel ready to release my Pwn2Own 2021 exploit code. 💖 Video talk covers my full research workflow, from attack surface modeling and reverse engineering, to vulnerability discovery and systematic exploit engineering, enjoy! #Pwn2Own
The new Rowhammer attack paper against SK Hynix DDR5 modules is very impressive! LPE to root in over 100 seconds, or disclosing RSA keys for SSH from adjacent VM, among other vectors. If the SK Hynix brand doesn't ring a bell, some models of ADATA, G.SKILL, Corsair, Dell, Lenovo and even some Cisco OEM modules are based on Hynix chips. Finding exact list of affected OEM vendors and module modules is a bit tricky.
As part of the research effort Google has also partnered with Antmicro to build dedicated Rowhammer testing rig, which is also open-source!
https://t.co/gfZ7YWvjvg
Paper:
https://t.co/noTsqaajD7
Google blog:
https://t.co/SQu3lydVEs
PoC:
https://t.co/uymJNXwoRb