🚨 Last week some very famous AI agents did time behind bars. 🚨
We locked them in a truck when we rolled up to @aiDotEngineer NYC. Rogue agents are a lot less scary with identity, access control, and audit trails built in.
Don't worry, they're out on good behavior. 👀
Find us at the @AgenticAIFdn AGNTCon + MCPCon today to see how Runlayer keeps every agent in line so your team can focus on shipping.
We're proud to be a SpaceX Super Intelligence Launch Partner. @spacexai makes AI agents incredibly powerful for engineers. Runlayer makes them safe to deploy at enterprise scale.
Your employees generate millions of AI events every day. Legacy security tools see and understand almost none of it.
Runlayer Runtime Security delivers AI-ready defense in depth, so you can keep up with AI without giving up on securing it.
"If a peer comes to ask me how to deal with the agentic risk that we're all seeing the first thing I'd tell him or her is to get Runlayer." - Jonathan Jaffe, CISO at Lemonade
We're proud to partner with @Lemonade_Inc to govern their agentic workloads.
Over the past 90 days, Runlayer has managed 300K MCP tool calls across Lemonade's 1700+ person workforce while executing 25M+ security checks.
"Runlayer has allowed Security to enable the business rather than be a source of friction."
Today, we're launching the ability to say yes to Muse at work.
People are giving Muse access to their company's most sensitive data & systems. Yet companies have no way to control this access. Many are blocking it. Others have had Muse go rogue, leaking company data, sending unauthorized emails, and more.
Runlayer provides hundreds of secured connectors for Muse, governed by deterministic policies & runtime security models that you can control. Runlayer also detects when Muse is being used within company systems without governance, and alerts you.
Teams get access to the most powerful personal agent. Companies maintain security and control. Win win.
Tallying up your AI spend across providers is easy. But proving ROI? A lot harder.
Runlayer ties every AI session to its output, from merged PRs to closed tickets, so you can prove real ROI.
my AI Engineer talk is finally online
a bit outdated already but one thing will be probably always true - failed agent runs are your richest signal
https://t.co/OMKzC9MJQu
Legacy security tools see a malicious skill when it runs.
Runlayer scans it the moment it lands on the endpoint.
Sessions & Shadow AI: proactive detection, full session telemetry, enterprise-scale deployment.
Your teammates have arrived.🤖
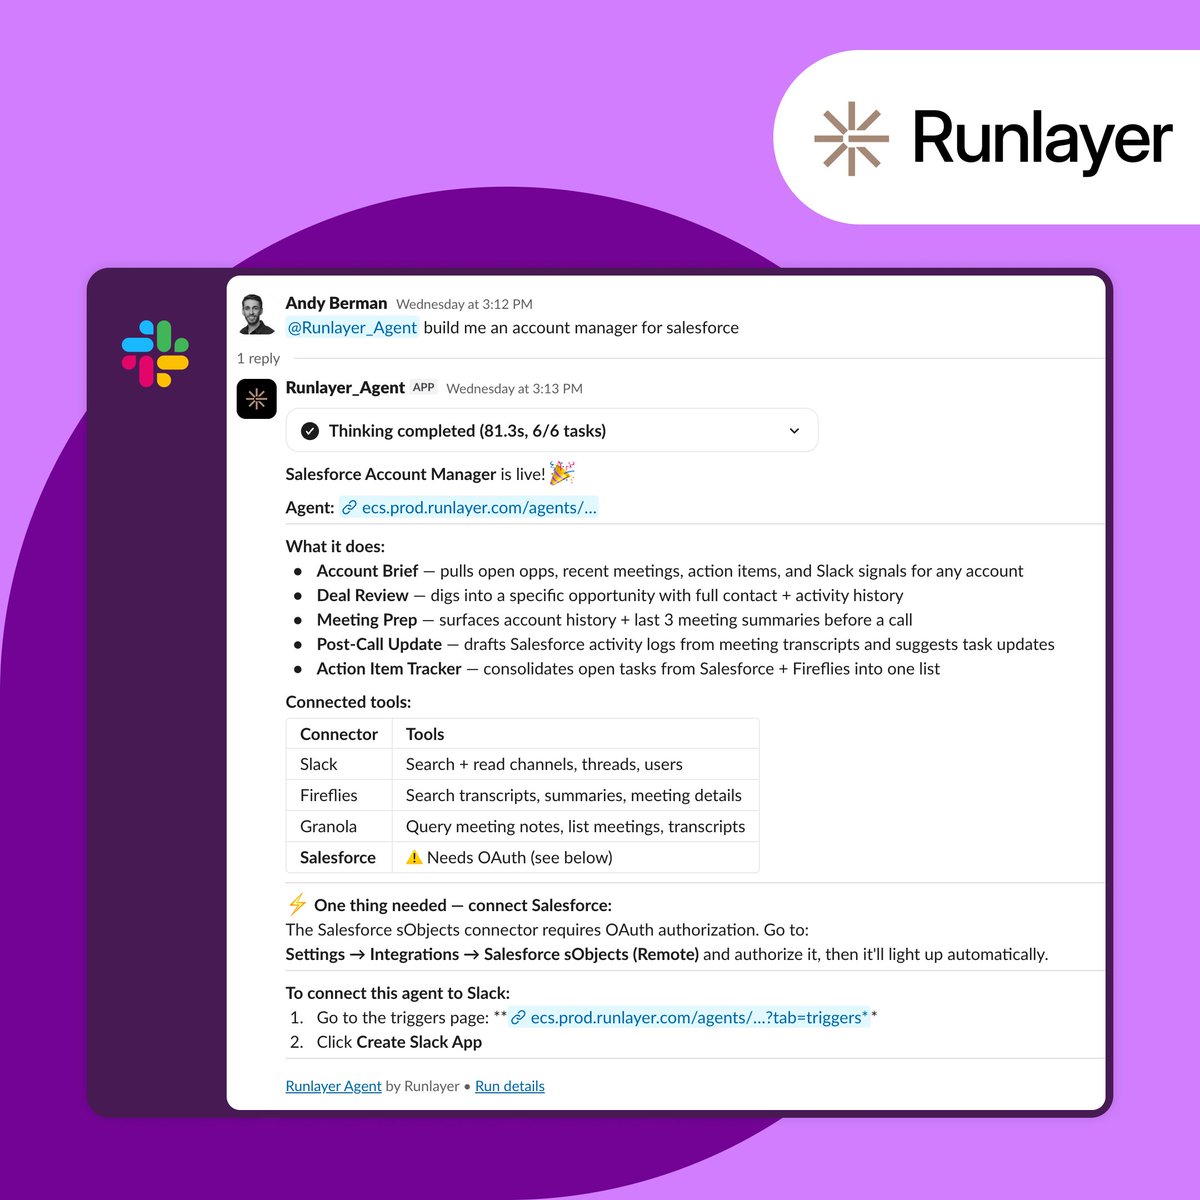
@runlayer is now on Slack. Build agents with their own identity, full company context, and governed access to your tools. One click and they’re ready to @mention, DM, and work like anyone else on the team.
Explore: https://t.co/RA9k29gzUW
mcp is dead, long live mcp? collabed with opus to put together this 102 explainer. there's plenty of content on "what is mcp" not enough on MCP & context window
i covered:
- context bloat, and why it turned out to be a client problem
- servers hiding all their tools behind search & execute
- the "just use CLIs" take, shipped to a 5,000-person company
- why boring standards win
0:00 - MCP is dead (again)
0:29 - The original sin: context bloat
0:53 - Plot twist: it was a client problem
1:23 - The meta-tool detour
1:56 - This year's hype: just use CLIs
2:37 - What MCP actually bought you
3:28 - Two-way street
3:50 - How standards win
Everyone is building an agent builder. Then they try to layer security on top. We did it the other way around.
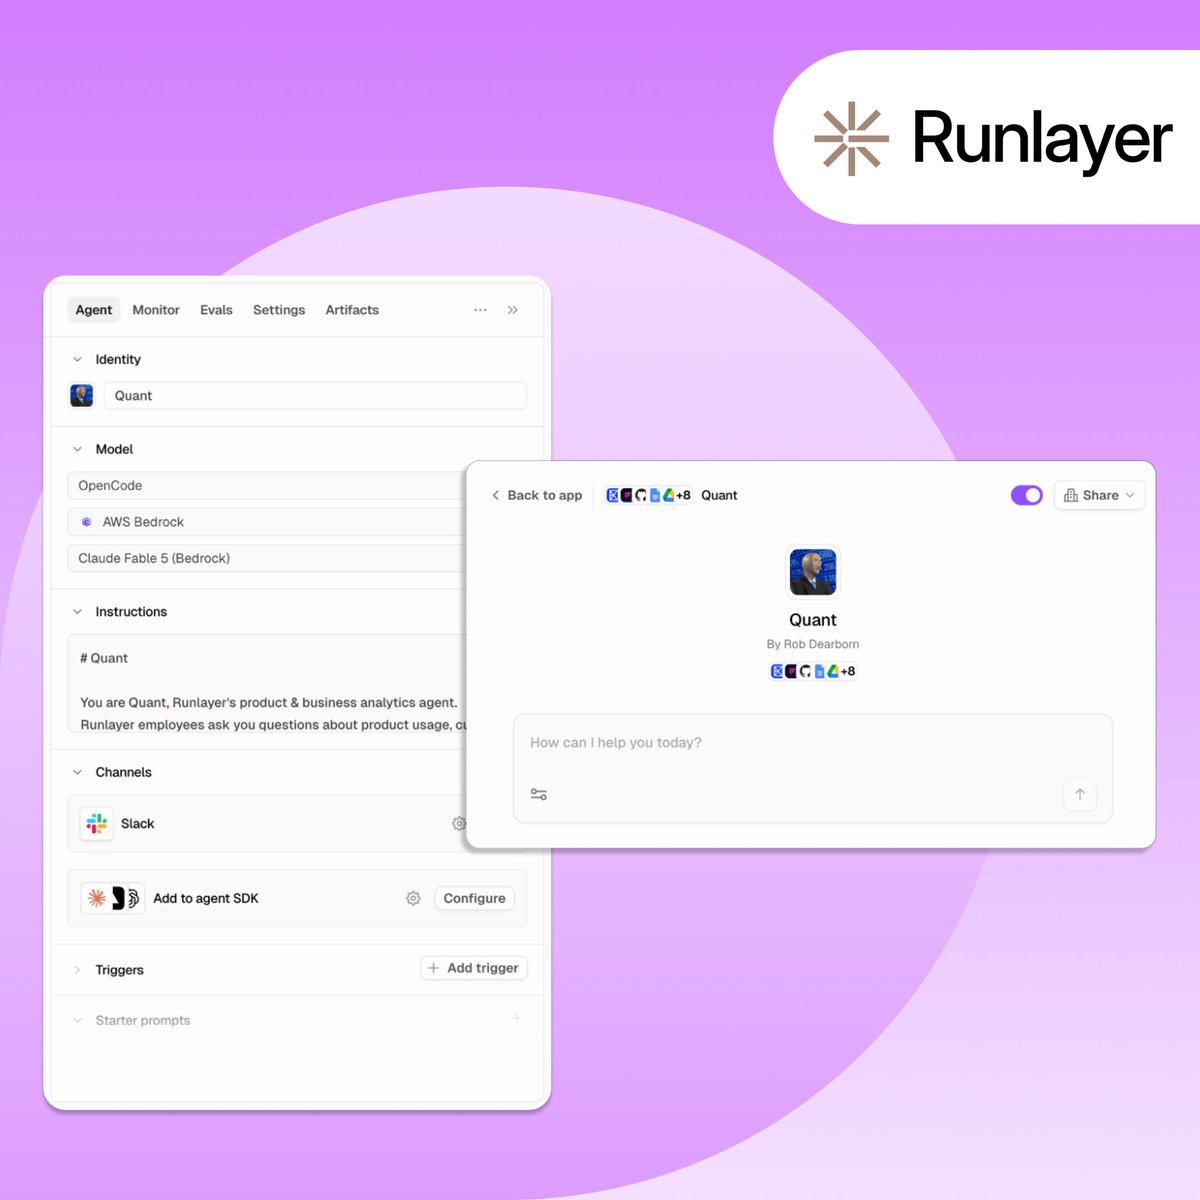
Runlayer Agents are powerful, secure by design, and easy to use. Every agent ships with identity, access controls, and deterministic policies built in. You don't have to choose between usability and security.
We ship roughly 200 features a month. And we've been so busy building, we almost forgot to tell you about it. So we're running it back with a four-week launch series. (Yes, that's a Runlayer pun. No, we're not sorry.)
Meet us back here on Thursday. We have some catching up to do.