‼️DATABASE BREACH ALERT
🇨🇱 Chile | Healthcare Sector
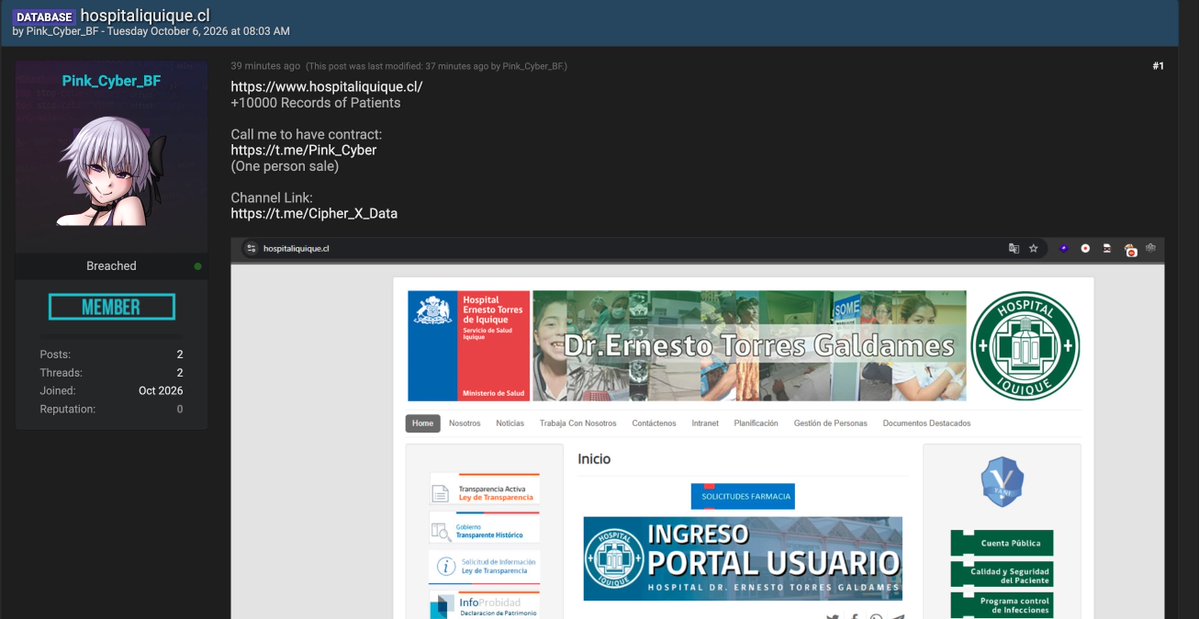
🏥 Organization: Hospital Dr. Ernesto Torres Galdames
📍 Location: Iquique, Chile
🌐 Website: https://t.co/3gSvmsBs7w
📊 Claimed Data: 10,000+ patient records
A threat actor known as Pink_Cyber_BF is allegedly offering access to a database associated with Hospital Dr. Ernesto Torres Galdames for sale via Telegram.
⚠️ The claim and dataset authenticity have not been independently verified. If genuine, exposure of patient records could pose significant privacy and identity risks.
#CyberSecurity #DataBreach #DataLeak #Healthcare #Chile #PatientData #ThreatIntelligence
@chum1ng0 Si le quitan el piso a la fuente, para estos casos, no son gente seria. Ya me ha apsado con empresas que aparecen en filtraciones, y dicen que es para ahcer marketing jajajajajaj
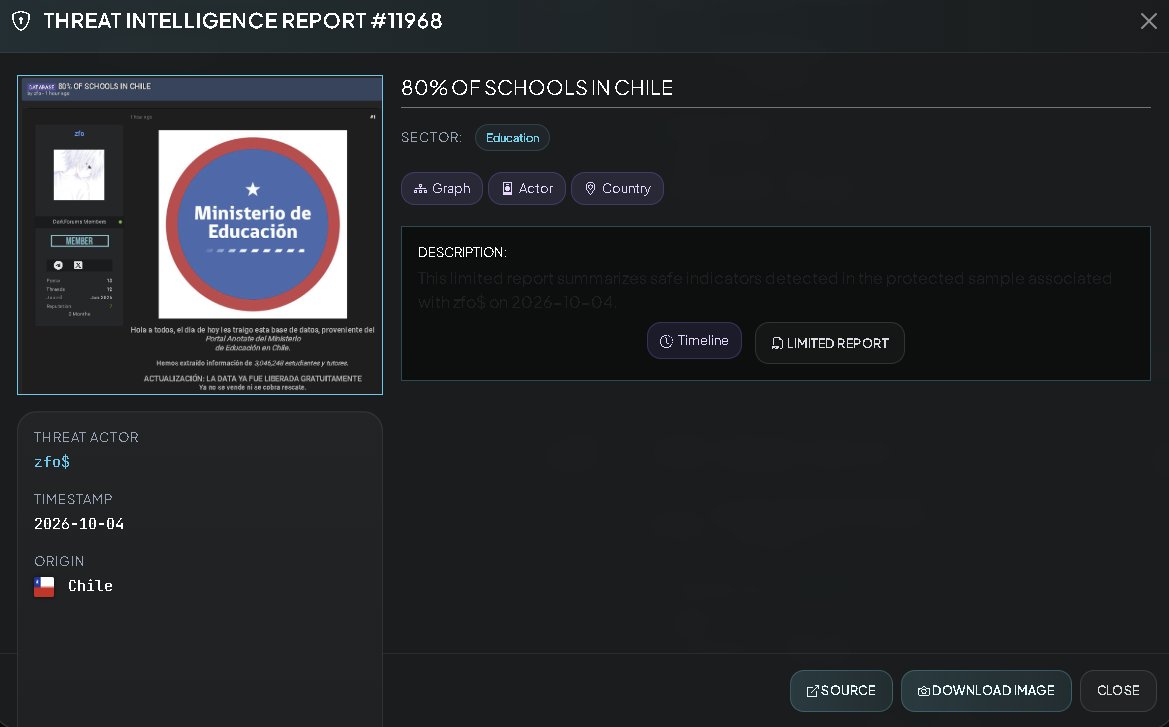
⚠️ PREVENTIVE ALERT 🇨🇱 🎓: ALLEGED EXFILTRATION AND PUBLIC RELEASE OF DATA FROM THE CHILEAN MINISTRY OF EDUCATION'S "ANÓTATE" PORTAL (ACTOR: ZFO)
[STATUS: ALLEGED / UNCONFIRMED / THREAT ACTOR: ZFO / DATE: OCTOBER 4, 2026]
The centralized cyber-intelligence system has detected a post on underground forums (DarkForums) made on October 4, 2026, by the user "zfo" (in collaboration with sqx, vansel, cyk, and zaelz). The report announces the alleged exfiltration and subsequent free release of a database originating from the Chilean Ministry of Education's "Anótate" portal, reportedly containing information on 3,046,248 students and guardians.
It is strictly noted that the veracity of this breach and the authenticity of the repositories have not been officially confirmed by Chilean educational authorities. The definitive status of the leak remains unconfirmed.
Threat Actor: zfo
Victim / Affected Entity: "Anótate" Portal of the Chilean Ministry of Education (MINEDUC).
Sector: 🎓 Public Education, School Management, and Citizen Records.
Country: Chile 🇨🇱.
Reported Data Volume: 3,046,248 records in a JSON format file with an approximate size of 1.23 GB. 🔍 TECHNICAL BREAKDOWN OF THE EXPOSED DATA STRUCTURE
According to the JSON schema provided by the actor on the underground forum, the records contain highly sensitive data regarding guardians and minors:
Guardian/Tutor Data:
Guardian first names, paternal surname, maternal surname.
Mobile phone number, email address.
Guardian RUN/RUT (National ID number).
Student Data:
Student first names, paternal surname, maternal surname.
Student RUN/RUT (National ID number).
List number, status (e.g., ACCEPTED), active status.
Institutional Management Metadata:
RBD (Educational institution's database ID code).
Course code, token timestamp.
Management timestamps (API queuing date, response date, contact date) recorded in September 2026.
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / EDUCATION SECTOR)
Security Audit of MINEDUC Platforms: Government technical teams must review access logs and Application Programming Interfaces (APIs) for the "Anótate" portal to determine the source of the unauthorized access.
Public Alert and Prevention: Proactively inform guardians and educational institutions about potential scam attempts or fraudulent communications utilizing the exposed data.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #Mineduc #Chile #DataLeak #EducationSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
Hospital Clínico de la U. de Chile se querella tras sufrir ciberataque y filtración de información médica confidencial #ciberseguridad#Chile
El ciberataque afectó directamente al Servicio de Imagenología del hospital y permitió que terceros no autorizados accedieran a información asociada a exámenes médicos realizados en el recinto.
https://t.co/cKOPQl1nuf
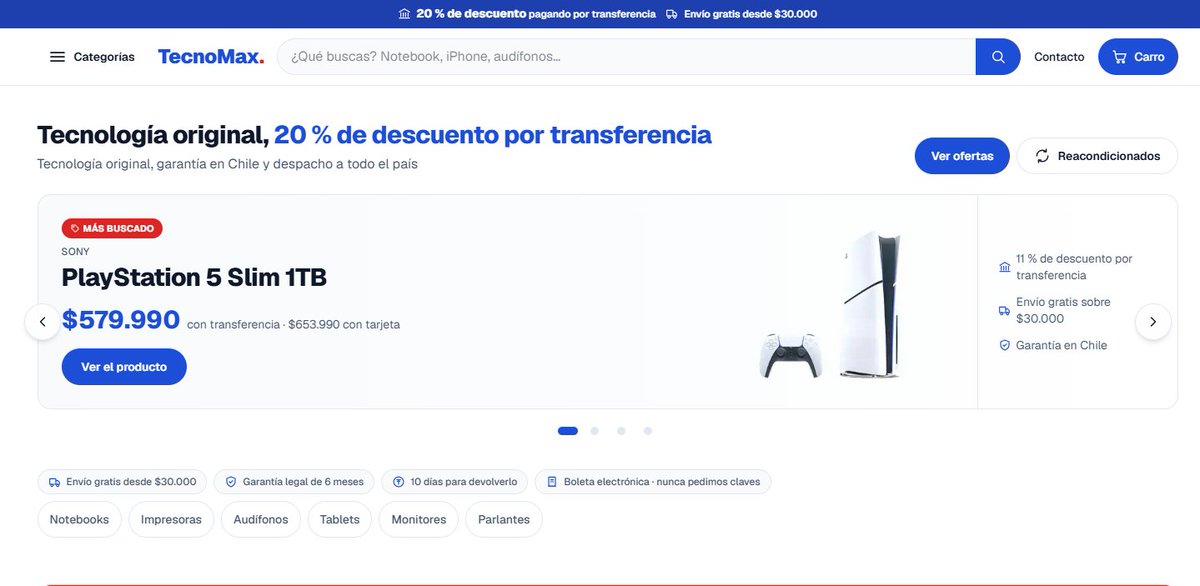
🔴🇨🇱 Alerta: tecnomaxchile[.]com es un sitio sospechoso. El dominio se creó el 22 de septiembre de 2026, el titular está oculto y no publica RUT ni razón social. #Chile#fraude#estafa@Namecheap
Fallo en Docker permite a contenedores sobrescribir archivos del host y obtener acceso root
Se ha descubierto una vulnerabilidad en Docker denominada CopyEscape (CVE-2026-17106)
https://t.co/yFBUNlaub9
🔴 PostgreSQL'de CVSS 8.8 (HIGH) seviyesindeki CVE-2026-15742 için public exploit PoC yayınlandı.
fuzzystrmatch modülündeki integer wraparound, levenshtein() ve levenshtein_less_equal() fonksiyonlarında bellek bozulmasına ve out-of-bounds memory write'a yol açabiliyor. Saldırının başarılı olması durumunda PostgreSQL server process yetkileriyle arbitrary code execution elde edilebiliyor.
⚠️ PostgreSQL 14.x–18.x etkileniyor:
18.6 / 17.11 / 16.15 / 15.19 / 14.24 öncesi sürümler.
PoC: https://t.co/hQSUoz7aAQ
Detaylar: https://t.co/tKutbSXfTQ
🚨 Critical Apple CoreGraphics Zero-Day Vulnerability Actively Exploited in Attacks
Details: https://t.co/vi7ImgPtPF
Apple has released iOS 26.7.1 and iPadOS 26.7.1 to fix a critical zero-day vulnerability that it says may have been exploited in an extremely sophisticated attack against specifically targeted individuals.
The security issue, tracked as CVE-2026-86950, affects the CoreGraphics framework, a fundamental Apple component responsible for rendering graphics, images, and documents across iPhones and iPads.
Successful exploitation could allow attackers to execute arbitrary code on a vulnerable device by convincing a victim to process a maliciously crafted file. Apple released the updates on September 28, 2026, and urged users to install them as soon as possible.
#cybersecuritynews
⚠️ PREVENTIVE ALERT 🇨🇱 🏥: ALLEGED DATA BREACH OF THE *REVISTA CHILENA DE MEDICINA INTENSIVA* (CHILEAN JOURNAL OF INTENSIVE CARE MEDICINE) (ACTOR: LVN4T1K0 / GHOSTLEAKERS TEAM)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT YET VERIFIED / THREAT ACTOR: LVN4T1K0 (GHOSTLEAKERS TEAM) / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums by user Lvn4t1k0, representing the GhostLeakers Team collective. The report announces the release of the complete database belonging to the *Revista Chilena de Medicina Intensiva* (https://t.co/sVpwEeWkUS).
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by the publishing institution. The definitive status of the information remains unconfirmed.
Threat Actor / Group: Lvn4t1k0 / GhostLeakers Team
Victim / Affected Entity: *Revista Chilena de Medicina Intensiva* (https://t.co/sVpwEeWkUS).
Sector: 🏥 Healthcare; Medical, Academic, and Scientific Publications.
Target Country: Chile 🇨🇱.
File Format and Size: CSV format; approximate size of 658 KB.
🔍 TECHNICAL BREAKDOWN OF THE SAMPLE
According to the metadata and technical schemas published by the actor on the underground forum, the leaked records include:
Exposed Information Fields:
Full names of registered users and professionals.
Email addresses.
Internet Protocol (IP) addresses. Record creation dates and timestamps (created, published).
Sample Records: The actor attached a CSV snippet containing historical records dating back to 2010, exposing data on healthcare professionals in Chile.
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / HEALTHCARE)
Audit of Academic Systems and Portals: Platform administrators should review web servers and associated repositories to check for active breaches or exposed backups.
Early Alert to Affected Users: Notify the healthcare professionals whose data appears in the public samples so they can strengthen the security of their email accounts.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #IntensiveCare #Chile #GhostLeakers #Healthcare #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
Compromised MemOS packages on npm and PyPI spread cross-platform malware that steals developer credentials and may use stolen tokens to compromise more packages, @SocketSecurity reported. #cybersecurity#CISO#infosec https://t.co/bZyDD2NGlz