3% of “critical” software security bugs, in all of recorded history, have been found in the last month.
This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total
Do you realize how fucking insane that is?
coworker passed away over the weekend. we were informed during a meeting, everybody was shocked for about a minute, then the meeting continued like nothing happened. bro, these jobs really aren’t worth the strain we put on ourselves
I think many of us working in tech tend to forget that the reason software engineering vs other engineering fields pays (a lot!) more, is a lot more flexible (WFH/remote), and has better perks:
Because this field changes much faster than other engineering fields. The premium is because fewer people are able/willing to pick up new technologies, methodologies so quickly.
But the field had ~10-20 years of stability, and so lots of folks forgot this is why a premium exists. And that AI is just another tech wave: software engineers who pick it up and master it will generally fare better; those not will struggle a lot more.
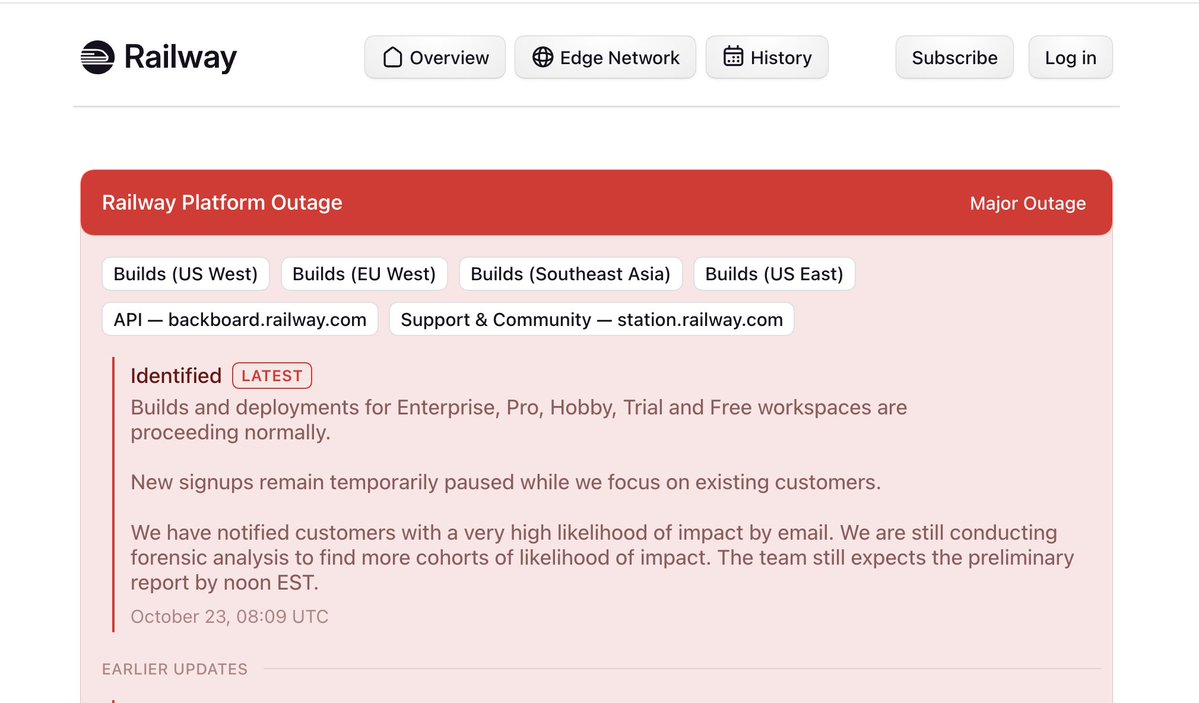
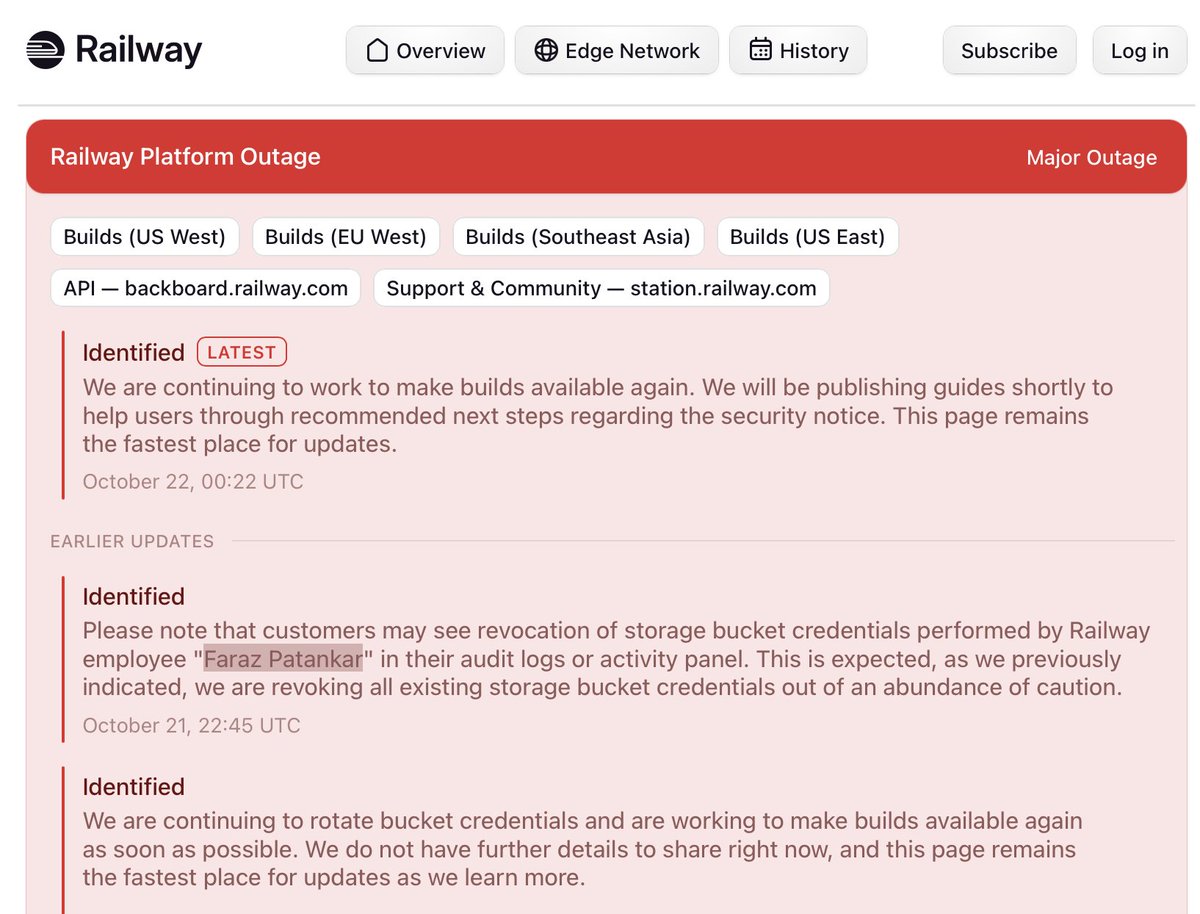
Products like Railway that over-index on developer experience without serious investment in security (dedicated security engineers, SecOps, and real collaboration with ecosystem players) are a ticking time bomb.
I can’t find a single dedicated security employee at Railway, let alone a full security team. The only people communicating anything about the breach have been CEO Jake Cooper and engineers.
If you’re a PaaS without a serious security org, your clock is running. Either Vercel and Cloudflare catch up on DX, or a breach wipes out the trust you’ve earned.
The only argument left is “muh cost savings”, aka the margin that should have paid for better security.
If you’ve EVER used Railway, assume your secrets could be compromised. Even if you deleted the project.
Apparently, deleting environment variables DOESN’T really delete them.
Claude dug up year-old deleted secrets through Railway’s internal API as if they still existed.
‼️ BREAKING: eMudhra, the Indian certificate authority whose private key was the number 4, is quitting the TLS business.
It blames social media for scrutiny "out of proportion" to a unit worth ~1% of revenue.
8 of its CA keys were numbers below 256, cracked in milliseconds.
Very pretentious from eMudhra’s part to say they *chose* to leave the business. The business is trust and they can’t be trusted. There is no business for them anymore.