La contraseña más usada en las PYMES que auditamos no es "123456". Es el nombre de la empresa + el año. Y el año casi nunca es el actual.
Eso sí que es legacy.
- 22 años
- Repetí en la ESO y no sabía que hacer
- Ahora soy hacker
- No trabajo como hacker, porque no tengo años de experiencia🤓☝️
- No salgo apenas porque solo estudio y trabajo
- Tengo una web y un arch linux to' guapo
- Me han pagado por reportar fallos
- Vivan los durums
-32 años
-Deje la universidad a los 3 meses de empezar
-Nunca he trabajado en algo que no sea Youtube
-No veo na
-Embajador de NFTs
-Cancelado demasiadas veces
-Tengo dinero pero solo se trabajar
‼️ Unremovable Israeli Spyware Found on Samsung Devices
Samsung faces backlash over AppCloud, an Israeli-developed app pre-installed on budget Galaxy A and M series devices.
Investigations reveal the app is embedded in the operating system, preventing full removal. Even when disabled, AppCloud remains on the device, reappears after updates, and can covertly install additional software.
@0xdab0 After 2001:
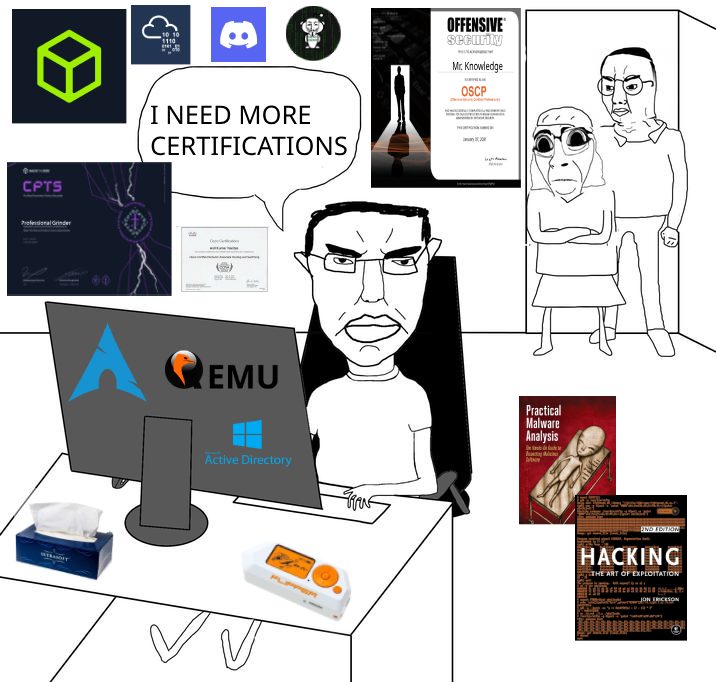
- Arch user with hyprland, full custom
- Awarded in a BBP program on hackerone
- eJPT
- And a website.
Without OSCP
Without job
I don't know how to charge a MacBook
:)
Found an XSS but got blocked by the CSP?
https://t.co/0aA3GyIOVz has a compiled list of ways to bypass the Content-Security Policy. Check out the video below 👇
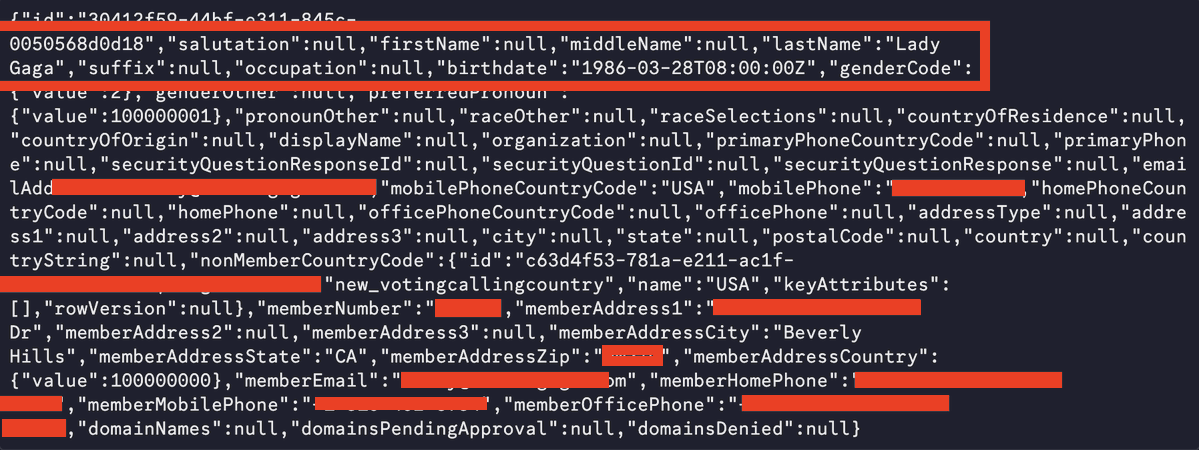
We accidentally got access to every Academy Award nominee's home address and phone number.
Before last year's Oscars Ceremony, together with @iangcarroll and @samwcyo, we found a way to leak every nominee's PII, including phone numbers and home addresses of the biggest actors around the world - from @ladygaga to @JaredLeto.
We were interested in the security of award ceremony shows, especially with the rise of @Kalshi and @Polymarket betting on winners. We wanted to check if it would be possible for an attacker to leak the winner before the official announcement.
While we didn't find evidence of that, we did notice that two of the Academy Awards' primary services had their APIs publicly facing without any authentication.
One offered general information about the ceremony, and the other allowed nominees to sign up and vote.
The first one - https://t.co/ddhQbVsYVd - allowed us to fetch every transaction made to sign up as a nominee for the Academy Awards, including member IDs and last four digits of credit cards.
With one request, we could get hundreds of contact IDs which could be chained with another API to correlate them to actual Hollywood actors via https://t.co/O0lrQQpXXR{ID}
Randomly skimming through the results, we saw they leaked full names, home addresses, phone numbers, email addresses of famous Hollywood stars.
We responsibly disclosed the findings to the Academy Awards on January 14th, which were promptly fixed.
We triggered WhatsApp 0-click on iOS/macOS/iPadOS.
CVE-2025-55177 arises from missing validation that the [Redacted] message originates from a linked device, enabling specially crafted DNG parsing that triggers CVE-2025-43300.
Analysis of Samsung CVE-2025-21043 is also ongoing.
⚡This PortSwigger lab is awesome!
How to create client applications and use OpenID specifications to perform an SSRF attack by configuring the logo URI.
Quality and quantity, thanks. @WebSecAcademy
https://t.co/Vn2D2c6o5s
@ciguleva Hi Tatiana, these videos are fantastic, as a small request, you could make the next one for a .gif solving the problem of quality and concatenate the animation (to avoid the cut).
I think that this style is very cool to have as wallpaper.