I’m excited to finally release a short book that’s about building C2 implants in C++. I hope it can serve as an educational resource for those in Red Teams who want to get started writing their own implants and related C2 components.
You can read it here: https://t.co/CMyRXtSO46
@_RastaMouse Really enjoying all the content you've been posting related to Crystal Palace, I've been able to supplement the update docs with your posts to better make sense of the material. Thanks!
In this post, I discuss one key difference in the thinking between sophisticated adversaries and many of the red teams that try to simulate them, as well as what that means for tradecraft and tooling.
https://t.co/FTEHcIsqsW
Open sourcing a side-project I’ve been working on called “Mochi”. It’s a PoC C++ loader that leverages ChaiScript to modularize and execute code. It was built to allow remote loading of ChaiScript files that execute offensive actions with the Windows API:
https://t.co/AaBduQdMlc
I may have reinvented the wheel in some areas, but hopefully it still serves as an interesting PoC. I’m not aware of any offensive tooling using ChaiScript, so if people have projects I could reference, please let me know!
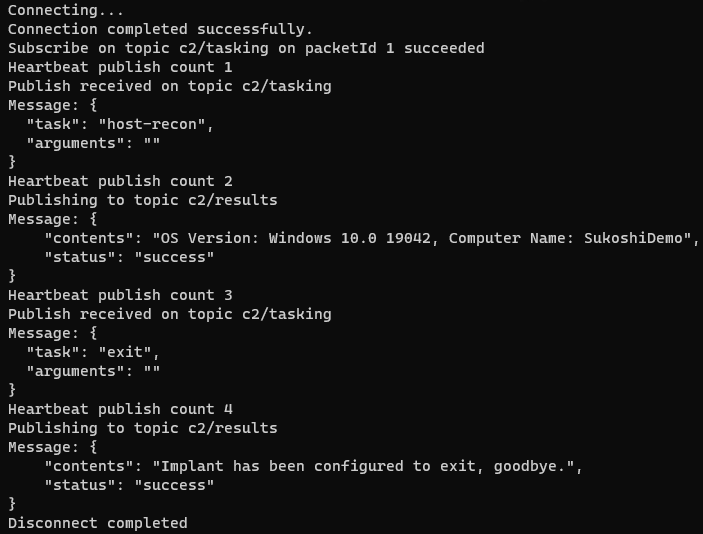
I've added a C++ version of the Sukoshi AWS IoT Core implant for those who are interested in experimenting with a binary. You can find an updated page with build instructions and C++ source code here: https://t.co/GGQomAO0CU
Lately, I’ve been experimenting with different protocols and methods for C2. As part of this, I developed a PoC Python implant called “Sukoshi”. It uses the MQTT protocol for C2 and leverages AWS IoT Core as its infrastructure: https://t.co/GGQomAO0CU
I’d like to shout out Daniel Abeles (@Daniel_Abeles) and Moshe Zioni for their work while at @Akamai Threat Research. Their MQTT-PWN project served as an excellent reference during development: https://t.co/Y0w78yQ3NX
I’m excited to finally release a short book that’s about building C2 implants in C++. I hope it can serve as an educational resource for those in Red Teams who want to get started writing their own implants and related C2 components.
You can read it here: https://t.co/CMyRXtSO46
🧠 Mental models are useful for developing solutions and stimulating thinking. In this post, I discuss some personal mental models I've found useful for offensive capability R&D, which can also generalize to understanding opponent processes in InfoSec.
https://t.co/anpVQqIpcV