Just published a blog on the Silver Platter room from @TryHackMe!
Walkthrough includes scanning, login bypass (CVE-2024-36042), token abuse & root.
If you're into web app vulns + logic flaws, give it a read : https://t.co/44qlgqtvQs
Just kicked off a new project: Snort Rule Mastery Lab
Building a custom detection lab using Snort to simulate real-world attacks and write custom IDS rules.
Learning by doing one packet at a time.
Blog & setup guide are attached
https://t.co/8mj2jTHikW
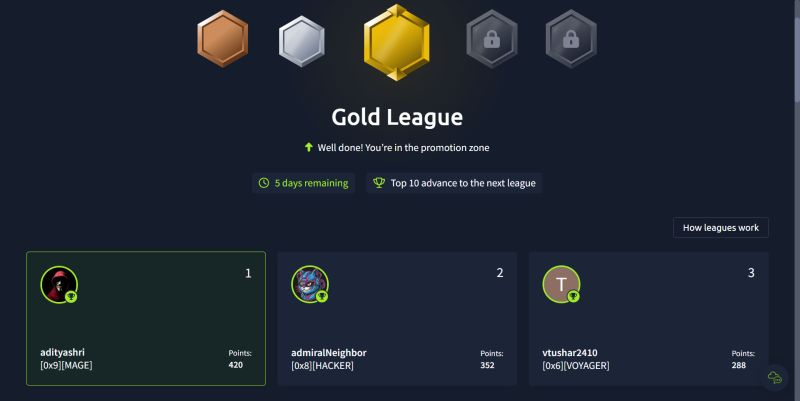
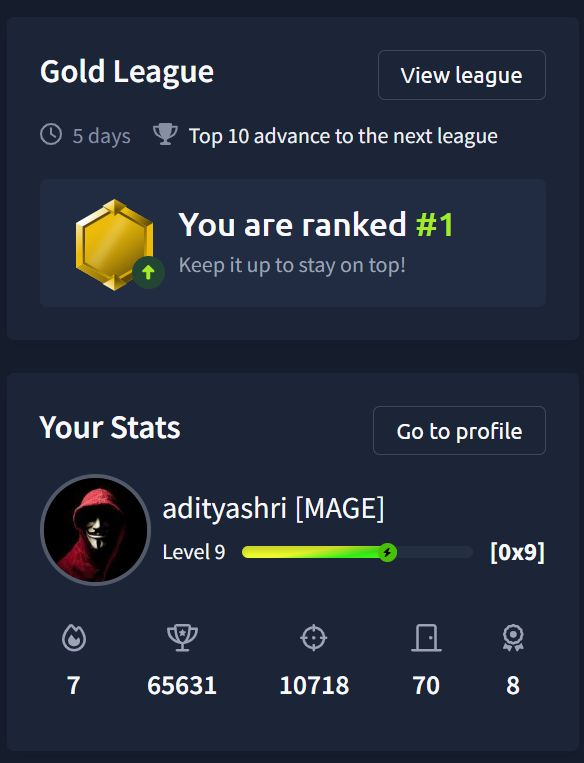
Ranked #1 in the Gold League on @tryhackme this week.
Been staying consistent with both fundamental and challenge rooms and it's good to see that effort reflected in the standings.
Not just chasing points, but discipline, routine, and growth.
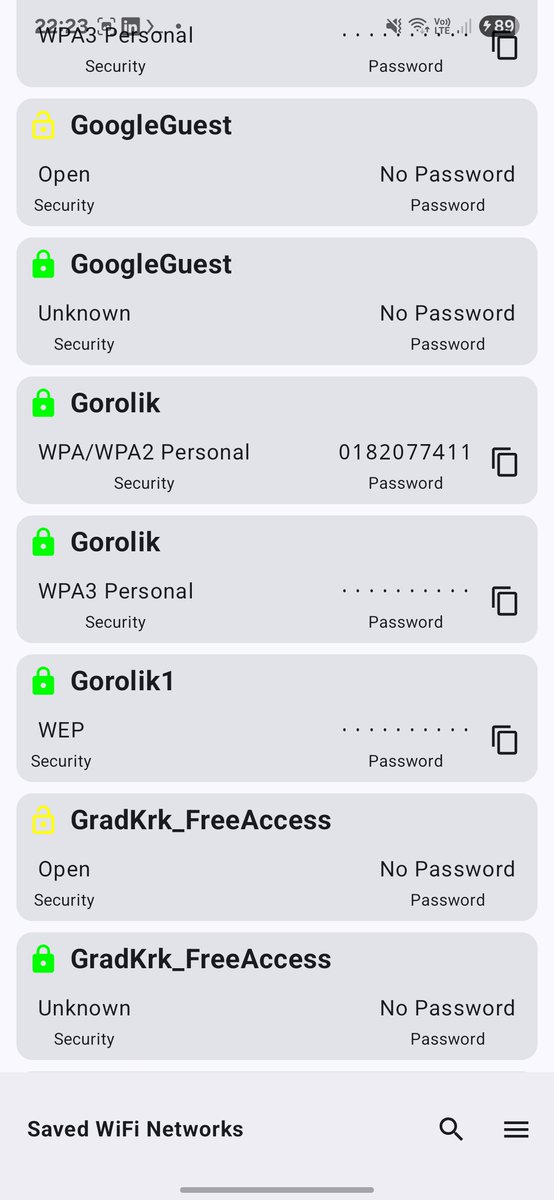
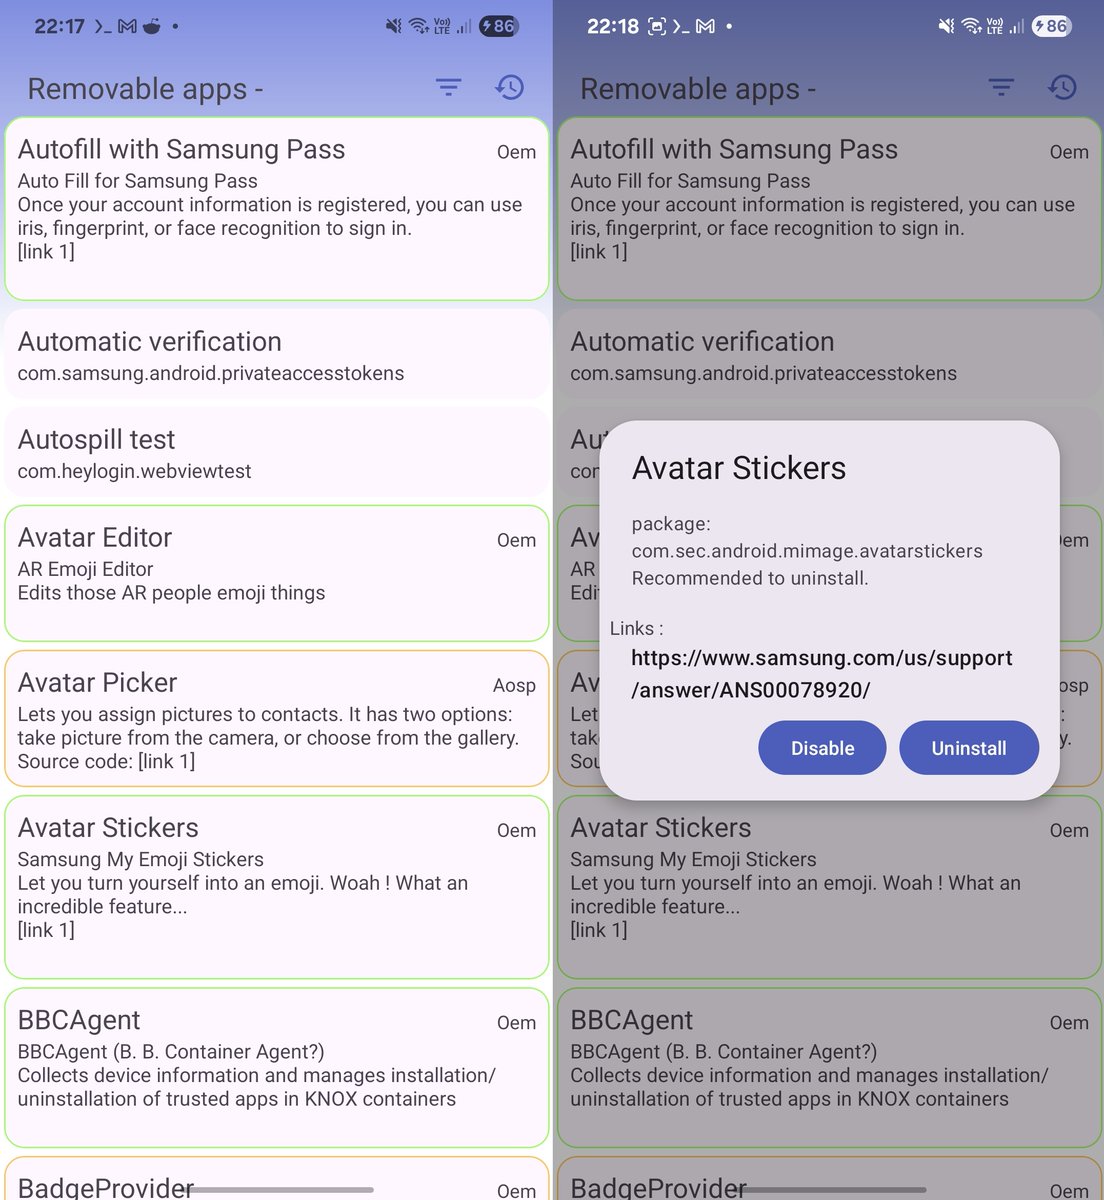
Shizuku unlocks advanced functionality on any Android
Using #Shizuku your Android gains ADB privileges to remove bloatware, list running processes, open listening ports, view stored Wi-Fi passwords, inspect logcat of other apps, etc.
https://t.co/634krfzRYj
DMARC can reveal more domains associated with a target.
https://t.co/IOZqvIUCEX<target-domain> allows you to find domains using the same DMARC record. Check it out 👇
There's also a python tool: https://t.co/MgbyS42HSn
Just wrapped up the Silver Platter room on THM
Labeled “Easy” but had me stuck at the Silverpeas login for way too long.
Turns out CVE-2024-36042 was the trick removing the password field from the POST did it.
Big wins💪😎
https://t.co/z5HMNQWU03 #tryhackme via @tryhackme
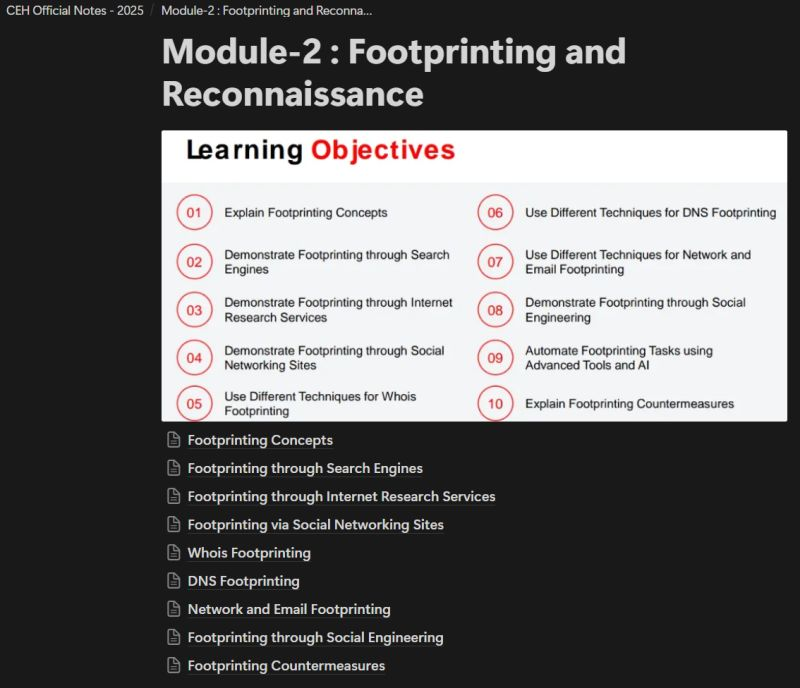
Just wrapped up the Footprinting & Reconnaissance module from CEH.
It covered how attackers gather intel before an attack
From passive methods like WHOIS & Google dorks to active scanning like Nmap & DNS enumeration.
Playing Shodan was interesting
Notes: https://t.co/h4M8jZKnz8
Just completed the Snort room on @tryhackme.
Understood IDS rules and how Snort detects suspicious traffic.
Planning to set up a small lab project soon to better understand real-world detection.
https://t.co/FidqUyt613 #tryhackme via @tryhackme
Just completed this room, I would say this was very interesting...I know its old and termed as "Easy" category but the privilege escalation part was still a challenge for me...
Anyway enjoyed it thoroughly
https://t.co/p7jQJ8wb1T #tryhackme via @tryhackme
Just completed this interesting THM CTF. Checkout W1seGuy if you haven't cried in days....😭
It surely made me cry
https://t.co/S5mEs1bca8 #tryhackme via @tryhackme