Dropping a new article.
It's about a new local privilege escalation technique that becomes viable when a writable system path is present. Yet another technique.
It uses Windows Audio for escalation and doesn't require system reboots.
https://t.co/sw9t5RKoMO
I'm super happy to announce an operationally weaponized version of @YuG0rd's BadSuccessor in .NET format! With a minimum of "CreateChild" privileges over any OU it allows for automatic escalation to Domain Admin (DA). Enjoy your inline .NET execution!
https://t.co/nvZmsNqjnG
A quick writeup on potential security issue of Windows LNK that I reported to MSRC last month. They decided to not fix due to relying on MOTW. In the blog I included the proof of concept. All you have to do is to Right-Click and get Info Disclosure :)
https://t.co/j2N7AQlO7Z
CimFS: Crashing in memory, Finding SYSTEM! @cplearns2h4ck dug into Microsoft CimFS, found a sneaky 0-day, and guess what? The fix by Microsoft was just locking the door 🔐on unprivileged users. 😂
Dive into the adventure with us: https://t.co/7g30HpmFzG
🚀 New Blog & PoC: Abusing IDispatch for COM Object Access & PPL Injection
Leveraging STDFONT via IDispatch to inject into PPL processes & access LSASS. Inspired by James Forshaw's research!
🔍 Blog: https://t.co/TKdtwuj509
💻 Code: https://t.co/tlppakaLPO
Happy New Years!
Also, overcome RDP session hijacking limitations in Windows Server 2025 (well, really 2019+) by shadowing a redirected console session in your current TS session with SharpRDPHijack.
https://t.co/ueS2emON2c
Get the scoop on a lateral movement technique within the distributed component object model (DCOM) Excel application. @GrayHatKiller details the method in our latest blog post. https://t.co/6NqDcEmjzD
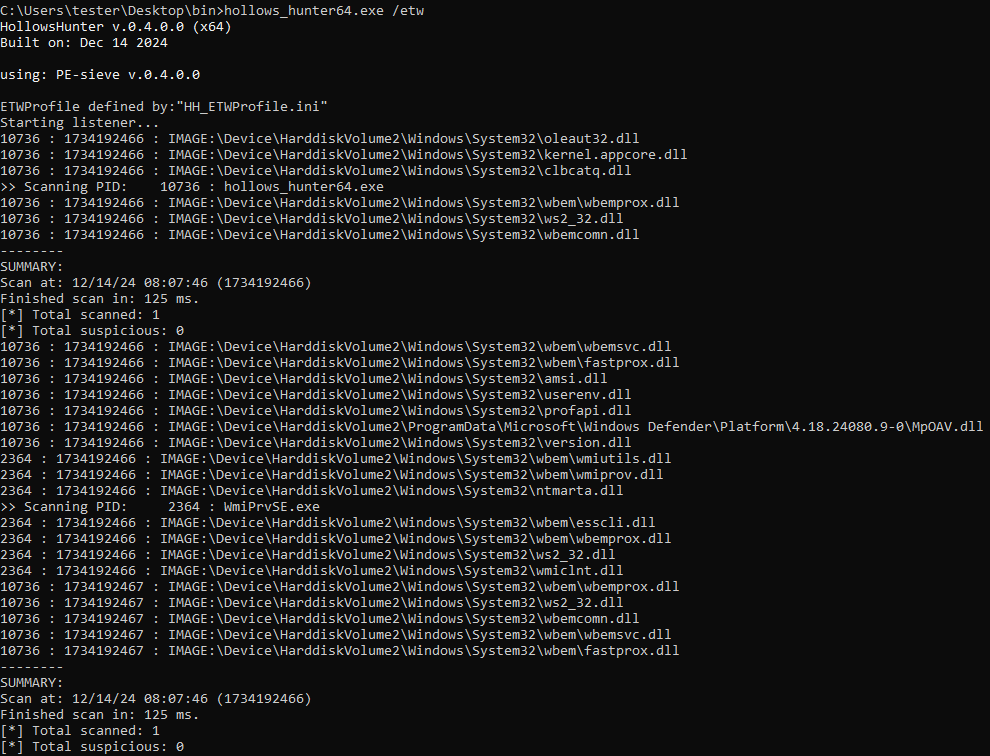
New #HollowsHunter (v0.4.0) is out: https://t.co/FBWjtKp8ez. Now you can use it in the classic mode, as well as in ETW mode - as a multi-threaded listener. The watched events can be defined by a simple profile - but it is just a beginning...
I am excited to share with you my latest research - "DCOM Upload & Execute"
An advanced lateral movement technique to upload and execute custom payloads on remote targets
Forget about PSEXEC and dive in!
https://t.co/ruQJlXgLqV
https://t.co/Yp25P6pZvH
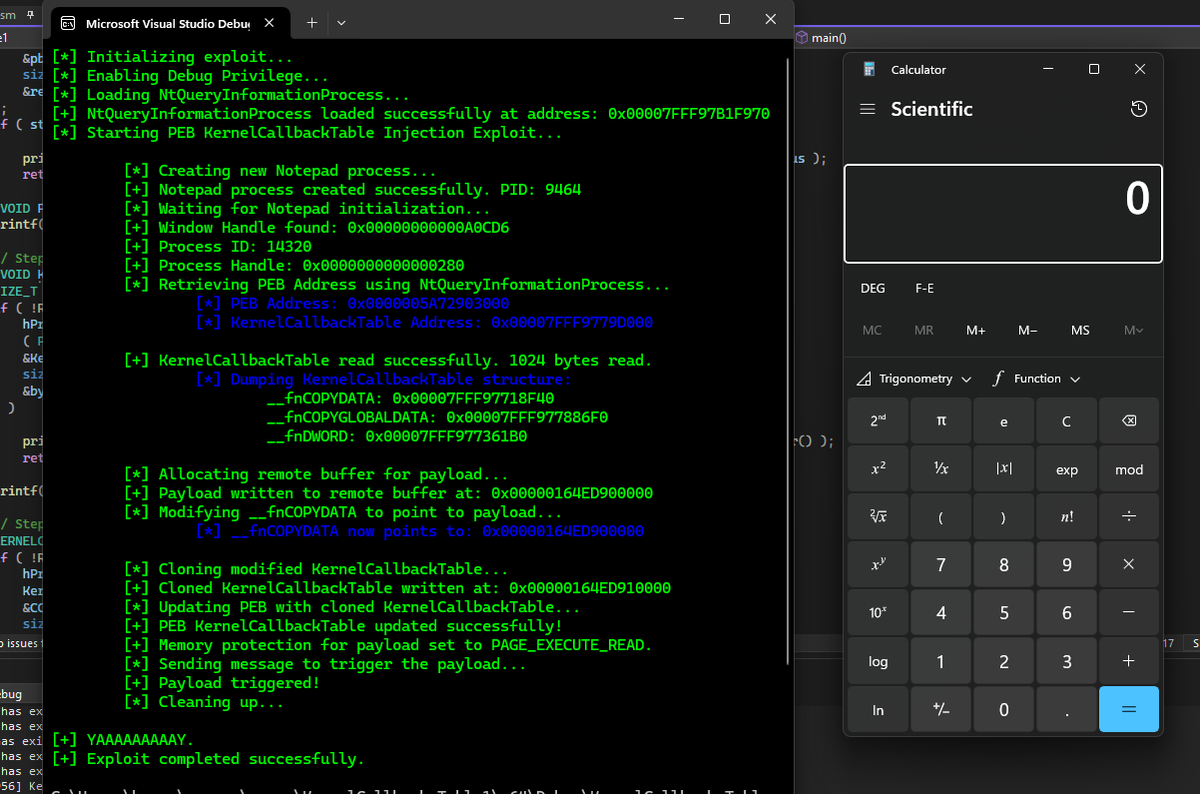
Published my PoC on Kernel Callback Table Manipulation for Process Injection! This technique exploits the PEB to redirect execution flow and inject payloads into target processes. Dive in here -> https://t.co/MFn5SZibSL
🚀 Just released a new tool: https://t.co/GkpwCJjmhr 🎉
✅ Perfect for Rust developers and security researchers seeking a cross-platform solution to easily verify PE file signatures.
Check it out on GitHub! #cybersecurity#windows#blueteam#pe#opensource#rust
I wrote a blogpost and a tool on how to abuse Vectored Exception Handling (VEH) along with indirect syscalls to produce legitimate call stack without manually constructing them.
Blog Link: https://t.co/zLCtetcPaY
Tool Link: https://t.co/AHdJgZB99O