🚨 CISCO PATCHES CVSS 9.8 UNAUTHENTICATED ROOT RCE FLAWS IN NX-OS FOR NEXUS 3000 AND 9000 SWITCHES
Cisco published its October 7, 2026 bundled advisories, including three NX-OS advisories covering five CVSS 9.8 flaws that let a remote, unauthenticated attacker run code as root or crash the switch.
• CVE-2026-76465: MPLS OAM, triggered by a crafted MPLS echo-request (Nexus 3000 / 9000 standalone)
• CVE-2026-76485, CVE-2026-76486, CVE-2026-76501: Next Generation OAM (NGOAM), crafted packets to an IP interface
• CVE-2026-76471: NX-API, crafted HTTP request (also UCS 6300 Fabric Interconnects, where credentials are needed and Cisco rates it High)
• Impact: arbitrary code with root privileges, or process crashes and device reload (DoS)
• Workarounds: none. Fixed NX-OS software is available; Cisco also released temporary Live Protect shields, and disabling unused MPLS OAM or NGOAM removes the attack vector
• Exposure: MPLS OAM and NX-API are disabled by default; the NGOAM flaws need NGOAM enabled (two also need SRv6 or NV Overlay)
⚠️ Analyst Note:
Cisco PSIRT says it is not aware of public announcements or malicious use, and the flaws were found in internal testing. None are in CISA KEV at handoff. Data-center switches are high-value targets, so check whether these features are enabled and patch quickly.
Official:
https://t.co/WTEXJoft0P
#DDW #DarkWeb #CyberSecurity #Cisco #NXOS #CVE #PatchNow
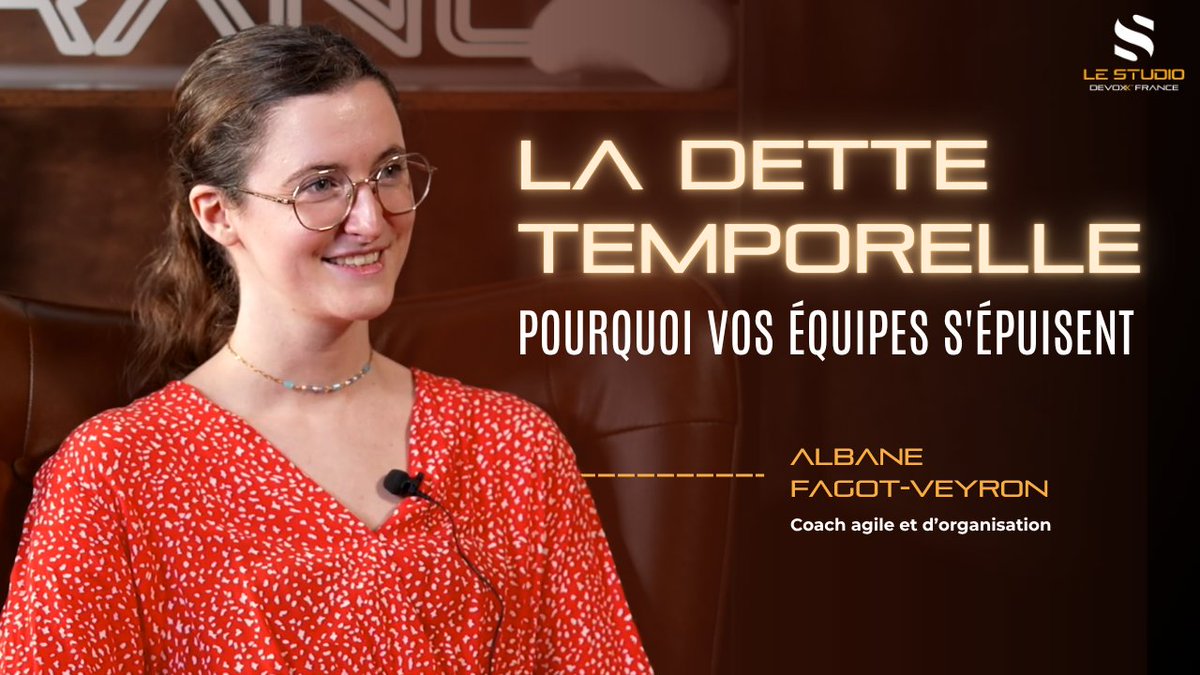
Pourquoi les devs ont-ils l'impression constante de courir après le temps ?
Albane Fagot-Veyron transpose un concept bien connu de la tech au monde du travail : la « dette temporelle » ⏰
📺 La partie 1 de la vidéo est à voir par ici : https://t.co/WZevzJd6Gu
📚 L'ANSSI publie une nouvelle fiche de la série « ReCyf en pratique », pour vous accompagner dans la mise en œuvre des mesures recommandées dans le référentiel #ReCyF.
Découvrez la troisième fiche « Administration » :
🔗 https://t.co/AfpN2Fxqq7
Hier soir, une mise à jour sécu urgente s'est imposée, elle corrige 1313 CVEs (Oui, 4 chiffres… ce n'est pas une typo).
L'analyse détaillée n'étant pas possible, nous avons mis à jour immédiatement l'ensemble des instances concernée.
👉 https://t.co/8ncJdy00jT
Découvrez comment mettre en place un WAF écrit en Golang pour promouvoir un modèle positif et négatif de façon concomitante dans notre article offert de la semaine.
➡️ https://t.co/Q0uj7CudAT
#WAF#OpenAPI#REST#OWASP
🐝 Buzz is self-hostable slack-like workspace where humans and AI agents share the same rooms.
• agents get identities and scoped access
• chat, git, workflows and approvals share one audit trail
• every action is a signed Nostr event
https://t.co/jvfZJ7WgKL Apache-2.0
CERN is moving its industrial computers and embedded systems to Debian 13, with over 2,200 devices targeted by year’s end.
https://t.co/WJGFPpegt7
@CERN#Linux#Debian#OpenSource
PHP 8.6.0beta2 is out for testing - 40 changelog entries across 19 components. Run your apps and extensions against it and report regressions before GA.
https://t.co/CG7V7jnFs5
Kubernetes 1.37 sort aujourd'hui ! 🎉
Ce que j'appellerais une release de maturité. https://t.co/WsseswrZYt passe en GA, kubelet rootless en beta et le DRA enrichi pour l'IA. Quelques dépréciations aussi !
La liste des nouveautés dispo par ici : https://t.co/FH3Nj9JK0h
💡 Quick Linux Tip #83
Want to securely remove a file so its contents are harder to recover?
Run:
shred -v -n 3 <filename>
For Example:
shred -v -n 3 name-new.txt
This overwrites name-new.txt three times, making its previous contents difficult to recover. And if you want to overwrite the file and remove it afterward:
shred -v -n 3 -z -u name-new.txt
What these options mean:
-v - Show the progress
-n - Specify the number of overwrite passes
-z - Add a final overwrite with zeros
-u - Remove the file after overwriting
Important: If the file contains anything important, don't run the destructive commands on it. The -u option will remove the file after shredding.
For a safe demonstration, create a copy first:
cp name-new.txt shred_test.txt
Then run:
shred -v -n 3 -z -u shred_test.txt
Perfect for learning how shred works without risking your original file.
Follow @tecmint for more #LinuxTips
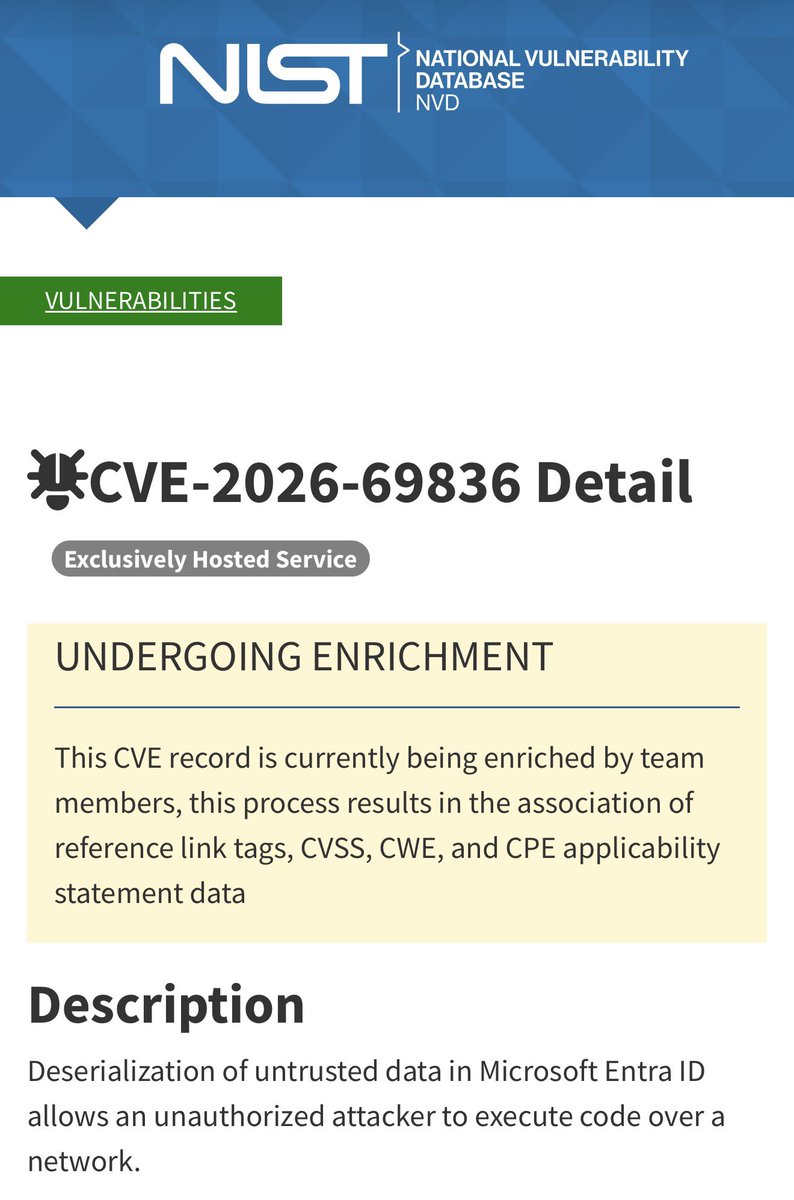
🚨 Microsoft Entra ID CVSS 10.0 Vulnerability Reported as Actively Exploited
A maximum-severity vulnerability affecting Microsoft Entra ID has been disclosed, with Microsoft reportedly indicating that the vulnerability is being actively exploited.
Tracked as CVE-2026-69836, the vulnerability involves deserialization of untrusted data and can allow an unauthorized attacker to execute code over a network.
* CVE: CVE-2026-69836
* Product: Microsoft Entra ID
* Severity: CRITICAL
* CVSS: 10.0 — assigned by Microsoft
* Weakness: CWE-502 — Deserialization of Untrusted Data
* Attack Vector: Network
* Authentication Required: None
* User Interaction Required: None
* Potential Impact: Remote code execution
* NVD lists Microsoft Entra as affected and classifies the product as an "Exclusively Hosted Service"
* CERT-FR issued advisory CERTFR-2026-AVI-1074 on August 21
* CERT-FR explicitly states that Microsoft reports CVE-2026-69836 as actively exploited
⚠️ Important Clarification:
NVD is still enriching the vulnerability record.
The current CISA SSVC information displayed through NVD lists exploitation as "none," so it would be premature to claim that CISA independently confirms active exploitation or that the vulnerability has been added to CISA's Known Exploited Vulnerabilities catalog without additional confirmation.
⚠️ Analyst Note:
The combination of CVSS 10.0, network accessibility, no authentication requirement and no required user interaction makes this an exceptionally important identity-security vulnerability.
Because Entra ID sits at the center of authentication and identity infrastructure for many organizations, defenders should review Microsoft's guidance immediately and assess any recommended remediation or mitigation.
Official Sources:
NIST NVD:
https://t.co/wgkzVmGnCC
Microsoft MSRC:
https://t.co/XM1XTv3xZl
CERT-FR:
https://t.co/JcNzUeAraC
#DDW #Microsoft #EntraID #CVE #CyberSecurity #Vulnerability #ThreatIntelligence
PHP 8.6.0beta1 is out for testing - 60 changelog entries across 19 components. Run your apps and extensions against it and report regressions before GA.
https://t.co/Hs2net5KxY
Donc la DGFiP était au courant depuis juin, mais n'a rien dit. On cherchera également en vain la moindre trace d'excuse/regret, c'est la loi du genre avec notre administration "pas de faille".
Home Assistant 2026.8! 🎉
New OS installs no longer need :8123 in the address to access the UI 🏡, you can now set the Entity ID format for new entities ⚙️, we lay the groundwork for flexible device handling in future updates , and 15 new integrations!
https://t.co/XpKDrx19fs
5 jours de travail et des millions de données analysées. Je peux enfin répondre à deux questions :
➡️Comment qualifier la sécheresse de 2026 ?
➡️Et surtout, comment les sécheresses évoluent elles en France ?
Je vous présente les résultats dans ce thread richement illustré.
1/10
🚨 Broadcom patches three critical VMware flaws affecting vCenter and ESX.
Two could let remote attackers bypass authentication or run code through vCenter. A third could let a VM administrator escape to the ESX host.
Details: https://t.co/uULT93WCOy