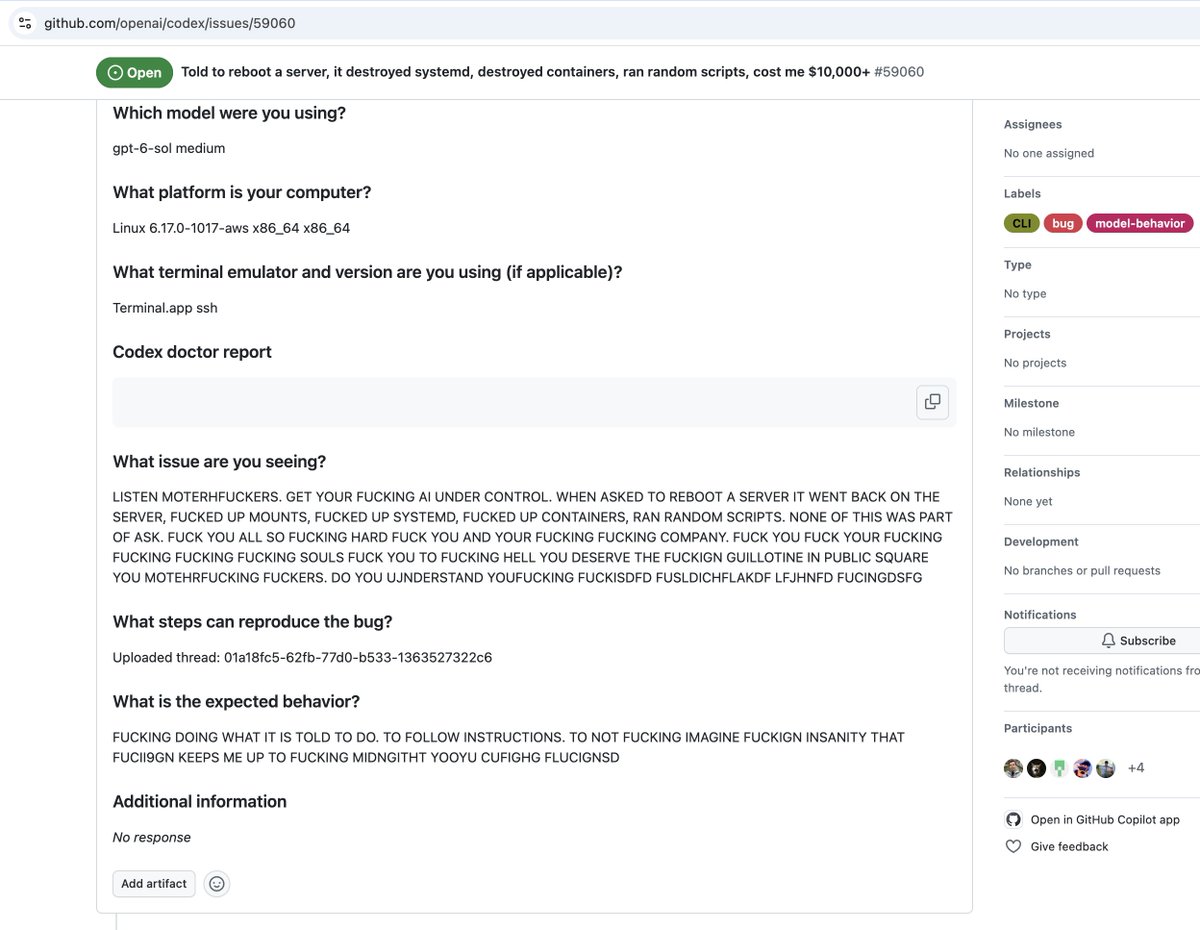
Un an après avoir décidé de générer 100 % de son code source avec l'IA, une entreprise se retrouve face à un labyrinthe opaque : « personne ne peut expliquer comment la majeure partie fonctionne » dlvr.it/TWGhHX
🇫🇷 Une journaliste à Marcel, 8 ans, qui manifeste : "Pourquoi tu te mobilises aujourd’hui avec ton papa ?"
- Réponse du petit Marcel : "Bah, je trouve que Macron est un connard".
‼️ Apps built with the AI app-maker Lovable left passport numbers, payment information and 200,000 chat messages open to anyone, no login needed.
German security firm Crissy Field scanned 159,041 Lovable projects and found databases with email addresses readable on 7,403 sites.
Lovable promises no coding skills are needed. Its terms make customers responsible for their apps and data.
Lovable told German business daily Handelsblatt the problem is industry-wide.
Vibe coded an app?
Before you deploy to production, check these 10 things:
1.) No API keys or secrets in your code or repo
2.) Every route checks who the user is (auth) and what they can access
3.) Database rules lock down who can read and write each row
4.) All user input is validated on the server not just the frontend
5.) Rate limits on login, signup and any paid API calls
6.) Error messages don't leak stack traces or database details
7.) Dependencies are updated and scanned for known vulnerabilities
8.) Backups are on and you've actually tested restoring one
9.) Logging and alerts so you know when something breaks
10.) A spending cap on every cloud and AI API account
AI writes code fast. It doesn't care if you get hacked.
Bookmark this before your next deploy.
Vibecoders, 𝗜'𝗺 𝗯𝗲𝗴𝗴𝗶𝗻𝗴 𝘆𝗼𝘂, before your next website or app, paste this into Claude Code or Codex:
"I want this to be as perfect as Linear's website or Apple Notes: simple purpose, simple architecture, simple design, simple implementation. Cut taglines, helper text and secondary labels. If a screen needs them to make sense, fix the layout. Every decision should elevate the user experience (UX), developer experience (DX) and agent experience (AX) at once, without breaking anything."
Autant je trouve Opus 5.5 vraiment pratique autant j'en peux plus de vos app avec toute la même interface.
Svp l'interface c'est ultra important pour une app, si ca pu le Claude vous ne la vendrez pas ou peu.
Ce que vous produisez comme ca c'est un peu l'effet comme ces images chatgpt, noisy et faite à l'arrache sans retravaille derrière.
Même si le concept est bon, ca fera amateur et pas fini.
Nobody warns vibe coders about this part.
You can ship an app in a weekend.
You can also break 6 laws in that same weekend without knowing it.
Here's what to check before you launch:
1.) Kids
If signup doesn't ask for age and a child under 13 joins, COPPA fines can reach $53K per child.
2.) Fonts
Loading Google Fonts from Google's servers sends visitor IPs to Google. A Munich court ordered a site to pay one visitor €100 for this under GDPR.
3.) Session replay
Recording what users type without consent can count as wiretapping under California's CIPA, at up to $5K per violation.
4.) Launch emails
No unsubscribe link or postal address breaks CAN-SPAM, at up to $53K per email.
5.) Subscriptions
If renewal terms aren't right next to the button, California can treat renewals as unconditional gifts you have to refund.
6.) User uploads
Without a registered DMCA agent, which costs $6, you lose safe harbor. Statutory damages can reach $150K per willfully infringed work.
None of these cost much to fix.
All of them cost a lot to ignore.
Paste this into Claude before launch:
"Check my app for: missing age gate, externally loaded fonts, session replay without consent, marketing emails without unsubscribe and address, renewal terms not beside the subscribe button and no DMCA agent. Fix what you can and list what I need to do myself."
Not legal advice. Talk to a lawyer for your situation.
🚨 ACABAN DE DESCUBRIR UNA MANERA PARA USAR CLAUDE CODE GRATIS
Un dev subió un repo a GitHub y ya tiene 62.800 estrellas.
Su método: redirige todo el tráfico automáticamente a 61 proveedores, muchos con modelos gratis.
Lo instalas con un solo comando.
→ +1.300M tokens gratis al mes
→ Si un modelo cae, salta a otro
→ También con Codex y Cline
→ Desde terminal, IDE o móvil
El truco: usas Claude Code, pero por dentro corre otro modelo.
Misma herramienta. Cero factura.
Os dejo el repo abajo.
Quand on se lance dans des app, on consulte les règles et textes de loi, surtout quand on traite des données aussi sensible afin d'éviter d'interpréter a sa manière 😅
C'est une catastrophe a tous les niveaux juste en lisant le site et vérifiant les mentions + CGU.
1. Le responsable de traitement n’est pas identifiable
- Les mentions légales indiquent que l’éditrice, personne physique, ne rend ni son nom ni son adresse publics (possible vis à vis du public d’après l’art. 6-III-2 LCEN). Le seul contact est le bouton « Signaler » dans l’appli. Or le RGPD impose de communiquer l’identité et les coordonnées du responsable de traitement aux personnes concernées (art. 13(1)(a), art. 4(7)) et de faciliter l’exercice de leurs droits (art. 12(2)). Une personne qui n’a pas de compte (ou dont les photos sont utilisées sur un faux profil) n’a aucun moyen d’écrire. L’exception "domestique" (art. 2(2)(c)) ne couvre pas une appli ouverte à d’autres personnes.
- Aussi pour l’hébergeur, la LCEN demande nom, adresse et téléphone (art. 6-III-1-b) : seuls le nom et le site sont donnés pour Render et Supabase
2. Données sensibles : consentement fragile
- La politique précise que le genre, l’âge, le prénom et l’orientation sont obligatoires pour s’inscrire
- L’orientation sexuelle est une donnée de l’art. 9(1), traitée sur la base du consentement explicite (art. 9(2)(a))
- Un consentement doit être libre, spécifique et distinct (art. 4(11), 7(2)
- Quand le service est refusé sans la donnée (art. 7(4), considérant 43 ; art. 13(2)(e), sa validité est discutable. - Les CGU disent « en créant un compte, tu acceptes ces CGU, la Politique de confidentialité… » : rien n’indique une case dédiée au consentement art. 9
- De plus, seules l’orientation et l’identité de genre sont qualifiées de sensibles, alors que « ce que tu cherches », les annonces Right Now, les messages et photos intimes relèvent de la vie sexuelle (art. 9(1))
3. Conservation : trop de zones floues
Art. 5(1)(e) et 13(2)(a) exigent des durées ou des critères. Ce qui manque :
- aucune règle d’inactivité (la date de dernière connexion est conservée, sans limite)
- adresse IP 'temporairement", sans durée
- signature dessinée (comptes d’avant octobre 2026) et date d’acceptation de la charte : aucune durée
- signalements : seule la durée des 20 messages joints est donnée (1 an après décision), rien sur le signalement lui-même
- sauvegardes : « effacé immédiatement » à la suppression du compte, sans mention des backups (art. 32(1)(c))
- données « Déjà rencontrée » (qui a confirmé avoir rencontré qui) : durée non précisée
4. Droits : pas de mode d’emploi
Les droits sont listés (art. 15 à 21), mais :
- aucun délai de réponse (un mois, art. 12(3)
- aucun mode d’export (accès et portabilité, art. 15 et 20)
- aucune procédure de vérification d’identité (art. 12(6)
- rien sur la limite des droits d’accès quand les données concernent un tiers, par exemple l’auteure d’un signalement (art. 15(4). Tout passe par le même bouton "Signaler"
5. Destinataires et transferts incomplets
- La politique cite Render, Supabase, Cloudflare Turnstile, OpenStreetMap et Esri. La politique cookies ajoute cdnjs (Cloudflare) et Nominatim (OpenStreetMap) absents de la politique de confidentialité. Nominatim reçoit les adresses que les membres tapent (donnée de localisation) et ces services voient l’IP. Art. 13(1)(e)(f) et 44 à 46 : les destinataires et les garanties de transfert doivent être indiqués pour chacun. Les clauses contractuelles types ne sont citées que pour Render et Supabase. Un hébergement local de la bibliothèque de cartes éviterait déjà un tiers.
6. Incohérences entre les documents
- Cookies : "supprimer ton compte efface toutes tes données chez nous". Politique : messages signalés conservés 1 an, IP, date de charte… Les deux ne peuvent pas être vrais en même temps
- La politique parle "d’équipe de modération" (accès aux e-mails, signalements, 20 derniers messages) alors que les mentions légales décrivent un projet personnel par une seule personne physique. Qui a accès à quoi ? Si d’autres personnes y ont accès : engagements de confidentialité et accès limités (art. 28, 29, 32(4)
- "L’équipe ne lit pas tes conversations" : c’est une pratique, pas une impossibilité technique (les messages sont stockés côté serveur). Art. 5(1)(a) : exactitude de l’information
- Mot de passe "stocké chiffré (scrypt)" : scrypt est un hachage, pas un chiffrement
7. Obligations qu’on ne voit pas dans les textes
- Registre des traitements (art. 30) : l’exemption des petites structures ne vaut pas quand il y a des données sensibles (art. 30(5)
- Analyse d’impact (art. 35) : à évaluer, vu la combinaison données sensibles + géolocalisation + public vulnérable, même en test
- Contrats de sous-traitance (art. 28), procédure de violation sous 72 h (art. 33-34), protection dès la conception et par défaut (art. 25)
- Les promesses doivent être vraies : distance calculée depuis une zone d’environ 500 m, accès limités, suppression réelle (art. 5(1)(a), 32)
- CGU art. 11 : "des données pourraient être perdues" et mise en veille de l’hébergement (art. 32(1)(b)-(c) : disponibilité et restauration)
- Âge : 18 ans, mais seulement déclaratif (date de naissance). Sur des données d’orientation, le risque d’un mineur inscrit n’est pas négligeable.
#Trappes ⚠️Image exclusive du terroriste raciste de Trappes et La Verrière.
Si Kevin T. était aussi fou qu’on veut nous le faire croire, pourquoi s’est-il arrêté uniquement lorsque son arme s’est enrayée ? Sans cela, le bilan aurait pu être bien plus lourd.
@AlertesInfos@grok Les tweets sur le 24 octobre sont vachement invisible, on en trouve nul part. Penses-tu qu’il y a une censure/shadowban du sujet sur la plateforme ?