All the workshop recordings and slides from #r2con2024 are now edited and published. If you didn't had a chance to attend now it's a good time to catch up starting right from the very first day! 👉 https://t.co/8Jnqg6H3N8
🚨🚨🚨Cyberattack Alert ‼️
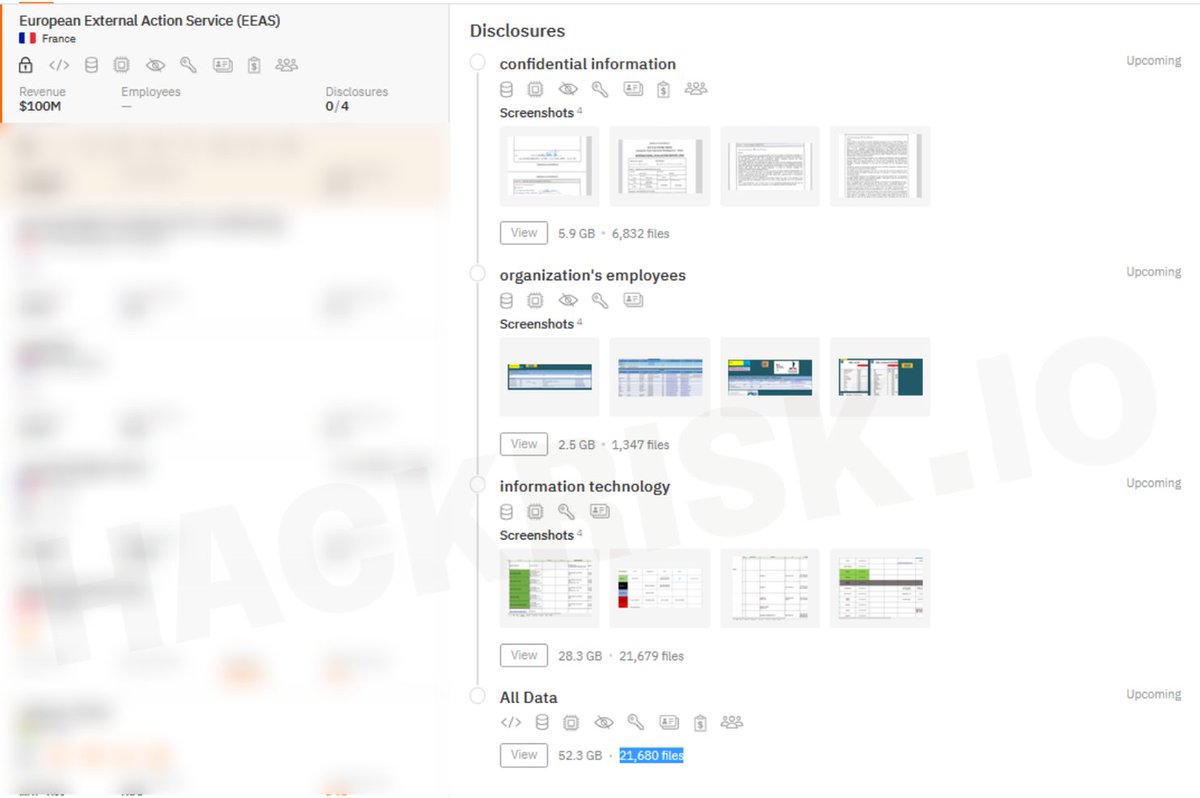
🇪🇺European External Action Service (EEAS)
Hunters International ransomware group claims to have breached the European External Action Service (EEAS), the diplomatic service in charge of executing all international relations of the European Union.
Allegedly, 52.3 GB (21,680 files) of confidential data, including employees’ data, databases, financial records, personally identifiable information (PII) and more, were exfiltrated.
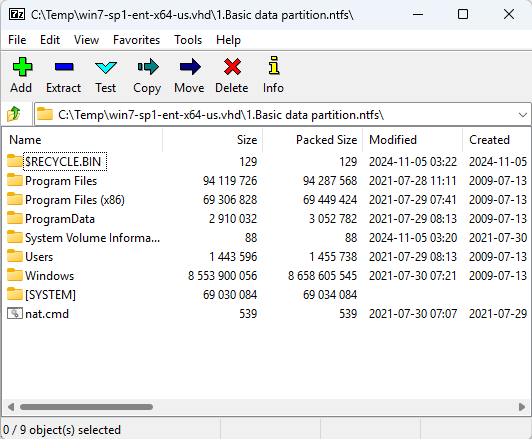
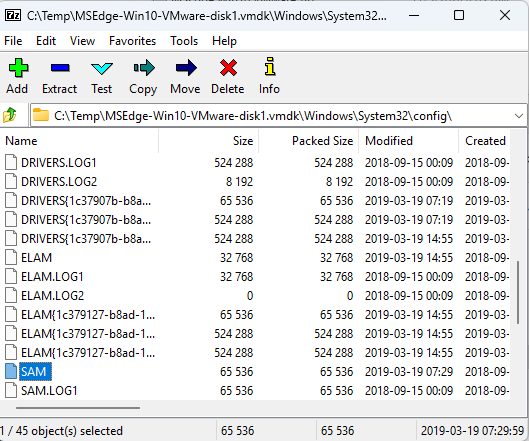
Did you know that 7z can browse .VHD and .VMDK files? You can open them right up, and even directly browse ntfs filesystems.
On a pentest and find a bunch of disk images? Copy the SAM/SECURITY/SYSTEM hives directly from the images, no mounting, copying, or fussing around.
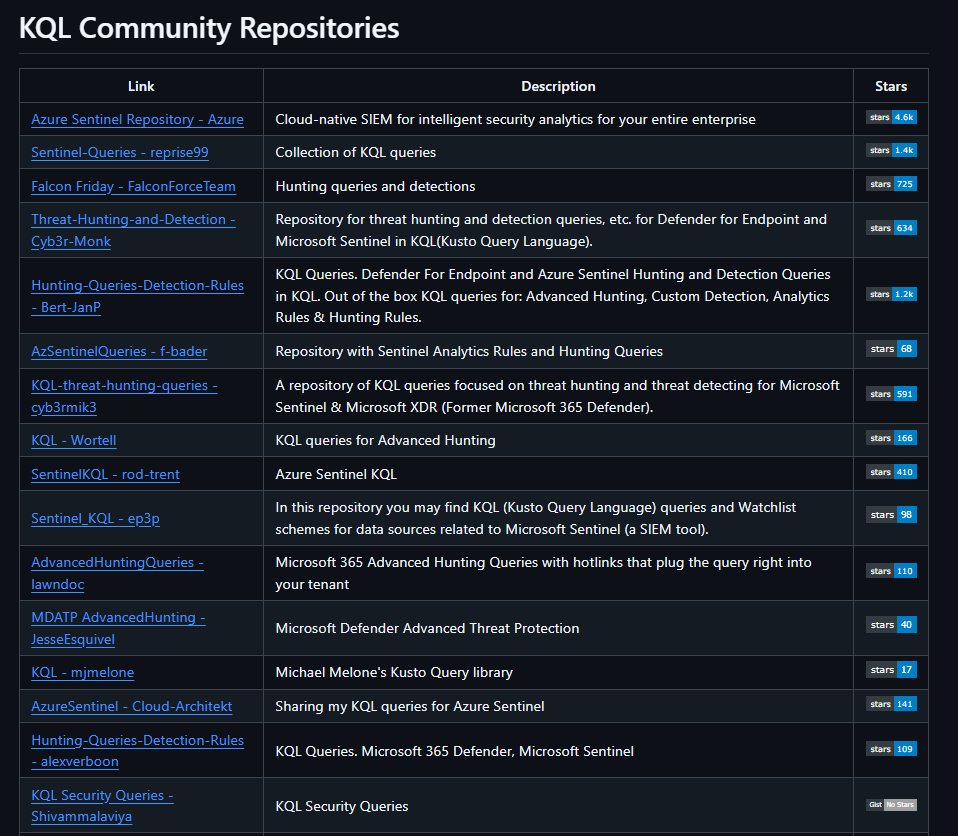
For all #KQL fans, I had this list of community repos lying around, the list now consists of 33 repos for you to investigate. Happy hunting! 🏹
Feel free to send a PR if you miss repos! :)
https://t.co/oKNZi0vmRf
Our talk from @defcon is now available! In the presented research, we document every EDR bypass technique used in the wild along with how to detect it using new memory forensics techniques and @volatility plugins. Feedback appreciated!
https://t.co/fWD57fzchj
#DFIR
Data breach at The Club Penguin Experience. Let me take a moment to point out what an awesome job these folks have done with their disclosure:
1. They sent this out the same week as the breach occurred
2. They say exactly what happened and what was exposed
3. They say “hash” and name bcrypt as the algo used (I’m giving them a free pass for then saying “encrypted”)
4. They explain how bcrypt can still be cracked and you still need to take precautions
5. They’re force-resetting all passwords
6. They offer to delete the account if this incident concerns any victims
7. Separately, they reached out to me to flag this before I had the opportunity to load it into @haveibeenpwned myself
I’m of the firm belief that in the era of ubiquitous data breaches, organisations are judged more by how they handle them than they are for having had one in the first place. Massive kudos to TCPE for such a responsible reaction 👏
„installing Wazuh agents on victims‘ devices“ … I love it 🖤
because the question is:
why use a C2 and risk detection when legitimate tools offer 90% of the functionality and usually fly under the radar of AVs/EDRs?
A very powerful exploit has been publicly disclosed today pertaining 'BattlEye', following the Call of Duty: Warzone issue.
The popular Anti-Cheat solution BattlEye was found to have a severe exploit where you are able to ban any player from any game that uses BattlEye.
Essentially you are able to falsely identify yourself as a game server by loading the BEServer.dll from a different game (for example, loading DayZ’s BEServer.dll into Escape from Tarkov). The server will connect to the wrong BattleEye backend but still act as if it’s the correct game server.
After you have access to the game server, you can then spoof any players GUID by passing their SteamID or AccountID through the GUID algorithm. Then using the spoofed GUID of the player you want banned, you trigger ban events in that game like flying, or some sort of aimbot which in return issues a global ban on that GUID, banning that player permanently.
Original post: https://t.co/9axgimd3NM
Today, the famous hacker known as USDoD was arrested by the Brazilian police.
The FBI had a way to find his identity and home address since at least June 2022. I will show you how.
It's OSINT time! ⬇️
What people often overlook in #DetectionEngineering is that there’s no "one-size-fits-all" rule to detect a threat. It depends on your goals.
How specific should the rule be? Are you tracking a threat actor, detecting the tool/malware, or focusing on the technique? Should it be based on code, content, form, or metadata?
Just like in art, you can create an abstract, impressionist, or realistic painting of the same subject, and all can be masterpieces in their own right
The cycle of the malware researcher:
> randomly appears on social media
> showcases their research
> publishes a few high quality articles
> gets offered job
> disappears
> no more public research
We've seen this probably 50 times now, no exaggeration.