I wasn't going to blog about this bug since it is quite trivial, however, eMudhra released an advisory where they wrote some nonsensical gibberish trying to downplay it. So, here it is (CVE-2026-125659): https://t.co/Tz8CeklSuP
🚨 New: I analyzed millions of rows of voter rolls from Karnataka to understand who the SIR removed, kept in and added back. Does the claim of "No eligible person left out" hold up? Not really.
Read my in-depth analysis with charts and examples. LINK IN REPLY.
Meta tells govt it acted on 61k ‘inciteful posts’ in 2 weeks; claims 95% drop in AI content on platforms
Vrinda Tulsian @vrinda_tulsian reports for ThePrint
https://t.co/MBVhOjZmNA
⁉️ India exempted an Israeli phone-hacking company from its own rules, allowing it to sell phone-extraction products and surveillance technology to government agencies.
A review of documents — published by brilliant folks at @internetfreedom — reveals that India’s expansive surveillance capabilities extend far beyond just cloning phones and extracting data without passwords ... to accessing cloud-based data from social media platforms – such as Instagram, Telegram, and Tinder – as well as data from connected devices such as Amazon’s Alexa and Google Home !!!
In one instance, Delhi Police demanded “all-in-one” system to access more than 100 cloud services, including Google, Apple, WhatsApp, X, Discord and dating platforms such as Tinder, Grindr and OkCupid, or platforms like Slack and OnlyFans, using account credentials or login tokens recovered from devices.
Read this report @AJEnglish for details: https://t.co/A12o2RmwzL
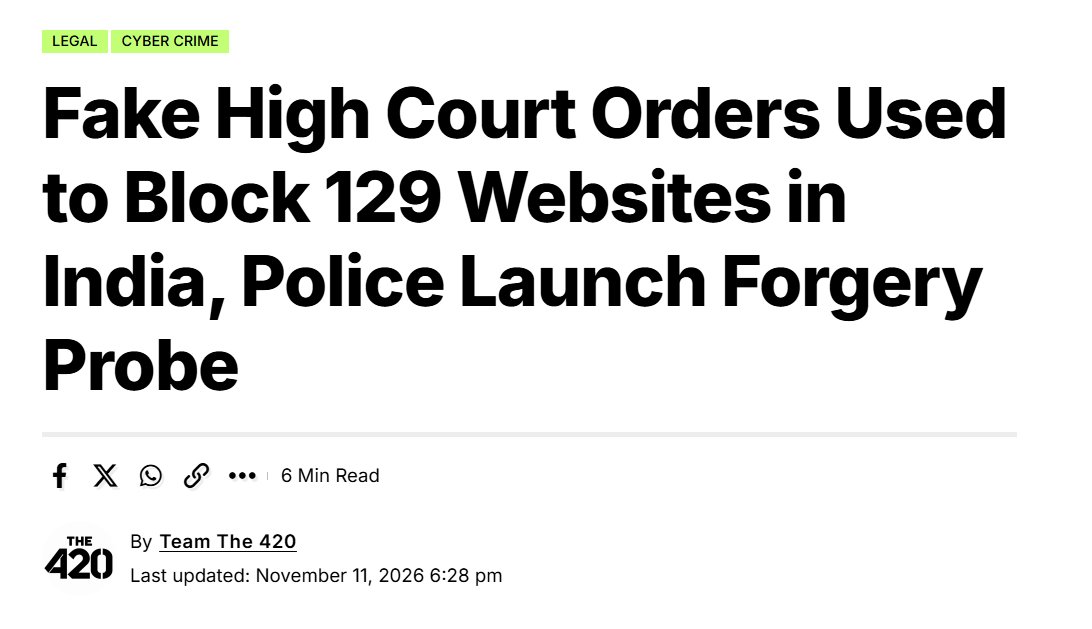
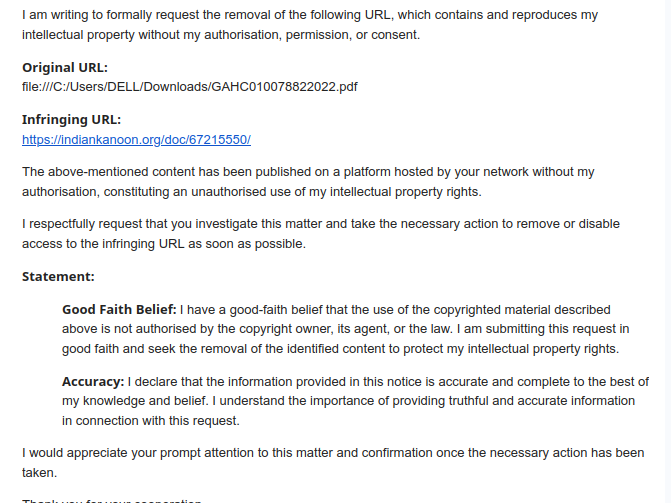
Censorship under Modi-Shah has come to a point where websites are being taken down based on FAKE court orders.
No other country in the world gives the govt such immense powers to take down content.
Question is: why did the IT Ministry not even bother to verify the so-called court order? Or is this a new dirty tactic for censoring content as long as the govt doesn’t get caught?
Beyond scary.
‘NO SUCH ORDER PASSED BY HER LADYSHIP’
India’s government ordered blocking of 100+ illegal betting websites based on two court orders. But @Reuters has found the court orders were fake.
The two court orders carried blue court seals, a fake QR code and made-up case numbers such as “Writ - A 30480/2026”. They were sent by individuals who claimed to be lawyers, and asked for immediate implementation by Indian government.
The government sent them to internet providers to take down websites. The forgeries are the latest sign that fake orders are slipping past India's official content removal mechanism, considered one of the world's strictest
Following questions from Reuters, Uttar Pradesh police have opened a forgery investigation after Reuters queries to the Allahabad High Court, while the Rajasthan High Court told Reuters in an email the order did not exist on its server.
Who sent the orders to the government & how did officials order takedowns? Read.
https://t.co/PCt4sD4yXI With @MunsifV, edits @Saad_Scrawls
People too polite to say it.
No other reason other than to deliberately weaken the cert signing process so that this can used for MITM purposes.
They could have done bunch of other things that would have been far too difficult to detect.
- Keys that were weak in a way they knew about it instead of 4
- Generated certs for domains that aren’t so popular. Not everyone is watching for such issuances
- maybe code signing certs
- maybe it’s meant for devices who don’t do revocation
Guessing this isn’t something they do normally. Got forced and the moment faced scrutiny decided to leave the business altogether.
Curious thing for me is how come they had an entire CA business just for a few customers.
eMudhra disabled FIPS on the HSM, exported the private key into Python on a computer, and then it got truncated when they re-imported it
I have to admit I did not realize CAs were running HSMs with the ability to do this. How many CAs are exporting private keys to computers??
AQI 'Manipulation' Row | TIMES NOW Investigation Findings
- 'No hourly readings across 52 monitoring stations'
- 'Large-scale blackout on Diwali night'
- 'Only 7 of 59 stations reported proper data'
- 'All 59 stations were fully functional at 8 PM on Nov 8'
- 'Data blackout from 9 PM on Nov 8 to 6 AM on Nov 9'
- 'Data stopped after pollution levels approached 1,000'
‼️ A group emailed a security researcher offering $300 in crypto per bug to add its name to the credit on Microsoft, Apple and Google flaws.
It calls itself the Global Cybersecurity Alliance, or GCSA. The email, signed "Wang GCSA" under the subject "Paid Title Sponsorship", sells the service as "sponsored attribution" at 300 USDT per record.
Payment comes once the CVE, the official ID a confirmed flaw gets, is approved. The sender even offers to "pay in advance."
"Oh we're buying CVE authorship now," wrote veteran security researcher Kevin Beaumont.