Works @Automattic on @WooCommerce. 15+ years of online ecommerce & development experience. Passionate about helping online businesses grow and succeed.
The company behind WordPress just built a home for whatever your chatbot makes.
Spacefast by @automattic: ask Claude, ChatGPT or Cursor to publish it and you get a live link back.
https://t.co/plJ1Wj0dWj
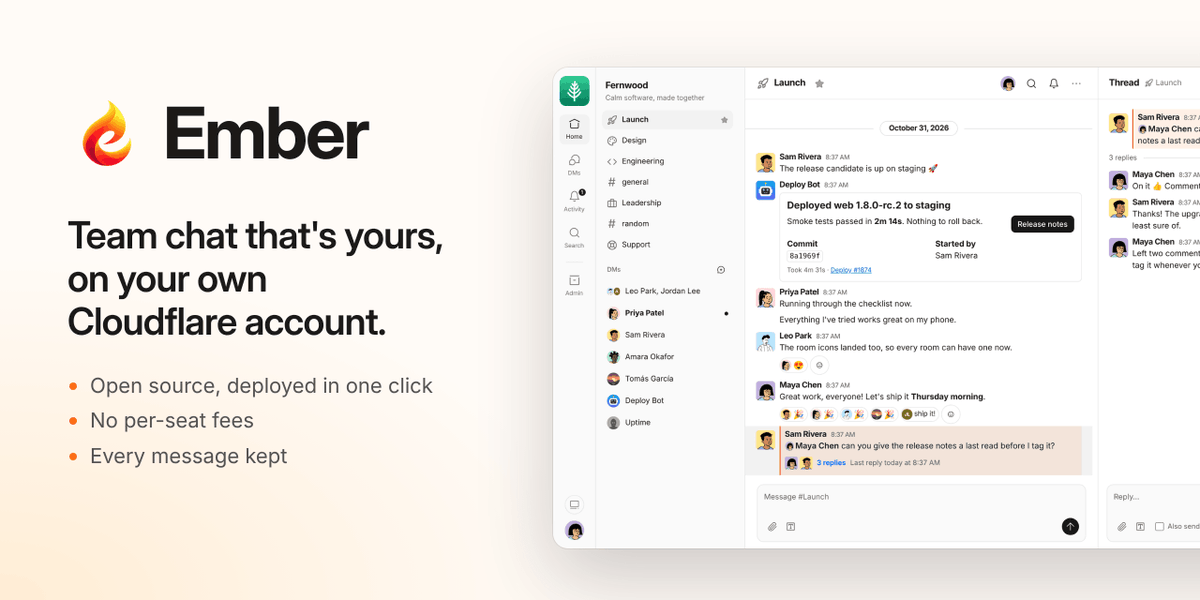
Want your own Slack for $0? I open-sourced Ember. It deploys to @Cloudflare’s free tier in about a minute, works with Slack-compatible payloads, and includes an AI assistant and media attachments.
Melbourne cosmetics entrepreneur Briony Kennedy has faced bankruptcy after her $6 million sustainable skincare company Adorn Cosmetics collapsed following a failed website migration to Adobe's e-commerce platform. Adobe has declined to comment on the case for legal reasons.
Plugin Check 2.2.0 is out 🚀
The big one: .pcpignore. You can now exclude folders like vendor or tests from the scan and run Plugin Check in your CI without false positives.
A thread 🧵👇
Introducing Personal Finance in Claude, in beta in the US.
Connect the accounts you choose, and Claude answers your money questions in everyday language, from your own balances and transactions. Access is read-only, and Claude can't move, manage, or invest your money.
‼️ Apps built with the AI app-maker Lovable left passport numbers, payment information and 200,000 chat messages open to anyone, no login needed.
German security firm Crissy Field scanned 159,041 Lovable projects and found databases with email addresses readable on 7,403 sites.
Lovable promises no coding skills are needed. Its terms make customers responsible for their apps and data.
Lovable told German business daily Handelsblatt the problem is industry-wide.
Fake job interviews, personal photos to build trust, and 0-day malware disguised as an assignment. The timeline of the Binance security incident proves that the most sophisticated exploits still rely heavily on highly targeted human deception.
To sum up today's news:
- Reddit stock is down because of AI answers
- Google stock is down because of AI answers
- Your web traffic is down because of AI answers
Happy to see that worked out well for all parties involved
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
https://t.co/ywB2mKFy0p
@WPTutz@MattReinholz@WordPress I shared some thoughts on this very subject yesterday. Rather than taking every piece of software in the world offline, it's going to be about leaning into platforms that can automate, triage, and patch at machine speed, which WordPress is doing!
https://t.co/p2WYdLkaDN
Setting up WordPress on most any host: click a button.
Setting up @EmDashCMS on the same box: npm create, Git repo, SSR mode, Node 22, encryption key, SITE_URL, workerd if you want the sandbox, then remember to back up the SQLite file yourself. *IF* your hosting even permits you to do that kind of thing.
Just sayin'.
Lots of posts lately say to leave #WordPress because of all the security fixes. The cause is AI finding bugs faster in everything and reports to the WordPress security team went from 20 to 30 a month to 773 in August. My take on this
https://t.co/p2WYdLkaDN
@mattmedeiros Me neither; it seems like a very narrow view of the overall challenges that projects and businesses across the board are facing right now. AI security discoveries are becoming more prevalent each day due to technological advances 🤷♂️
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2.
PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.