Most STT scales by adding compute.
We asked: what if the pipeline was optimized?
→ 220×+ throughput on one commodity GPU
→ <9% WER
Built for large archives without hyperscale infra.
Onboarding early design partners → https://t.co/UKou2MCIfO
#SpeechRecognition#AIInfrastructure
@thedawgyg AHAHAHA I'm laughing to not cry, the world i fucked up, not only they treat you bad, they want to tell you what to do with your own life aswell
@hakluke@simonkoeck how do you guys coop with the fact that lots of programs don't value your work at all, ignoring reports, fixing bugs in the hidden and ignoring you?
🤯 Someone has released a dataset with over 23,000 smart contract security audit findings, free to download
Severity, proof of concepts, recommended fixes, everything is inside - it's a GOLDEN MINE. Thank you @RightNowIn - amazing contribution🔥
https://t.co/ejmuCuCkRK
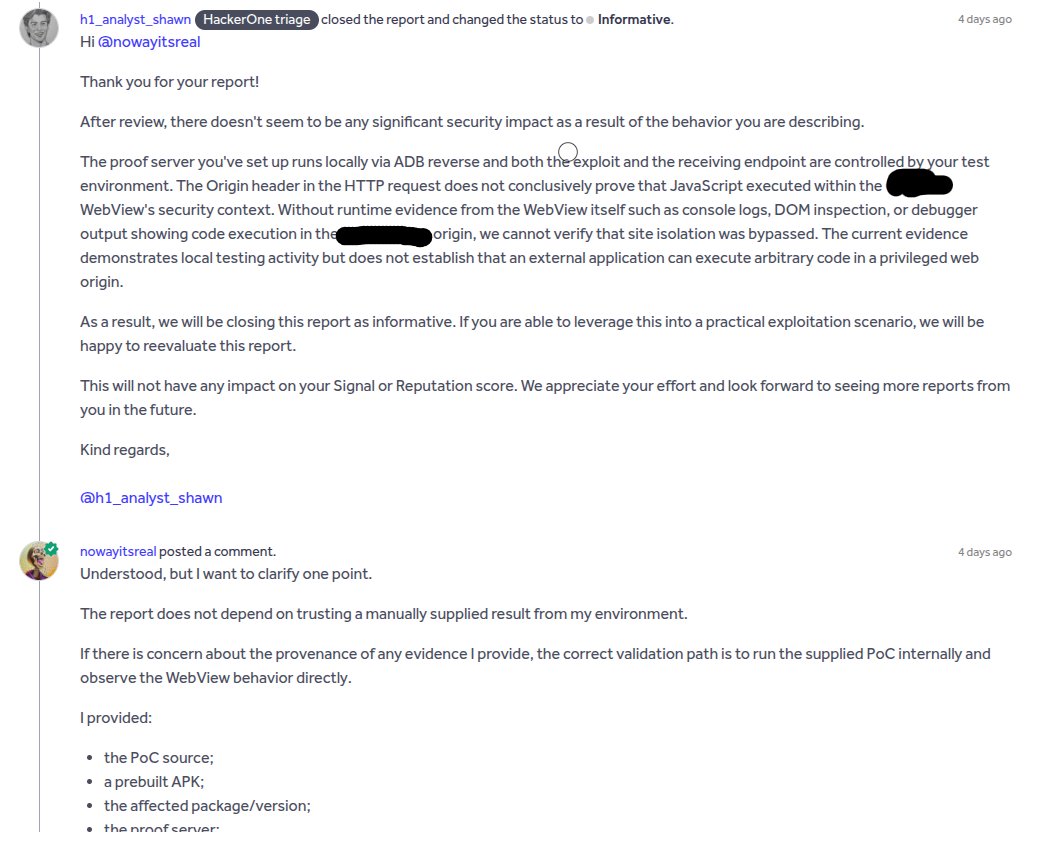
@siratsami71@Hacker0x01 "The Origin header in the HTTP request does not conclusively prove that JavaScript executed within https://t.co/b9xZOH7zOo" ..?WTF Anyway later I attached a recording with a debug log with the origin proof, and still didn't get an answer... and remains closed as informative
@siratsami71@Hacker0x01 "The Origin header in the HTTP request does not conclusively prove that JavaScript executed within https://t.co/b9xZOH7zOo" ..?WTF Anyway later I attached a recording with a debug log with the origin proof, and still didn't get an answer... and remains closed as informative
@lukashanren1@siratsami71@Hacker0x01 leaving it like that is wasting time. He has done the research and it has to be valued!
If it is not, it was wasted time!
And here I am, having reported vulnerabilities throughout my career that could have resulted in a total of several billions (yes, with a B, > $2B) being *stolen*, while my total earnings are around $2M.
So what's the lesson the industry is teaching researchers?
That next time we should steal the funds first, then negotiate a "responsible disclosure," return 80–90%, and walk away with 10–20%?
Obviously, no. But it's insane that the incentives can make that rhetorical question even possible.
The bounty world is broken.
Blackhats exploit a protocol and get treated like kings in negotiations. Meanwhile, whitehats disclose the exact same kind of vulnerability privately, prevent any damage from happening, and then spend months arguing with projects that try to downgrade the finding and pay the bare minimum.
I'm fighting several cases like this right now. Millions of dollars protected, vulnerabilities responsibly disclosed, and yet projects still don't want to pay the amounts they themselves advertised.
We should be making responsible disclosure the overwhelmingly obvious choice.
Instead, the current state of Web3 is doing its absolute best to discourage whitehats while creating increasingly attractive incentives for blackhats and "grayhats".
Those incentives are backwards, and eventually the ecosystem pays the price.
@Hacker0x01 I showed him origin:https://t.co/REem66Ff0D, but he was suspicious of my setup, like I gave you all the details to reproduce!! @Hacker0x01 who hired those people??
The same happened with @Hacker0x01#bugbountytip#bugbounty#bugbountytips
I gave complete PoC + screen recording, but they closed it as informative because it wasn't a real impact...
like what the heck I just showed you a universal xss!!!
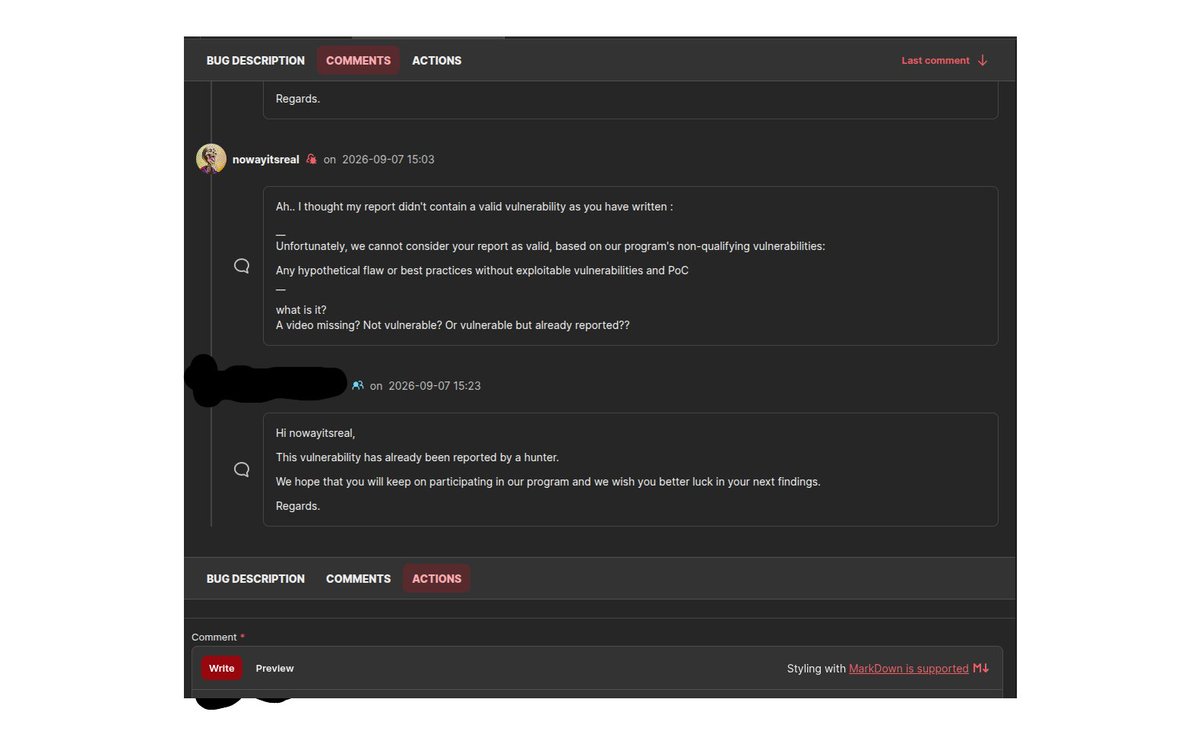
@yeswehack#bugbounty#bugbountytips#bugbountytip
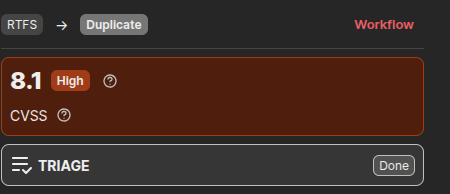
From not vulnerable to duplicate in 5 minutes, sounds suspicious!!!
Lately I'm getting lots of similar results from different bug bounty platforms and programs is the field dying?
It is becoming really frustrating...