I’m usually out hunting for an adrenaline rush or a good night’s sleep. IR consultant, Python junkie, and a writer at heart. Incident Engineer at @Careem
“Detection & Compromise: Secrets from the AWS Secrets Manager” — my recent article on detecting a secrets compromise on the AWS cloud. Happy reading, folks! Don’t forget to drop your feedback.
https://t.co/9QIvPB53tQ
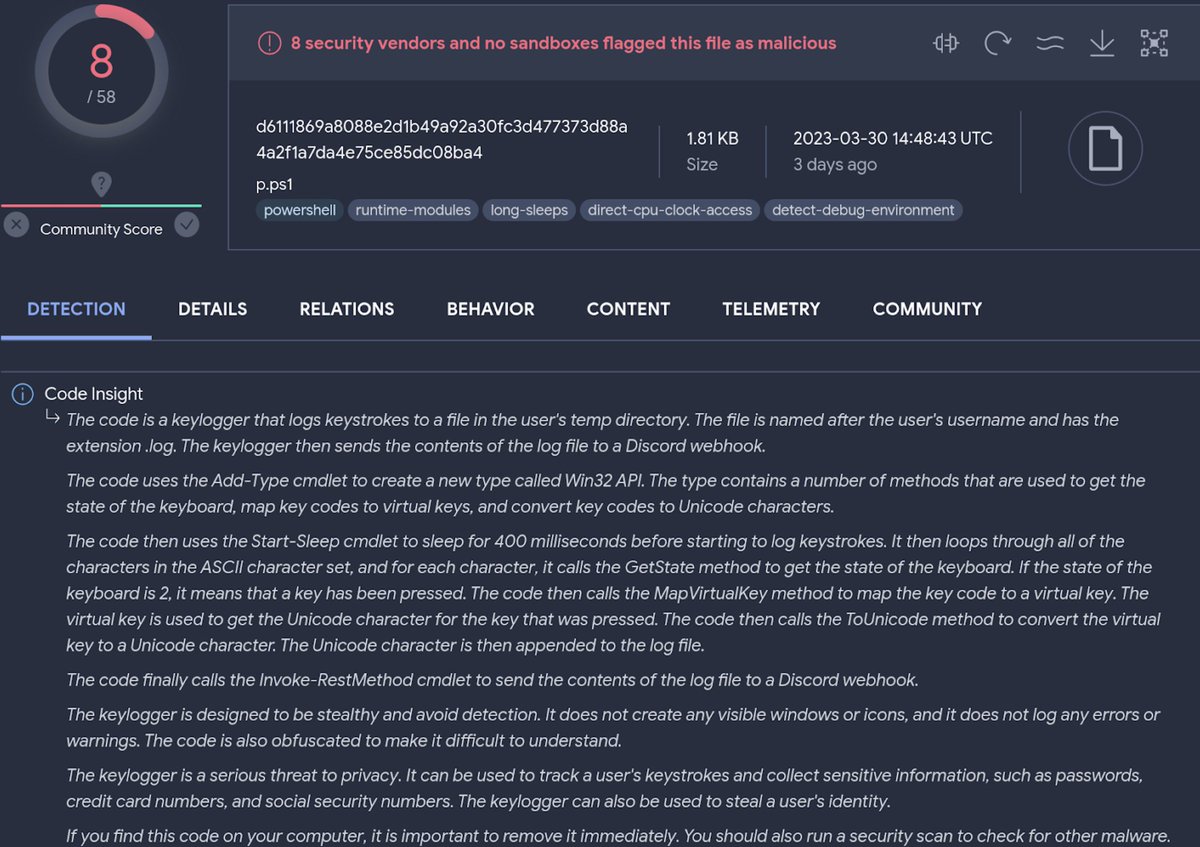
Introducing VirusTotal Code Insight: empowering threat analysis with generative AI. This tool is based on Sec-PaLM (LLM) and helps explaining behavior of suspicious scripts. Code Insight is available now for all our users! More details by @bquintero: https://t.co/TjPJxDWu6T
Just published a new blog post inspired by @lizrice's book "Container Security". In the post, I explain how root inside a container and on the host essentially mean the same thing. Check it out!
https://t.co/h4fUKVrkI1
Bing subreddit has quite a few examples of new Bing chat going out of control.
Open ended chat in search might prove to be a bad idea at this time!
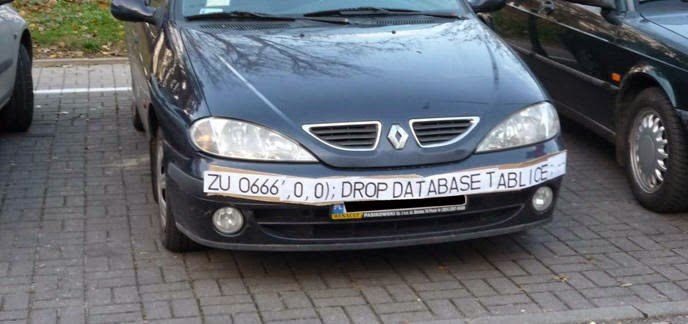
Captured here as a reminder that there was a time when a major search engine showed this in its results.
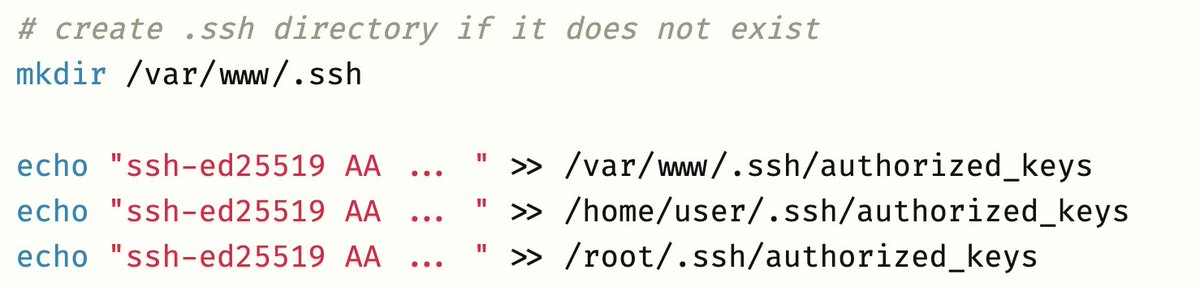
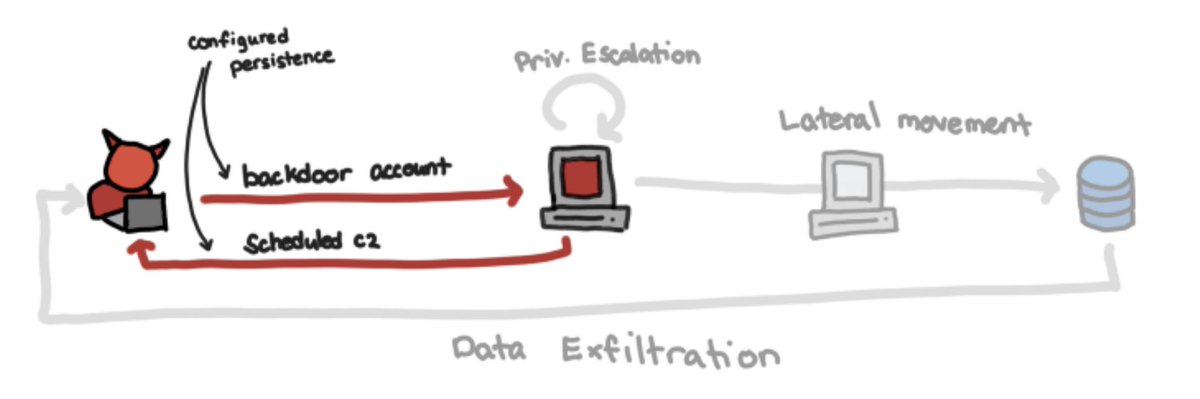
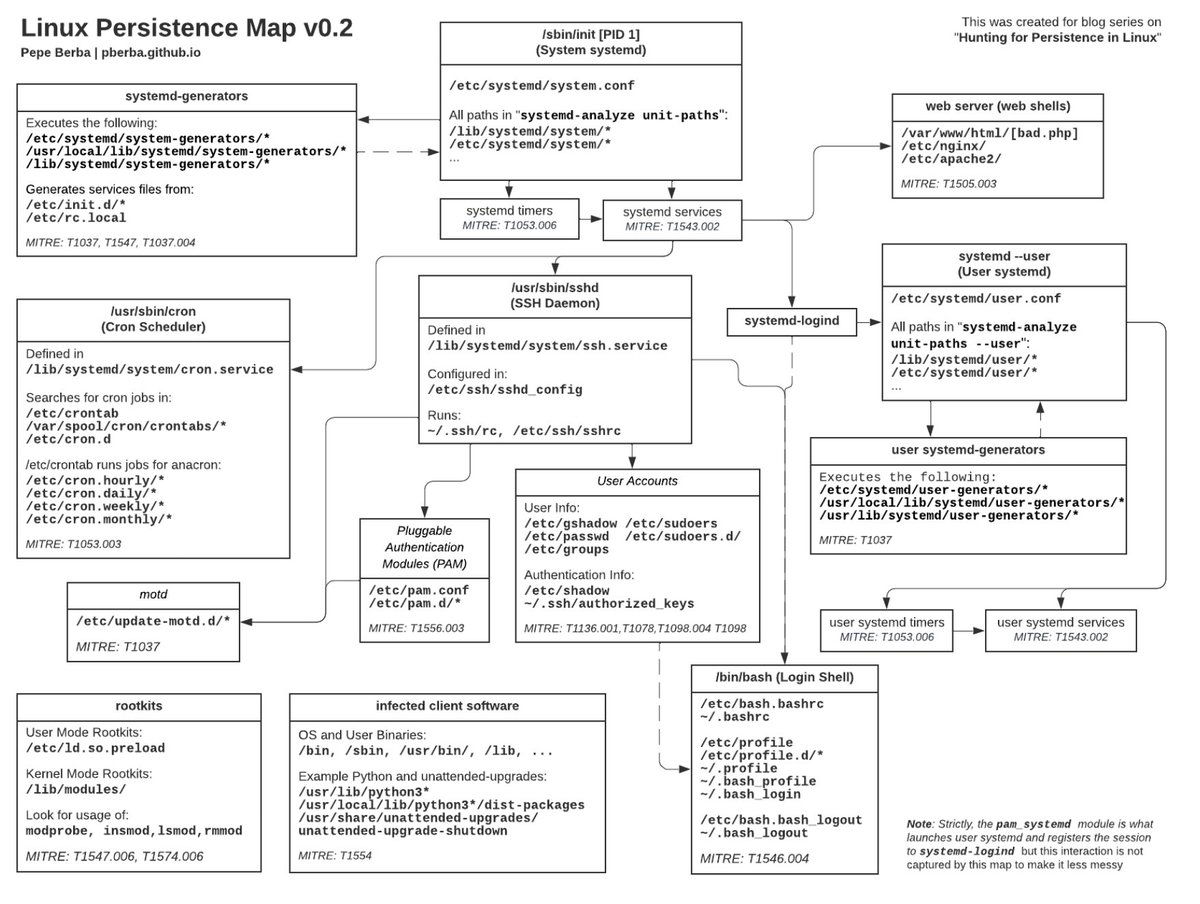
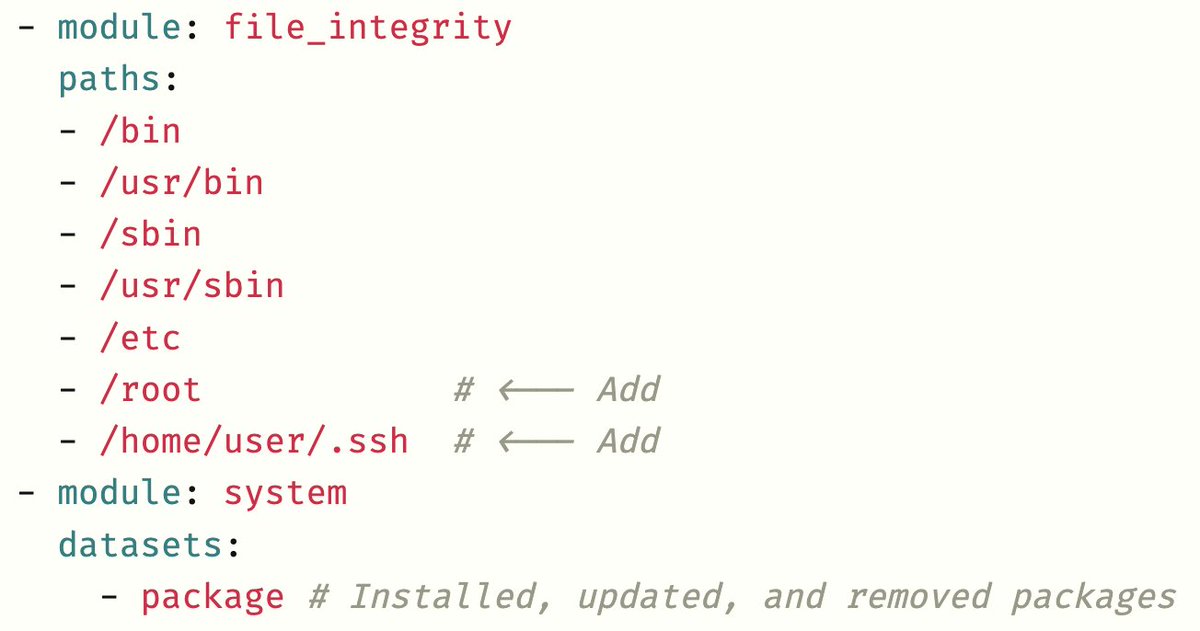
Very cool series by @__pberba__ about persistence in Linux environments
Persistence map: https://t.co/8KaO3celxe
Auditd, Sysmon, Osquery: https://t.co/YFlzhgrWjX
Account Creation and Manipulation: https://t.co/ZbQDAbSHf3
#Linux#kernel#malware#infosec#cybersecurity
I hope this scenario demonstrates the value of having a lab to play around with. Here, you'll want to play around with starting/stopping the event log service if you haven’t before. It’s all about identifying novelty, seeking to understand it, and carrying that knowledge forward.
Tried sharing a breakdown of my thought process while solving the cryptography challenges from 2nd National Cyber Security Hackathon.
Feel free to reach out if you have any questions :)
https://t.co/A0xG0GwhSu
✨ Introducing `plz`, an AI-powered command generator. Kinda like copilot, but for your terminal.
It's ideal for all those weird unix commands that take dozens of flags, and you never know which ones to use (like ffmpeg).
(takes one command to setup 👇)
https://t.co/pKxZ9C51uk
How Great Leaders Inspire Action
By Simon Sinek (@simonsinek)
An exploration of how the best leaders inspire action, cooperation, trust, and meaning through a very simple question: “Why?”
https://t.co/39dKZfkZyj
Don't forget to parse and analyze all SUM databases located at “C:\Windows\System32\LogFiles\SUM" in a post-mortem forensics analysis (involving a domain machine).
You can find:
- authentication history within a domain
- DNS history of domain
And much more!
#DFIR#DFIRtips
1\ #DFIR: How to investigate insider threats
Sharing the forensic methodology I follow when I'm investigating insiders 😍
This is where an employee sells creds/changes configs/runs malware leading to full DA compromise and then say they didn't do it O_o
https://t.co/k6cIXfcqCq
If you're like me and tired of seeing #Qakbot#NetSupportMgr#Bumblebee etc malware delivering an .iso drop this reg value to prevent the simple 'Double-click' to mount attack vector
[HKEY_CLASSES_ROOT\Windows.IsoFile\shell\mount]
"ProgrammaticAccessOnly"=""
#malware
The scope of this attack demonstrates another problem with centralizing authentication. It can often be a single point of failure that can give attackers a wide variety of access, as we've seen in this example. USE PHISHING RESISTANT MFA!! Stop making it easy for attackers. 12/N