This one was really tough, but exciting and I loved solving the challenges. Diving deep into the web, reviewing 1000s of lines of code, chaining exploits and fully automating them, this was a wonderful ride.
Thank you @offsectraining for an expert level course 🙌
#oswe#infosec
Thrilled to welcome @techhacker98 (aka Bitten Tech), Senior Security Analyst at @HackerOne, to the stage this 22–23 August at PIET Campus! 🏰
🎤 Talk: Beyond the Bug - The Anatomy of Impact Hunting 🔥
🎟️ Passes: https://t.co/eFwTgdtpgP
#BSidesJaipur#BugBounty#BittenTech
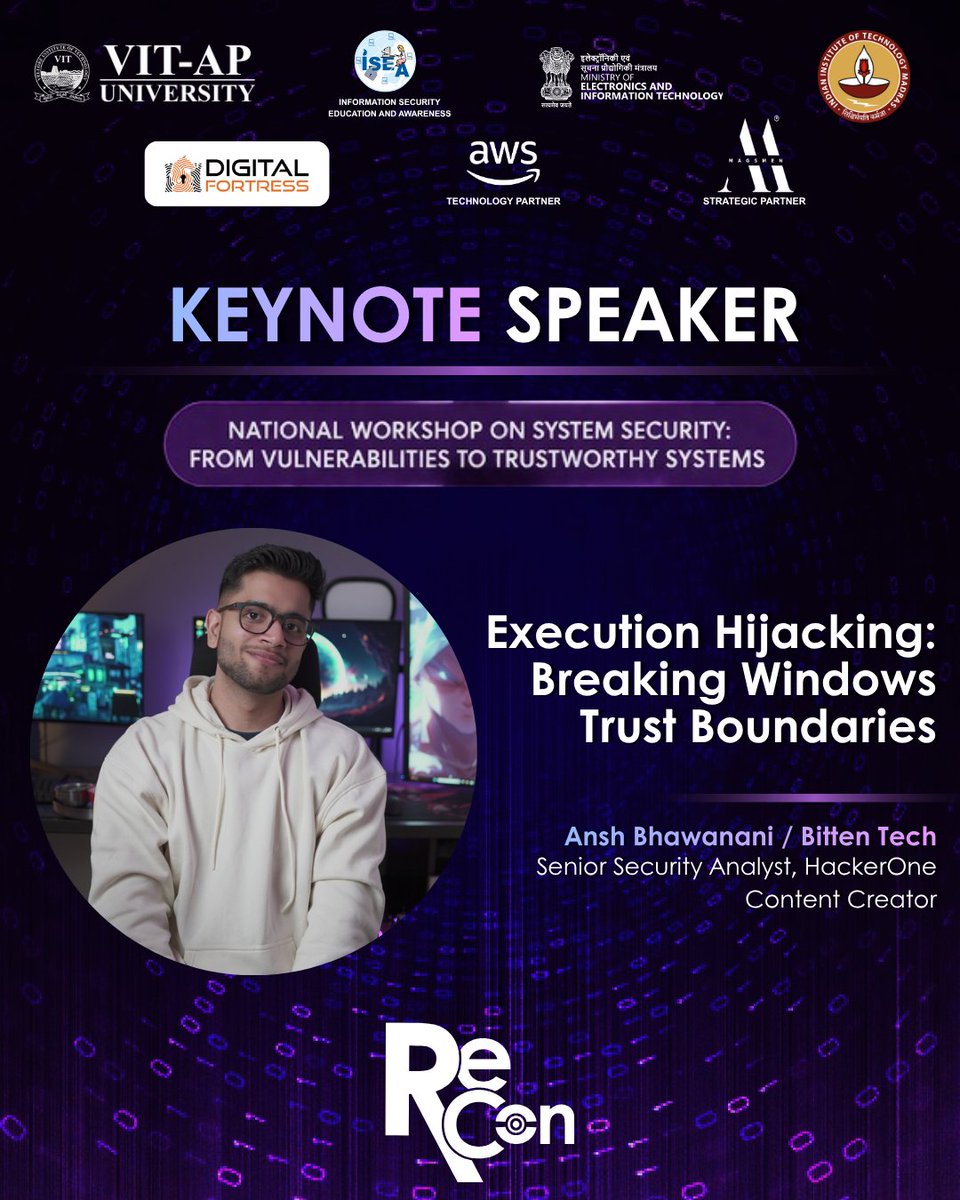
🚨 KEYNOTE SPEAKER REVEAL 🚨
Welcome to RECON 2K26, @techhacker98 , we're SO ready for this one! 🔥
Ansh Bhawanani is a Senior Security Analyst at @Hacker0x01 , an OSCE3-certified app security specialist, a hands-on vulnerability researcher, AND the content creator breaking down offensive security for the masses on YouTube. The guy makes the hardest concepts feel learnable💥
His keynote? Buckle up:
🎯 "Execution Hijacking: Breaking Windows Trust Boundaries"
Windows internals, trust abuse, real-world exploitation, this is going to be an absolute masterclass.
Stay locked in for more drops:)))
#RECON2K26 #CyberSecurity #ethicalhacking #offensivesecurity #redteam #bittentech
Most people think developers ignore security, but what they really ignore is friction.
In AppSec we are always taught to keep a balance between compliance and delivery. Finding a critical cannot necessarily block a release.
For the stakeholders, business velocity > security.
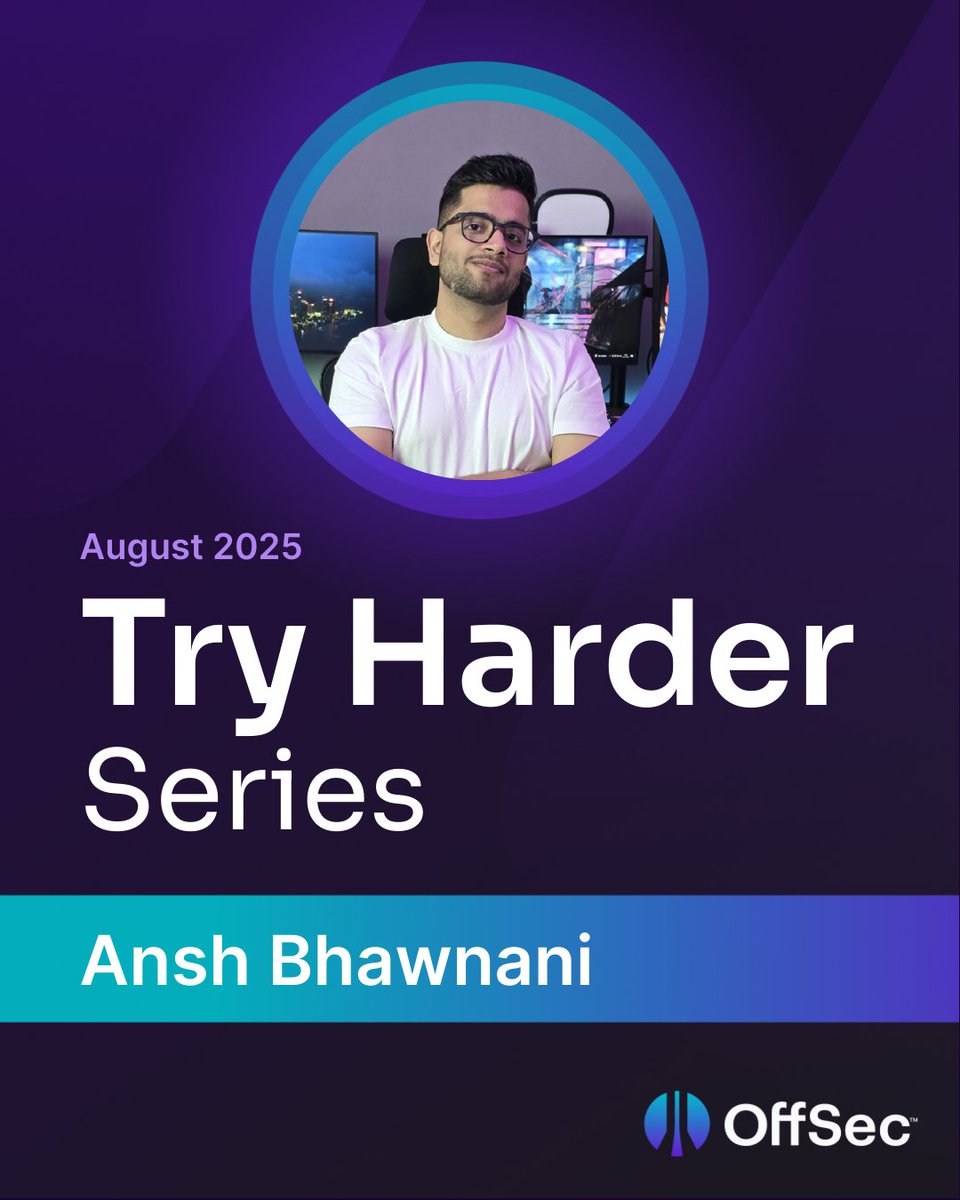
Congratulations, Ansh Bhawnani! 🦊👏
To continue with our Try Harder monthly series, we're celebrating dedicated individuals who embody the spirit of #TryHarder. This month, we’re recognizing Ansh, who just passed OffSec's OSED exam, completing the OSCE³ trio (OSED, OSEP, OSWE) 🪙
"This was about pushing myself to the limit, through fear, doubt and everything unknown. Thank you to OffSec for an awesome course and a breathtaking exam."
💪 Want to be OffSec's next #TryHarder hero? Tag us in your success story to be considered for a feature 🏷️
Is bug bounty a realistic full-time career in 2025? 🤔 My friend's
@techhacker98
awesome video, 'Reality of Bug Bounty 2025' by Bitten Tech, dives deep into the challenges & opportunities! A must-watch for aspiring bug bounty hunters! Reality of Bug Bounty 2025 https://t.co/Yx58mpgmYG #bugbounty #cybersecurity #ethicalhacking
Read “Unauthenticated Kibana Dashboard Access — A Serious Security Risk You Can’t Ignore“ by Pratik Dabhi on Medium: https://t.co/zZgpVx0luT
#bugbounty#infosec#hacking
The same people concerned about their privacies are happily posting their artistic photos all over the internet.
I mean the evolution is great and exciting but the right way to do it is not to train those public AI models with your personal stuff.
#RatanTata is the World's Biggest Donor.
He has donated ₹829,734 crore.
Built multiple free hospitals, schools & saved millions of lives.
Today, on his death, the whole world is crying.
Some unheard instances of Mr. Tata that will make you cry: 🧵
Five activities every web hacker should do at least once:
1. Read the source code of an HTTP request parser
2. Write a small web application with registration, authentication, file upload...
3. Read an RFC
4. Participate in a Capture The Flag competition.
5. Fix a vulnerability in an open-source project.
#NCIIPC is looking for expert pen-testers, security researchers and ethical hackers to secure nation's CIIs. Join NCIIPC scheme for Crowdsourcing of Pen Testing of CIIs.
The Okta hack that keeps on giving!
Cloudflare announced a new data breach today in it's continued battle against creds stolen during a previous Okta hack
Let's dig in:
Daily Notes : Day 79
File Upload Escalation:
1. Set filename to ../../../tmp/lol.png and try to achieve a path traversal
2. Set filename to sleep(10)-- -.jpg and you may be able to achieve a SQL injection
3. Set filename to <svg onload=alert(document.domain)> to achieve a XSS
4. Set filename to ; sleep 10; to test some command injection (https://t.co/Ie1zZ2heCu)
5. JS file upload + XSS (https://t.co/N6Pdi2LahK)
6. you can indicate the web server to catch an image from a URL you could try to abuse a SSRF. If this image is going to be saved in some public site, you could also indicate a URL from https://t.co/SxO5uMQB2n and steal information of every visitor.
Reference: hacktricks
The new year is almost here, don’t forget to add the following to your password cracking/spraying lists:
Spring2024
Spring2024!
Summer2024
Summer2024!
Winter2024
Winter2024!
Fall2024
Fall2024!
Password2024
Password2024!
Companyname2024
Companyname2024!
This one was really tough, but exciting and I loved solving the challenges. Diving deep into the web, reviewing 1000s of lines of code, chaining exploits and fully automating them, this was a wonderful ride.
Thank you @offsectraining for an expert level course 🙌
#oswe#infosec