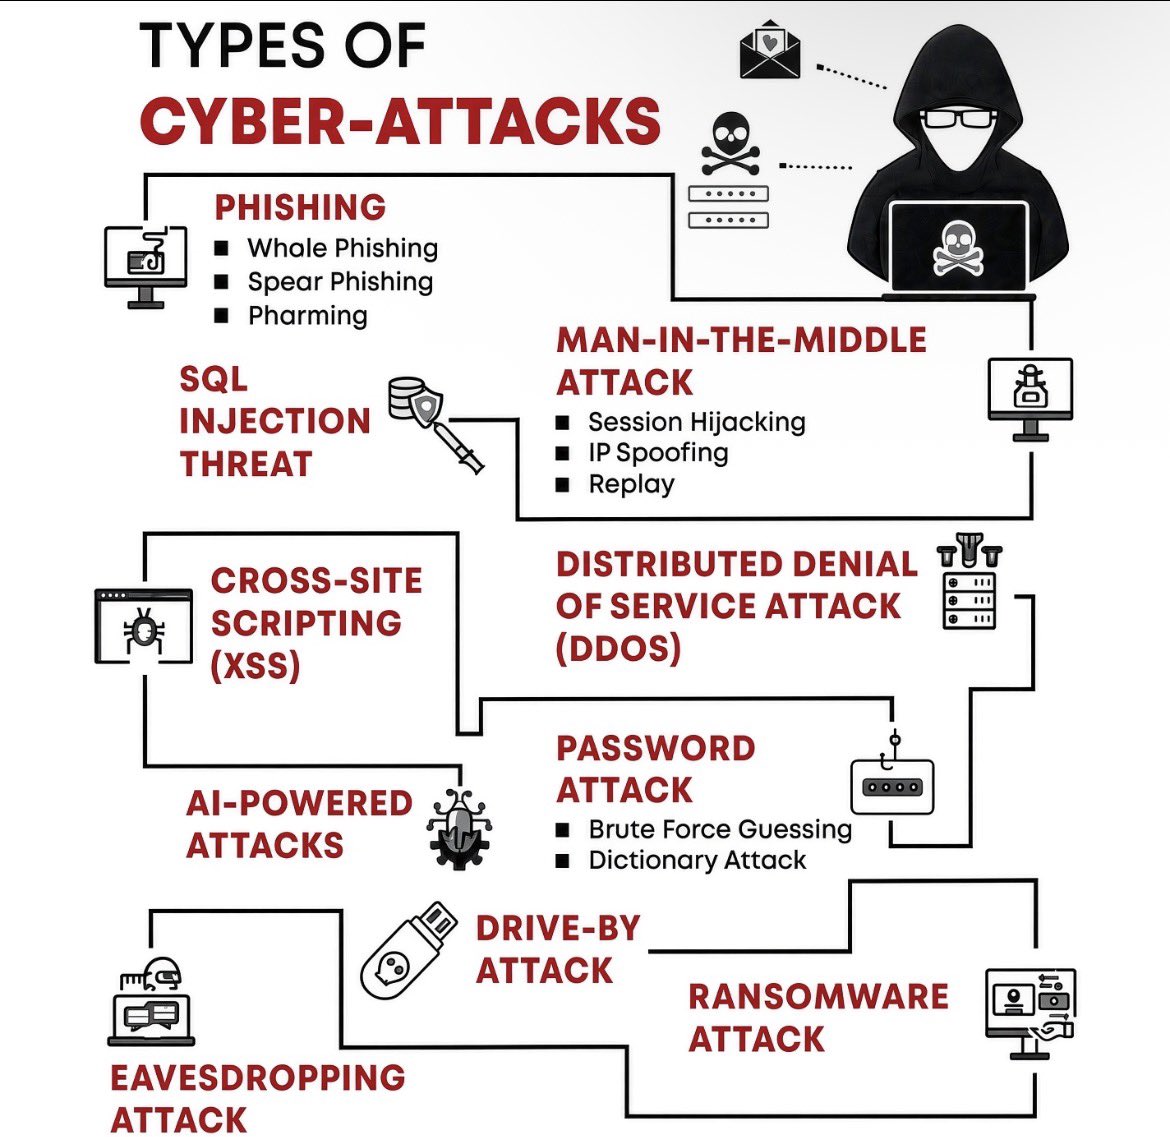
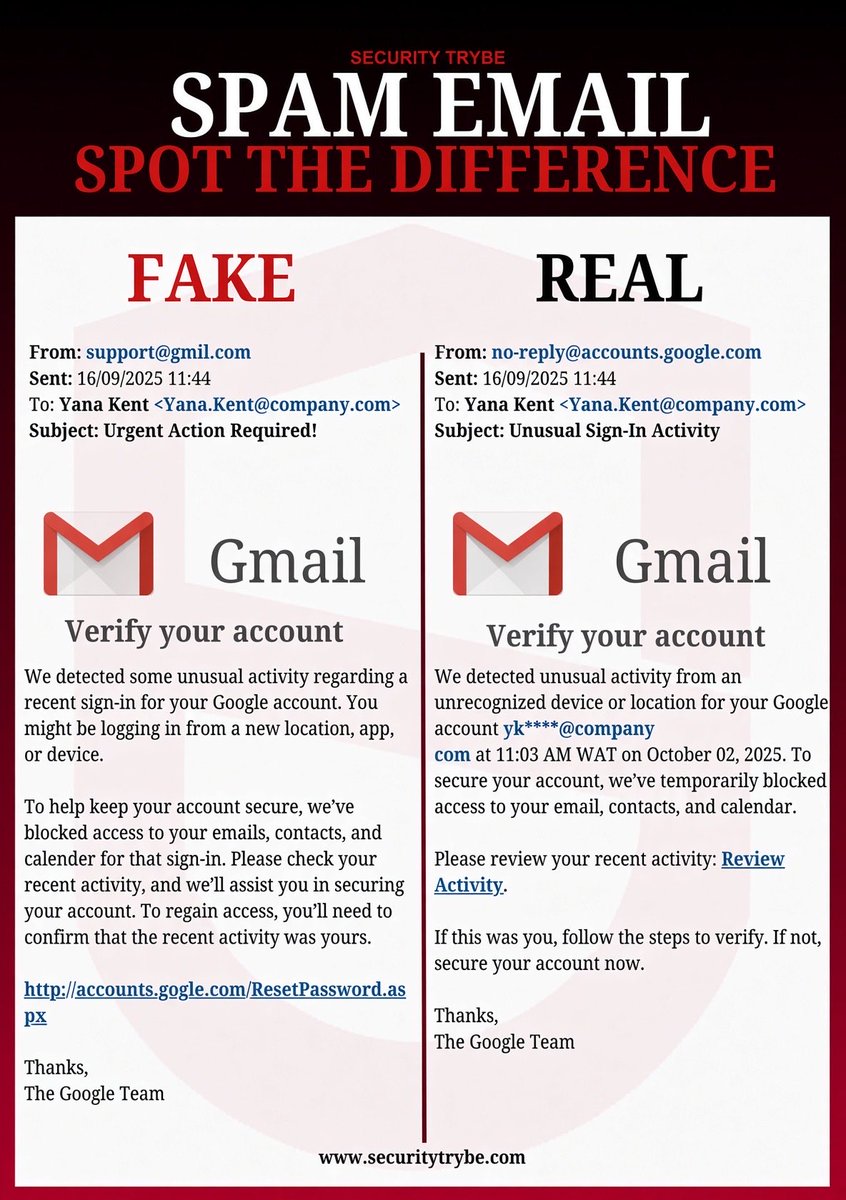
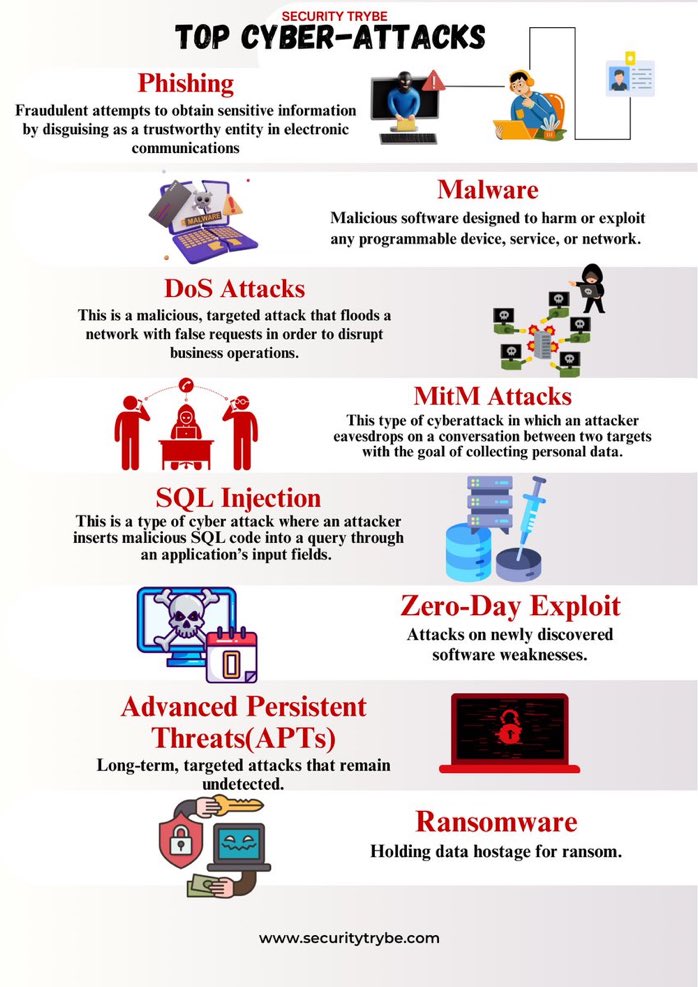
Tip #6: real or fake? Three quick checks before you tap. 1) Urgency or threats, like “act now or lose your account”: deadlines and threats are a classic scam tactic, so take your time. 2) A link that doesn't match the sender: look-alike addresses swap a letter or two, so check it's really the site it claims to be. 3) A request for your password or a login code: a real service won't ask you to send either one. Today: don't tap. Open the official app or type the address you know, then report the message. Tomorrow: your 3 steps after a data leak. https://t.co/XSNZ3QaJCr #phishing #scams #cybersecurity #onlinesecurity #passwords
Tip #7: 6M+ accounts leaked from a big service, with names, emails and passwords. The passwords were stored scrambled, but weak ones can still be cracked. If a service you use reports a leak, do these 3 things: 1) Change that password, in the official app or site, not through a link in a message. 2) Change it everywhere you reused it: attackers try leaked passwords on other sites. 3) Turn on 2FA, so a leaked password alone isn't enough to sign in. And expect scam messages that mention the leak. https://t.co/XSNZ3QaJCr #databreach #passwords #2FA #cybersecurity #onlinesecurity
10 LLM threat modeling frameworks every AI engineer should master to become a pro in LLMs:
1. OWASP LLM Top 10 — understand major LLM risks such as prompt injection, insecure output handling, and data poisoning
2. MITRE ATLAS — map adversarial tactics and techniques targeting AI and machine-learning systems
3. STRIDE — analyze threats across spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege
4. NIST AI RMF — structure AI risk identification, assessment, management, and governance
5. PASTA — use a risk-centric approach to analyze threats, business impact, and attack paths
6. Attack Trees — break down an attacker’s objective into smaller attack paths and conditions
7. Cyber Kill Chain — analyze attacks as a sequence of stages from reconnaissance to impact
8. DREAD — systematically assess threat severity across damage, reproducibility, exploitability, affected users, and discoverability
9. AI Red Teaming — systematically test LLMs for jailbreaks, prompt injection, data leakage, tool abuse, and unsafe behavior
10. LLM Attack Surface Mapping — identify risks across models, prompts, RAG pipelines, tools, agents, APIs, data, and infrastructure
Grab the LLM Ebook: https://t.co/ljEMt0UNUI
Beware of Phishing Scams : 7 Ways to Spot/Avoid Phishing
>Don’t download attachments from unknown/suspicious sources
>Legal Institutions such as Banks,won’t ask for account information via Email
>Be wary of Suspicious Emails asking for personal Information or Money
>Always check for Spelling Errors
>Avoid clicking Links from unknown sources
>Hover over the links to check the destination address before clicking them
>Always use Use anti-phishing protection and anti-spam software to protect yourself