If you don't want GitHub Copilot to use your data for AI model training, do this:
1) Go to: https://t.co/6iXN89qKA5
2) Scroll to Privacy, and locate "Allow GitHub to use my data for AI model training"
3) Select "Disabled"
#MDE custom collection is finally in public preview! It's a centrally managed solution to improve visibility and detection opportunities.
We're releasing a management tool and rule repository in YAML format to share new rules with the community.
https://t.co/kxit8fFjhU
@_ZeroPointSec@chstx64 I would assume the 2 other courses i have that aren't on the platform will be migrated RTO2 and the C2. I don't see the ability to download yet. I will check back.
Me and the homies are dropping browser exploits on the red team engagement 😎. Find out how to bypass WDAC + execute native shellcode using this one weird trick -- exploiting the V8 engine of a vulnerable trusted application.
https://t.co/ykJv0sePN9
@King_Wasabi69 @Yessir80654681 Non injury kept him from playing. Parents vicariously benefiting from their successful kids has been a growing problem. Look back at Tyrese Hunter or even Omaha beliew…
This ended up being a great applied research project with @d_tranman on weaponizing a technique for fileless DCOM lateral movement based on the original work of @tiraniddo. Excellent work, Dylan!
- Blog: https://t.co/4cXnRjhyK0
- PoC: https://t.co/3rR2CJYeG3
Had a lot of fun digging into COM stuff with @bohops recently! We ended up finding a way to laterally move without dropping a file.
https://t.co/F6NahVpuHP
Think you’ve got what it takes to break into systems, find vulnerabilities, and show off your cyber skills? 🧑💻🔍
Put your skills to the test in a hands-on hacking competition where you’ll tackle real-world scenarios, outsmart defenses, and compete for prize money 🏆💰.
This new article from @dez_ reveals 4 attack techniques linked to SmartScreen and SmartAppControl. Check it out: https://t.co/73Src39xie
Will you be at #BHUSA? Stop by @elastic booth #2350 to chat with Joe or catch his lightning talk!
#ElasticSecurityLabs#threattechnique
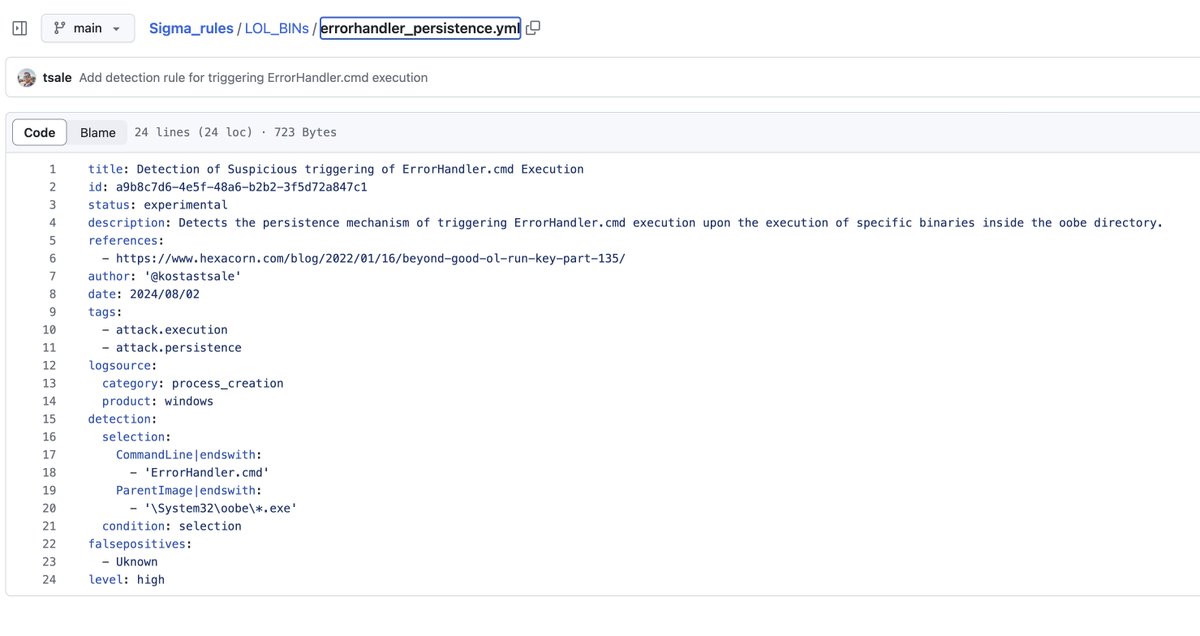
I came across a great persistence mechanism and created a Sigma rule for it. Just drop your batch script or add a line that points to your payload inside C:\Windows\Setup\Scripts\ErrorHandler.cmd, and upon execution of C:\Windows\System32\oobe\Setup.exe, the payload will run. In the clip below, I have cmd.exe /c calc.exe as the payload. If ErrorHandler doesn't exist, you can create it along with the directory.
Thanks to @Hexacorn for posting about it 🙏
In regards to the rest binaries under the C:\Windows\System32\oobe\ directory, most of them will not work, whereas others will force a restart (i.e. audit.exe)
🔗: https://t.co/pqe949qgBY