Our next macOS Vulnerability Researcher trainings with @gergely_kalman will be:
📆 2026-10-12 - 15: Self-organized, 4 (!!!!) day training (Budapest, Hungary)
📆 2026-11-15 - 17: Objective by the Sea v9 (Hawaii, USA)
More info here:
https://t.co/SQ4zNuVa6T
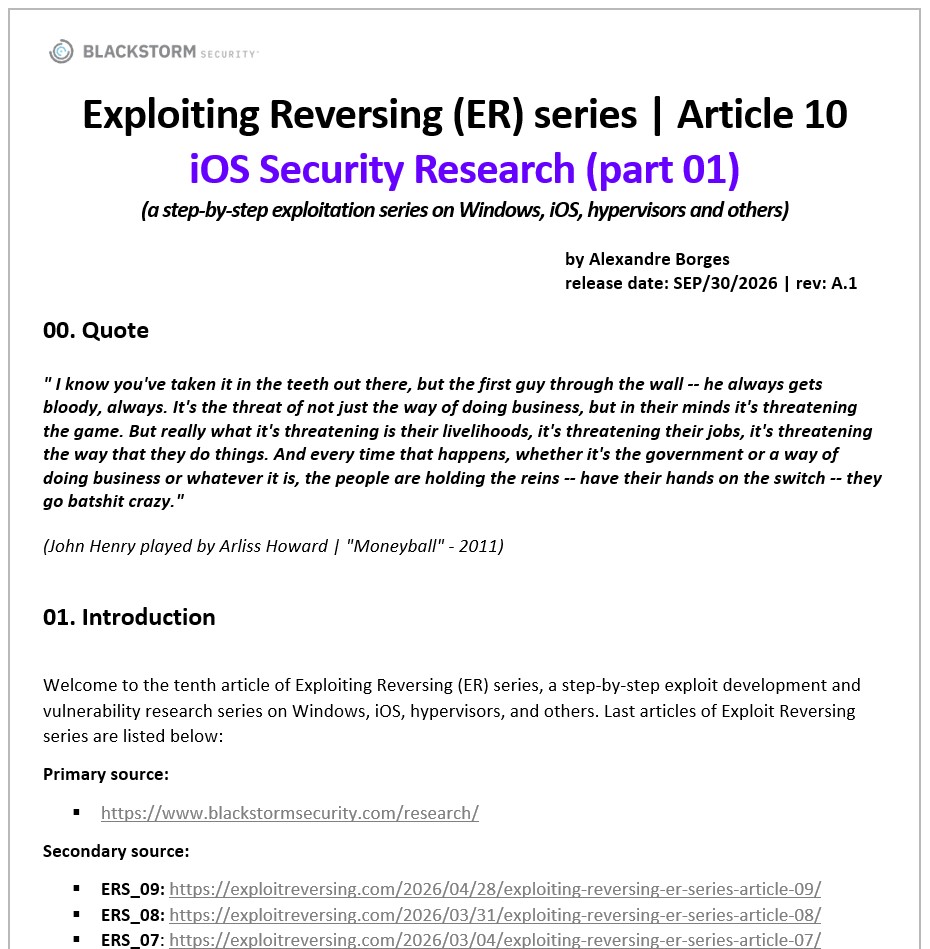
Exploiting Reversing (ER) Series | Article 10: iOS Security Research (part 01)
223 pages, free. The first article in the series aimed at iOS itself, and the opening of a multi-part sequence.
Published on:
https://t.co/VlebcByqKG
This article will be published on https://t.co/GBDi0lO8Zd next week.
I would like to thank Ilfak Guilfanov (@ilfak) and Hex-Rays SA (@HexRaysSA) for the continuous support.
Hope you enjoy the read!
#iOS #Apple #VulnerabilityResearch #ExploitDevelopment #ReverseEngineering
Using process coalitions in the XNU kernel to benefit incident response process trees. A short writeup on some updates I made to the TrueTree project
https://t.co/vYYaXKHPxN
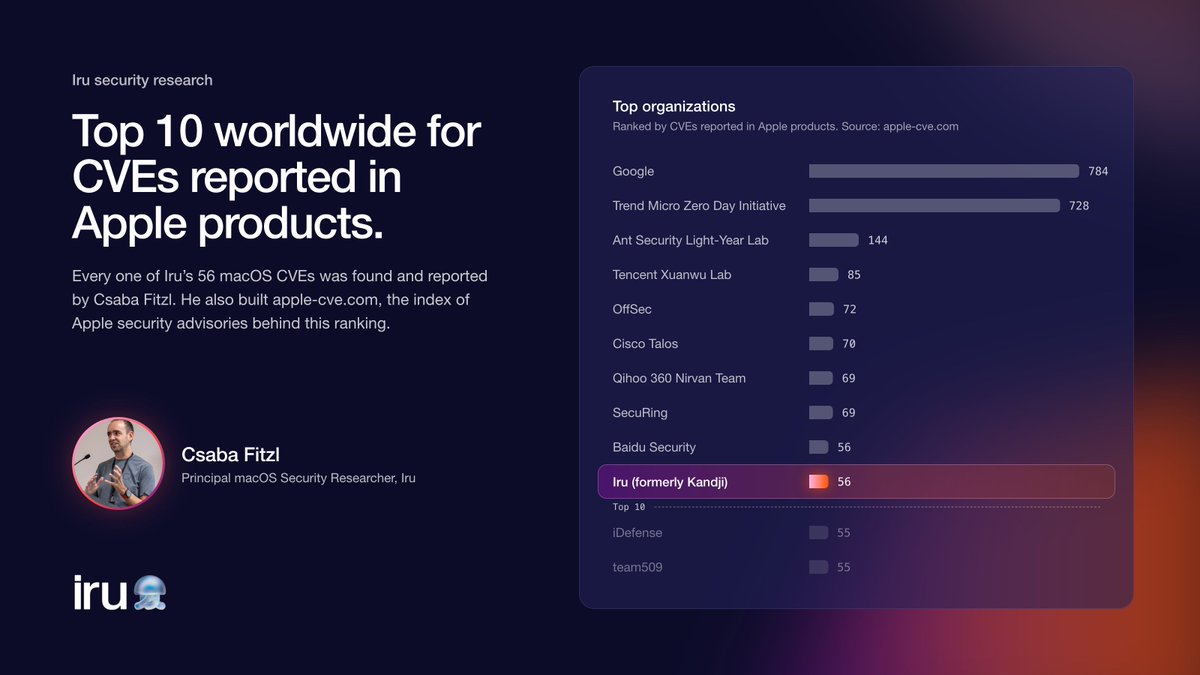
Shoutout to our Principal Security Researcher, @theevilbit , for the 56 vulnerabilities he submitted that put Iru on the board of the top 10 companies reporting CVEs in Apple.
#OBTS v9.0 is officially SOLD OUT! 🎉🌴
Registration is now closed, but if you're still hoping to join us in Maui, get on the waitlist!
📩 [email protected]
A few spots usually open up as the conference gets closer, so there's still a chance! 🤞
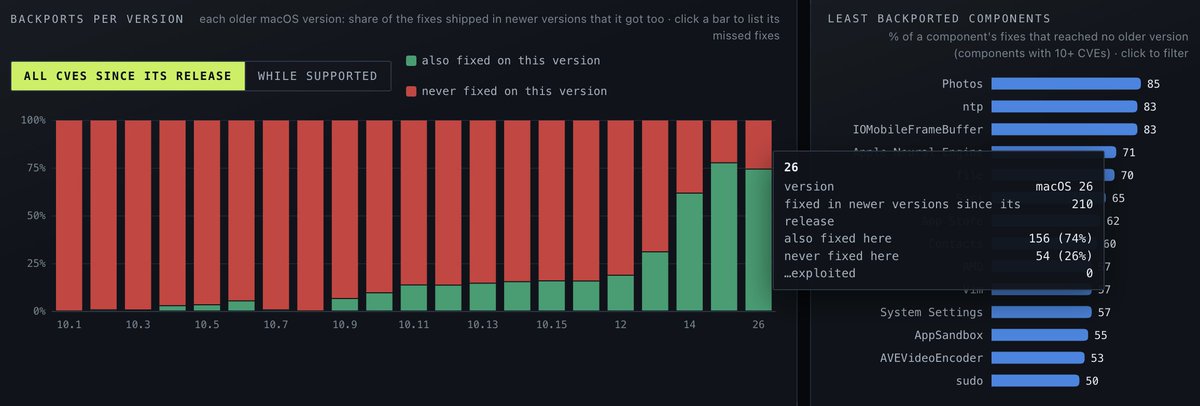
@yo_yo_yo_jbo@Apple Sadly it's very common... and it was always the case. n-1 and n-2 doesn't get the same treatment. You can get some stats about it on my CVE site. #shamlessplug :D
Not sure what to watch tonight?
Pick a session from the Top 5 List at MacSysAdmin Conference 2026.
Platform SSO - All Grown Up!
From Zero-Touch to Zero-Trust
Orchestrate Your Deployment
Infrastructure as… Claude?
You’re Not Home Alone
https://t.co/MK4Fxe8dxo #msa2026
@patch1t They fixed my app protection bypass after 3 years, I reexploited it 😅 and then had to get dirtynib working again because the old one I had was broken in GG. From there it’s a piece of 🍰
🍎 Closing the week strong, with a 💻 chain:
1️⃣ App TCC bypass -> allows modifying NIB files
2️⃣ DirtyNib reborn without user interaction -> Inject to any* GUI app
3️⃣ Get more TCC bypass + Full LPE
⏭️ Hunting for more privs
*non launch constrained
🏝️ 🌺 🌊
Do you want to spend 3 days (or 6) in this location?
Do you have some year-end budget left that you need to spend?
Fear no more! We got you covered with @gergely_kalman !
Just come to our "macOS Vulnerability Researcher" training, which will be at Nov. 15th - 17th, in Maui, Hawaii.
Then stay for the conference.
➕ As a side effect: you will gain a ton of macOS knowledge with the likelihood that you will find some cool 0days after, and earn 💰
➕ ➕ Bonus: You will have a chance to meet some of the best minds of the macOS attack and defense space at the conf.
We only have a few spots left, so don't overthink it, just sign up.
More info here:
https://t.co/w5s1OiGyyh
Microsoft macOS devs should take our macOS exploitation training with @gergely_kalman . 🤪
We have a few places left for our Hawaii 🏝️ training. Just saying.
Submitted a macOS LPE to MSRC. 🍿
Open-sourced CryptSn0w, our now obsolete untethered iOS ≤27/≤A20 Pro jailbreak via rare Apple server-side TSS/Cryptex bug. PATCHED, educational only. NOT a working jb
Built w @GenericCoding@D4RK7ET. SBInject: @htrowii. Help: @Jakeashacks@forcequitOS
https://t.co/AymD6hbbBM