Stoked for the next (ad)venture: "DoubleYou" https://t.co/DpPe5fQxzV
Cofounded w/ long-time friend @hexlogic, we're empowering those building security tools for Apple devices 🍎🛡️
And by bootstrapping this venture, our core value of democratizing security remains our focus!
🚀 I’ve launched App Scam DB — a new home for my investigations into scam apps and misleading App Store listings.
Some apps launch as generic tools, then change their names, icons and screenshots to borrow the identity of brands people trust — while pushing expensive weekly subscriptions.
🔎 I track those changes and examine developer identities, websites and pricing.
📸 Reports include original screenshots, before-and-after comparisons and downloadable evidence.
👥 Written for everyday users, not just security researchers.
Explore the reports 👇
https://t.co/CjuvLhegkA
1/ We tore apart a #macOS C2 implant that's currently sailing past engines on VT - 0 detections as of today. Shared by @malwrhunterteam.
Written in Zig, and engineered like red-team infrastructure.
Here's what makes it interesting 👇
#OBTS v9.0 is officially SOLD OUT! 🎉🌴
Registration is now closed, but if you're still hoping to join us in Maui, get on the waitlist!
📩 [email protected]
A few spots usually open up as the conference gets closer, so there's still a chance! 🤞
We've also added a HeartBreaker sample and its metamorphic framework to our public macOS malware repository:
https://t.co/QcaSI536nC (pw: infect3d)
#SharingIsCaring
Our free, open-source tools, like RansomWhere?, use behavioral heuristics rather than signatures ...so metamorphose all you want! 😆
RansomWhere?
https://t.co/mMrn6JbwDg
It’s not every day we encounter metamorphic ransomware targeting macOS! 👀
Our @patrickwardle recently presented at @macsysadmin & @virusbtn on “Heartbreaker,” a new ransomware sample that rewrites & recompiles itself every time it runs!
Blog & slides: https://t.co/ghYQTrAXFL
Join us and @Rippling for a happy hour in NYC on Nov. 11! 🥳
Connect with fellow IT & security pros over drinks & light bites, plus hear from @patrickwardle on hacking AI agents & assistants 🤖🔍
RSVP: https://t.co/rObMl9Nu6c
🏝️ 🌺 🌊
Do you want to spend 3 days (or 6) in this location?
Do you have some year-end budget left that you need to spend?
Fear no more! We got you covered with @gergely_kalman !
Just come to our "macOS Vulnerability Researcher" training, which will be at Nov. 15th - 17th, in Maui, Hawaii.
Then stay for the conference.
➕ As a side effect: you will gain a ton of macOS knowledge with the likelihood that you will find some cool 0days after, and earn 💰
➕ ➕ Bonus: You will have a chance to meet some of the best minds of the macOS attack and defense space at the conf.
We only have a few spots left, so don't overthink it, just sign up.
More info here:
https://t.co/w5s1OiGyyh
Calif’s Chollima jailbreak:
• Kernel r/w, SPTM bypass, sandbox escape
• iOS 27.0.1; demoed on MIE-enabled 17e & 18 Pro
• Unpatched 0-days: Duo could get a day-one untethered jailbreak
• Will get released at some point but no ETA
• Get your 18 Pro/PM on 27.0.1 or buy one now
Neat ChatGPT bug 🐛
Found manually (even after @OpenAI “pointed Astra at its own systems until it ran out of bugs")
Local (unpriv'd) attacker:
• Hijack your Dot
• Take over your account
• Access protected macOS files
+more 👀
@OpenAI's $500 bounty donated to @objective_see
One week to go until VB2026! ❗
We’re officially into the final week, so if VB2026 is still in your plans, now’s the time to secure your ticket.
🇪🇸 14–16 October 2026 | Seville, Spain
🎟️ Get your ticket: https://t.co/C5cRq4IzcB
#VB2026#CyberSecurity#Seville#VBConference
@sunsetsyntax ah, good point - thanks! 🙏
Have made some improvements: (https://t.co/TsVHsSJ2rF), still testing, but will push out these in next version!
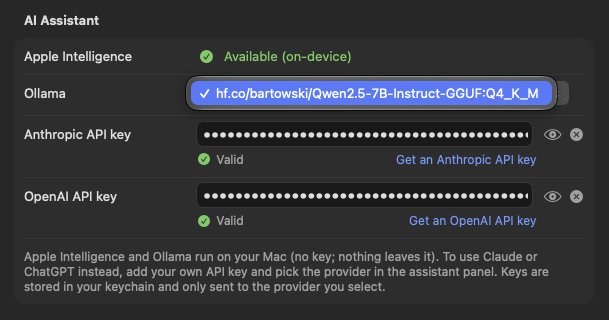
TaskExplorer now natively integrates with Ollama 🤖
...so you can bring your favorite local LLM to the party!
Latest version available here:
https://t.co/1TF7pQw3NA
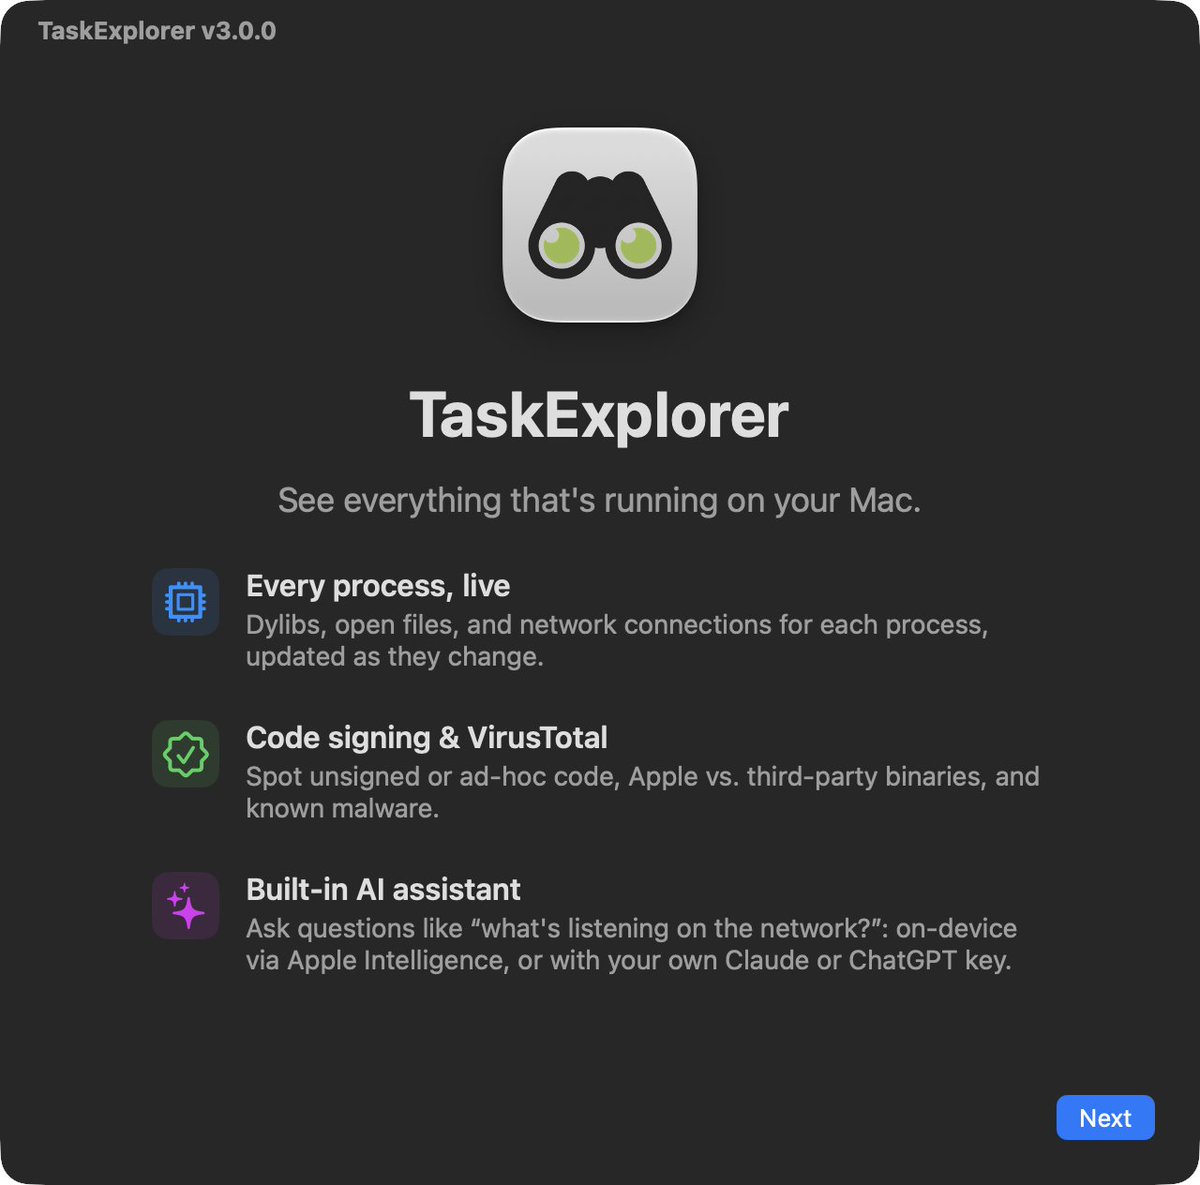
I've just (re)written TaskExplorer
Think Process Monitor but for macOS, open source, & much more powerful 💪🏽
Highlights:
• CLI + JSON export
• On-device AI assistant
• Code signing + VirusTotal context
• Live process/file/dylib/network activity
https://t.co/1rfeBWoEVE
what we've shipped:
muse ♥️
ton of connectors 🔧
muse invite codes 💌
muse phone call beta ☎️
muse for mac
muse in canada 🇨🇦
muse connector platform 🛠️
muse mac computer use 💻
muse for small business 💼
muse gadgets 🕹️
muse memes 🤡
no butthole 🍰
what should we ship next?
Apple is already understandably annoyed by poorly written/insecure/greedy AI agents/assistants insisting on Full Disk Access, and then once granted/obtained, abusing that, to access <all the things>.
...that didn't take long!
Apple says it will add new controls around macOS’s Full Disk Access permission, warning that increasingly capable AI agents make broad access to users’ files, messages, mail, and browsing history riskier.
https://t.co/bIcSeMx9oG
@patrickwardle I read: "We will add more prompts or clicks to approve FDA". 🤯 The entire FDA thing should be redesigned from scratch, it's been always horrible and it just gets worse.
Last week, our @patrickwardle spoke with @ThomasClaburn at @TheRegister about this exact issue: AI apps "undoing" Apple's hard work on security & privacy.
Great to see @Apple jumping into action to protect the security & privacy of its users.
Read: https://t.co/SY2jvxONJc