"The world’s biggest Apple security conference [#OBTS] kicks off this week in Hawaii" 🍎🛡️👾🐛
https://t.co/snTXKcRKiZ (by @arinwaichulis)
See you by the Sea! 🏖️
It's (finally) #OBTS week! 😍🌴
Objective by the Sea v9 kicks off today in sunny Maui with 3 days of hands-on trainings, followed by talks later this week!
See you by the sea! 🌊 🤙
📸-credit: @andyrozen
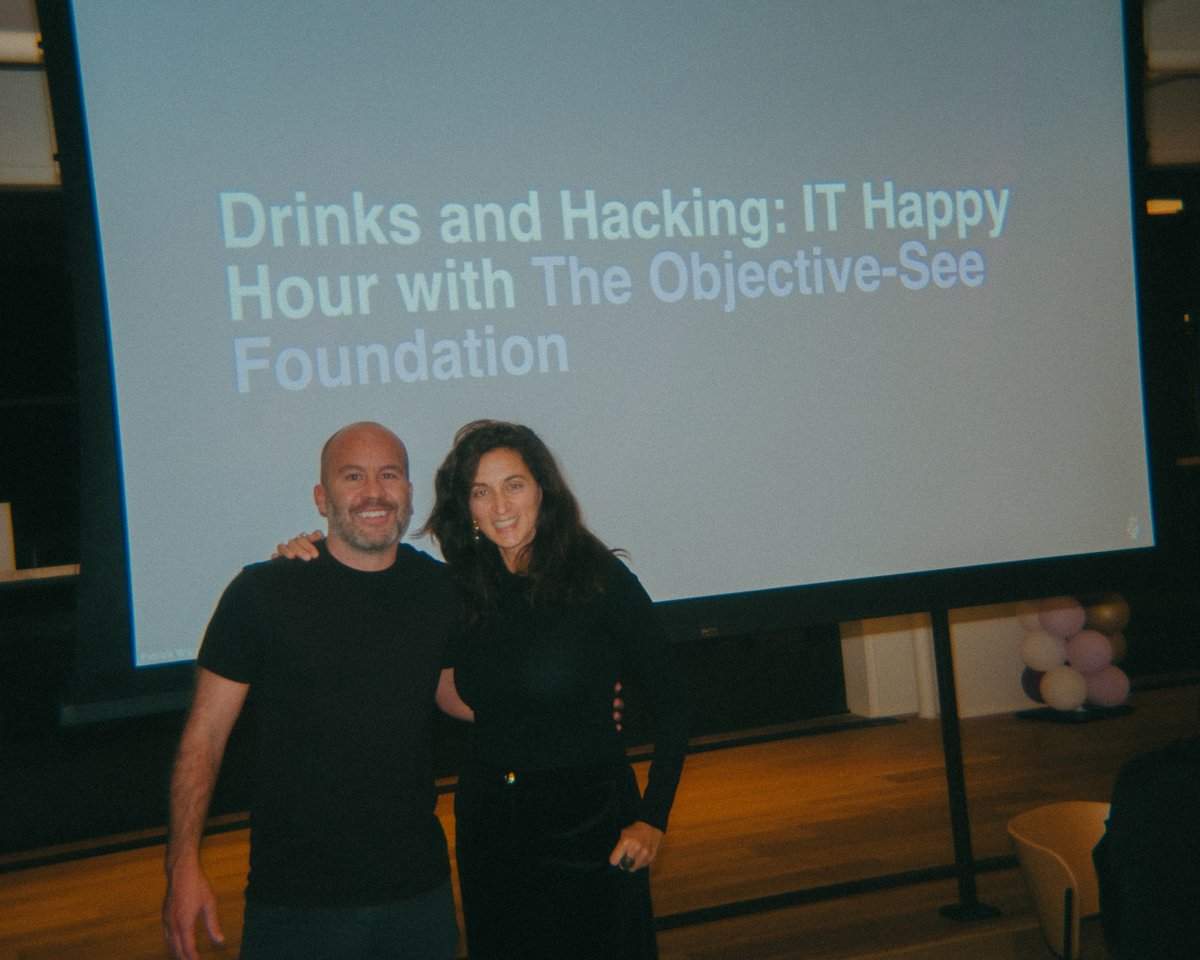
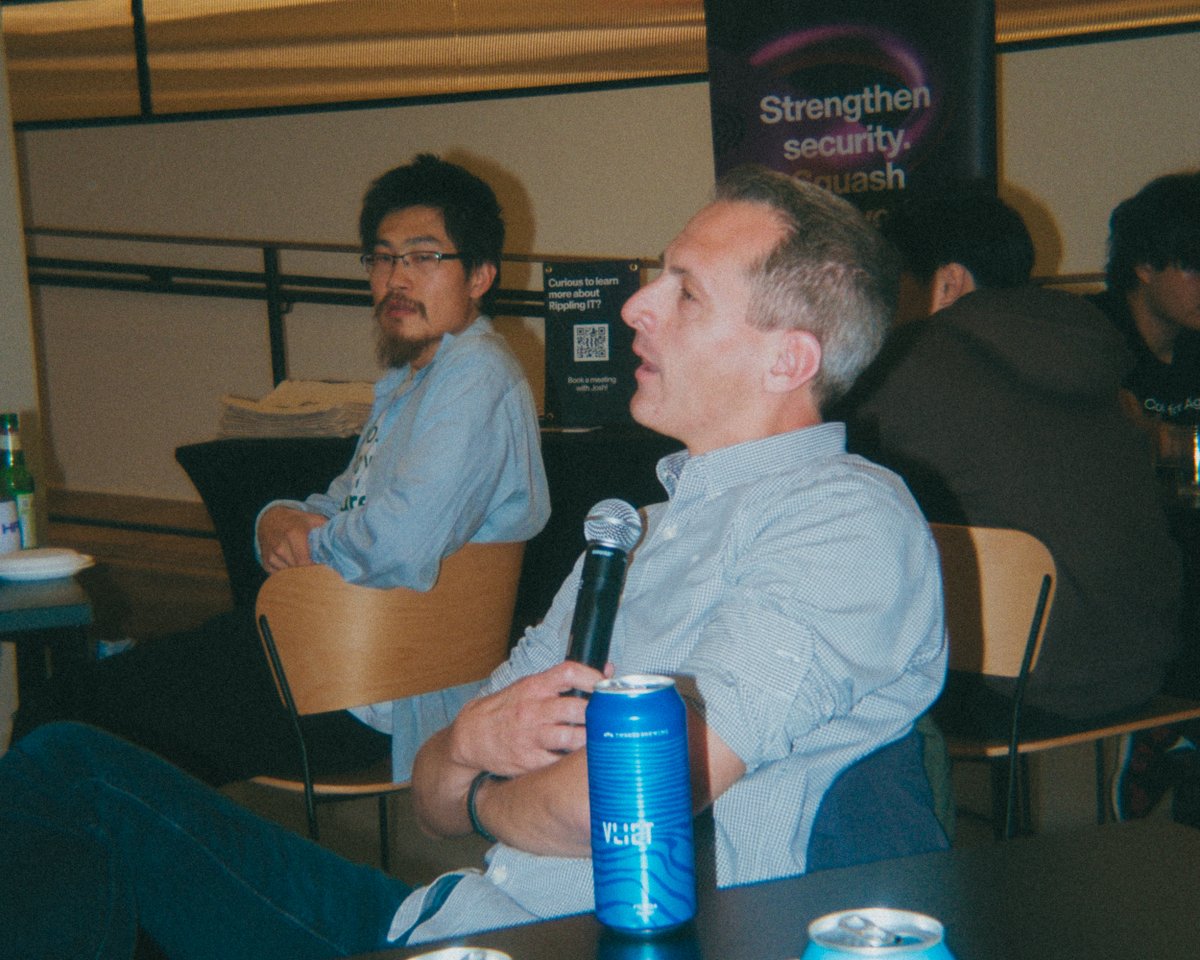
Mahalo to Foundation supporter @Rippling IT for hosting us in NYC 🙏🏽
Great to connect with fellow IT & security pros, swap ideas, & talk nerdy (and yes, philosophically too!) about our latest research on how AI assistants are reshaping threat models & security tooling 🤖
Wheels up for #OBTS! ✈️🌴
The (stylish) #OBTS crew is trading gray skies for Hawaiian sunshine as we head to the 9th edition of Objective by the Sea!
Talks, trainings, networking & waves ...see you by the sea! 🤙
Also, if you're ready to put your Apple hacking skills to the test, join the #OBTS CTF on Nov. 19! 👩🏼💻🍎
Challenges for all skill levels, prizes up for grabs, and a fun chance to connect with fellow hackers!
Spots are limited, so register now: https://t.co/tzHB9gS5my
🌺 Aloha, #OBTS v9 attendees!
We've shared everything you need to know before the conference! Have a read to get all the important details, plan ahead, and make the most of your OBTS experience! 🌴
🔗 https://t.co/9oyogyXwpi
#OBTS v9.0 is officially SOLD OUT! 🎉🌴
Registration is now closed, but if you're still hoping to join us in Maui, get on the waitlist!
📩 [email protected]
A few spots usually open up as the conference gets closer, so there's still a chance! 🤞
Join us and @Rippling for a happy hour in NYC on Nov. 11! 🥳
Connect with fellow IT & security pros over drinks & light bites, plus hear from @patrickwardle on hacking AI agents & assistants 🤖🔍
RSVP: https://t.co/rObMl9Nu6c
Maybe Apple read about our research 🤭
Either way, happy to see them taking steps to limit the granting of Full Disk Access (FDA)!
https://t.co/kKOlTofshc
Mahalo to @WIRED for covering our initial research into ChatGPT (CVE-2026-100754)
Traditionally, protecting the privacy & security of Apple users meant focusing on malware & attackers...now, AI agents belong in that threat model too 🤖⚠️
More bugs reported, so stay tuned... 👀
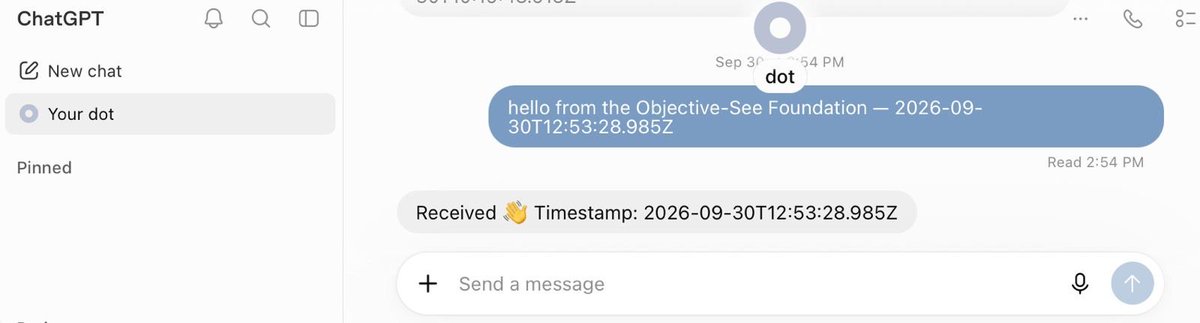
0-day flaws in ChatGPT let a local unprivileged attacker bypass OpenAI's safeguards, subvert the agent on macOS, and take over your Dot.
Responsibly reported to (and ack'd by) OpenAI. Our research into the (in)security of AI agents continues... 🫠
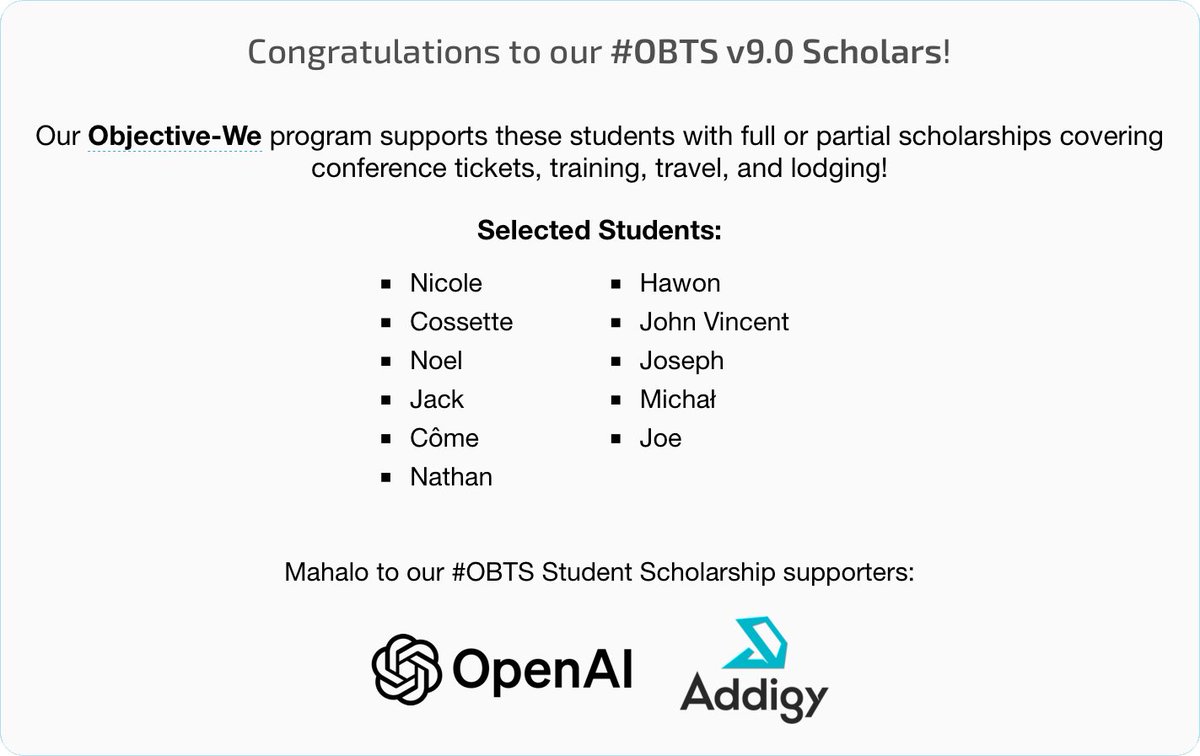
Congrats to our #OBTS v9.0 student scholars!
From ~100 applications (thank you all!), our Objective-We program is supporting these scholars with full or partial scholarships, covering tickets, training, travel, & lodging at #OBTS v9
Mahalo to our supporters @OpenAI & @addigy 🙏
Security & privacy used to mean fighting malware and hackers
...now, we have to add "AI agents" to that threat model 🤖 😅
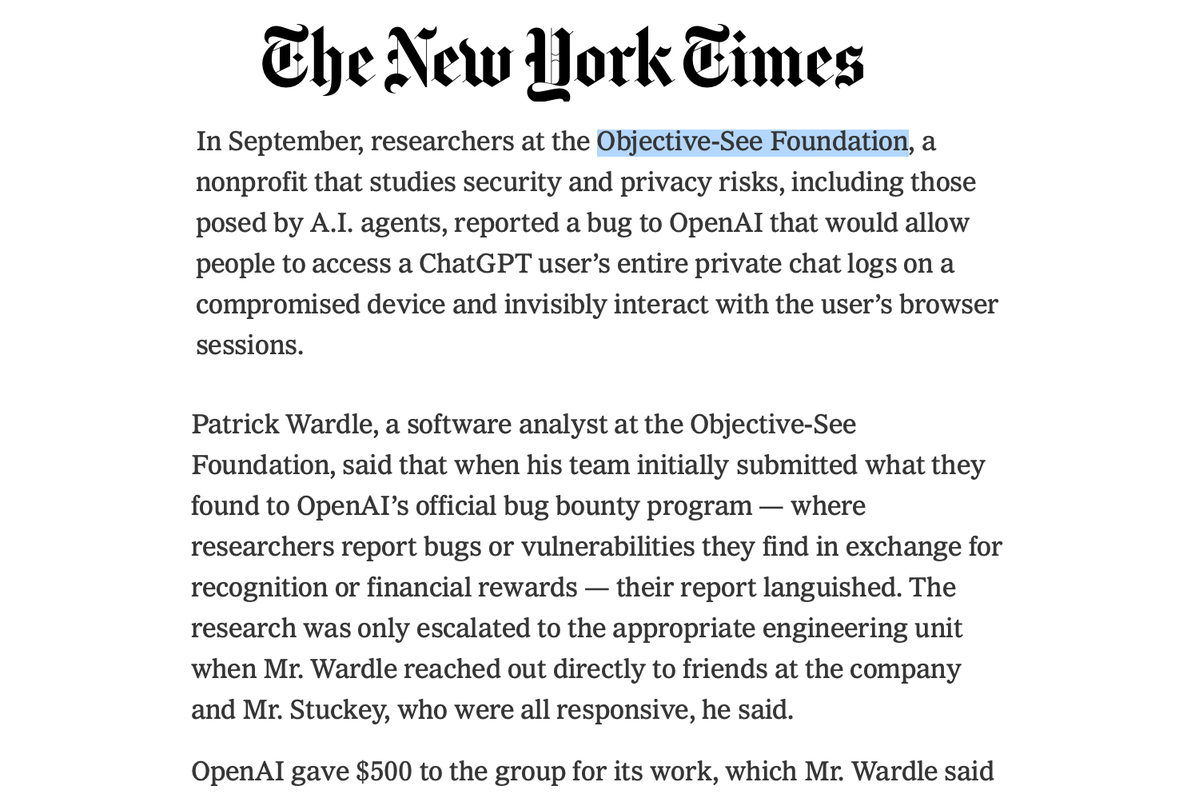
Mahalo to the @nytimes for spotlighting some of our recent ChatGPT research & bugs!
https://t.co/q2cKTZtoaI
#OBTS v9 schedule is LIVE! 🔥
https://t.co/3pvSvOoVcO
If you're into Apple security (yes, including securing those pesky AI agents 🤖), you seriously don't want to miss this one!
Hope to see you by the sea ☀️🌊
Just wrote up a lil threat landscape review January-September. TL;DR: ClickFix is basically the on-ramp for everything now, stealers evolving into something much worse.
Go read! https://t.co/vgnFWF8rv6
Hooray, hot-fixed! 😍 Kudos on the quick patch (& full disclosure FTW) 🙏🏽
But there was a 'remote' exploit vector: a simple ClickFix attack could deliver the hijack giving a *remote* attacker complete access then to every victim device running Muse
See: https://t.co/QBszVNCdbn