I am still on the hunt for an experienced Windows EDR researcher with @stuartjash to come develop new ways to make environments hostile to threats.
US-based due to some synchronous obligations, let us know if you’re interested.
Jamf Threat Labs uncovered fake macOS installers tied to Contagious Interview. The threat actors continue to test new ways to deliver their malicious payloads.
Read more about it on our blog.
https://t.co/nLAwNFHIAt
#macos#malware#ioc#dprk
Just announced: talks for #OBTS v9 🥳
Stoked on an epic lineup of cutting-edge 🍎- security research, covering exploitation, malware, reversing, security tools, AI, & more!
Check out the full lineup:
https://t.co/aGwpUhN2xZ
Which one(s) are you most looking forward to!? 🤔
Jamf Threat Labs uncovered a macOS campaign using a fake Zoom installer to deliver Overlord RAT.
The downloader (ZoomMeetings) is a self-contained .NET 10 Mach-O binary, unusual for macOS malware.
Because .NET is cross-platform, the same codebase also targets Windows.
https://t.co/Eij27U91kl
#malware #macOS #reverseengineering #RAT
🚨 The CFP for #OBTS v9 closes this Friday (July 31)!
Have some novel or innovative Apple security research to share? We'd love to see your submission:
https://t.co/7Sb2N54gZd
Welcoming submissions on any Apple security topic (offensive & defensive)! 🍎🐛🛡️
One of the most time consuming parts of macOS research is identifying what you're looking at - AMOS, NovaStealer, DigitStealer, MacSync, or maybe Shlayer or Adload.
You can now pull in this Malware Research skill to help you classify malware quickly.
https://t.co/rPFZGnGuwD
I attempted to do this with the Malware KB, but that still required sifting through the many websites and articles. This repo, either as a standalone dataset or integrated as an AI skill, can help map IOCs and samples to different malware families.
https://t.co/pH2tgMr786
Meet CrashStealer. This one takes delivery more seriously than most, a signed and Apple-notarized dropper that's pulling its second stage payload down through GitHub.
The payload is a native C++ stealer with client-side AES-GCM encryption and layered anti-analysis.
Check out our writeup for additional details and indicators of compromise.
https://t.co/3IhuEmrsZj
#infostealer #malware #macos #threatresearch
Meet CrashStealer. This one takes delivery more seriously than most, a signed and Apple-notarized dropper that's pulling its second stage payload down through GitHub.
The payload is a native C++ stealer with client-side AES-GCM encryption and layered anti-analysis.
Check out our writeup for additional details and indicators of compromise.
https://t.co/3IhuEmrsZj
#infostealer #malware #macos #threatresearch
New AMOS campaign details.
Attackers are using a phishing page hosted on https://t.co/Q8HpzW5rSk, tricking users into executing a malicious command in Terminal:
hxxps://api-metrics-5453[.]com/curl/3e97b0eddfddb28e10008f9348381b2665e1ad12476315b24a64808696c3347b
The bash script downloads and launches the next-stage stager: “helper”.
“helper” is a heavily obfuscated loader/dropper. It does not steal data directly, but prepares and launches the next stage (AMOS stealer + backdoor).
The rest you already know.
Infrastructure:
api-metrics-5453[.]com — first stage
prismdata48[.]com — Phishing site
solidlattice65[.]com — Phishing site
#AMOS #STEALER #macOS #malware #detection
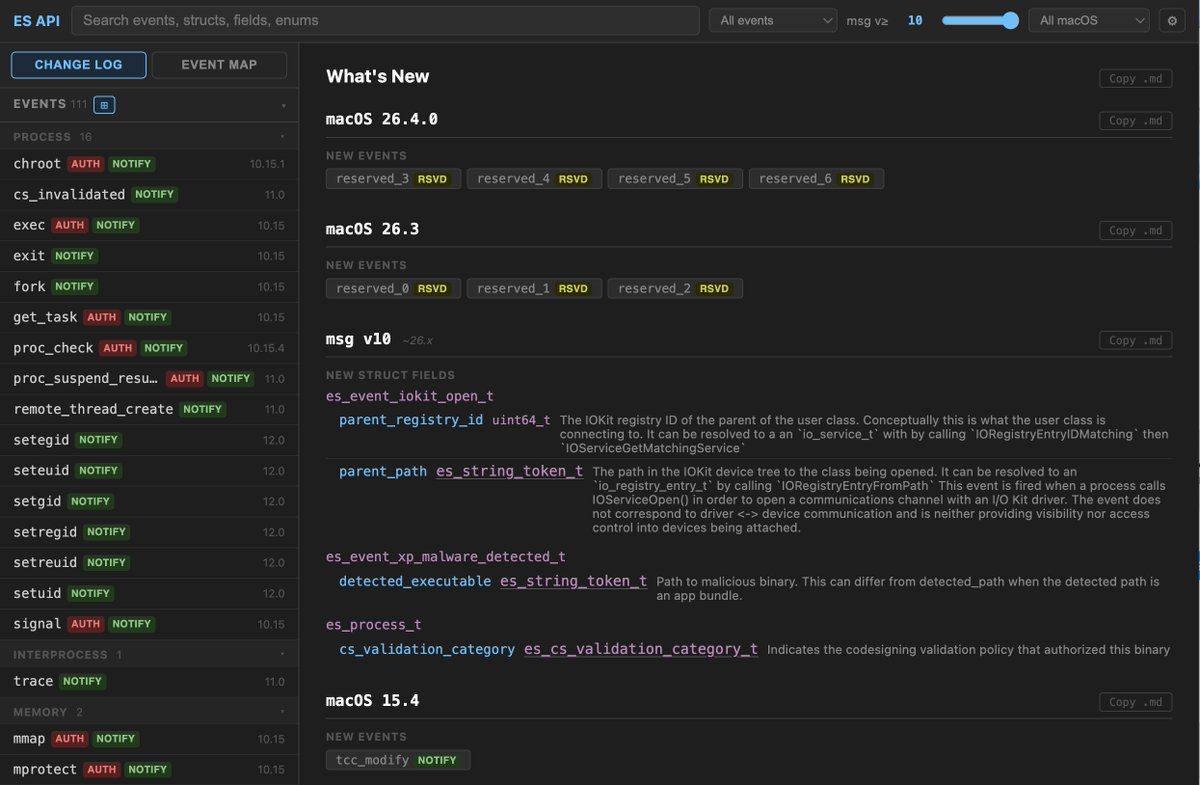
Spent some time with Claude this weekend making an Endpoint Security reference for research and development. Checks for the latest SDK, parses the ES headers, and publishes. Includes a dedicated ES change log and telemetry matrix.
https://t.co/b0HZ6IKOpW
🧵 The axios @npmjs compromise dropped a @macOS backdoor that closely mirrors North Korea's (@DPRK) recent WAVESHAPER backdoor. Let's take a quick look the full intrusion:
You can now build macOS firewalls/network tools via Endpoint Security - no Network Ext. needed! 🤯
Reversing macOS 24.6’s new ES_EVENT_TYPE_RESERVED_* ES events shows some are network auth/notify hooks
Read: “Building a Firewall…via Endpoint Security!?”
https://t.co/gR4t6dPbbr
In macOS Tahoe 26.4 Apple added a new security feature to Terminal that warns users of potentially malicious pastes with a "Possible malware, Paste blocked" prompt. Here how it actually works 🧵
I've exited from tech and am doing guided tours in and around Yellowstone.
https://t.co/7tYTmFirYi
Thanks to everyone for some great years! This will be my last post here. 🐬
DFIR analysts who use macOS as their daily driver deserve free and native forensic tooling. So I built one. 🍎
Introducing 𝗜𝗥𝗙𝗹𝗼𝘄 𝗧𝗶𝗺𝗲𝗹𝗶𝗻𝗲 — a timeline analysis app built from the ground up for Mac-based DFIR folks, forensic investigators, or SOC analysts. Built in appreciation of, and inspired by, Eric Zimmerman’s Timeline Explorer.
Every feature in this tool was shaped by real IR casework. Handling massive timelines, parsing artifacts here and there, and pivoting across logs during active investigations. I built IRFlow Timeline to be the native macOS timeline analyzer that actually keeps up with a live case. Every button and view is intentional; if it’s in the app, it’s because I needed it mid-case and realized the standard tools fell short.
No dependencies. Zero setup. Just drag, drop, and analyze.
#dfir #incidentresponse #timeline #macos #threathunitng #digitalforensics
Apple dropping some XProtect updates (v5331) which seem to be every couple of Tuesdays. The new yara rules which look at some AMOS stealers are really interesting in that they're looking at the assembly instructions and the script-based stuff continues to move into XPScripts.yr.