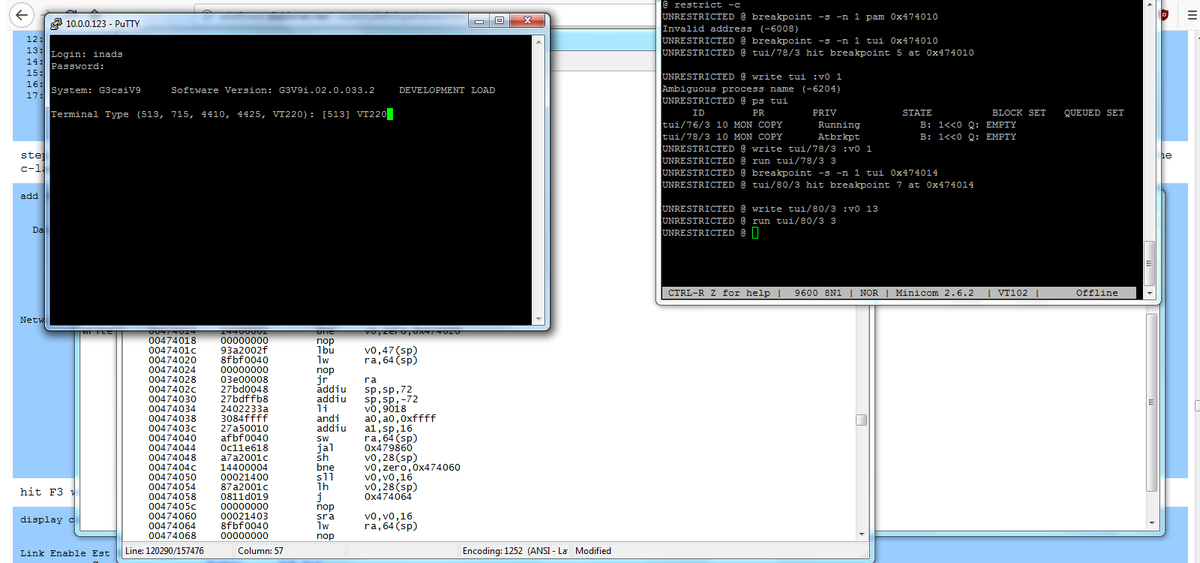
@Dialogic Hey! Do you have a bug bounty program for your products? If so, where would I submit any vulnerabilities to? I'd very much appreciate knowing.
@strongbadactual Is 1950s stock character Strong Bad a greaser? Strong Sad a beatnik? I sorta figured him for beat poetry in any decade, but there he might actually have a following.
@Mitel What is Mitel's policy on bug bounties, particularly on high risk exploits, such as buffer overflows and arbitrary code execution? I tried emailing tech support, and they blew me off for not having an account. Just making sure this is what you want.
@shadytel@NEC@NEC_Enterprise@NECUnified I love the timing of this; several hours before, they pinned a tweet about the SV9100 (Nucleus based) being "reliable and secure". https://t.co/qScKgQy3fl
You can have an easy, straight out-of-the-box, hybrid #cloud communications for your business that is cost-effective and maintains an on-premises system. It's @NEC's reliable and secure SV9100 BLUE. #UCaaS#univergeblue https://t.co/Xk5mMcnorL
@JBrodkin Looks like someone is challenging the FCC again. Hopefully all these days in court will actually make a sizable difference. https://t.co/n3V6H6r9VB
@evandoorbell I know I'm skating on thin ice asking a question like this about a digital switch, but I do have to ask - do you think this announcement(via the White Plains intra-LATA 5E)captures some vague aesthetic qualities of the old network? It's warm. https://t.co/4ECm5K8hIm
@furan@shadytel Hey! This particular machine is with me in California. It's in pseudo-production service, but if you'd like to make it do something, I can introduce new code into the software Alternatively, some of the PCI versions of these cards are like $30 on eBay. I can help on IRC.
@evandoorbell Random trivia: those calls were looped through the first DMS-10 ever, Fort White. Not for any particular ceremonial reason; it was just convenient for me and the bridged Dialogic card to perch on it and do international callback. Also, two files in last tweet.