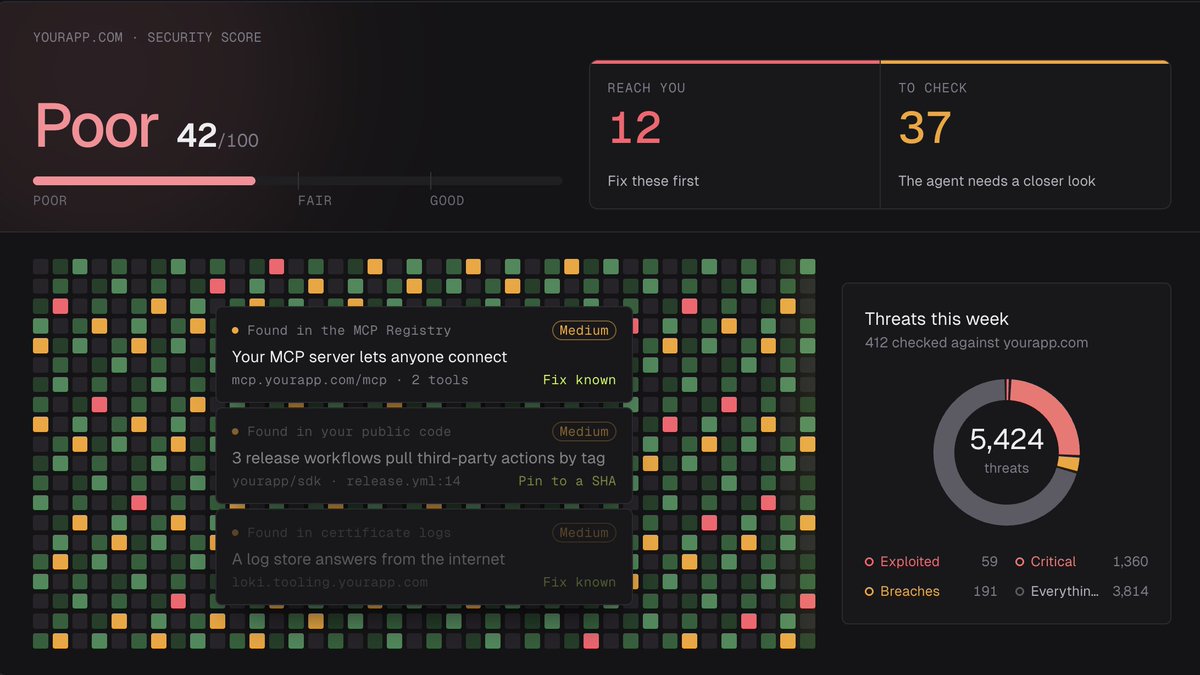
We built a massive threat intelligence database and we're opening it up for free.
Now your Claude Code, Cursor, or other coding agents can check for emerging threats, malicious packages, and vulnerabilities while coding or reviewing PRs.
https://t.co/qyk9xLzD4U
🛡️ Cloudflare shipped a Nov 19 WAF rule against PHP2Shell, the PHP code execution flaw disclosed in October.
If you run PHP, upgrade anyway: the rule is set to Block in Cloudflare's Free and Managed rulesets but only filters matching requests proxied through Cloudflare. Traffic that reaches your php-fpm, mod_php or container hosts any other way gets nothing from it.
First public Oct 20 · exploited in the wild · CISA KEV · fix 8.2.35, 8.3.36, 8.4.27, 8.5.12
https://t.co/3ZGEzQfTYD
👀 Dutch police say Revolut customer data stolen in September was used to plan violent attacks in the Netherlands.
If Revolut contacted you about the theft, your identifying data was taken: follow Revolut's and the police's safety advice. Contacted or not, treat calls or texts "from Revolut" or "from the police" that quote your details as suspicious.
First public Nov 19 · attacks foiled in The Hague and Amsterdam, arrests made
https://t.co/qKiJBblcj5
👀 Dutch police say Revolut customer data stolen in September was used to plan violent attacks in the Netherlands.
If Revolut contacted you about the theft, your identifying data was taken: follow Revolut's and the police's safety advice. Contacted or not, treat calls or texts "from Revolut" or "from the police" that quote your details as suspicious.
First public Nov 19 · attacks foiled in The Hague and Amsterdam, arrests made
https://t.co/qKiJBblcj5
👀 JPMorgan Chase, Visa and Mastercard say attackers hit vendors holding customer names and emails; n0n claims it.
If you bank with Chase or are in a Visa or Mastercard card benefit program, expect phishing citing this breach. Contact them only through their own app or the number on the back of your card.
First public Nov 19 · no card or payment data taken, all three say · vendors not named · breach date unknown
https://t.co/rP2k9miyCV
100% demo-to-customer conversion at @infrastack_ai so far.
we didn't build another security dashboard. we built agents that actually investigate threats and tell you what needs fixing.
once people see it live, they get it.
time to retire some legacy security software.
who wants a demo?
great work by Moritz and the Codex team.
happy to help from the @infrastack_ai side too. if you're running Ruby or Rails, we'll help you check your exposure, inventory affected versions and figure out what needs patching.
free scan. just DM me.
https://t.co/qsW4O2GDWj
i actually think one platform for analytics, logs and observability makes a lot of sense. less jumping between vendors.
What's stopping you from copying PostHog's analytics into Sentry?
especially now that agents can connect the dots across all that data and see the bigger picture...
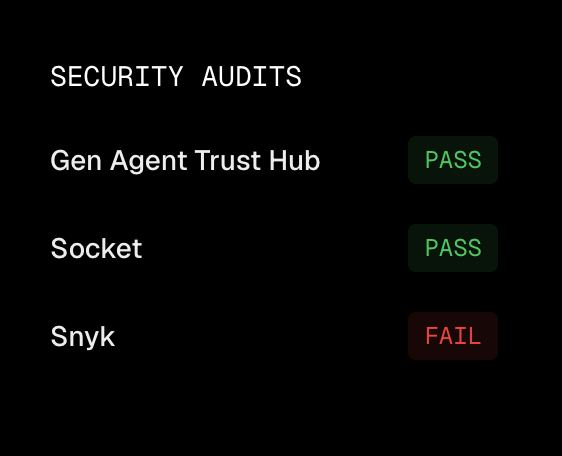
anyone from @snyksec here who can help rescan our updated skill? been waiting 2 days :)
also, maybe it's time to outsource these audits instead of putting them behind an API key. happy to help with that too.