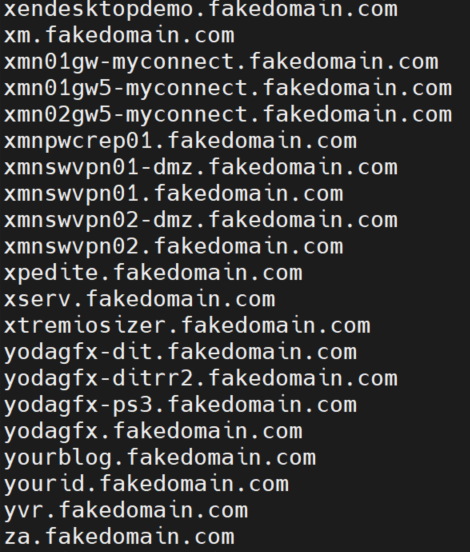
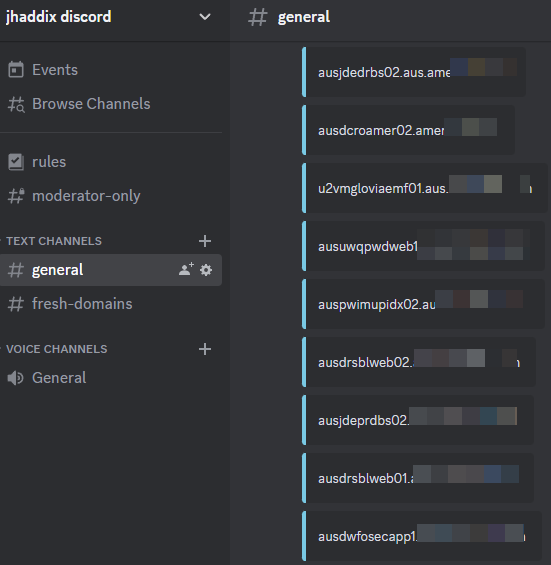
⏰ Want a one-liner that notifies you of any fresh domains (if they come up) to you each hour?
#3 ⬇️
> screen
> subfinder -silent -d {target}.com -o {target}
> while true; do subfinder -silent -dL {target} -all -nW | anew {target} | notify; sleep 3600; done
The sky is the limit with Katana's customizable field options! 🚀 🪐 🌌
🌀 Here's a basic example of how katana could be used to look for API keys in responses!
📝 Change the regex to match actual API keys!
More details 👉 🔗 https://t.co/np1oO96TnE
#Hackwithautomation
Use PTR queries to extract subdomains associated with an ASN using dnsx! 🚀
Discover more subdomains by querying PTR records!
Install dnsx now 👉 https://t.co/1319t7GcEd
#Hackwithautomation#ASN#Security
📣 Nuclei Cloud Beta is fast approaching. We're excited to announce a new feature, Nuclei Cloud AI!
Use AI to write templates based on vulnerability reports, blogs, and more! Here's @olearycrew to tell you all about it!
https://t.co/IFGP8KYF9p
How to hack web applications in 2023: Part 1 🚀
💻 Types of web apps
⚙️ Setting up for testing
🪲 RCE
🐞 SQLi
🐛 XXE
🪳 Insecure Deserialization
🐜 XSS
And that's just Part 1! 😱 👇 #hacking#pentesting#bugbounty
https://t.co/uHIDJu0if2
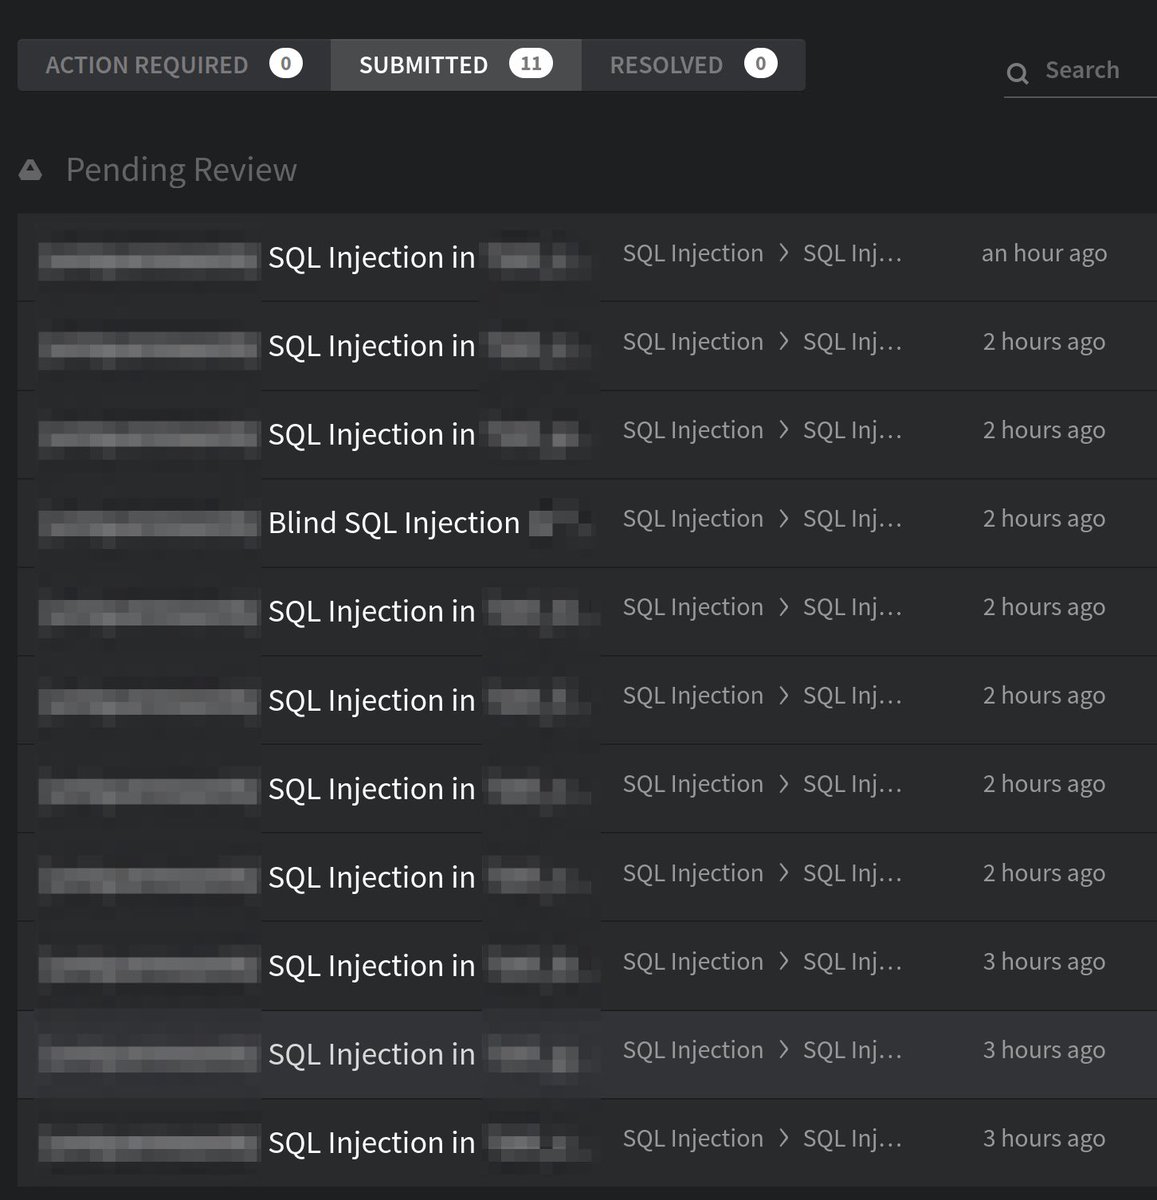
The old auth bypass by editing http responses from 302 to 200 never stops paying. 10 unique endpoints vuln to sqli.
Always pay attention to 30x redirects with unusually long responses.
Again, another occasion for the “expectation VS reality” check. Will find out soon enough
A bug bounty hunters guide to building a fast one-shot recon script! 🚀
🎯 DNS enum
subfinder, shuffldns, haktrails, puredns + dnsx
🚢 Port scanning
nmap, httpx (+ naabu)
🕷 Crawling
gospider (+ katana)
Learn how 👇 #hackwithautomation
https://t.co/TWMVZjD7HW
Found another SQLi on @Bugcrowd 's private program
#ItTakesACrowd#BugBounty#bugbountytips#bugbountytip
Tip: Use this payload 0'XOR(if(now()=sysdate(),sleep(15),0))XOR'Z
In the value of every parameter and check if response delays according to the provided time in payload
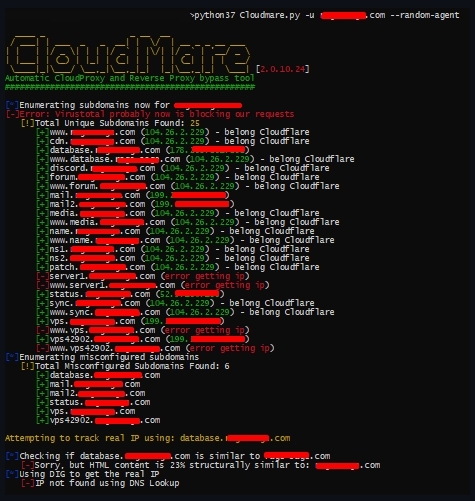
Cloudmare
Cloudmare is a simple tool to find the origin servers of websites protected by Cloudflare, Sucuri, or Incapsula with a misconfiguration DNS.
https://t.co/PwtptyDZcx https://t.co/1x8DDmt76g
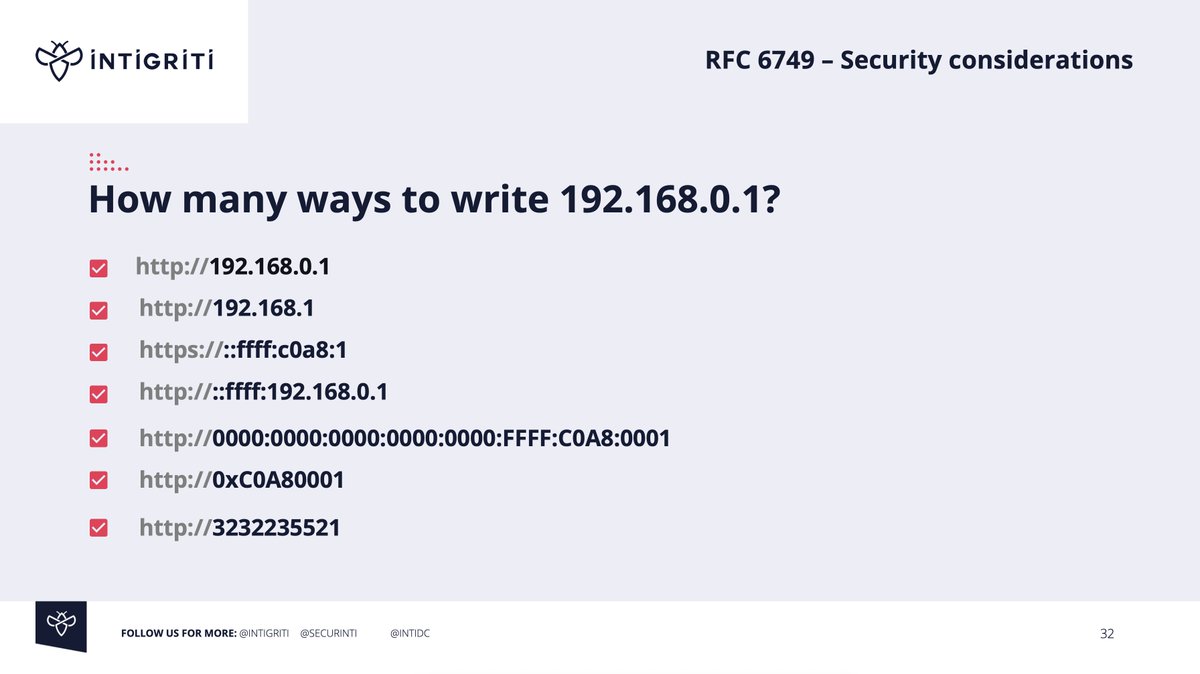
Same goes for IP addresses.. turns out there's a lot of ways to write the same thing. If your application only blacklists one, these can be easy bypasses!