How many times did your @Liferay customer's license expire, and you were the last to know? 🔑
Not anymore. The 37 Audits License auditor flags the activation screen the moment it replaces the site, even when uptime monitors say all good.
https://t.co/RFgi7qZkqc
@philnash@astrodotbuild@Cloudflare@resend Phil, I built a Contact Form checker that submits the form from time to time. It uses Resend's Inboud. https://t.co/8g231Z58Hw
37 Audits now checks your sites for the Black October flaws: PHP (CVE-2026-109618/109619) and Node.js (CVE-2026-111497). Run the php2shell and node2shell auditors against your own domains to see if you're exposed. https://t.co/6XGbLZ8L8B
Auditors that probe a site for weaknesses, like exposed admin paths or XML-RPC, now run only on domains you've proven you own. Verify in one click with your work email, or with a DNS record or a file. 37 Audits won't be pointed at someone else's site. https://t.co/6XGbLZ8L8B
37AuditsBot is now a Cloudflare verified bot ✅
It signs every request with Web Bot Auth, so sites behind Cloudflare can recognize 37 Audits and let your audits through instead of blocking them as unknown traffic.
https://t.co/zKJVMh2XNL
Patching is hard enough. Figuring out what to patch is way harder.
That's why I'm building 37 Audits: know what your sites run before the CVE drops.
https://t.co/6XGbLZ8L8B
Two critical PHP RCEs dropped today. CVSS 9.8, no auth needed.
This is satire. It's also a pretty accurate situation:
4 hours to patch.
11 hours to find out what PHP actually runs.
https://t.co/jKDCHztDdc
Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
@wasim117@37audits@wasim117 have you tried to run it on top of a Liferay project? Before run it don't forget to configure Liferay as a software stack. Let me know your feedback. Thanks
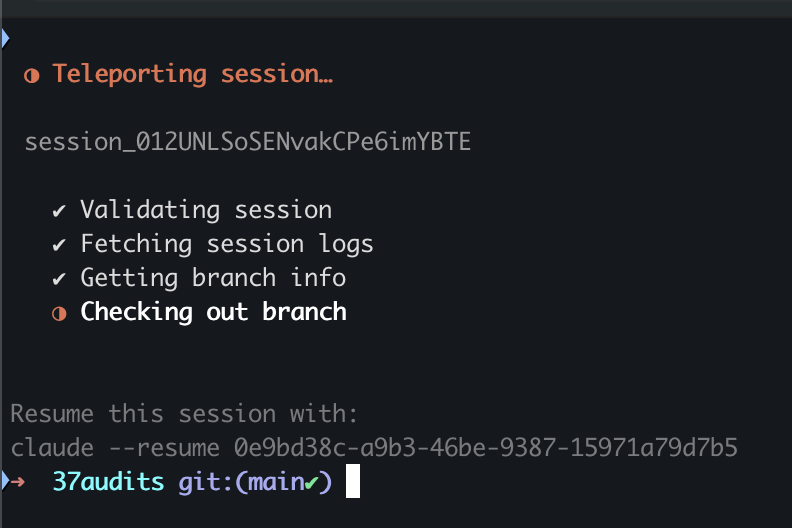
Today I tried a new dev workflow:
Started ideation and implementation on Claude Mobile, then switched to my computer to test and finish the work.
With `--teleport`, I picked up right where I left off.
Turns out AI-powered development is becoming multichannel too. 🚀
How many times did your @Liferay customer's license expire, and you were the last to know? 🔑
Not anymore. The 37 Audits License auditor flags the activation screen the moment it replaces the site, even when uptime monitors say all good.
https://t.co/RFgi7qZkqc
Great demo today with a Liferay partner. Their take on 37 Audits: "it fills the gaps" and "it automates several manual steps." Liferay CVEs, end of life, caching and security headers for every customer site, on one screen. https://t.co/6XGbLZ8L8B
New in 37 Audits: Stack Freshness. We now flag any software stack entry nobody has reviewed in 90 days (fail at 180, both configurable), so vulnerability and end-of-life alerts match what your site really runs. Still accurate? One click confirms it.
https://t.co/IMob0KEheI
More of your users will meet your product through an AI agent.
New on 37 Audits: a journey to make your SaaS agent-ready. llms.txt, markdown, an API agents can use, an MCP server card, checked on your site.
https://t.co/bkcYTafpvw
Consultancies and agencies: you can now earn 20% of what every customer you bring to 37 Audits pays, for 24 months, paid monthly.
Apply, share your link, and follow every customer and payout on your affiliate dashboard.
https://t.co/0KNEVCeHhS
Week two trying to focus on GTM (posting it 5 days late, which says something):
• 14 production deploys (15)
• 3 new auditors (2)
• 2 blog posts (0)
• 7 X posts (5)
• 7 cold messages (7)
• 2 prospect calls (2)
Promised fewer deploys, more conversations. Got one fewer deploy and the same conversations. Content moved, outreach didn't.
This week: double the cold messages before touching code.
One week trying to focus on GTM:
• 15 production deploys
• 2 new auditors
• 0 blog posts
• 5 X posts
• 7 cold messages
• 2 prospect calls
Made some moves, but 15 deploys tells the story: still too much building.
Next week: fewer deploys, more conversations.
This week I learned how `git worktree` works.
Now I can work on multiple things at once without constantly switching branches.
Wish I'd discovered this sooner!
Most outages aren't dramatic. A domain expires, a certificate doesn't renew, a backup was never restored.
New on 37 Audits: a journey to keep your website online, with auditors that catch what expires before it does.
https://t.co/GJsqzejIdc
Just released the referral program for @37audits 🎉
Invite a friend: they start with 2 extra full audits' worth of credits, and you get 2 full audits for every person who joins with your link. No limit, and the credits never expire.
https://t.co/e1FZWREQGM