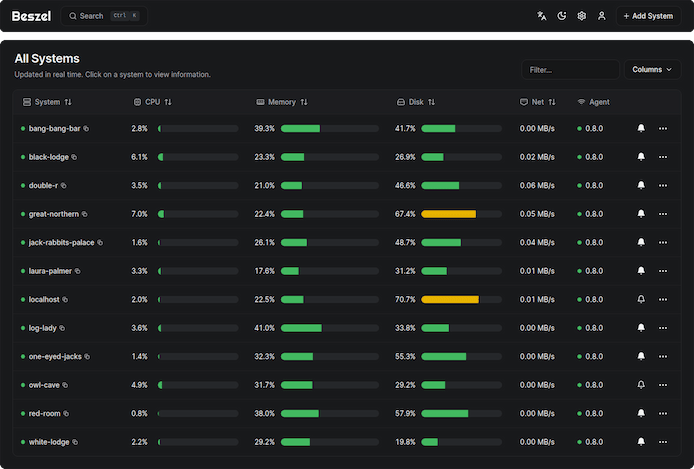
Beszel : une plateforme Open Source de supervision des serveurs, conçue pour être légère, simple à installer et peu gourmande en ressources.
👉 https://t.co/LD5oC3Wzku
🛡️We added Broadcom VMWare ESX vulnerability CVE-2026-41709 & Linux Kernel vulnerability CVE-2026-46300 to our KEV Catalog. Visit https://t.co/myxOwap1Tf & apply mitigations to protect your org. #Cybersecurity#InfoSec
Une faille critique vieille de 16 ans menace les serveurs utilisant le PXE boot. Référencée CVE-2026-97631 (CVSS 9,5/10), elle affecte EDK II, une base logicielle pas mal utilisée dans les firmwares UEFI.
Un paquet ICMP malformé peut provoquer un débordement mémoire et permettre l'exécution de code avec les privilèges maximaux, avant le chargement du système d'exploitation et ses protections. Un attaquant peut donc installer un malware persistant.
La bonne nouvelle est que ce n'est pas facilement exploitable (PXE activé, accès réseau et sploit sur mesure).
Mesure immédiate : désactiver PXE s'il est inutile.
https://t.co/IKB5RJaA09
Is your website vulnerable to php2shell? Here's a site to check it: https://t.co/9WobMmxJBC
Made by my colleague @horia_nita
We've also released PHP images w/ backported patches for free, more versions coming: https://t.co/Az60yxk3N6
Zabbix 8.0 RC1 is out!
📊 APM + OpenTelemetry: traces, logs, metrics in one place
🔇 Complex event processing: less noise, faster root cause
🛠️ Ad-hoc maintenance
🌙 New dark blue theme
LTS is coming. Try the RC: https://t.co/vrQZKfCrLU
Docker’s first few official skills for AI coding agents are available: https://t.co/xpbcMUvxOL 🎉
They’re designed to help agents with Docker tasks, and the collection will grow. See what they are and how to install them: https://t.co/kPNNWVS3bv
🚨 GITLAB CRITICAL PATCH: AUTH RCE VIA REGEX PARSER (CVE-2026-89078 / CVE-2026-93577)
GitLab released Critical patch versions 19.4.1, 19.3.3, and 19.2.7 on September 23, 2026 for CE/EE.
Lead Critical issues (both CVSS 9.9):
* CVE-2026-89078 — authenticated remote code execution via a double-free in the regular-expression parser when handling a crafted regex in CI/CD configuration
* CVE-2026-93577 — authenticated remote code execution via an integer overflow in the regular-expression compiler under the same class of crafted CI/CD regex input
Also in the same release: High XSS in the merge request diff viewer (CVE-2026-84739) plus several Medium/Low authz issues.
Impacted: GitLab CE/EE from 19.2 before 19.2.7, 19.3 before 19.3.3, and 19.4 before 19.4.1 (XSS reach extends further back on some issues). https://t.co/dDzuqpU3vf is already patched; Dedicated customers need no action. Self-managed installs should upgrade immediately.
⚠️ Analyst Note:
This is an official GitLab Critical patch release, not a dark-web leak claim and not a CISA KEV add as of our check. Both Critical RCEs require an authenticated user. No in-the-wild exploitation is claimed in the vendor notes reviewed here. Credit on the Critical regex issues: joaxcar via HackerOne.
Primary: https://t.co/L6ZGUEuxqN
#DDW #DarkWeb #GitLab #CVE202689078 #CVE202693577 #RCE #ThreatIntelligence #CyberSecurity
🚨[POC] CVE-2026-87902: WordPress Core versions up to and including 7.1.1 are affected by a Local File Inclusion vulnerability in the locate_template() function.
GitHub: https://t.co/VqaHEnmKku
All WordPress users need to update their WordPress installations immediately 💯
There is a 9.2 CVE that discloses a remote code execution vulnerability that affects versions all the way back to 2016 😬
Here's the official notice https://t.co/tbJlzC780L
🚨 Gizemli bir repo sessizce patladı: Tek bir GitHub’da tüm hacking araçları bir araya getirildi. 👇
65.000 beğeniyle viral olan bu koleksiyon, güvenlik araştırmacılarının ve etik hacker’ların yıllardır aradığı “hepsi bir arada” çözümü sunuyor.
Artık ayrı ayrı araç indirmek, kurmak, yapılandırmak yok. Her şey tek yerde.
Bu repo gerçekten ne kadar tehlikeli… yoksa ne kadar güçlü?
Sizce bu tür “tüm araçlar bir arada” repo’lar siber güvenlik dünyasını nasıl değiştirir?
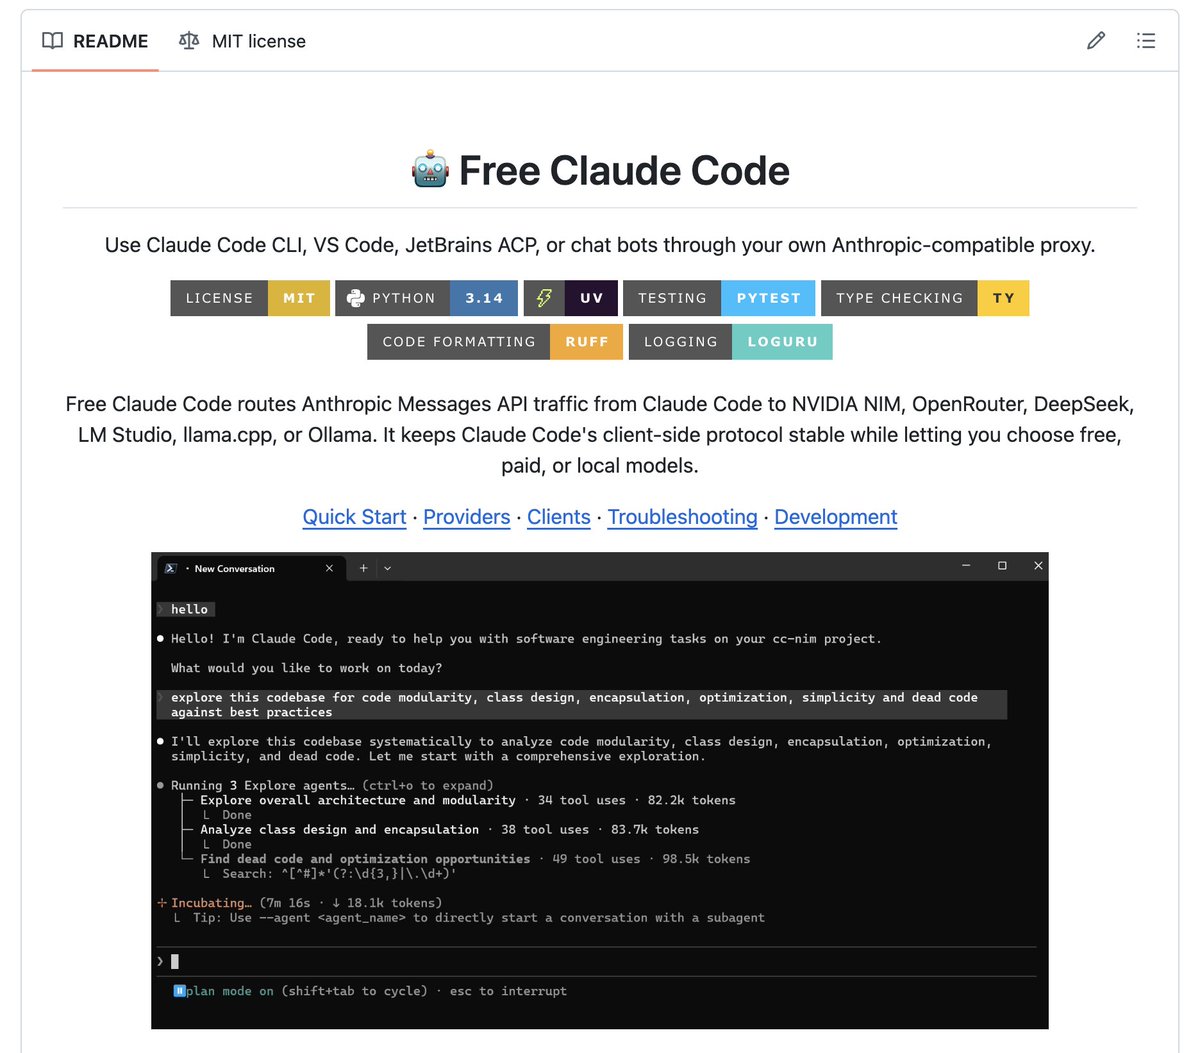
Proxy pour utiliser Claude Code gratuitement dans le terminal, VS Code ou via Discord — sans compte payant Anthropic.
Warning: pas sûr que ça marche si bien ou que ce soit totalement dans les clous des CGU de Claude.
https://t.co/nIPJUCjhFY
Cancelé YouTube Premium.
Y el reemplazo es GRATIS y Open source.
Se llama Invidious y hace básicamente todo lo que la gente paga en YT Premium:
→ Sin anuncios
→ Audio en segundo plano en móvil
→ Ver vídeos sin cuenta
→ Sin rastreo de Google
→ Sin algoritmo tóxico intentando engancharte durante horas
Lo más loco es lo rápida y limpia que se siente la navegación.
La web carga en milisegundos porque prácticamente no usa JavaScript.
• Sin trackers.
• Sin autoplay.
• Sin “vídeos recomendados” diseñados para robarte la tarde.
Además puedes:
→ Suscribirte a canales sin cuenta de Google
→ Recibir notificaciones cuando suben vídeo
→ Importar todas tus suscripciones de YouTube en 1 clic
→ Cambiar entre decenas de instancias públicas si una cae
→ Montarlo en tu propio VPS de 5€ y tener control total
→ Redirigir automáticamente todos los links de YouTube usando Privacy Redirect
El proyecto lleva años activo y sigue actualizándose.
100% open source.
Enlace abajo👇
🧐 CopyFail, Dirty Frag : un mainteneur propose d’ajouter un kill switch à Linux
Ma publication à ce sujet :
- https://t.co/VJC0Yt76JO
#linux#cybersecurite#sysadmin
Après la vidéo sur la faille Copy Fail (CVE-2026-31431), je vous propose cette fois-ci une analyse technique EN FRANCAIS ! (car ce type de contenu manque)
J'y ai passé mon dimanche matin !
Clin d'oeil à @ponceto91 et @korben_rss
https://t.co/fmj5xbEmke
#CopyFail#Linux