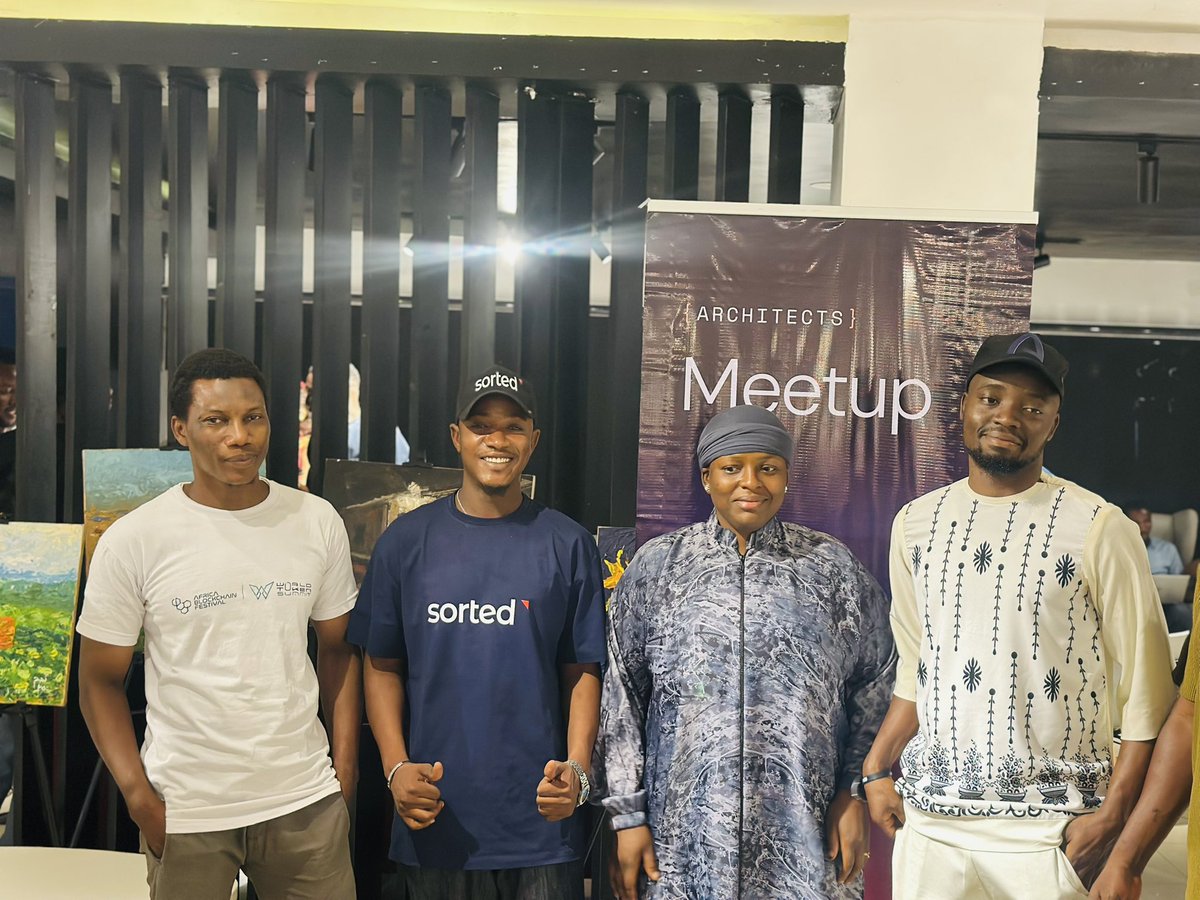
Web3 Family 💙🤝
Uncle @saeifchain_ 🤝
His little guy, @imamuswap 😎
Our Web3 Aunty, @ZaraFatoluu 💙
Our Web3 Lawyer, @web3_attorney ⚖️
By the way, Web3 Father, Sir @SdkSaddik was busy enjoying his food. Man was focused on the real priorities! 😂🍽️
Funny how Web3 brought us together. What started as conversations about Web3 has now made us feel like one big family. ❤️
Big thanks to @Abujaweb3connec for bringing us together! 🤝
Bridging is rarely the end goal.
The goal is what comes next: accessing apps, markets, liquidity, and opportunities across ecosystems.
USDC Bridge gives users a direct, Circle-built path to move USDC across supported chains with less friction and more transparency.
Move USDC crosschain. Then do what you came to do.
https://t.co/ugyPAhtrhm
Was North Korea really behind the Binance hack, or was it an inside job?
On October 29, approximately $6.4 billion was stolen from @binance in the largest crypto hack in history.
Blockchain intelligence firms including @trmlabs, @chainalysis and @elliptic have linked the attack to North Korea's TraderTraitor group.
But hundreds of users online, including @cozypront, @ylukem, @Hannibal9972485, @zectrillionaire and @jords, are raising suspicions of a possible inside job.
We examined the arguments on both sides:
> Arguments for False: What challenges the North Korea attribution?
1. Attackers left billions in stolen funds exposed to freezes.
@elliptic found that the attackers were unusually slow to convert stolen stablecoins, allowing issuers to freeze more than $2.6 billion.
North Korean hackers typically convert such assets much faster. This unusual delay warrants scrutiny, although the unprecedented scale of the theft could explain the difference.
2. The attackers used a different laundering strategy from the North Korean Bybit hackers.
@trmlabs and @elliptic observed that the Binance attackers relied heavily on large swaps through market makers and DeFi lending protocols. The North Korea-linked Bybit hackers, meanwhile, relied much more on cross-chain bridges and mixers.
3. Crypto accounts publicly questioned whether the hack was an inside job.
@CoinGapeMedia documented speculation from crypto commentators questioning how a compromised laptop could enable billions in unauthorized withdrawals.
@Cointelegraph also reported Binance's preliminary findings pointing to a compromised DevOps engineer's laptop.
However, compromised employee infrastructure is consistent with an external attack. No verified evidence currently establishes that Binance or its executives orchestrated the theft.
> Arguments for True: What links the attack to North Korea?
1. The attackers used preparation tactics matching earlier North Korean crypto thefts.
@trmlabs identified small Tornado Cash withdrawals, advance testing, and pre-signed authorizations executed in a coordinated burst. Similar tactics were observed in the 2025 Bybit hack, which the FBI attributed to North Korea's TraderTraitor group. The operational resemblance strengthens the attribution, although these techniques aren't exclusive to North Korean hackers.
2. Stolen Binance funds reached the same address as proceeds from another North Korea-linked hack.
@chainalysis identified stolen Binance funds mixing with proceeds from September's Bitget hack, previously attributed to North Korean actors. @elliptic independently confirmed the shared destination.
This creates a direct on-chain connection between the incidents, although shared laundering infrastructure doesn't conclusively establish that the same attackers were responsible.
3. Multiple blockchain intelligence firms independently linked the theft to North Korea.
@trmlabs attributed the attack to TraderTraitor with high confidence, citing on-chain and off-chain intelligence. @chainalysis separately reached a similar conclusion through fund tracing, while @elliptic also assessed North Korea-linked actors as responsible.
So what does the evidence tell us?
The strongest evidence currently points toward North Korea's TraderTraitor group.
The arguments against that attribution raise questions worth examining, but they don't carry equal evidentiary weight. And that's precisely why examining the underlying evidence matters.
On Verifact, we've brought together the arguments, evidence, and sources supporting both True and False, allowing traders to evaluate the claims themselves.
What does openEuler bring to embedded devices?
Wanming Hu explains openEuler Embedded's approach with MICA, then explores how IB-Robot connects robotics and AI software stacks.
▶️ Watch the full intervie.
[#2026MAMA] FANS’ CHOICE Category 2nd VOTE
& FANS' CHOICE OF THE YEAR with VISA OPEN
Vote for the Best Artist of 2026!
👉https://t.co/8KRMaKzaIq
📆Voting Period : Oct 28 6PM ~ Nov 8 11:59PM (KST)
✅One vote per day, per device, per ID
📌Each time you vote, you can select only one group per category for <FANS' CHOICE OF THE YEAR with VISA> and <FANS' CHOICE MALE/FEMALE Category>
==
FANS’ CHOICE 부문 2차 투표
& 올해의 팬스 초이스 with VISA OPEN
2026년 최고의 아티스트를 결정해 주세요!
👉https://t.co/8KRMaKzaIq
📆투표기간 : 10월 28일 18:00 ~ 11월 8일 23:59 (KST)
✅1일 / 1기기 / 1개 ID 당, 1회 투표 가능
📌1회 투표 시 <올해의 팬스 초이스 with VISA>,<FANS’ CHOICE 남자/여자> 부문별 1팀에게만 투표 가능
#MAMAAWARDS #2026MAMAAWARDS
#MnetPlus #엠넷플러스 @MnetMAMA
@jerallaire Native burn-and-mint transfers imply minimal user control over funds transfer process - what changes will this bridge bring to address potential security concerns?
@circle@proof@money2020 CCTP is expanding beyond USDC, which means more assets are being supported and transferred between blockchains, a clear step towards increasing interoperability and adoption within crypto ecosystems.
The Seine's gentle flow is often overlooked in favor of the city's grand architecture, but it's the subtle beauty that truly captures the essence of Paris.
BREAKING: Post-tropical Isaias still packs a dangerous punch as destructive winds, flooding threaten millions.
@jonathanserrie has the latest.
Follow live updates on the storm on @foxweather: https://t.co/nDvwhSccFd
After landfall we started driving towards Pensacola and as expected, tons of trees were down, along with power lines. Daylight is going to be interesting. Currently back at the hotel, with no power of course.
$120 FOR ONE CAN OF SPAM, AND YOU'RE PAYING FOR IT.
Nick Shirley caught what looks like a food stamp for cash swap on the streets of Seattle, with SNAP cards being traded like Pokémon cards and stores allegedly in on it.
Food stamps are supposed to feed hungry families, not bankroll hustlers.
Every dollar stolen this way comes out of taxpayers' pockets and off the tables of people who actually need it.
Prosecute the fraudsters, pull the licenses of any store that plays along, and audit the whole program.