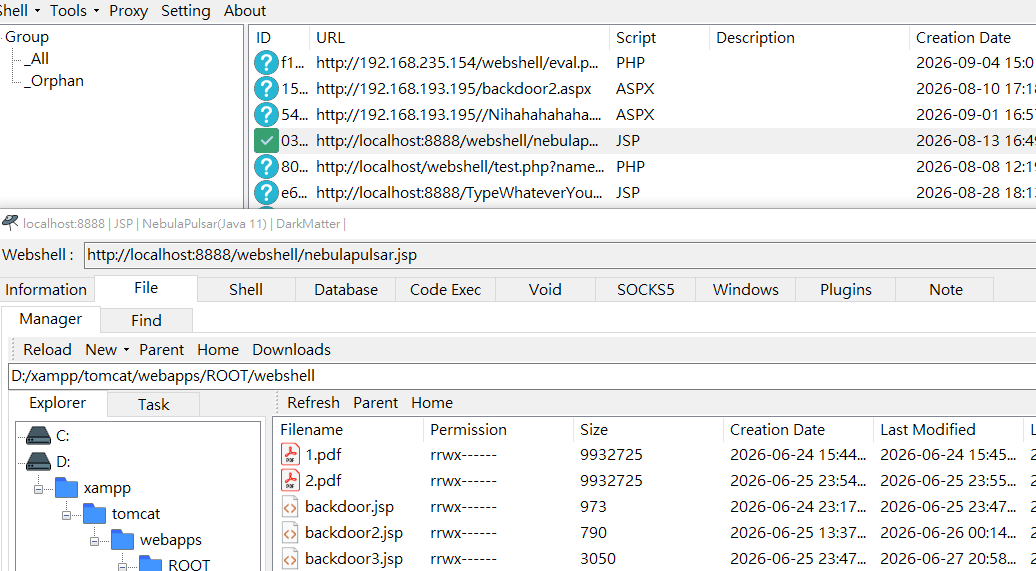
Plan to update my Alien webshell RAT (v5.2.0), just not sure if the release interval between the two versions is too short...
The fileless mem-shell will be more stable. And I think I will draw all my anime wallpapers for my tools from now on.
#Alien#webshell#memshell
Came across an exposed server at 176.97.218[.]79:8080 while looking through suspicious infrastructure and ended up finding what looks like a working Pulsar RAT setup.
The open directory contains Pulsar RAT 6.0 builds and source code, along with Donut, Xen-OFCrypt and a custom loader. What caught my attention was the exposed client configuration. It points directly back to 176.97.218[.]79:4782 and has persistence, keylogging, anti-debug and UAC bypass enabled.
There is also a client debug log from August 16 showing Pulsar running under DESKTOP-FIA5RHA, with repeated errors while trying to capture remote desktop frames.
That machine could just be the operator's test box, so I wouldn't call it confirmed victim activity yet. Still, this looks like more than someone simply hosting a copy of the Pulsar source. The server appears to have been set up and actually used as a working Pulsar RAT environment.
Back-to-school season is here and starting today, eligible college students can get a full year of Gemini on us:
- US students: 1 year of Google AI Pro at no cost
- 140+ countries: 1 year of Google AI Plus at no cost
Here’s what’s new for students �Back-to-school season is here and starting today, eligible college students can get a full year of Gemini on us:
- US students: 1 year of Google AI Pro at no cost
- 140+ countries: 1 year of Google AI Plus at no cost
Here’s what’s new for students �Back-to-school season is here and starting today, eligible college students can get a full year of Gemini on us:
- US students: 1 year of Google AI Pro at no cost
- 140+ countries: 1 year of Google AI Plus at no cost
Here’s what’s new for students �Back-to-school season is here and starting today, eligible college students can get a full year of Gemini on us:
- US students: 1 year of Google AI Pro at no cost
- 140+ countries: 1 year of Google AI Plus at no cost
Here’s what’s new for students �Back-to-school season is here and starting today, eligible college students can get a full year of Gemini on us:
- US students: 1 year of Google AI Pro at no cost
- 140+ countries: 1 year of Google AI Plus at no cost
Here’s what’s new for students �Back-to-school season is here and starting today, eligible college students can get a full year of Gemini on us:
- US students: 1 year of Google AI Pro at no cost
- 140+ countries: 1 year of Google AI Plus at no cost
Here’s what’s new for students 👇
Want to run an entire Tailscale daemon from memory inside a C2 implant with zero disk artifacts, no kernel drivers, traffic indistinguishable from HTTPS to a CDN, and relay connections from the victim network back through the tailnet.
Now you can. Enjoy!
https://t.co/WmBlShAnLr
Trying to learn security research and getting overwhelmed by all the details?
I just published a guide showing my process for step-by-step analysis of a security feature: https://t.co/7k87w8DhFh
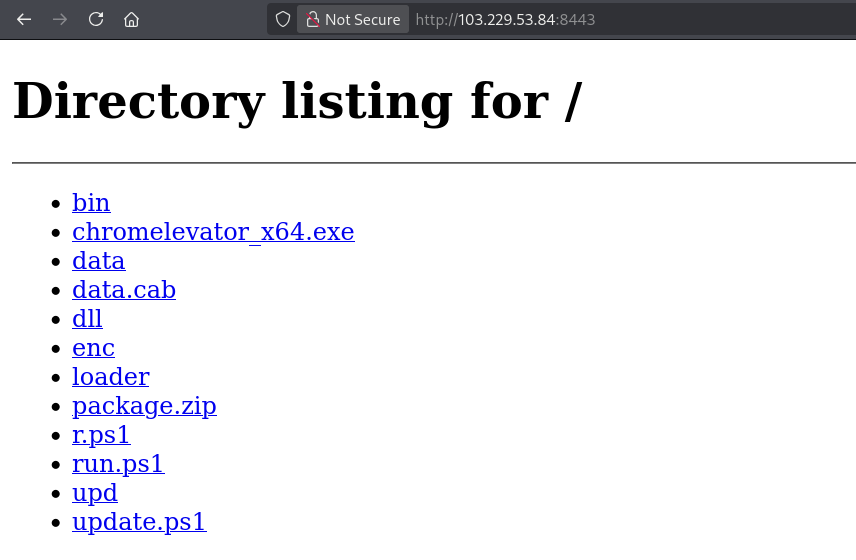
Found http://103.229.53[.]84:8443 through @Huntio during a C2 hunt. The host had directory listing enabled, which exposed several PowerShell loaders along with chromelevator_x64.exe, package[.]zip, data[.]cab, and a few encoded payload variants.
The loaders use more than one delivery method. One pulls the payload directly, another retrieves an XOR-encoded /bin object and decodes it with key 42, while other variants make use of certutil and different Windows process execution methods. The decoded PE is then launched with ChromElevator's output arguments and pointed at a local output directory.
From there, the scripts look for generated browser artifacts such as cookies, passwords and tokens. Cookie data is additionally transformed into a format that can be imported back into a browser session, after which the collected output is compressed and exfiltrated through Telegram.
The interesting part is that the Telegram bot token and destination are hardcoded across the chain, which provides a useful pivot into the operator's surrounding infrastructure.
This might be the most insane C Compiler I've ever seen in my life.
It turns C Code into Turing-complete single instruction assembly code with MOV only. It would be a nightmare to sift through malware compiled with this thing. @xoreaxeaxeax is so cracked.
https://t.co/y02eyiEUOn
@JoenOwek@skocherhan@OpcodeIntel@malwrhunterteam@smica83 You a security researcher and you left your server wide open to the public ?
Why not use cloudflare tunnel to hide it ?
Share it locally expose it with cloudflare to the public only who know the domain can access it