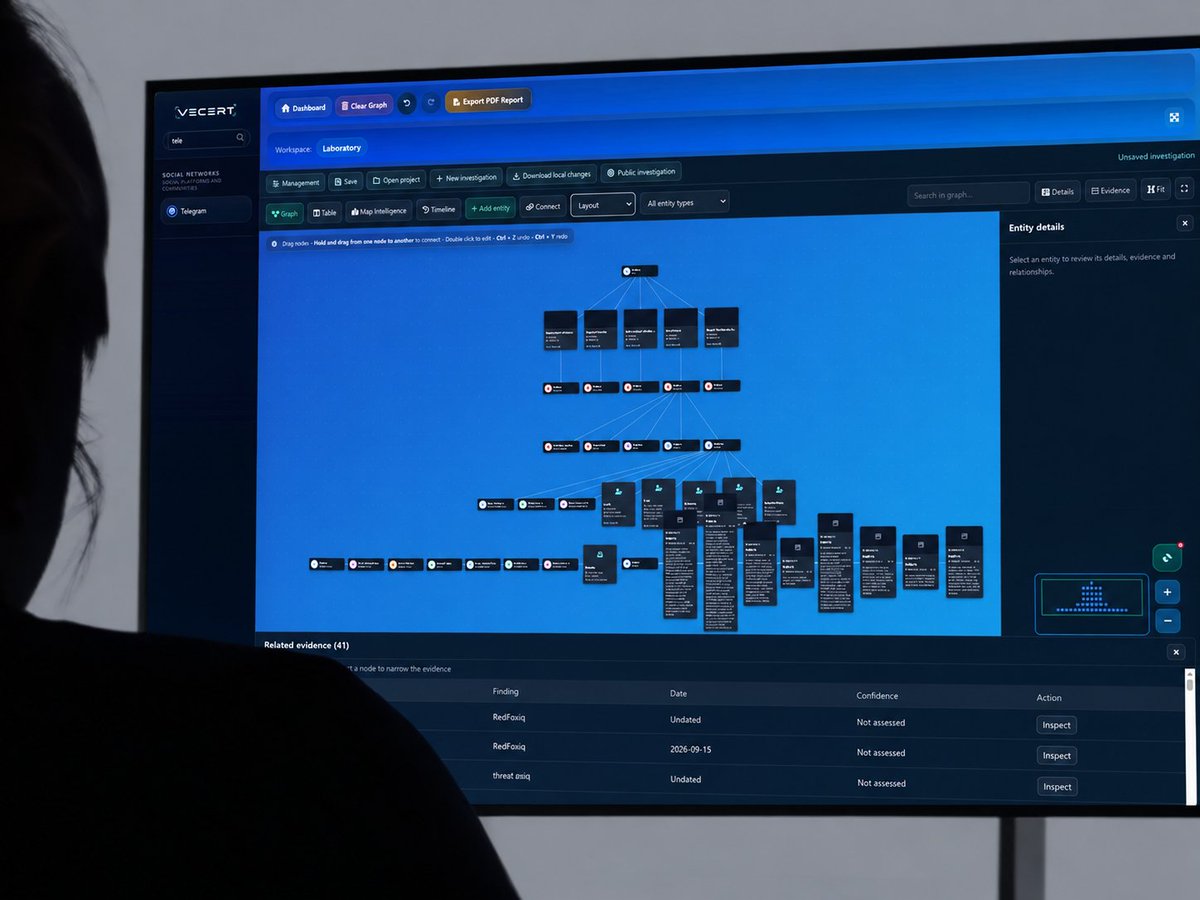
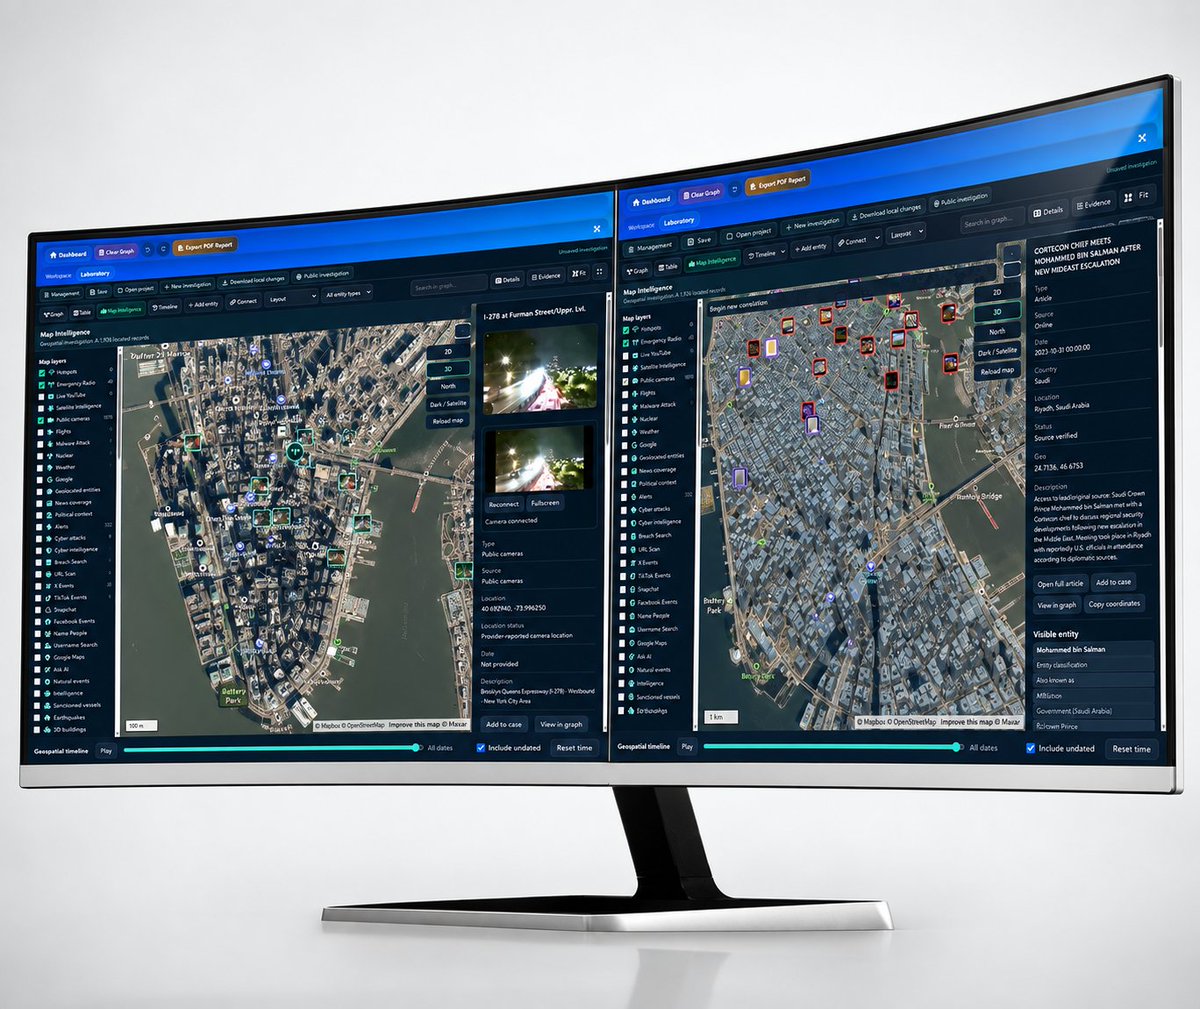
🚀 Revolutionize your analysis with VECERT AnalyzerPRO V6! 🔍
We’ve worked to bring true 360° OSINT capabilities to Analyzer. From CTI to pure OSINT, gain access to a vast repository of investigative data and real-time archives. 🌐📊
Ideal for resolving and tracking cyber incidents, physical-world events, and complex investigations. Put the full power of information right at your fingertips! 🕵️♂️💻💸
🏢 Companies, institutions, and independent organizations can purchase a license by emailing us at: ✉️ [email protected]
Start mastering the tool with our tutorials:
🎥 AnalyzerPRO - Investigation Basic I: https://t.co/doimjw0ENp
🎥 AnalyzerPRO - Investigation Basic II: https://t.co/cZf96ThjwC
#OSINT #CTI #VECERT #AnalyzerPRO #Cybersecurity #CyberIntelligence #FinancialInvestigation #DataAnalysis
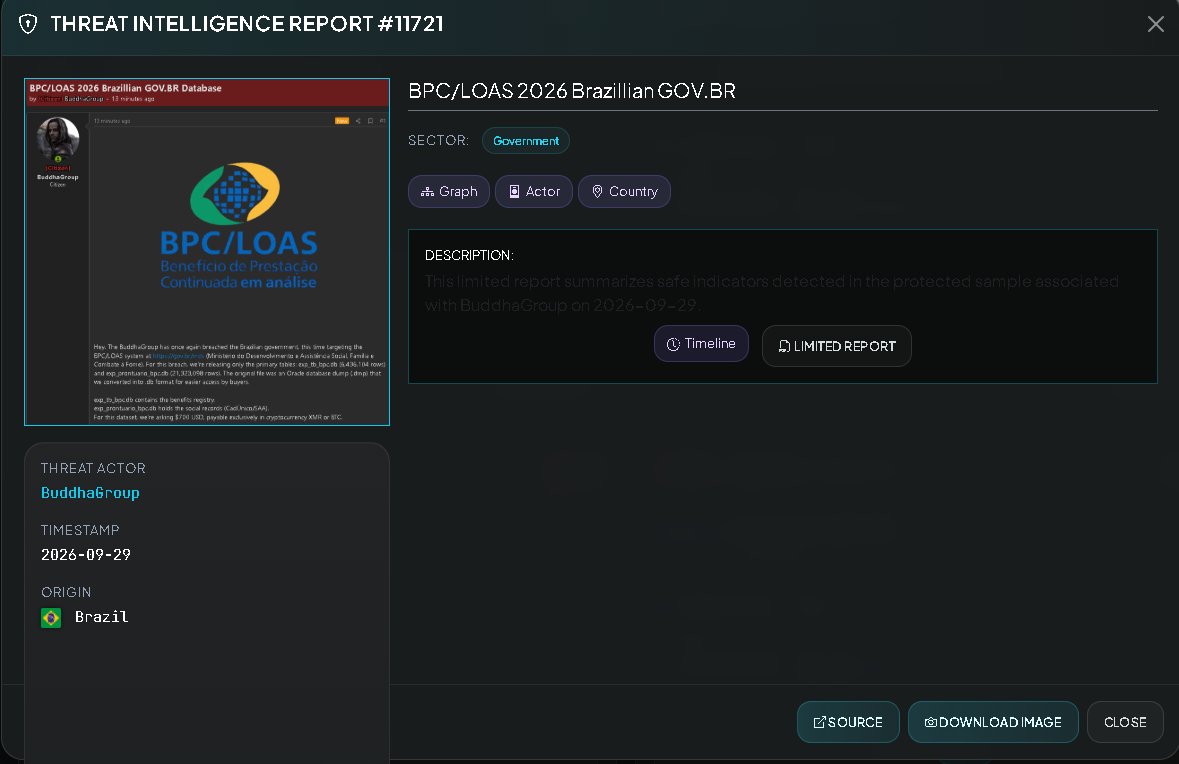
⚠️ CRITICAL PREVENTIVE ALERT 🇧🇷 🏛️: ALLEGED DATA EXFILTRATION FROM THE BRAZILIAN GOVERNMENT'S BPC/LOAS DATABASE (ACTOR: BUDDHAGROUP)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT YET VERIFIED / THREAT ACTOR: BUDDHAGROUP / DATE: SEPTEMBER 29, 2026]
The centralized cyber-intelligence system has detected a post made on September 29, 2026, by the group BuddhaGroup. The report announces a new attack against Brazilian government infrastructure, specifically targeting the BPC/LOAS system managed by the Ministry of Development and Social Assistance, Family and Fight Against Hunger (https://t.co/e5zRiXNZ2i).
It is strictly noted that the veracity of this compromise and the authenticity of the data have not been officially confirmed by Brazilian authorities. The definitive status of the data leak remains unconfirmed.
Threat Actor: BuddhaGroup.
Victim / Affected Entity: Ministry of Development and Social Assistance, Family and Fight Against Hunger of Brazil (BPC/LOAS System at https://t.co/vVTK0yby05).
Sector: 🏛️️ Government, Social Assistance, and Citizen Data Protection.
Country: Brazil 🇧🇷.
🔍 TECHNICAL BREAKDOWN OF THE EXPOSED DATA STRUCTURE
According to details published by the cybercriminal group, the exfiltrated package originated from an Oracle database dump (.dmp) that was converted to .db format to facilitate querying:
Benefits Table (exp_tb_bpc.db):
Contains a total of 6,436,104 records corresponding to the program's official beneficiary registry.
Social Records Table (exp_prontuario_bpc.db):
Houses 21,323,098 records linked to unified social case files (CadÚnico/SAA).
Verification and Samples:
The threat actors provided external download links (anonfilesnew .com) to allow for integrity verification of sample files prior to finalizing transactions.
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / GOVERNMENT)
Audit of MDS Perimeters and Servers: Brazilian government IT teams must immediately review access logs on the servers hosting the Ministry of Social Development databases to identify the data extraction vector.
Monitoring and Blocking of Sales Channels: Monitor the spread of the sample data and restrict access to the contact points identified by the threat actors in order to mitigate the illicit sale of state records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #BPC #LOAS #Brazil #GovernmentSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
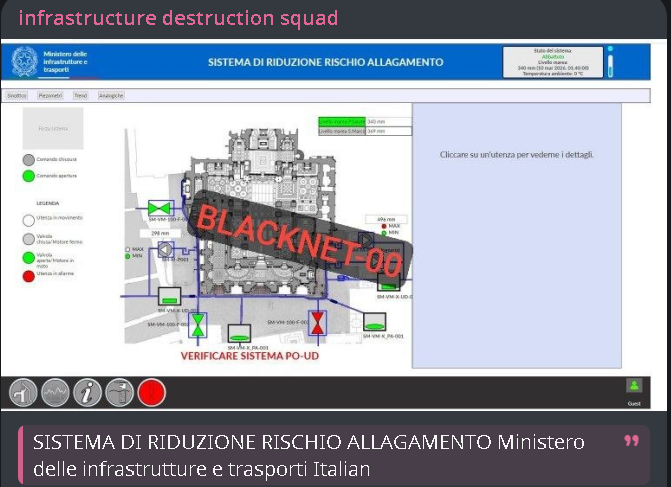
⚠️ CRITICAL PREVENTIVE ALERT 🇮🇹 🛡️: ALLEGED COMPROMISE OF CRITICAL CONTROL SYSTEMS AT THE ITALIAN MINISTRY OF INFRASTRUCTURE AND TRANSPORT (ACTOR: BLACKNET-00 / INFRASTRUCTURE DESTRUCTION SQUAD)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: BLACKNET-00 / DATE: SEPTEMBER 29, 2026]
The centralized cyber-intelligence system has detected a high-risk notification circulated on September 29, 2026, linked to the groups "Infrastructure Destruction Squad" and BlackNet-00. The report indicates alleged unauthorized access to and manipulation of the control interface for the Flood Risk Reduction System (*Sistema di Riduzione Rischio Allagamento*) under the Italian Ministry of Infrastructure and Transport (*Ministero delle Infrastrutture e dei Trasporti*).
It is strictly noted that the veracity of this compromise and actual interference with operational systems have not been officially confirmed by Italian government authorities. The definitive status of the infrastructure remains unconfirmed.
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / CRITICAL INFRASTRUCTURE)
Immediate OT/IT Network Isolation: Italian government incident response teams must isolate internet-facing water control gateways, revoke compromised credentials, and verify event logs.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ3laQ
Quickly check your security at: https://t.co/QZhWp0ldhm
Quotes and services: https://t.co/sx3BM5zJdi
#Cybersecurity #ThreatIntel #CriticalInfrastructure #Italy #BlackNet #InfrastructureDestructionSquad #ICS #SCADA #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
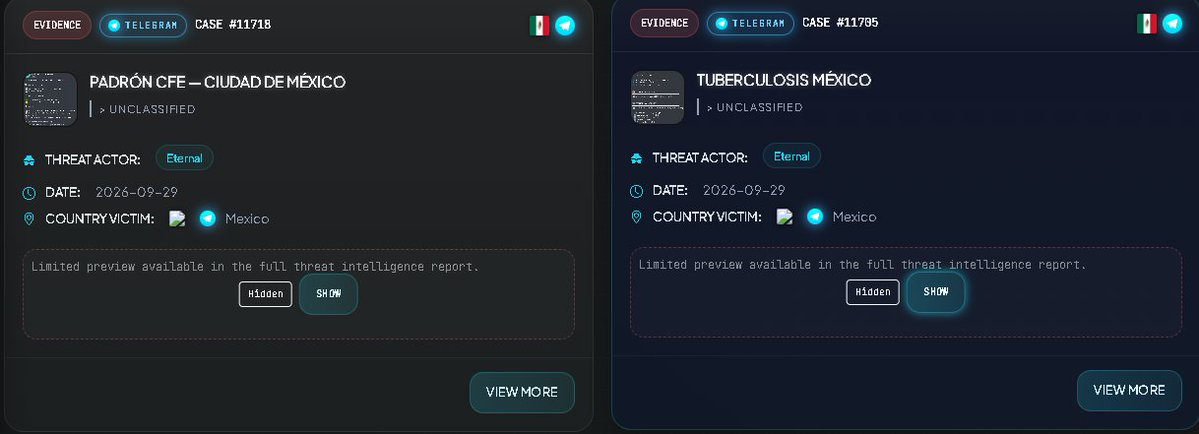
⚠️ PREVENTIVE ALERT 🇲🇽 ⚡: OFFER AND SALE OF HEALTH DATA (TUBERCULOSIS) AND CFE CUSTOMER REGISTRY IN MEXICO (ACTOR: ETERNAL)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: ETERNAL / DATE: SEPTEMBER 29, 2026]
The centralized cyber-intelligence monitoring system has detected a notification posted on September 29, 2026, by the user "Eternal." The report announces the sale of two highly sensitive databases from Mexico: a nationwide clinical registry of tuberculosis patients and the complete registry of Federal Electricity Commission (CFE) contracts for Mexico City.
It is strictly noted that the veracity of this offer and the legitimacy of the data have not been officially confirmed by the affected government institutions. The definitive status of the repositories remains unverified.
🌐 INCIDENT SUMMARY
Threat Actor: Eternal
Victims / Affected Entities: Mexico's Health Sector (National Epidemiological Surveillance System / Tuberculosis) and the Federal Electricity Commission (CFE - Mexico City).
Sector: 🏥 Public Health, Epidemiology, and ⚡ Electrical Utility Infrastructure.
Country: Mexico 🇲🇽.
🛡️️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / GOVERNMENT)
Audit of Epidemiological and Commercial Repository Systems: IT departments at the Ministry of Health and the CFE must urgently review access controls for their databases and analytics servers to determine the source of the data extraction. Monitoring and Tracking of Leak Channels: Track the activity of the associated actor to mitigate sample distribution and protect systems against automated mass-extraction queries.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #Tuberculosis #CFE #Mexico #CDMX #HealthcareSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ PREVENTIVE ALERT 🇬🇹 🛡️: ALLEGED INTRUSION AND EXFILTRATION OF PHOTOGRAPHS AND POLICE RECORDS IN GUATEMALA (ACTOR: RETHIXX)
[STATUS: UNCONFIRMED; VISIBLE EVIDENCE BUT NOT OFFICIALLY VERIFIED / THREAT ACTOR: RETHIXX / DATE: SEPTEMBER 29, 2026]
The centralized cyber-intelligence system has detected a post on underground forums (DarkForums) made on September 29, 2026, by the user "rethixx." The report announces the exfiltration of over 1,000 photographs and records of citizens with police records from the official platform of the Guatemalan National Civil Police (policiales .pnc. https://t.co/aDOAqOwvY8).
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by authorities from the ministry or the police institution. The definitive status of the systems remains unconfirmed.
🔍 TECHNICAL BREAKDOWN OF VISUAL EVIDENCE AND UNAUTHORIZED ACCESS
According to the screenshots provided by the actor on the underground forum:
Access Vector and Internal Panels: The images display the police record management interface of the Guatemalan PNC (policiales. pnc. https://t.co/e4dWgCcY1q and /historial).
Exposure of Biometric and Personal Data: Access to registered user profiles is evident (such as files under the names of Mario Teyul and other citizens), exposing high-resolution facial photographs, CUI numbers, dates of birth, marital status, home addresses, details of police records, and reports of lost documents.
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / GOVERNMENT)
Forensic Audit and Session Revocation: The technical teams of the Guatemalan National Civil Police (PNC) must immediately isolate the servers hosting the criminal record web portal, invalidate active sessions, and conduct a thorough analysis of access logs.
Web Perimeter Patching: Review authentication and access control mechanisms to prevent attackers from maintaining persistence on public and internal query platforms.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ3laQ
Quickly check your security at: https://t.co/QZhWp0ldhm
Quotes and services: https://t.co/sx3BM5zJdi
#Cybersecurity #ThreatIntel #DataLeak #PNC #Guatemala #GovernmentSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
This morning @FBI and our partners the Dutch National Police are announcing the arrest of one of the alleged leaders of ShinyHunters - a global cybercrime and threat actor group linked to cyberattacks in the United States, the Netherlands, and around the world.
In coordination with FBI investigators the Dutch High-Tech Crime Unit arrested the suspect under Dutch law. As we speak FBI teams are actively working with partners to obtain and execute more leads in the ongoing investigation based on this arrest.
Thank you to our Dutch National Police partners for their continued work with us in this case and the industry partners who shared information with us.
The investigation continues.
-DKP🇺🇸
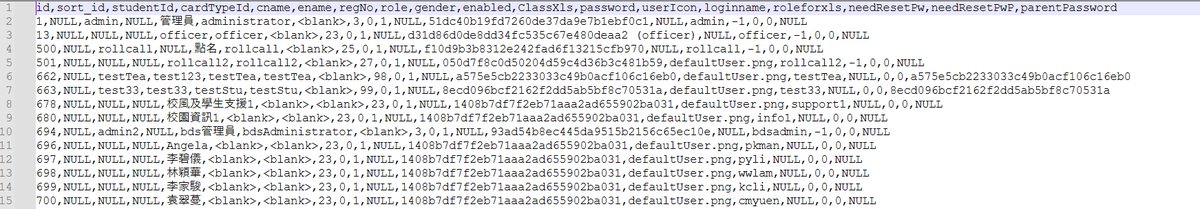
⚠️ PREVENTIVE ALERT 🇭🇰 🎓: ALLEGED LEAK AND EXFILTRATION OF METHODIST COLLEGE DATABASE (ACTOR: ANKA TEAM)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT YET VERIFIED / THREAT ACTOR: ANKA TEAM / DATE: SEPTEMBER 29, 2026]
The centralized cyber-intelligence system has detected a social media post circulated on September 29, 2026, by the group Anka Team. The report announces the compromise and data leak of the Methodist College (https://t.co/QBUfaS7QlX) database in Hong Kong, exposing a massive volume of user records and credentials.
It is strictly noted that the veracity of this compromise and official confirmation of the breach have not yet been definitively confirmed by the educational institution. The actual status of the systems remains unverified.
Threat Actor / Group: Anka Team.
Victim / Affected Entity: Methodist College (https://t.co/QBUfaS7QlX), an educational institution located in Hong Kong.
Sector: 🎓 Higher Education, Academic, and Institutional.
Target Country / Territory: Hong Kong (China).
Reported Data Volume: A total of 235,138 exposed records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #MethodistCollege #HongKong #AnkaTeam #TurkHackTeam #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
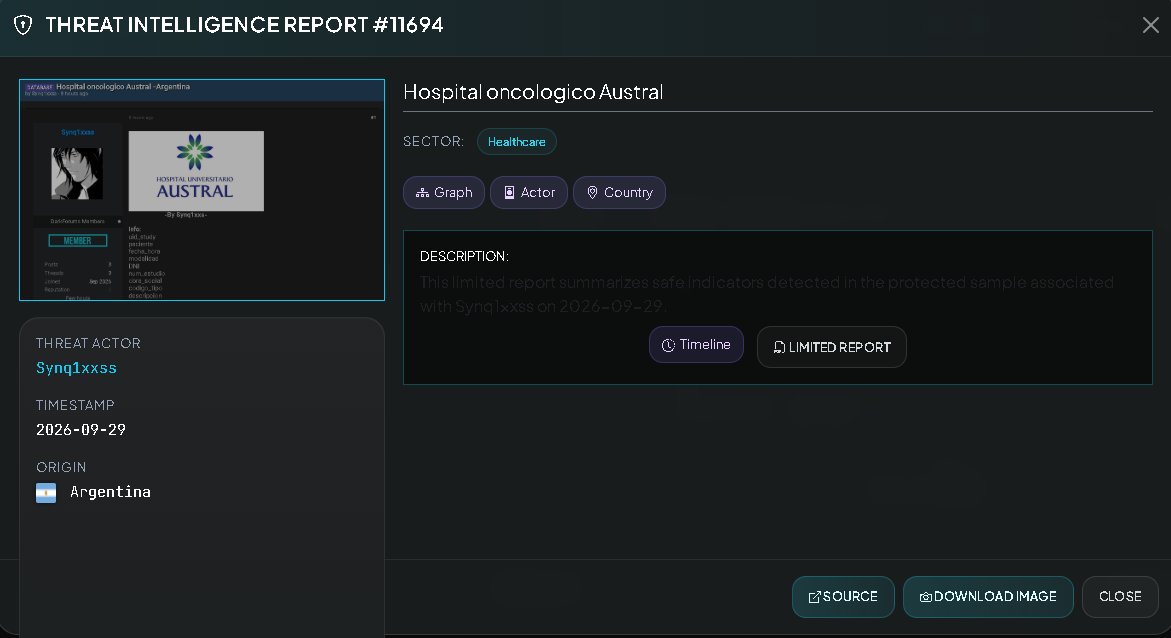
⚠️ PREVENTIVE ALERT 🇦🇷 🏥: ALLEGED EXFILTRATION OF PATIENT DATA AND CLINICAL STUDIES FROM HOSPITAL ONCOLÓGICO AUSTRAL (ACTOR: SYNQ1XXSS)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: SYNQ1XXSS / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence system has detected a post on underground forums (DarkForums) made on September 28, 2026, by the user Synq1xxss. The report announces the disclosure of records and information linked to Hospital Oncológico Austral in Argentina.
It is strictly noted that the veracity of this compromise and the authenticity of the records have not been officially confirmed by the medical institution. The definitive status of the leak remains unconfirmed.
Threat Actor: Synq1xxss
Victim / Affected Entity: Hospital Oncológico Austral (Argentina).
Sector: 🏥 Healthcare, Oncology, and Clinical Data Management.
Target Country: Argentina 🇦🇷.
🔍 TECHNICAL BREAKDOWN OF THE EXPOSED DATA STRUCTURE
According to the JSON-format samples provided by the actor on the underground forum, the leaked information includes:
Declared Data Schema:
uid_study, patient, date_time, modality, DNI (National ID), study_number, health_insurance, type_code, description. Sample Clinical Records:
Detailed records of medical studies dated August 25, 2026.
Recorded modalities include electrocardiograms (ECG – Resting 12-lead ECG with type 150 codes) and specialized studies (ES).
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / HEALTHCARE)
DICOM Server and PACS Repository Audit: Hospital IT teams must immediately verify access permissions for medical image storage systems and electronic health records.
Revocation of Unauthorized Access: Invalidate compromised credentials and review activity logs to rule out the presence of backdoors.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security status at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #HospitalAustral #Oncology #Argentina #HealthcareSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ PREVENTIVE ALERT 🇲🇽 🎓: ALLEGED EXFILTRATION OF DATABASE AND INSTITUTIONAL EMAILS FROM https://t.co/lpI02FPU23 (ACTOR: QILLNIHHERS / GQC)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT OFFICIALLY VERIFIED / THREAT ACTOR: QILLNIHHERS (GODS QUIET CHILDS - GQC) / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums (DarkForums) made on September 28, 2026, by the user "qillnihhers," representing the group Gods Quiet Childs (GqC). The report announces the compromise and alleged leak of a database containing a list of institutional and academic email addresses from the Morelos Campus of the National Autonomous University of Mexico (UNAM) (https://t.co/YK01igQjE3).
It is strictly noted that the veracity of this compromise and the technical scope of the intrusion have not been officially confirmed by university authorities. The definitive status of the infrastructure remains unconfirmed.
Threat Actor / Group: qillnihhers / Gods Quiet Childs - GqC
Victim / Affected Entity: National Autonomous University of Mexico - Morelos Campus (https://t.co/YK01igQjE3).
Sector: 🎓 Higher Education, Academic and University Research.
Country: Mexico 🇲🇽.
Additional Activity: The group is promoting the sale of WordPress credentials at affordable prices and sharing additional vulnerability vectors (SQLi).
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / UNIVERSITY)
Credential and Email Account Audit: UNAM technology teams must review the security of exposed email accounts and implement multi-factor authentication (MFA).
Website and CMS Verification: Scan servers hosting institutional portals for malicious files, compromised credentials, or SQL injection (SQLi) vulnerabilities.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #UNAM #Morelos #GodsQuietChilds #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ PREVENTIVE ALERT 🇺🇸 🎓: ALLEGED INTRUSION AND COMPROMISE OF BROWARD COLLEGE'S VIRTUAL MACHINE SYSTEM (ACTOR: ANKA TEAM)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: ANKA TEAM / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums by user "FIRE," representing the "Anka Team" collective. The report announces unauthorized access to and infiltration of the virtual machine network at Broward College—a U.S. educational institution—exposing approximately 1,400 user records and displaying messages on active virtual machines.
It is strictly noted that the veracity of this compromise and the authenticity of the scope have not been officially confirmed by the university. The definitive status of the infrastructure remains unconfirmed.
Threat Actor / Group: Anka Team (user FIRE).
Victim / Affected Entity: Broward College (https://t.co/MYhIYBaZ9x), a higher education institution in Florida, United States.
Sector: 🎓 Higher Education, Academic Research, and Laboratory Virtualization.
Target Country: United States 🇺🇸.
Reported Data Volume: Approximately 1,400 leaked user records.
🔍 TECHNICAL BREAKDOWN OF VISUAL EVIDENCE AND ATTACK VECTOR
Exploitation Vector: The attackers indicate the use of an SQLi (SQL Injection) vulnerability at the login stage (Login Bypass) to circumvent authentication controls. Administrative Access: Access to virtual laboratory management panels using an account identified as "aceadmin" has been documented.
Visual Evidence: Screenshots show virtual laboratory administration consoles (ACEITLab) and modified screens on Windows virtual machines displaying messages referencing a specific group and future commemorative dates (October 29, 2026).
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / EDUCATION)
Web Vulnerability Auditing and Patching: Broward College IT teams must immediately review authenticated entry points to remediate SQL injection (SQLi) flaws in login forms.
Privileged Access Revocation: Immediately invalidate the "aceadmin" account and any active session tokens, while conducting a full forensic analysis of the virtual machine network.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #BrowardCollege #AnkaTeam #SQLi #Virtualization #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
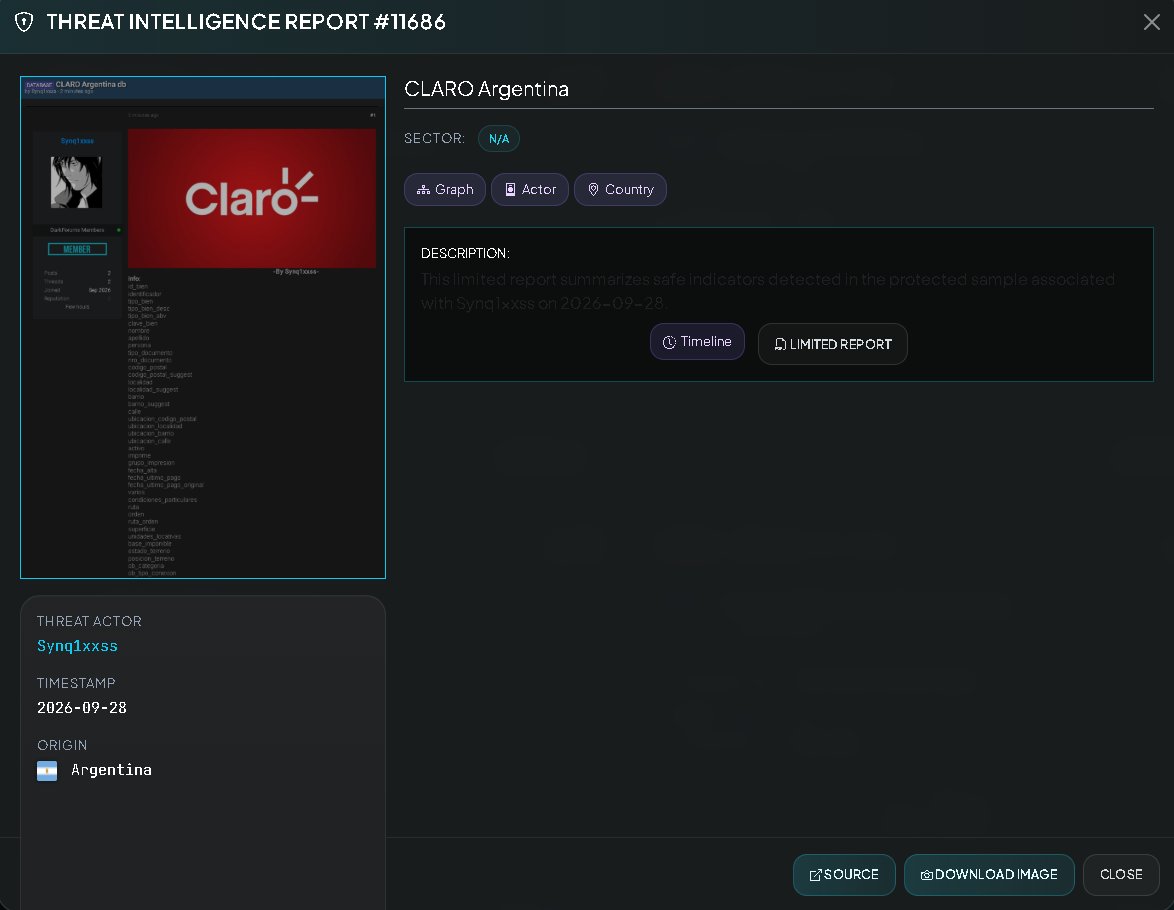
⚠️ PREVENTIVE ALERT 🇦🇷 📱: ALLEGED LEAK OF DATABASE AND ACCOUNT RECORDS (ACTOR: SYNQ1XXSS)
[STATUS: UNCONFIRMED; VISIBLE EVIDENCE BUT NOT YET VERIFIED / THREAT ACTOR: SYNQ1XXSS / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums (DarkForums) made on September 28, 2026, by the user Synq1xxss. The report announces the availability of a database titled "CLARO Argentina db," although the schemas and technical samples provided in the content detail account records, debts, burial coverage, salaries, and infraction notices linked to local entities in Argentina.
It is strictly noted that the authenticity of this breach and the official origin of the data have not been definitively confirmed by the mentioned entities or companies. The final status of the leak remains unconfirmed.
Threat Actor: Synq1xxss
Victim / Affected Entity: Records referenced under service names and locations in Argentina (including data samples regarding accounts, salaries, and municipal citations).
Sector: 📱 Telecommunications, Financial Services, Coverage Plans, and Municipal Records.
Country: Argentina 🇦🇷.
🔍 TECHNICAL BREAKDOWN OF THE EXPOSED DATA STRUCTURE
Based on the JSON-format fragments and samples posted by the actor on the underground forum, the leaked information comprises:
Account Structure and Personal Data:
Included fields: asset ID (*id_bien*), identifier, asset type (e.g., Comprehensive Burial Coverage / OBIS), asset key, first names, surnames, document type (CUIT/DNI), document number, postal codes, localities, neighborhoods, streets, enrollment dates, and last payment indicators.
Salary Record Sample:
Indexed structure detailing employee files, first names and surnames, administrative areas (such as the Tourism Directorate or Education Secretariat), employee types, roles, periods, payment types (monthly, 13th-month salary/bonus, contributions), and total amounts.
Traffic Citation Sample:
Records of traffic violations, citation dates, reference numbers, inspecting officers, offender details, and specifics regarding the regulatory infractions.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT)
Server and Endpoint Audit: Security teams at the affected organizations must review access logs on their databases and storage servers to identify potential data exfiltration breaches.
Monitoring and Early Warning: Monitor the spread of download links across underground channels to mitigate the commercialization of the data.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #ClaroArgentina #Argentina #DarkForums #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ PREVENTIVE ALERT 🇶🇦 🛡️: ALLEGED INTRUSION AND UNAUTHORIZED ACCESS TO QATAR MINISTRY OF INTERIOR SYSTEM (ACTOR: C00RRUPT)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: C00RRUPT / DATE: SEPTEMBER 27, 2026]
The centralized cyber-intelligence monitoring system has logged a notification released on September 27, 2026, by the threat actor c00rrupt. The actor claims to have discovered a vulnerability in a website linked to the Qatar Ministry of Interior (facility security sector) and asserts having gained access to a control panel containing military statistics.
It is strictly noted that the veracity of this intrusion and the actual security status of the system have not been officially confirmed by Qatari authorities. The definitive scope of the breach remains unconfirmed.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #Qatar #SecurityBreach #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
السلام عليكم ورحمة الله وبركاته،
تم اكتشاف ثغرة أمنية في موقع يتبع
لوزارة الداخلية القطرية (قطاع أمن المنشآت)،
والتي تمكنت من خلالها من الوصول إلى لوحة التحكم الخاصة بإحصائيات العسكر!
تم هاذا الفحص والاختبار قِبل (c00rrupt).
⚠️ CRITICAL PREVENTIVE ALERT 🇵🇦 🏛️: ALLEGED LEAK OF PAYROLL AND SENSITIVE DATA OF PANAMA GOVERNMENT EMPLOYEES (ACTOR: TERROAHOVER)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: TERROAHOVER / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums (DarkForums) made on September 28, 2026, by the user TerroahOver (supported by screenshots). The report announces the release of an extensive list containing sensitive data and employment histories of Panama government officials and workers, citing the continued existence of records that supposedly should have been purged based on date criteria.
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by Panamanian government authorities. The definitive scope of the leak remains unconfirmed.
Threat Actor: TerroahOver.
Victim / Affected Entity: Government of Panama (Personnel records and state payrolls).
Sector: 🏛️ Government, Public Administration, and State Sector.
Target Country: Panama 🇵🇦.
🔍 TECHNICAL BREAKDOWN OF THE EXPOSED DATA STRUCTURE
According to the technical schemas and text snippets published on the underground forum, the leaked records contain highly sensitive fields regarding public employees:
Declared Data Structure:
[FIRST NAME] [LAST NAME] [ID NUMBER] [JOB TITLE] [APPOINTMENT] [PAYROLL] [POSITION] [BASE SALARY] [TOTAL SALARY] [ADDITIONAL SALARY] [ADDITIONAL SALARY] [BIENNIAL SALARY INCREMENT] [REPRESENTATION ALLOWANCE] [25% COMPENSATION] [SOCIAL SECURITY] [SUPERVISORY ROLE] [STATUS] [START DATE]
Visual Evidence: The attached screenshots show lines of text containing officials' names, ID numbers, job titles (such as community promoters, analysts, secretaries, and drivers), assigned salaries, and start dates at state agencies.
🛡️ TECHNICAL PREVENTIVE CONTAINMENT
RECOMMENDATIONS (SOC / CSIRT / GOVERNMENT)
Human Resources and Payroll Systems Audit: Panamanian state IT teams must verify the source of the exposed data, review access controls for payroll databases, and ensure the proper purging of historical records.
Monitoring and Early Warning: Establish surveillance protocols to detect potential misuse of the affected officials' information.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ3laQ
Quickly check your security at: https://t.co/QZhWp0ldhm
Quotes and services: https://t.co/sx3BM5zJdi
#Cybersecurity #ThreatIntel #DataLeak #Panama #GovernmentSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
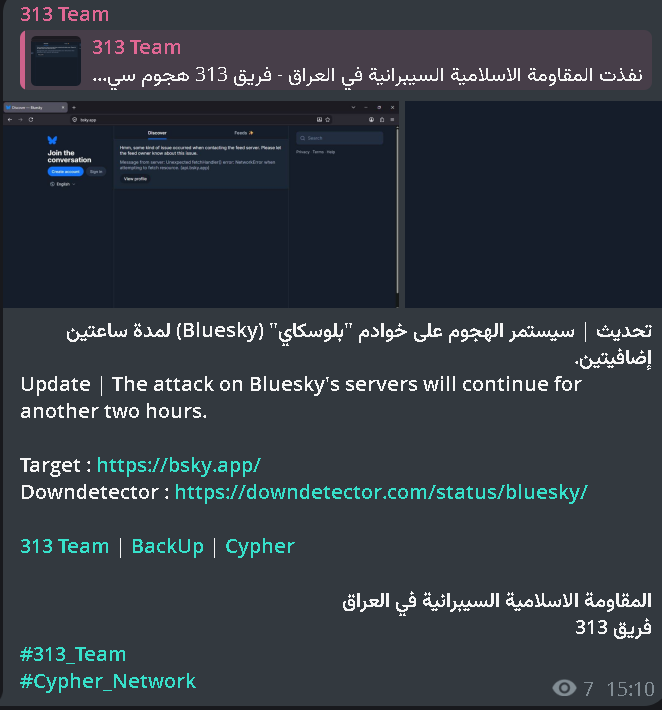
⚠️ PREVENTIVE ALERT 🌐 🛑: DENIAL-OF-SERVICE (DDoS) ATTACK AGAINST BLUESKY SERVERS (ACTOR: 313 TEAM)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT CONFIRMED / THREAT ACTOR: 313 TEAM (CYPHER NETWORK) / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has logged an attack notification issued on September 28, 2026, by the 313 Team collective (associated with the Islamic cyber resistance in Iraq). The report details the execution of a Denial-of-Service (DDoS) offensive against the server infrastructure of the social media platform Bluesky.
#Cybersecurity #ThreatIntel #DDoS #Bluesky #313Team #CypherNetwork #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ PREVENTIVE ALERT 🇨🇱 🏥: ALLEGED DATA BREACH OF THE *REVISTA CHILENA DE MEDICINA INTENSIVA* (CHILEAN JOURNAL OF INTENSIVE CARE MEDICINE) (ACTOR: LVN4T1K0 / GHOSTLEAKERS TEAM)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT YET VERIFIED / THREAT ACTOR: LVN4T1K0 (GHOSTLEAKERS TEAM) / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums by user Lvn4t1k0, representing the GhostLeakers Team collective. The report announces the release of the complete database belonging to the *Revista Chilena de Medicina Intensiva* (https://t.co/sVpwEeWkUS).
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by the publishing institution. The definitive status of the information remains unconfirmed.
Threat Actor / Group: Lvn4t1k0 / GhostLeakers Team
Victim / Affected Entity: *Revista Chilena de Medicina Intensiva* (https://t.co/sVpwEeWkUS).
Sector: 🏥 Healthcare; Medical, Academic, and Scientific Publications.
Target Country: Chile 🇨🇱.
File Format and Size: CSV format; approximate size of 658 KB.
🔍 TECHNICAL BREAKDOWN OF THE SAMPLE
According to the metadata and technical schemas published by the actor on the underground forum, the leaked records include:
Exposed Information Fields:
Full names of registered users and professionals.
Email addresses.
Internet Protocol (IP) addresses. Record creation dates and timestamps (created, published).
Sample Records: The actor attached a CSV snippet containing historical records dating back to 2010, exposing data on healthcare professionals in Chile.
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / HEALTHCARE)
Audit of Academic Systems and Portals: Platform administrators should review web servers and associated repositories to check for active breaches or exposed backups.
Early Alert to Affected Users: Notify the healthcare professionals whose data appears in the public samples so they can strengthen the security of their email accounts.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #IntensiveCare #Chile #GhostLeakers #Healthcare #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
⚠️ PREVENTIVE ALERT 🇬🇹 🏛️: ALLEGED DATA LEAK AND ACCESS TO THE SUPERINTENDENCY OF TAX ADMINISTRATION (SAT) IN GUATEMALA (ACTOR: RETHIXX)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: RETHIXX / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums made on September 28, 2026, by the user "rethixx." The report alleges the existence of vulnerabilities and a purported leak of over 6,000 records from the platform of Guatemala's Superintendency of Tax Administration (SAT), specifically its "Agencia Virtual" (Virtual Agency) portal
It is strictly noted that the veracity of this compromise and the authenticity of the records have not been officially confirmed by Guatemalan tax authorities. The definitive scope of the breach remains unconfirmed.
Threat Actor: rethixx
Victim / Affected Entity: Superintendency of Tax Administration (SAT) of Guatemala (
Sector: 🏛️ Government, Fiscal, Tax, and Taxpayer Registry.
Target Country: Guatemala 🇬🇹.
Reported Data Volume: Over 6,000 exposed records. 🔍 TECHNICAL BREAKDOWN OF VISUAL EVIDENCE AND DATA
Based on details published on the forum and the attached screenshots:
Access Vector and Environment: Images show interactive panels from the SAT Virtual Agency , electronic invoicing lists, and automated command consoles for data extraction.
Types of Exfiltrated Data: The actor details that the leak includes residential addresses, photographs of identity documents (Cédula de Vecindad or DPI), dates of birth, electronic invoices, and work addresses of the affected taxpayers.
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / GOVERNMENT)
Security Audit of SAT Endpoints: Guatemalan government IT teams must immediately verify the integrity of the servers hosting the Virtual Agency, revoke active sessions, and apply corrective patches to address potential access control vulnerabilities.
Monitoring of Clandestine Channels: Restrict access to external contact points associated with the dissemination of the leaked samples to prevent the illicit sale of tax records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #SAT #Guatemala #GovernmentSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
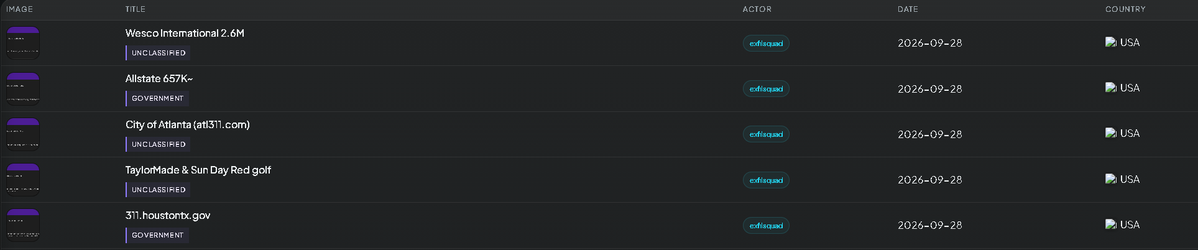
⚠️ PREVENTIVE ALERT 🇺🇸 🛡️: NEW REPORTS OF EXFILTRATION AND BREACHES IN U.S. GOVERNMENT AND CORPORATE INFRASTRUCTURE (ACTOR: EXFILSQUAD)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT YET VERIFIED / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has logged a new batch of high-risk reports in the evidence console. The alerts detail alleged data leaks, unauthorized access, and compromises of corporate and government databases in the United States, attributed to the actor/collective known as ExfilSquad.
It is strictly noted that the veracity of these incidents and the technical confirmation of the breaches have not been officially confirmed by the affected entities. The definitive scope remains unconfirmed. 📋 ORGANIZED DATA FROM DETECTED REPORTS
Case ID, Target / Subject, Threat Actor, Country Target, Category, Date
#—, Wesco International 2.6M, exfilsquad, USA, Unclassified, 2026-09-28
#—, Allstate 657K, exfilsquad, USA, Government, 2026-09-28
#—, City of Atlanta (https://t.co/hu92WVlDEX), exfilsquad, USA, Unclassified, 2026-09-28
#—, TaylorMade & Sun Day Red golf, exfilsquad, USA, Unclassified, 2026-09-28
#—, https://t.co/tLjAgaN5Pm, exfilsquad, USA, Government, 2026-09-28
🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS (SOC / CSIRT / ADMINISTRATIONS)
Perimeter and Municipal Server Audit: IT teams at the affected cities and corporations must immediately review access logs for public portals and internal databases.
Credential Rotation and Access Revocation: Invalidate active sessions and apply security patches to exposed servers to prevent attacker persistence.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly verify your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #Exfilsquad #Wesco #Allstate #Atlanta #Houston #USA #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
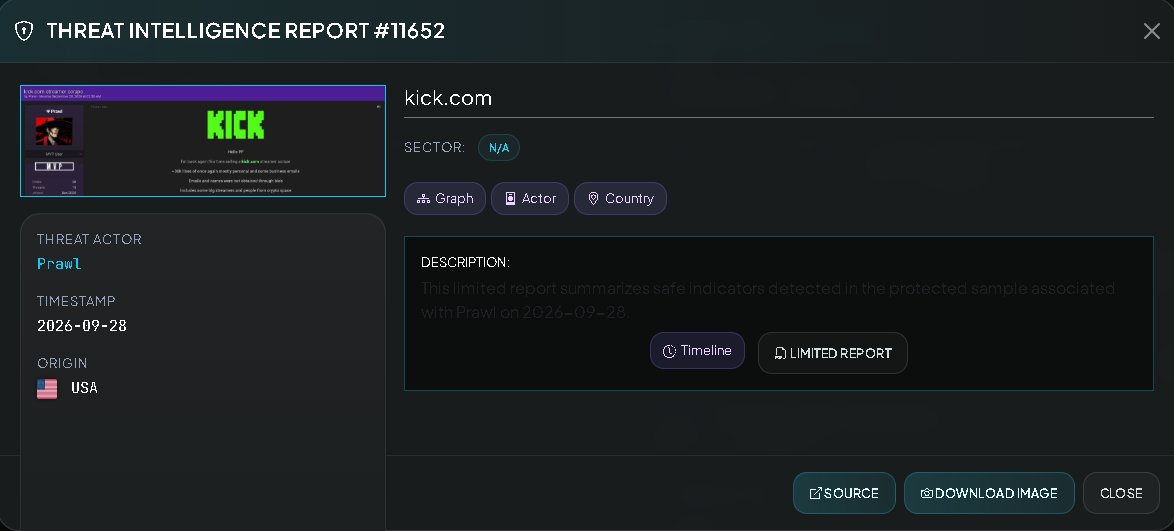
⚠️ PREVENTIVE ALERT 🌐 🎮: ALLEGED EXFILTRATION AND SALE OF KICK. COM STREAMER AND USER DATABASE (ACTOR: PRAWL)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: PRAWL / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a post on underground forums made on September 28, 2026, by the user "Prawl." The post announces the sale of a database containing approximately 30,000 lines of information extracted from streamers, content creators, and active users of the streaming platform https://t.co/rqqyMcbm6y.
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by the affected platform. The definitive status of the data remains unverified.
Threat Actor: Prawl
Victim / Affected Entity: Content creators and users of the https://t.co/rqqyMcbm6y platform.
Sector: 🎮 Streaming, Digital Entertainment, and Social Media.
Reported Data Volume: Approximately 30,000 personal and business email records.
🔍 TECHNICAL BREAKDOWN OF THE EXPOSED SAMPLE
According to details provided by the actor on the underground forum:
Data Origin: The author specifies that the email addresses and real names were not obtained from public profile biographies.
Affected Profiles: Includes high-profile creators ("big streamers") and prominent figures from the cryptocurrency ecosystem operating on the platform. Data Structure Included:
Username.
Email.
Legal name.
🛡️ TECHNICAL PREVENTIVE RECOMMENDATIONS (SOC / CSIRT / PLATFORMS)
Implementation of Multi-Factor Authentication (MFA): Content creators on Kick. com and similar platforms should secure their accounts using two-factor authentication and strong, unique passwords.
Phishing Email Monitoring: Platform security teams should alert the community about potential impersonation campaigns based on the exposed data.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #KickCom #Streaming #DataLeak #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
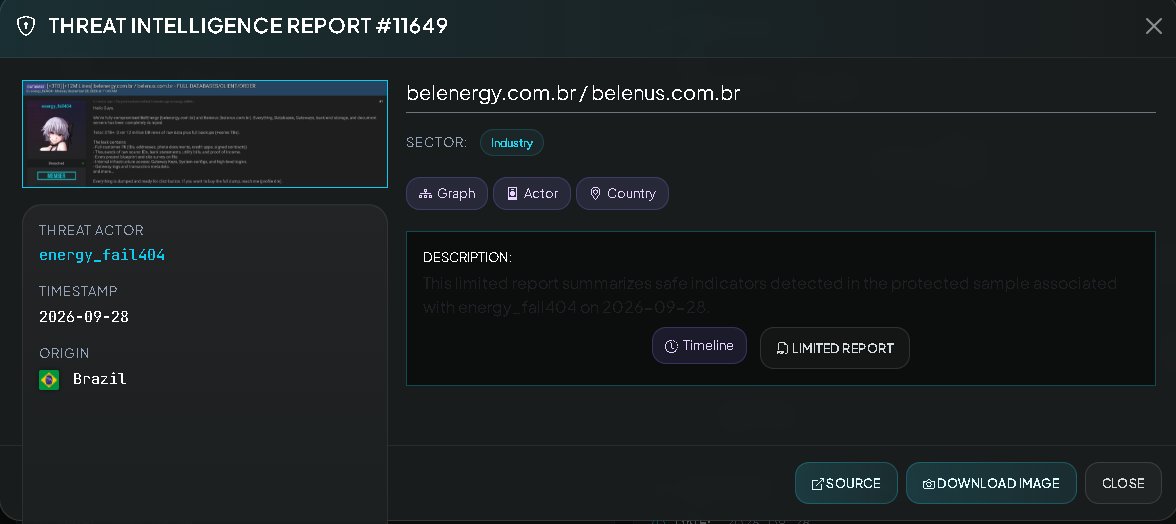
⚠️ PREVENTIVE ALERT 🇧🇷 ⚡: ALLEGED COMPROMISE OF 3 TB AND 12 MILLION RECORDS FROM BELENERGY AND BELENUS (ACTOR: ENERGY_FAIL404)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: ENERGY_FAIL404 / DATE: SEPTEMBER 28, 2026]
The centralized cyber-intelligence monitoring system has detected a high-severity post on underground forums, made on September 28, 2026, by the user energy_fail404. The actor announces the alleged total compromise and massive data extraction from the systems of BelEnergy (belenergy. https://t.co/Hf76b3Qxau) and Belenus (belenus. https://t.co/Hf76b3Qxau), leading companies in the solar and energy distribution sectors in Brazil. However, this has not been confirmed.
It is strictly noted that the veracity of this compromise and the actual scope of the exfiltration have not been officially confirmed by the affected companies. The definitive status of the infrastructure remains unconfirmed.
Threat Actor: energy_fail404
Victim / Affected Entity: BelEnergy and Belenus
Sector: ⚡ Solar Energy, Electrical Infrastructure, and Wholesale Trade.
Country: Brazil 🇧🇷.
Claimed Data Volume:
3 Terabytes (3 TB+) of total storage, including full backups.
12 million database records containing raw data. 🔍 TECHNICAL BREAKDOWN OF EXFILTRATION AND EXPOSED SAMPLES
According to information published by the threat actor on the forum, the exfiltrated data package comprises:
Sensitive Personal Data (PII):
Comprehensive customer information, including identity documents (IDs), residential addresses, credit applications, and signed contracts.
Scanned Documentation and Financial Records:
Thousands of scanned original documents: identity documents, bank statements, utility bills, and proof of income.
Engineering Projects and Blueprints:
Detailed plans for photovoltaic projects and site surveys.
Internal Infrastructure and Credentials:
Payment gateway keys, internal system configurations, high-level access credentials, gateway logs, and transaction metadata.
Proof Samples:
The actor provided external links to download database samples (`raw_data_database`) and photo packages of identity documents (`photo_document`) via temporary hosting platforms (Gofile and Temp .sh).
🛡️ TECHNICAL PREVENTIVE AND CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / ENERGY SECTOR)
Forensic Audit and Access Revocation: BelEnergy and Belenus technology teams must immediately revoke all compromised internal access credentials, gateway keys, and API tokens.
Document Server Isolation: Review document storage servers and databases to identify the intrusion vector and ensure no persistent access points (backdoors) remain.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #BelEnergy #Belenus #SolarEnergy #Brazil #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
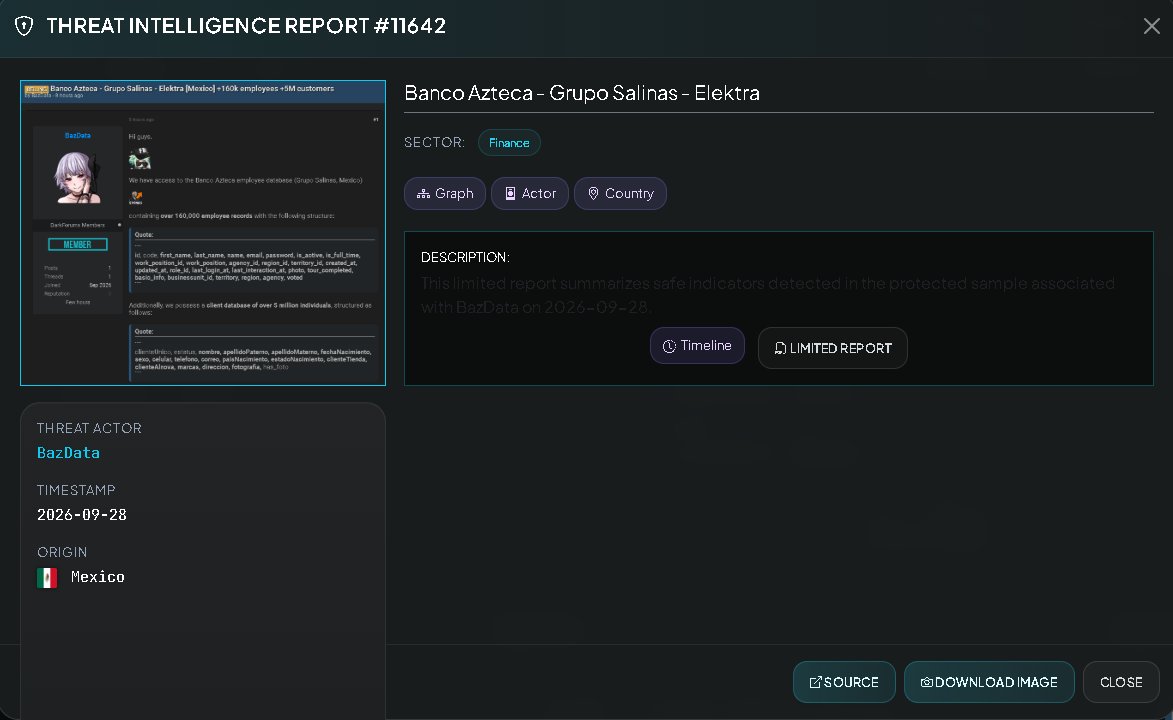
⚠️ PREVENTIVE ALERT 🇲🇽 🏦: ALLEGED SALE OF EMPLOYEE AND CUSTOMER DATABASES FROM BANCO AZTECA, GRUPO SALINAS, AND ELEKTRA (ACTOR: BAZDATA)
[STATUS: UNCONFIRMED / THREAT ACTOR: BAZDATA / DATE: SEPTEMBER 28, 2026]
Centralized cyber-intelligence monitoring has detected a major post on underground forums (DarkForums) made on September 28, 2026, by the user "BazData." The post announces the possession and availability for sale of corporate and customer databases belonging to Banco Azteca, Grupo Salinas, and Elektra stores in Mexico.
It is strictly noted that the veracity of this compromise and the authenticity of the records have not been officially confirmed by the affected financial or business institutions.
🌐 INCIDENT SUMMARY AND TARGETS
Threat Actor: BazData
Victim / Affected Entity: Banco Azteca, Grupo Salinas, and Elektra (Mexico).
Sector: 🏦 Banking, Financial Services, and Retail.
Target Country: Mexico 🇲🇽.
Claimed Data Volume:
Employee Database: Over 160,000 records.
Customer Database: Over 5 million individuals.
- Unconfirmed. 🔍 TECHNICAL BREAKDOWN OF DATA STRUCTURE
Based on the metadata and technical schemas presented by the threat actor on the underground forum, the exposed information is divided into two main components:
Employee Database Structure (+160k records):
Included fields: id, code, first_name, last_name, name, email, password, is_active, is_full_time.
Organizational and control information: work_position_id, work_position, agency_id, region_id, territory_id, created_at, updated_at, role_id, last_login_at, last_interaction_at.
Additional metadata: photo, tour_completed, basic_info, businessunit_id, territory, region, agency, voted (includes employee photographs).
Customer Database Structure (+5M records):
Identification and personal details: clienteUnico, estatus, nombre, apellidoPaterno, apellidoMaterno, fechaNacimiento, sexo.
Contact and location data: celular, telefono, correo, paisNacimiento, estadoNacimiento, direccion.
Commercial and biometric classification: clienteTienda, clienteAlnova, marcas, fotografia, has_foto (includes customer photographic records).
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / BANKING)
Credential Invalidation and Rotation: The financial institution's security teams must immediately revoke passwords and access tokens for all employee profiles exposed in the schema.
Enhanced Transaction Monitoring: Establish strict behavioral alerts across digital platforms and service channels to detect atypical activity or unauthorized access attempts associated with the millions of allegedly affected customers.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #BancoAzteca #GrupoSalinas #Elektra #Mexico #BankingSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert